
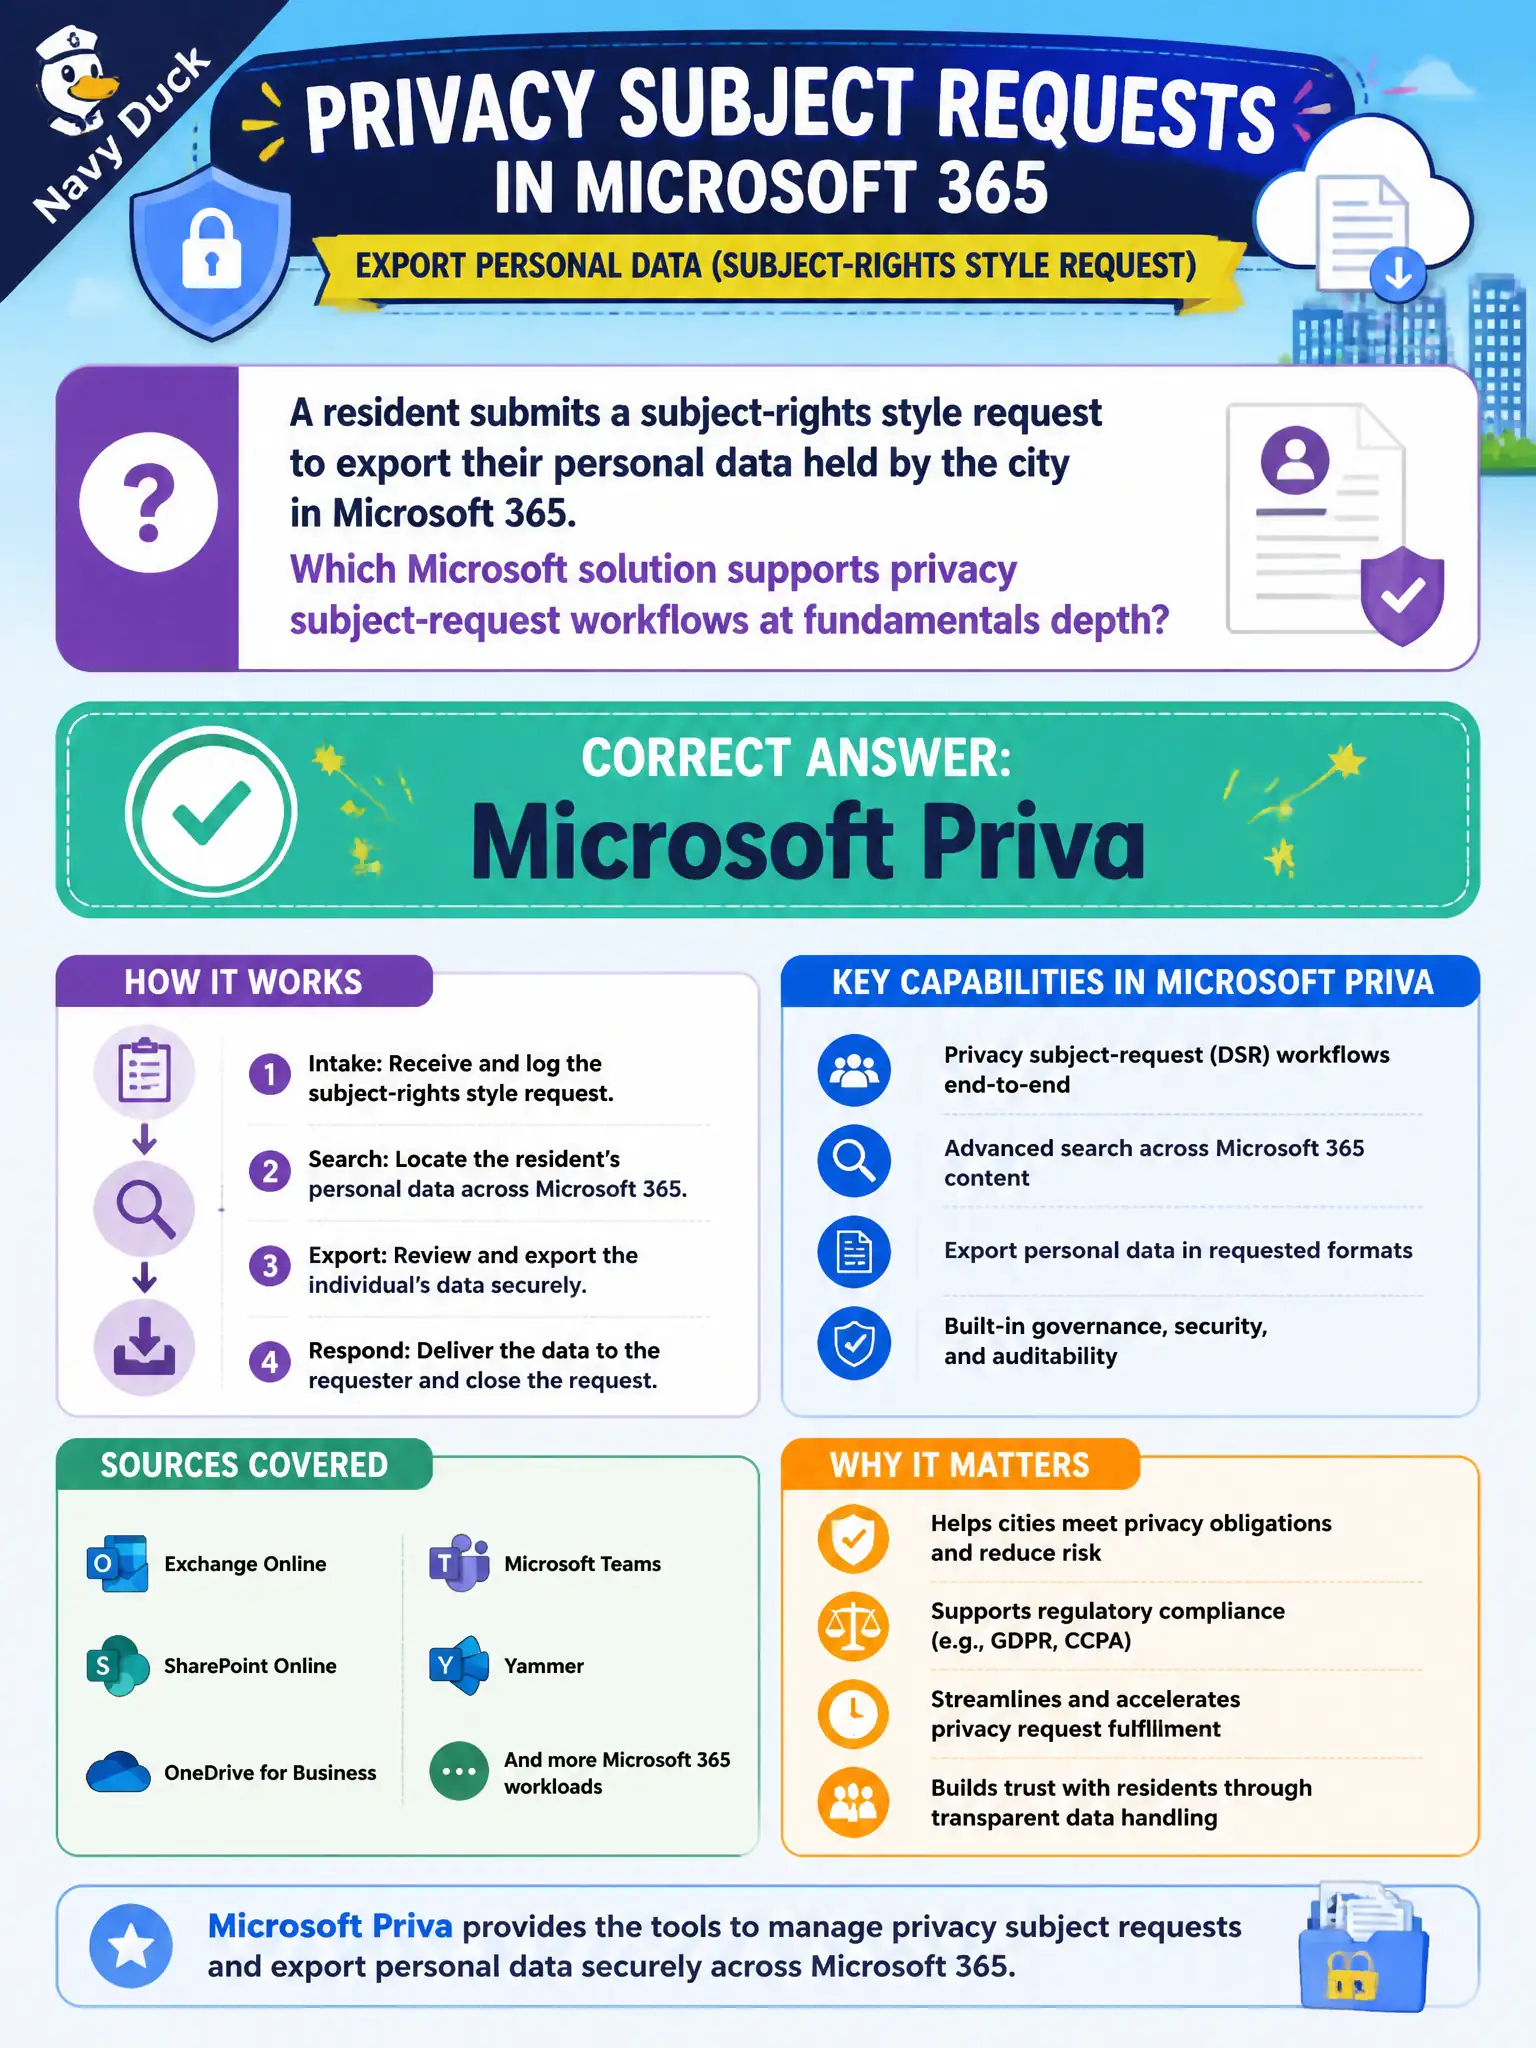
A resident submits a subject-rights style request to export their personal data held by the city in Microsoft 365. Which Microsoft solution supports privacy subject-request workflows at fundamentals depth?
Select an answer to reveal the explanation.
Short Explanation
When someone asks for their personal data export, that is a privacy subject-rights story. Microsoft Priva is the fundamentals answer for those workflows—not a firewall DNAT rule.
Full Explanation
When a resident submits a subject-rights style request to export their personal data held by the city in Microsoft 365, Microsoft Priva supports privacy subject-request workflows at fundamentals depth. That maps citizen access and export style requests to the privacy product rather than to endpoint isolation or network firewall features.
Microsoft Defender for Endpoint device isolation alone contains compromised devices; it does not fulfill privacy export requests. Azure Firewall DNAT rules alone manage network translation and publishing, not privacy subject rights. Windows Autopatch solely manages update deployment and cannot produce a privacy export package for a resident.
Exam caveat: legal may still define verification of the requester identity and lawful scope; Priva provides tooling, not automatic legal approval for every municipal request. Operational check: run a pilot subject-rights request for a test data subject, verify collected Microsoft 365 locations, confirm redaction and review steps with privacy counsel, and measure turnaround against the city’s policy deadlines. In municipal Microsoft 365 fundamentals scenarios, always map the business need to the named capability, reject distractors that describe a different pillar, and verify the control in the admin portal before telling leadership the risk is closed.