
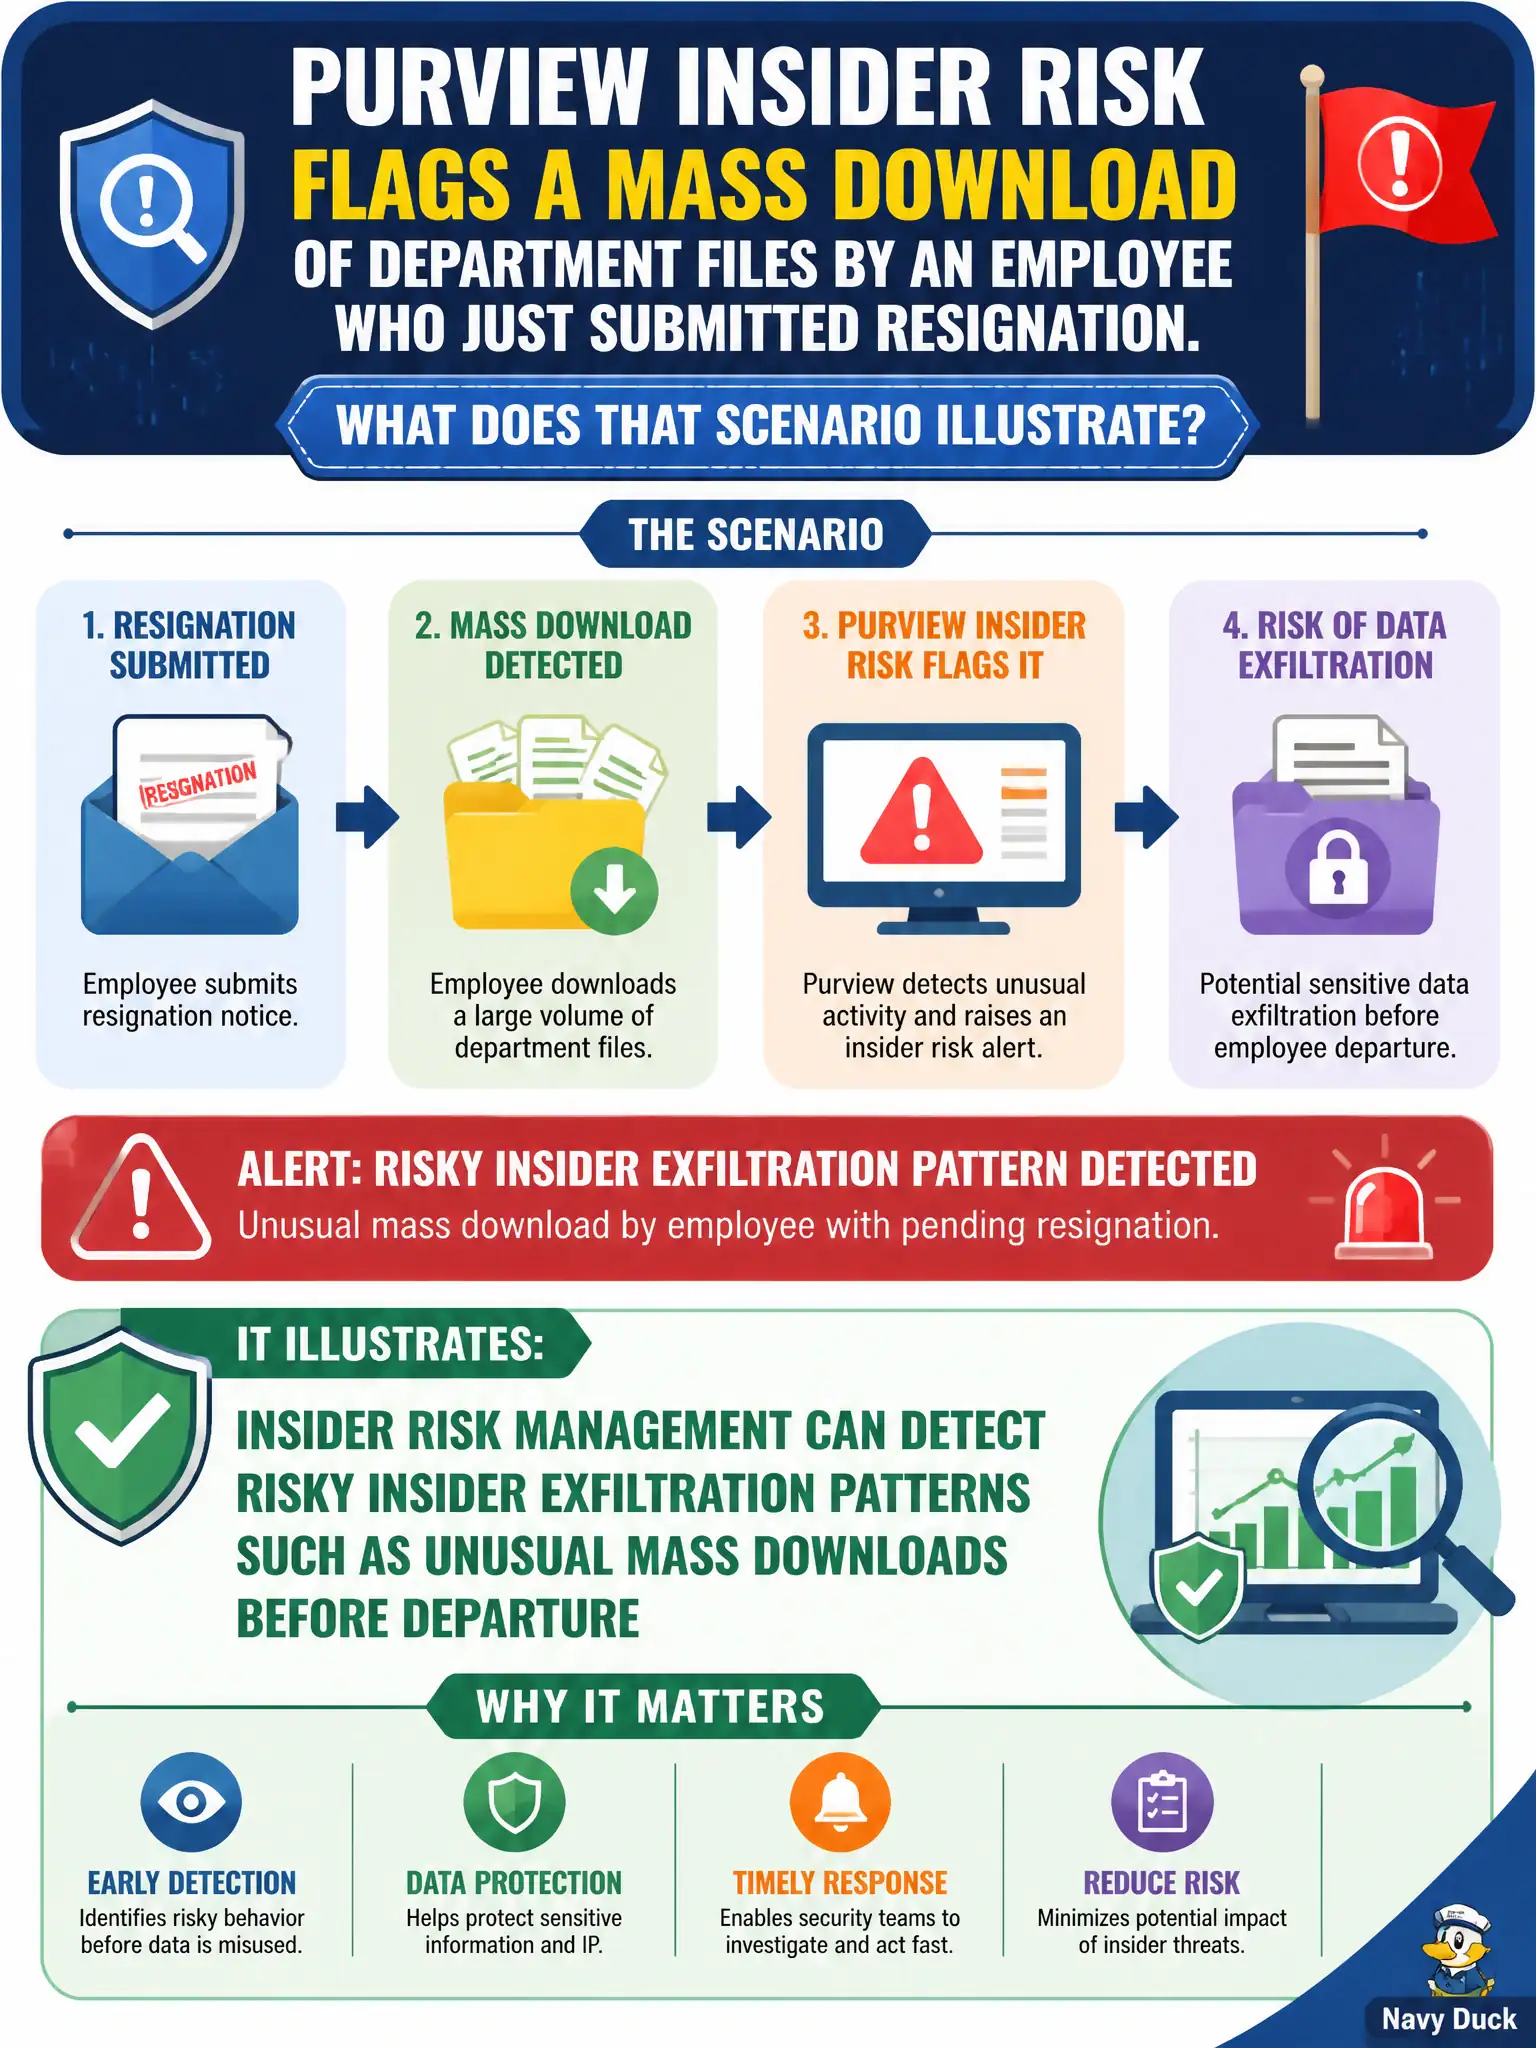
Purview insider risk flags a mass download of department files by an employee who just submitted resignation. What does that scenario illustrate?
Select an answer to reveal the explanation.
Short Explanation
A resignation plus a sudden file vacuum is classic insider-risk storytelling. Purview insider risk looks for those exfiltration-shaped patterns so security and HR can respond.
Full Explanation
Purview insider risk flagging a mass download of department files by an employee who just submitted resignation illustrates that insider risk management can detect risky insider exfiltration patterns—especially unusual bulk access near departure. That scenario is the classic municipal HR and security story MS-900 associates with insider risk capabilities.
Insider risk does not only track cafeteria badge swipes. It is not identical to Autopilot provisioning. Mass download alerts do not prove DLP labels have been deleted permanently; insider risk and DLP are different controls that may both fire for related but distinct reasons during an investigation.
Exam caveat: alerts indicate risk patterns for investigation—they are not automatic proof of malicious intent; HR and legal processes still matter for employment actions. Operational check: review the insider risk alert timeline against HR resignation dates, confirm whether downloads targeted sensitive sites, preserve audit evidence, and coordinate response without tipping off a potentially malicious actor prematurely. For municipal MS-900 scenarios, keep the product-to-purpose mapping explicit so distractors about unrelated UX, networking, or licensing features do not displace the correct compliance or security control.