
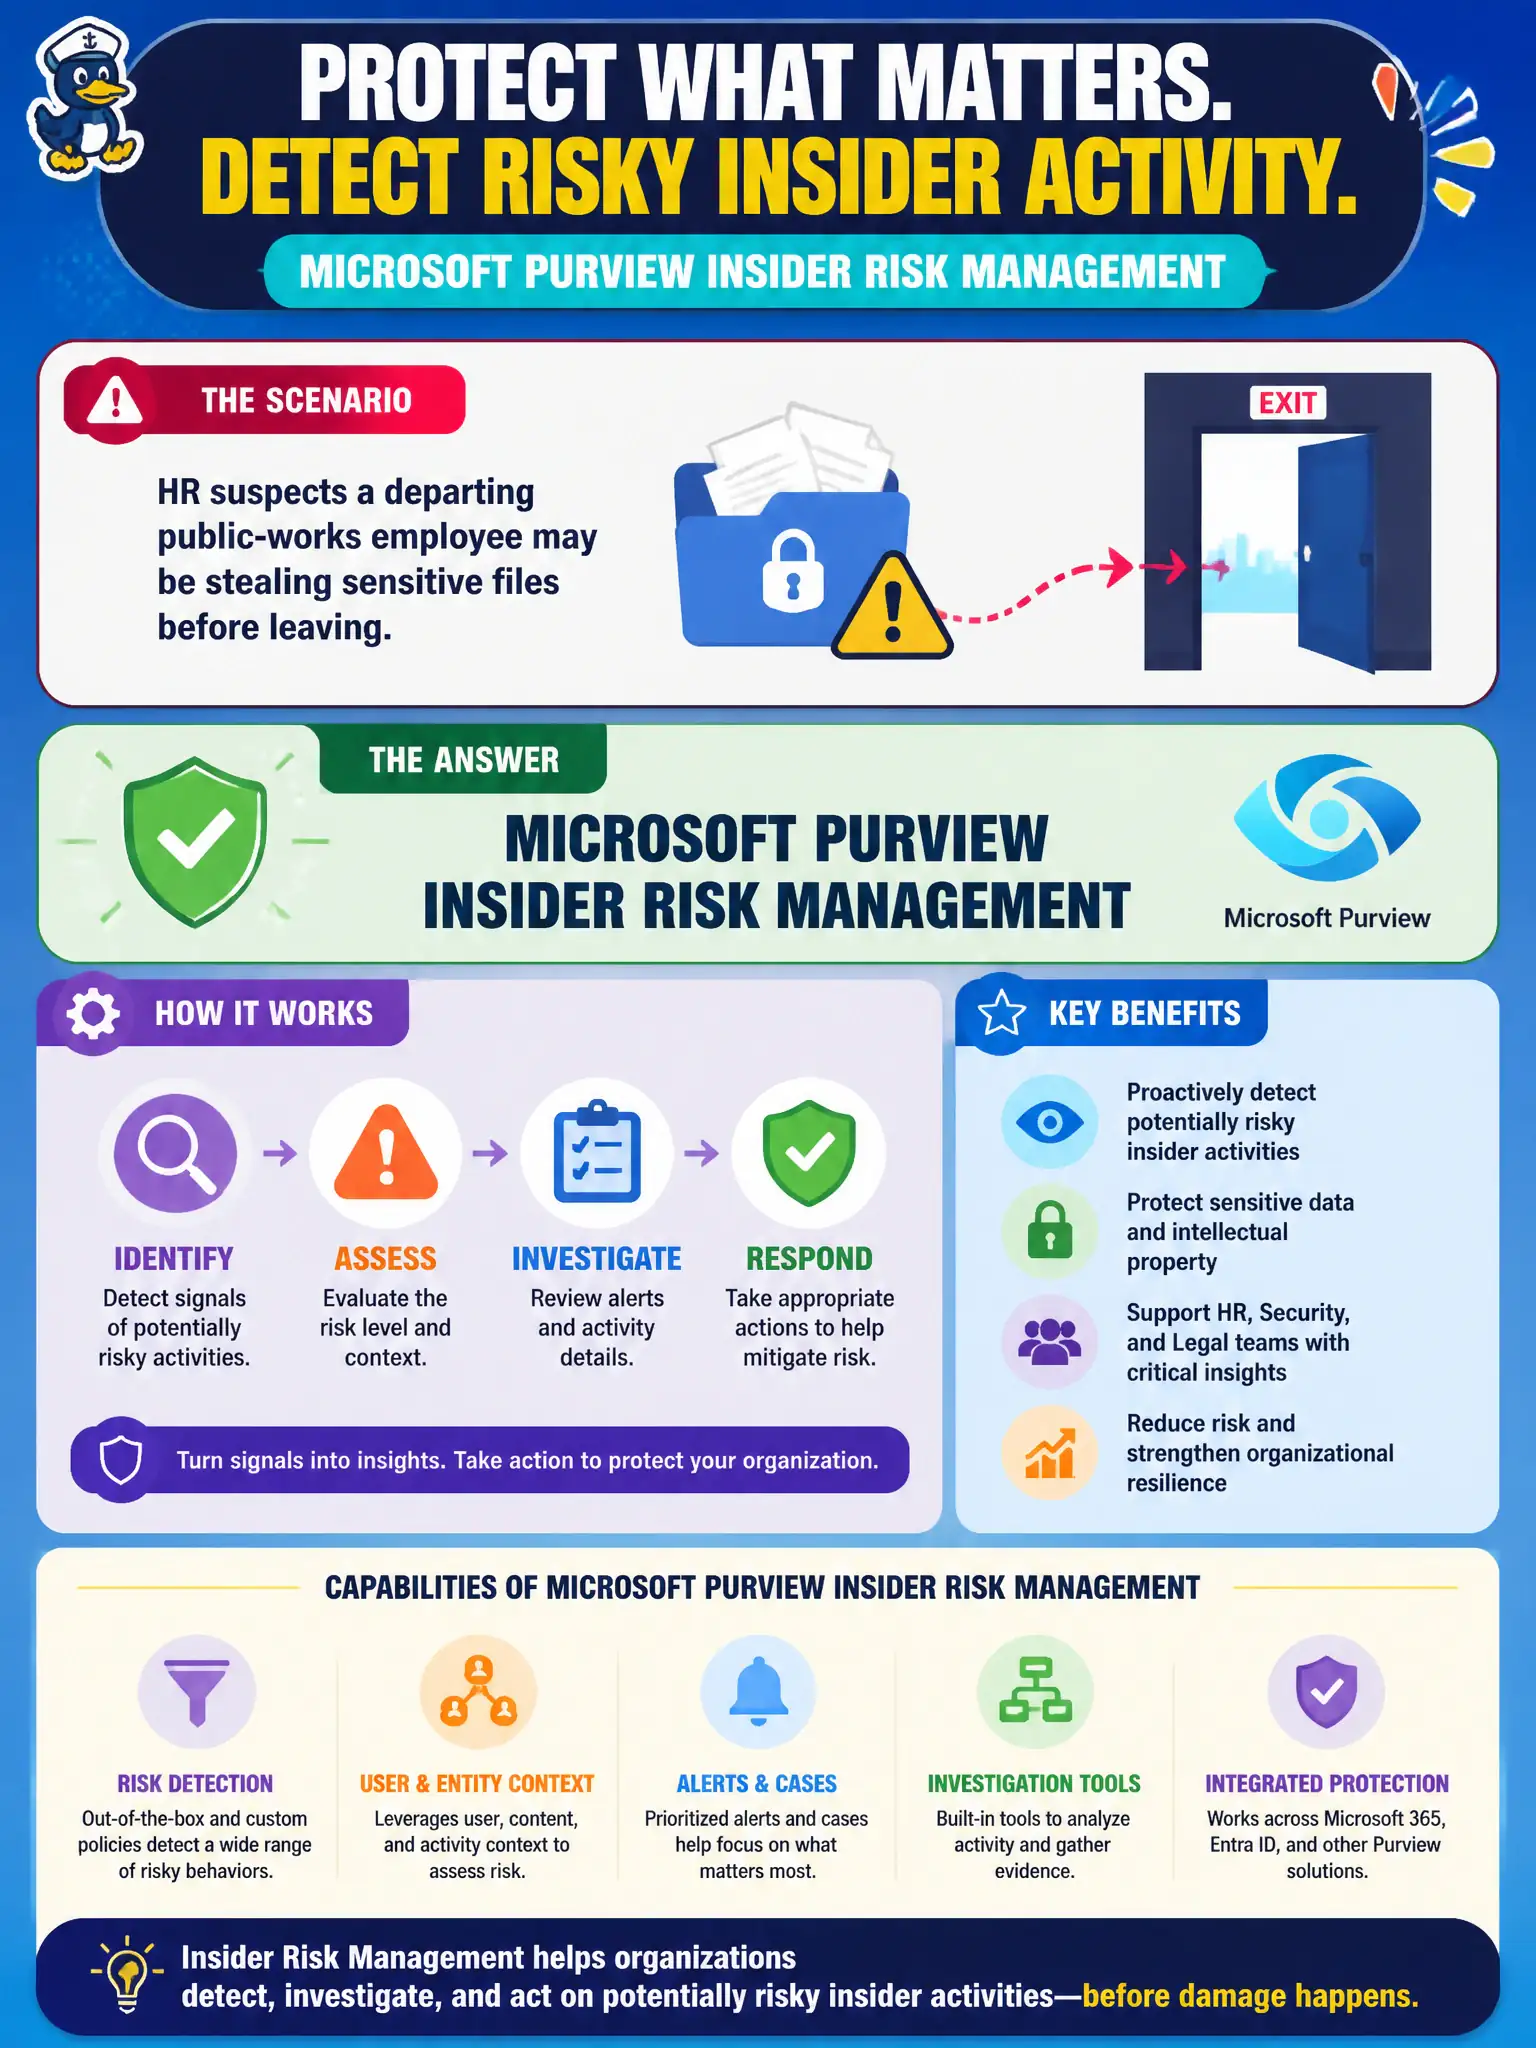
HR suspects a departing public-works employee may be stealing sensitive files before leaving. Which Microsoft Purview capability is designed for potentially risky insider activities?
Select an answer to reveal the explanation.
Short Explanation
When the risk is an insider packing a digital suitcase on the way out, Purview insider risk is the compliance tool to name. It looks for risky people patterns—not Planner colors or dial plans.
Full Explanation
Microsoft Purview insider risk management is designed to help organizations detect and respond to potentially risky insider activities—such as unusual data access or exfiltration patterns around departure—which matches HR’s concern that a departing public-works employee may be stealing sensitive files. At fundamentals depth, associate insider-focused behavioral risk with Purview insider risk rather than with productivity or telephony settings.
Microsoft Planner bucket colors organize tasks and do not detect insider exfiltration. Windows Autopatch rings manage update deployment channels, not insider file theft. Teams Phone dial plans configure voice routing and are unrelated to compliance insider-risk detection for municipal file repositories.
Exam caveat: insider risk management complements DLP and auditing; DLP focuses on sensitive content policies, while insider risk emphasizes user risk patterns—do not treat them as identical on the exam. Operational check: ensure HR and security have a playbook for departure-related alerts, confirm insider risk policies cover relevant indicators for municipal file shares, and review a sample alert workflow without exposing unnecessary employee personal data beyond need-to-know.