
A security engineer needs to implement continuous monitoring for configuration drift in Azure AI security controls. Specifically, the engineer needs to detect when Azure OpenAI resources have their public network access re-enabled after being configured as private-only. Which Azure service provides real-time drift detection and alerting?
Select an answer to reveal the explanation.
Short Explanation
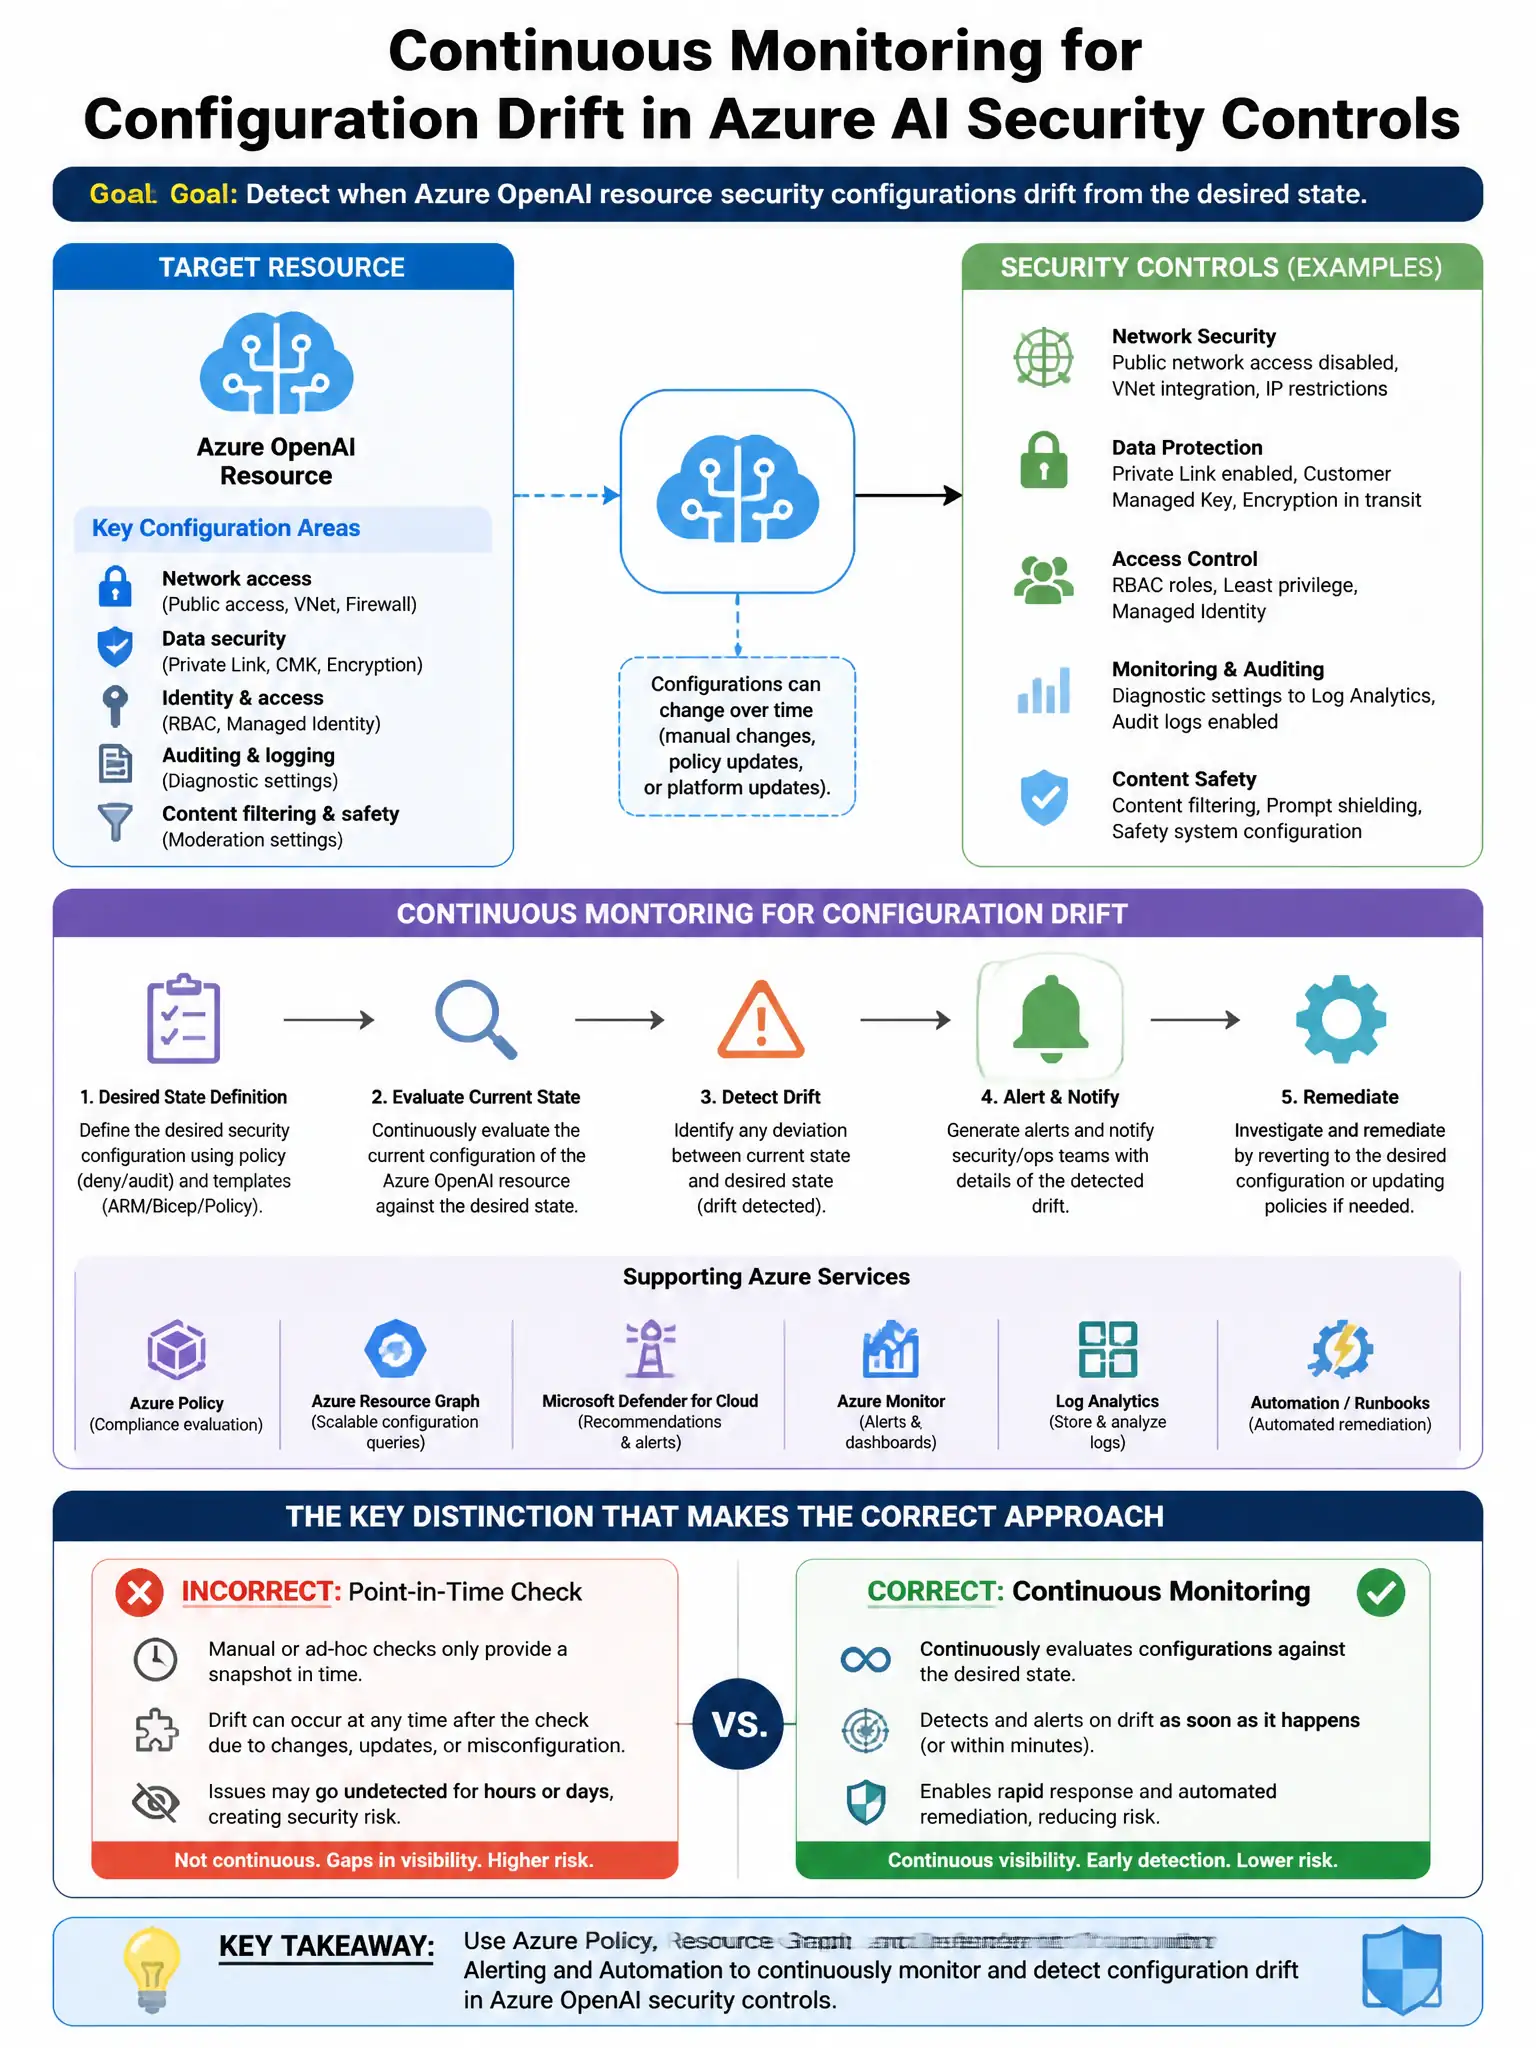
You want near-real-time drift detection, so use Azure Monitor with an activity log alert on write operations where public network access is set to Enabled. That fires when the change happens, not on a delayed scan or scheduled query.
Full Explanation
Azure Monitor with an activity log alert on 'Microsoft.CognitiveServices/accounts/write' operations where publicNetworkAccess is set to Enabled is correct because it can trigger on the specific resource operation and condition when public network access is re-enabled. This provides near-real-time detection, typically within minutes, and alerts the security team immediately when the control is changed. Microsoft Defender for Cloud with an Azure Policy audit rule generating a recommendation when public access is enabled is incorrect because recommendations based on audit rules are evaluated periodically, not in real time, and may take hours to reflect a change. Microsoft Sentinel with a scheduled analytics rule querying AzureActivity for Azure OpenAI configuration changes is incorrect because scheduled analytics rules run on a defined interval, with a minimum of five minutes, so they detect the change with higher latency than an Azure Monitor activity log alert that fires on the event itself. Azure Policy with a deny effect preventing public network access re-enablement on Azure OpenAI resources is incorrect because a deny effect prevents the change from occurring, which is a preventive control, while the question asks for drift detection and alerting rather than prevention.