
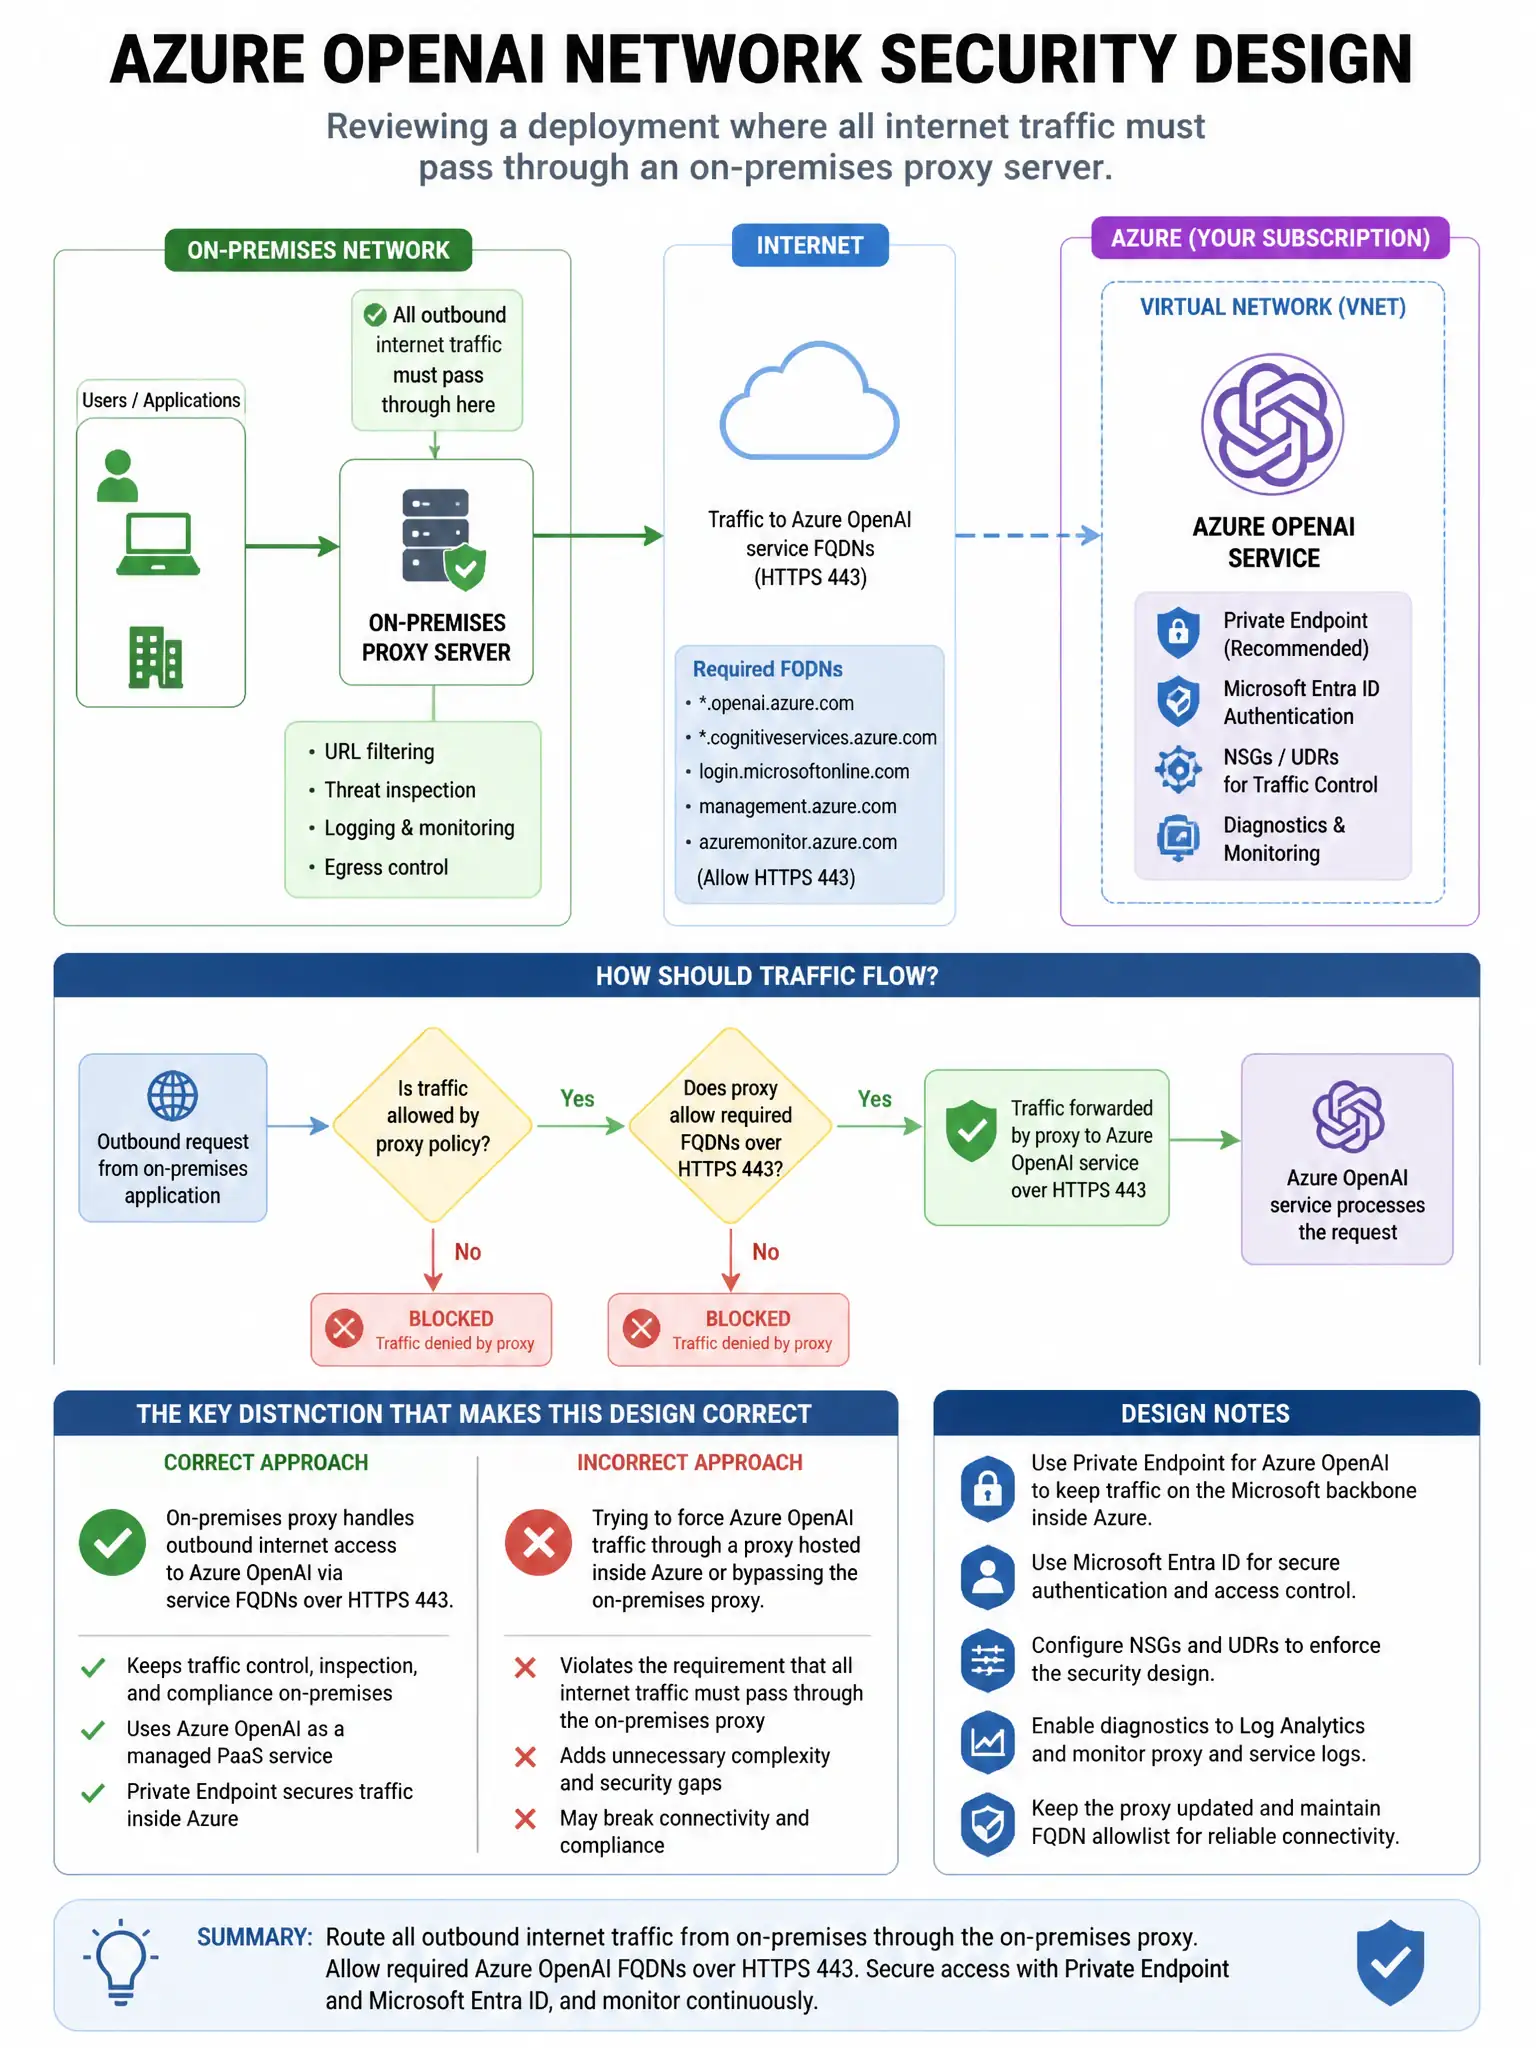
A security architect is reviewing the network security design for an Azure OpenAI deployment. The organization has an on-premises proxy server that all internet traffic must pass through for inspection. The AI application running on Azure App Service needs to call Azure OpenAI via the private endpoint. How should the network route be configured?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you want App Service regional VNet Integration so the app can reach the Azure OpenAI private endpoint directly inside Azure's network, while a UDR sends only internet-bound traffic to the on-premises proxy through ExpressRoute. That keeps inspection where it's needed without dragging Azure service traffic through on-prem.
Full Explanation
The correct configuration uses App Service regional VNet Integration with a private endpoint for Azure OpenAI and a User Defined Route that sends only internet-bound traffic to the on-premises proxy via ExpressRoute, while Azure service traffic uses the private endpoint directly. This lets the App Service reach the Azure OpenAI private endpoint within Azure's network, bypassing the internet and the on-premises proxy for that specific traffic, while still providing security inspection for internet traffic without routing internal Azure service traffic unnecessarily through on-premises. The option that configures App Service VNet Integration and routes Azure OpenAI traffic through a private endpoint in the integrated VNet while bypassing the on-premises proxy is incomplete because it does not clarify that only Azure private traffic uses that path; internet traffic still needs to pass through the proxy. The option that configures App Service to use the on-premises proxy for all outbound traffic, including Azure OpenAI calls routed through ExpressRoute, is incorrect because it adds significant latency, creates a potential bottleneck, and defeats the purpose of private endpoints. The option that deploys Azure API Management between App Service and Azure OpenAI to inspect traffic without the on-premises proxy is incorrect because it adds another service component and does not replace the requirement for proper network routing.