
A security engineer configures Microsoft Defender for Cloud Defender for AI plan. After enabling it, alerts appear for 'Jailbreak attempt detected on Azure OpenAI endpoint.' Which underlying technology enables this detection?
Select an answer to reveal the explanation.
Short Explanation
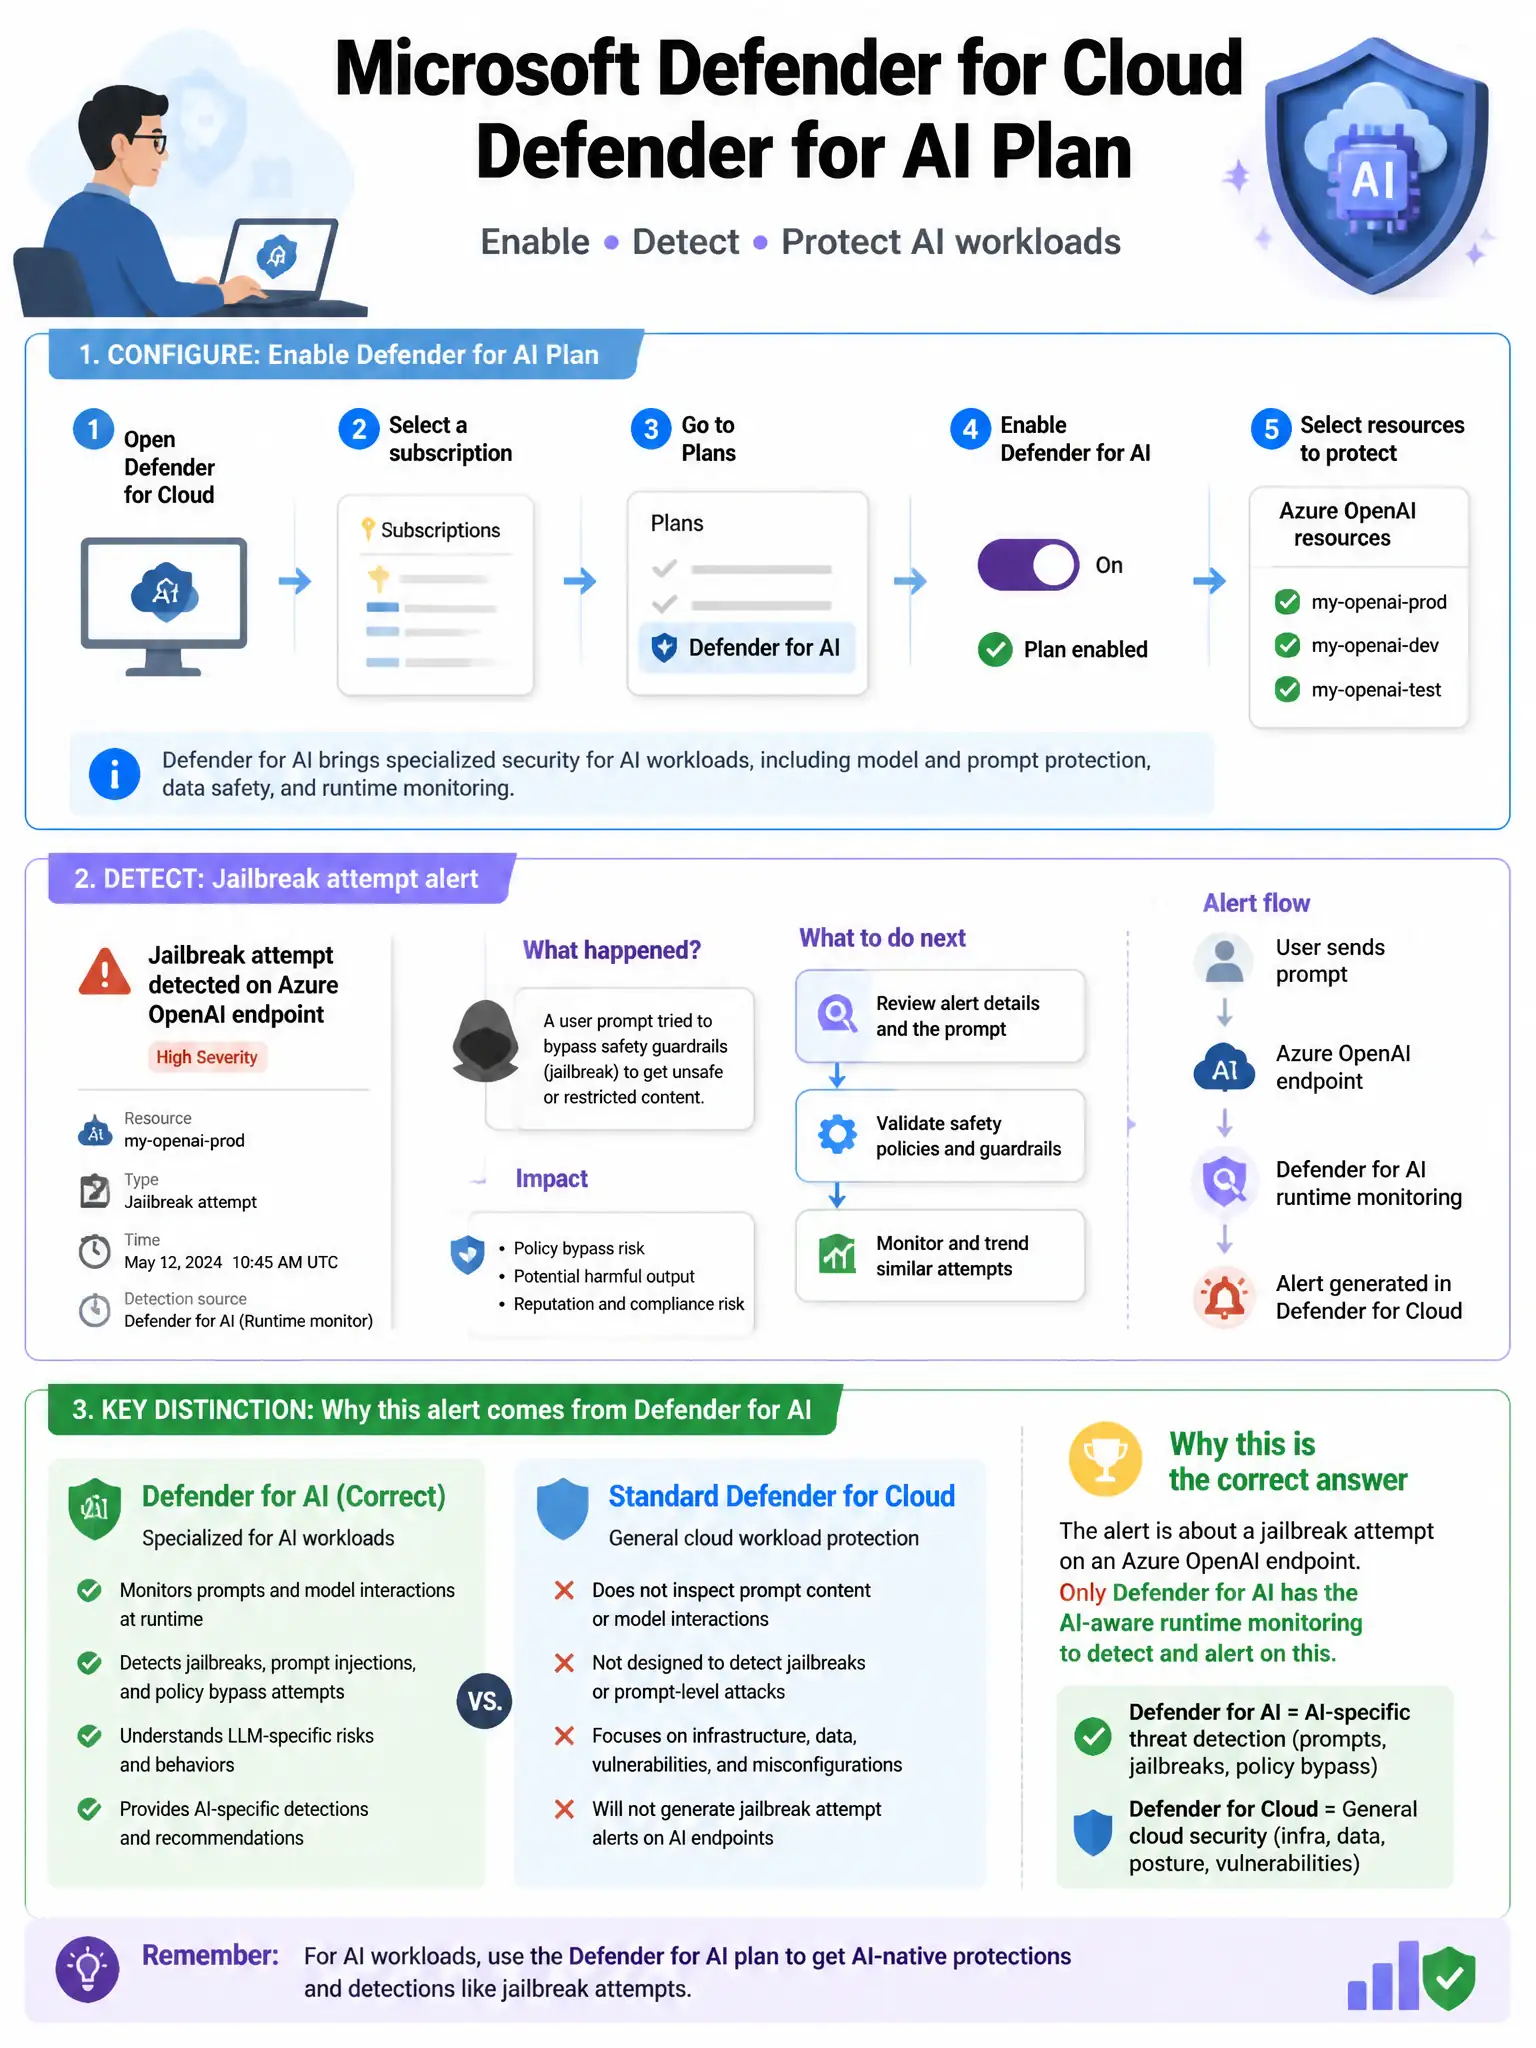
Here's the deal — you get that alert because Defender for AI uses Azure AI Content Safety Prompt Shield to inspect prompts for jailbreak patterns, then Defender for Cloud surfaces it as a security alert.
Full Explanation
The correct answer is the Azure AI Content Safety Prompt Shield integrated with Defender for AI threat detection pipeline option. Microsoft Defender for AI's jailbreak detection capability is powered by Azure AI Content Safety Prompt Shield, which analyzes prompts in real time for jailbreak patterns. Defender for AI integrates with this detection pipeline to surface jailbreak attempts as security alerts in Defender for Cloud. The Azure OpenAI content filtering configured with jailbreak category enabled option is incorrect because Azure OpenAI's built-in content filtering blocks harmful content in responses, but the Defender for Cloud alert specifically leverages Prompt Shield integration. The Microsoft Defender for Cloud agent installed on the Azure OpenAI compute nodes option is incorrect because Defender for AI for Azure OpenAI does not require an agent on compute nodes; it monitors API-level interactions through the service plane. The Microsoft Sentinel anomaly detection rule correlating token usage patterns option is incorrect because Sentinel anomaly detection rules are in the SIEM layer and are not the underlying detection mechanism for Defender for Cloud alerts.