
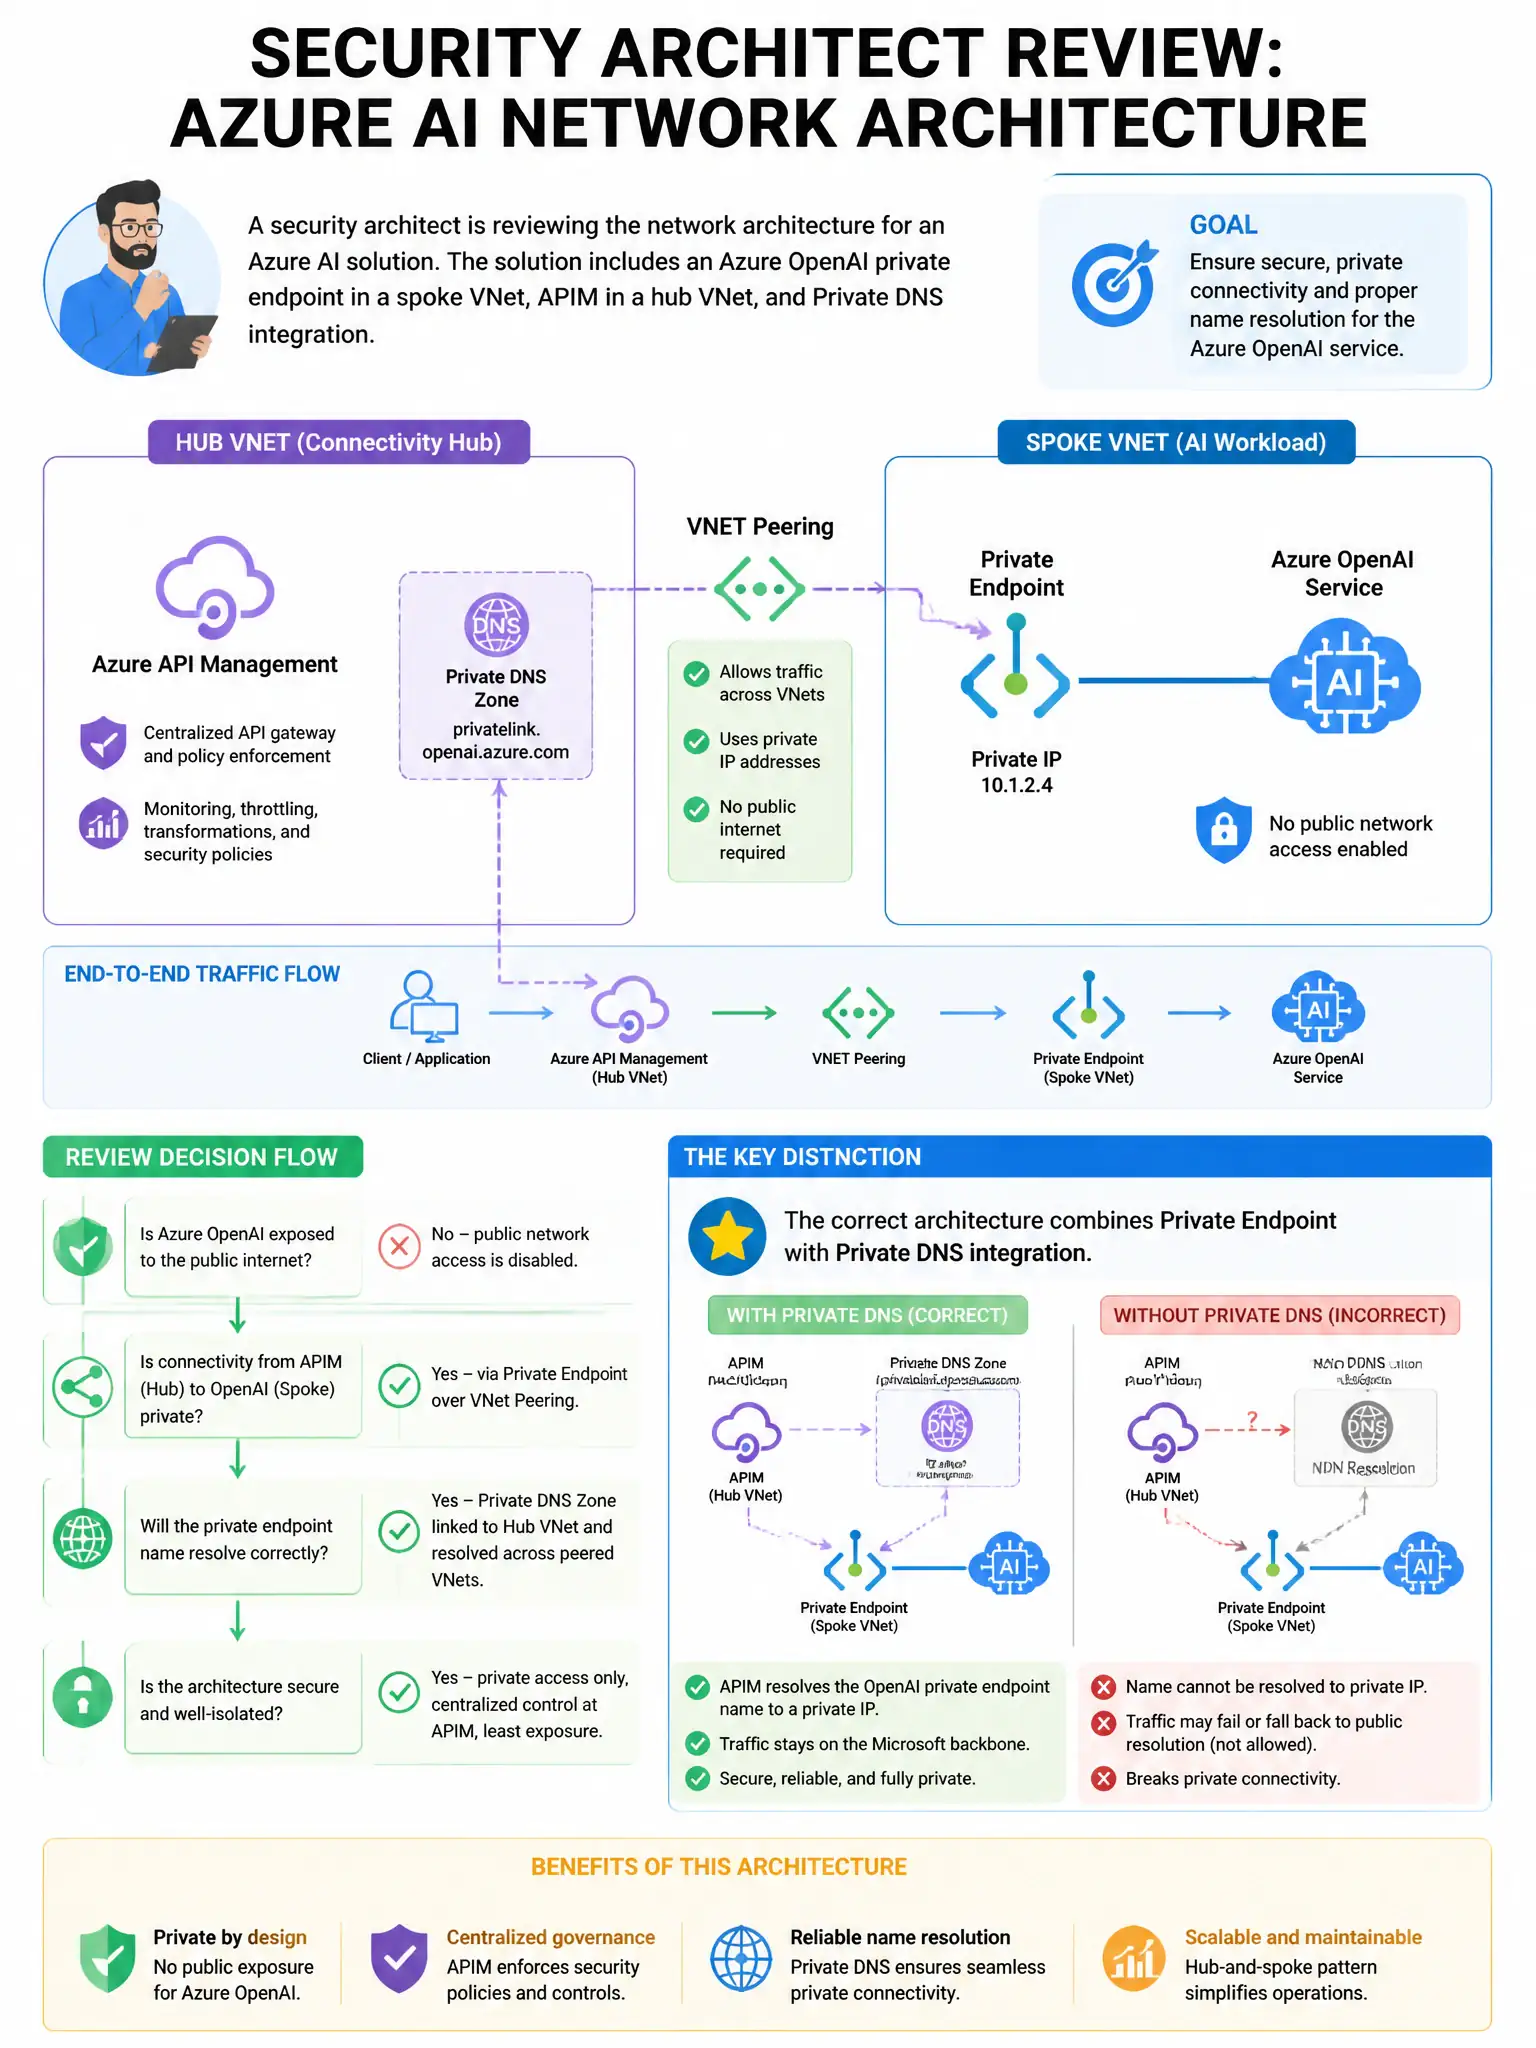
A security architect is reviewing the network architecture for an Azure AI solution. The solution includes an Azure OpenAI private endpoint in a spoke VNet, APIM in a hub VNet, and on-premises clients connected via ExpressRoute. The security team requires that DNS resolution for the Azure OpenAI private endpoint works correctly for on-premises clients. What DNS configuration is required?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need a private DNS zone for privatelink.openai.azure.com linked to the hub VNet, and you need on-prem DNS to forward those queries to Azure DNS. That gives on-prem clients the private endpoint IP without relying on public DNS.
Full Explanation
The required configuration is to create an Azure Private DNS Zone for privatelink.openai.azure.com linked to the hub VNet, and configure on-premises DNS forwarders to forward privatelink.openai.azure.com queries to Azure DNS resolver. For on-premises clients to resolve Azure Private DNS Zones like privatelink.openai.azure.com, the Azure Private DNS Zone must be linked to a VNet reachable from the ExpressRoute path. On-premises DNS servers must be configured to conditionally forward queries for the privatelink.openai.azure.com zone to Azure DNS via a DNS resolver or forwarder VM in Azure, enabling private endpoint IP resolution. The hosts-file approach is incorrect because hosts file entries are not scalable and do not update automatically if the private endpoint IP changes. The spoke-VNet DNS Private Resolver approach is incorrect because the DNS Private Resolver in the spoke VNet forwards Azure DNS queries to on-premises, not enabling on-premises clients to resolve Azure private DNS zones. The auto-registration approach is incorrect because auto-registration registers VM hostnames in private DNS zones, not privatelink DNS zone records for private endpoints.