
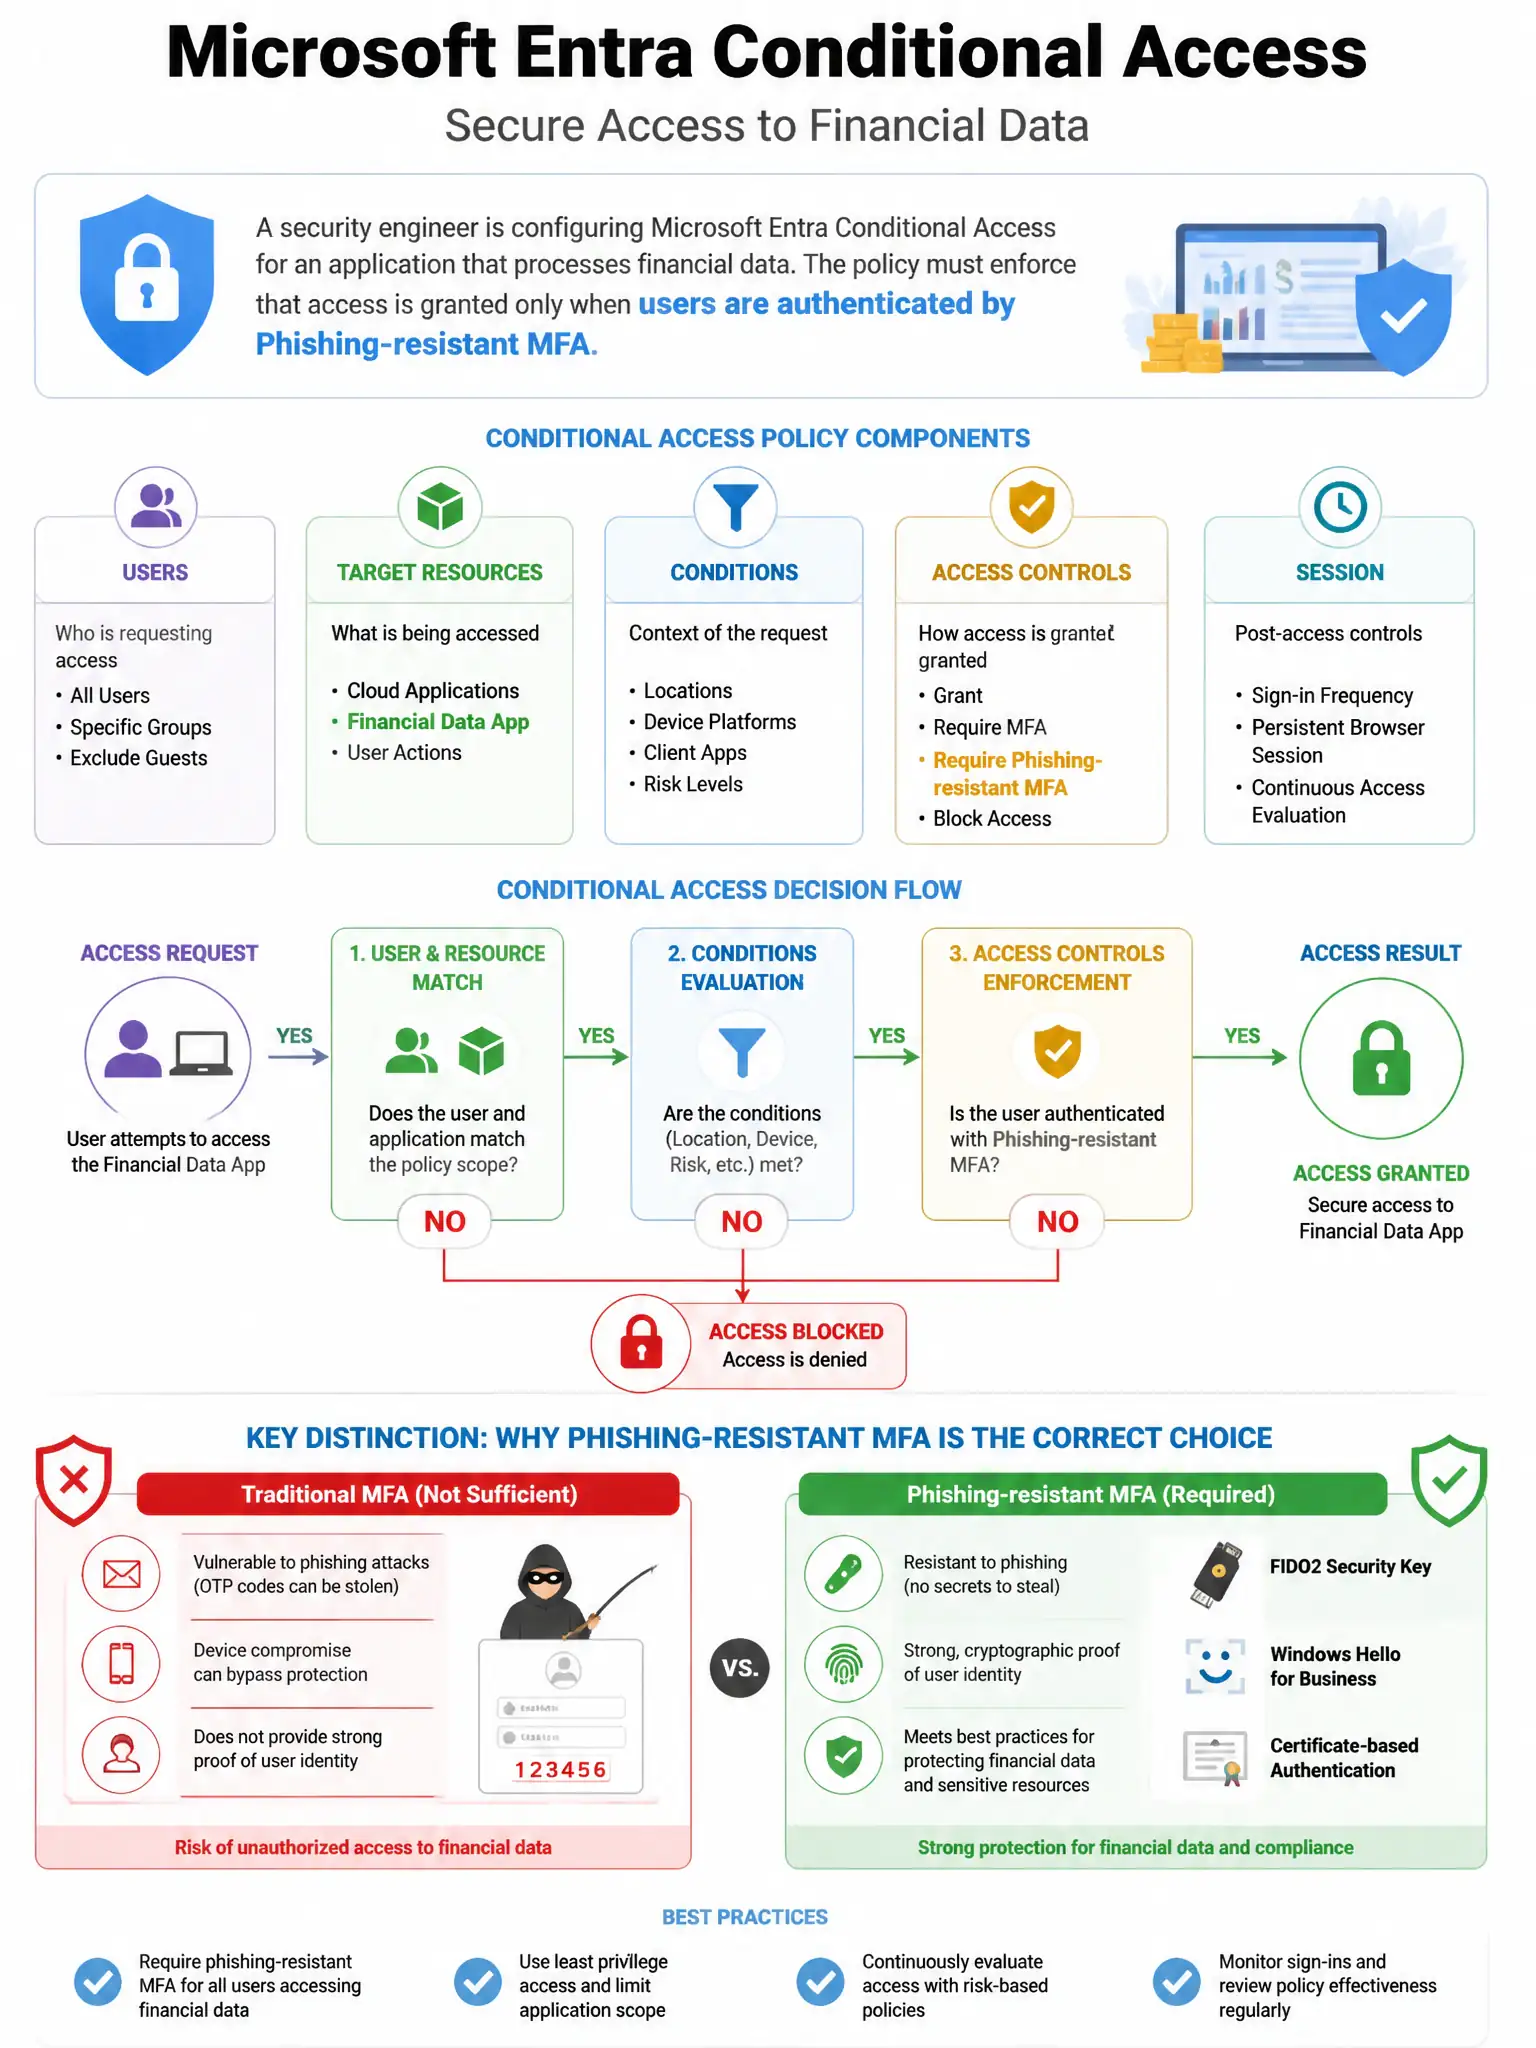
A security engineer is configuring Microsoft Entra Conditional Access for an application that processes financial data. The policy must enforce that access is granted only when users are on compliant devices AND connecting from a named location AND have low sign-in risk. What grant controls and conditions must be set?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need to require a compliant device, include only trusted named locations, and allow only low sign-in risk. That makes all three conditions true at once.
Full Explanation
Set the grant control to require a compliant device, set Conditions > Locations to include only trusted named locations, and set Conditions > Sign-in risk to Low only. This makes all three required conditions true simultaneously: compliant device, trusted named location, and low sign-in risk. The configuration that requires a compliant device, includes named locations generally, and allows low sign-in risk and above is incorrect because named locations without the trusted qualifier could include all named locations, and low and above permits more than low sign-in risk. The configuration that requires a compliant device and MFA, includes named locations, and allows medium and below sign-in risk is incorrect because MFA adds a condition not required, and medium risk exceeds the low-risk requirement. The configuration that requires a compliant device, excludes all named locations except trusted, and allows low sign-in risk only is incorrect because excluding all except trusted is functionally similar, but including trusted named locations more accurately reflects the Conditional Access interface.