
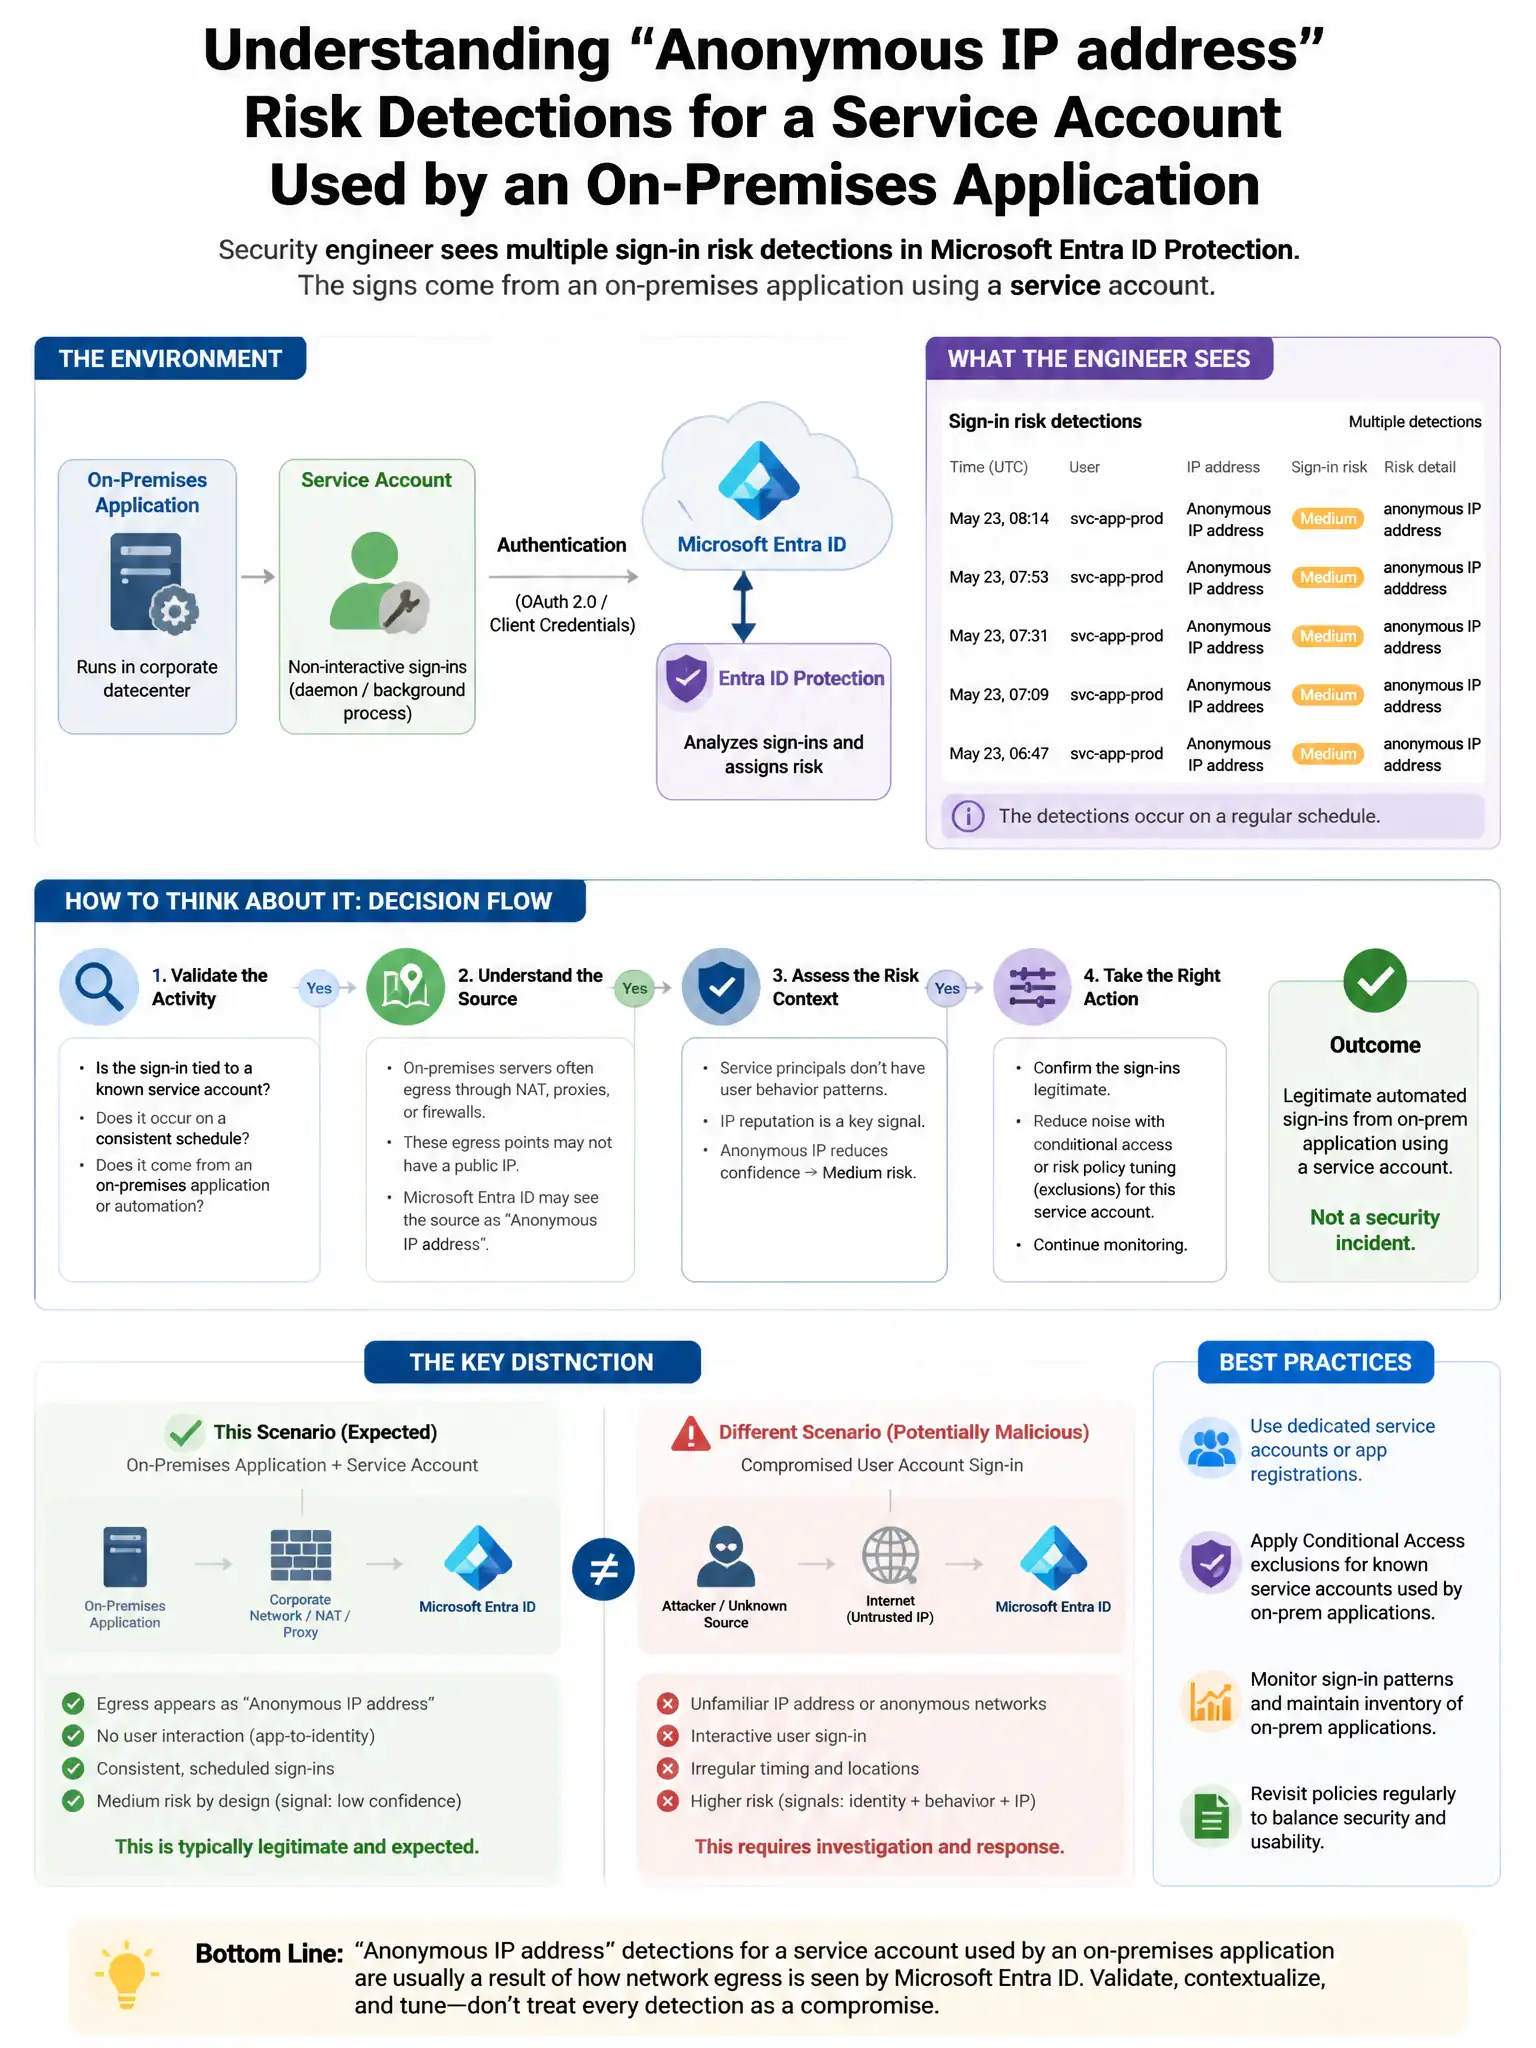
A security engineer reviews Microsoft Entra ID Protection and sees multiple 'Anonymous IP address' sign-in risk detections for a service account used by an on-premises application for API calls. What is the most likely cause and appropriate remediation?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — if a service account keeps hitting Anonymous IP address detections, the app's outbound IP is probably flagged as anonymous in Microsoft threat intelligence. Add that legitimate IP to a named location so Entra ID treats it as trusted and stops the false positive.
Full Explanation
The correct answer is the option stating that the on-premises application's network egress uses an IP address flagged as anonymous by Microsoft threat intelligence and that the IP should be added to named locations. 'Anonymous IP address' detections on service accounts often indicate that the application's outbound IP is categorized as anonymous, such as a VPN, proxy, or hosting provider, in Microsoft's threat intelligence. Adding the legitimate IP to a named location in Entra ID marks it as trusted and prevents false positive risk detections. The option saying the service account is compromised and should be blocked and rotated is incorrect because service accounts with consistent anonymous IP detections from a single source are more likely a false positive from network egress configuration. The option blaming the Entra Connect sync agent is incorrect because Entra Connect sync agents would not cause IP-based risk detections on a separate service account. The option about missing MFA registration is incorrect because service accounts typically cannot complete MFA and the detection is not related to MFA registration.