
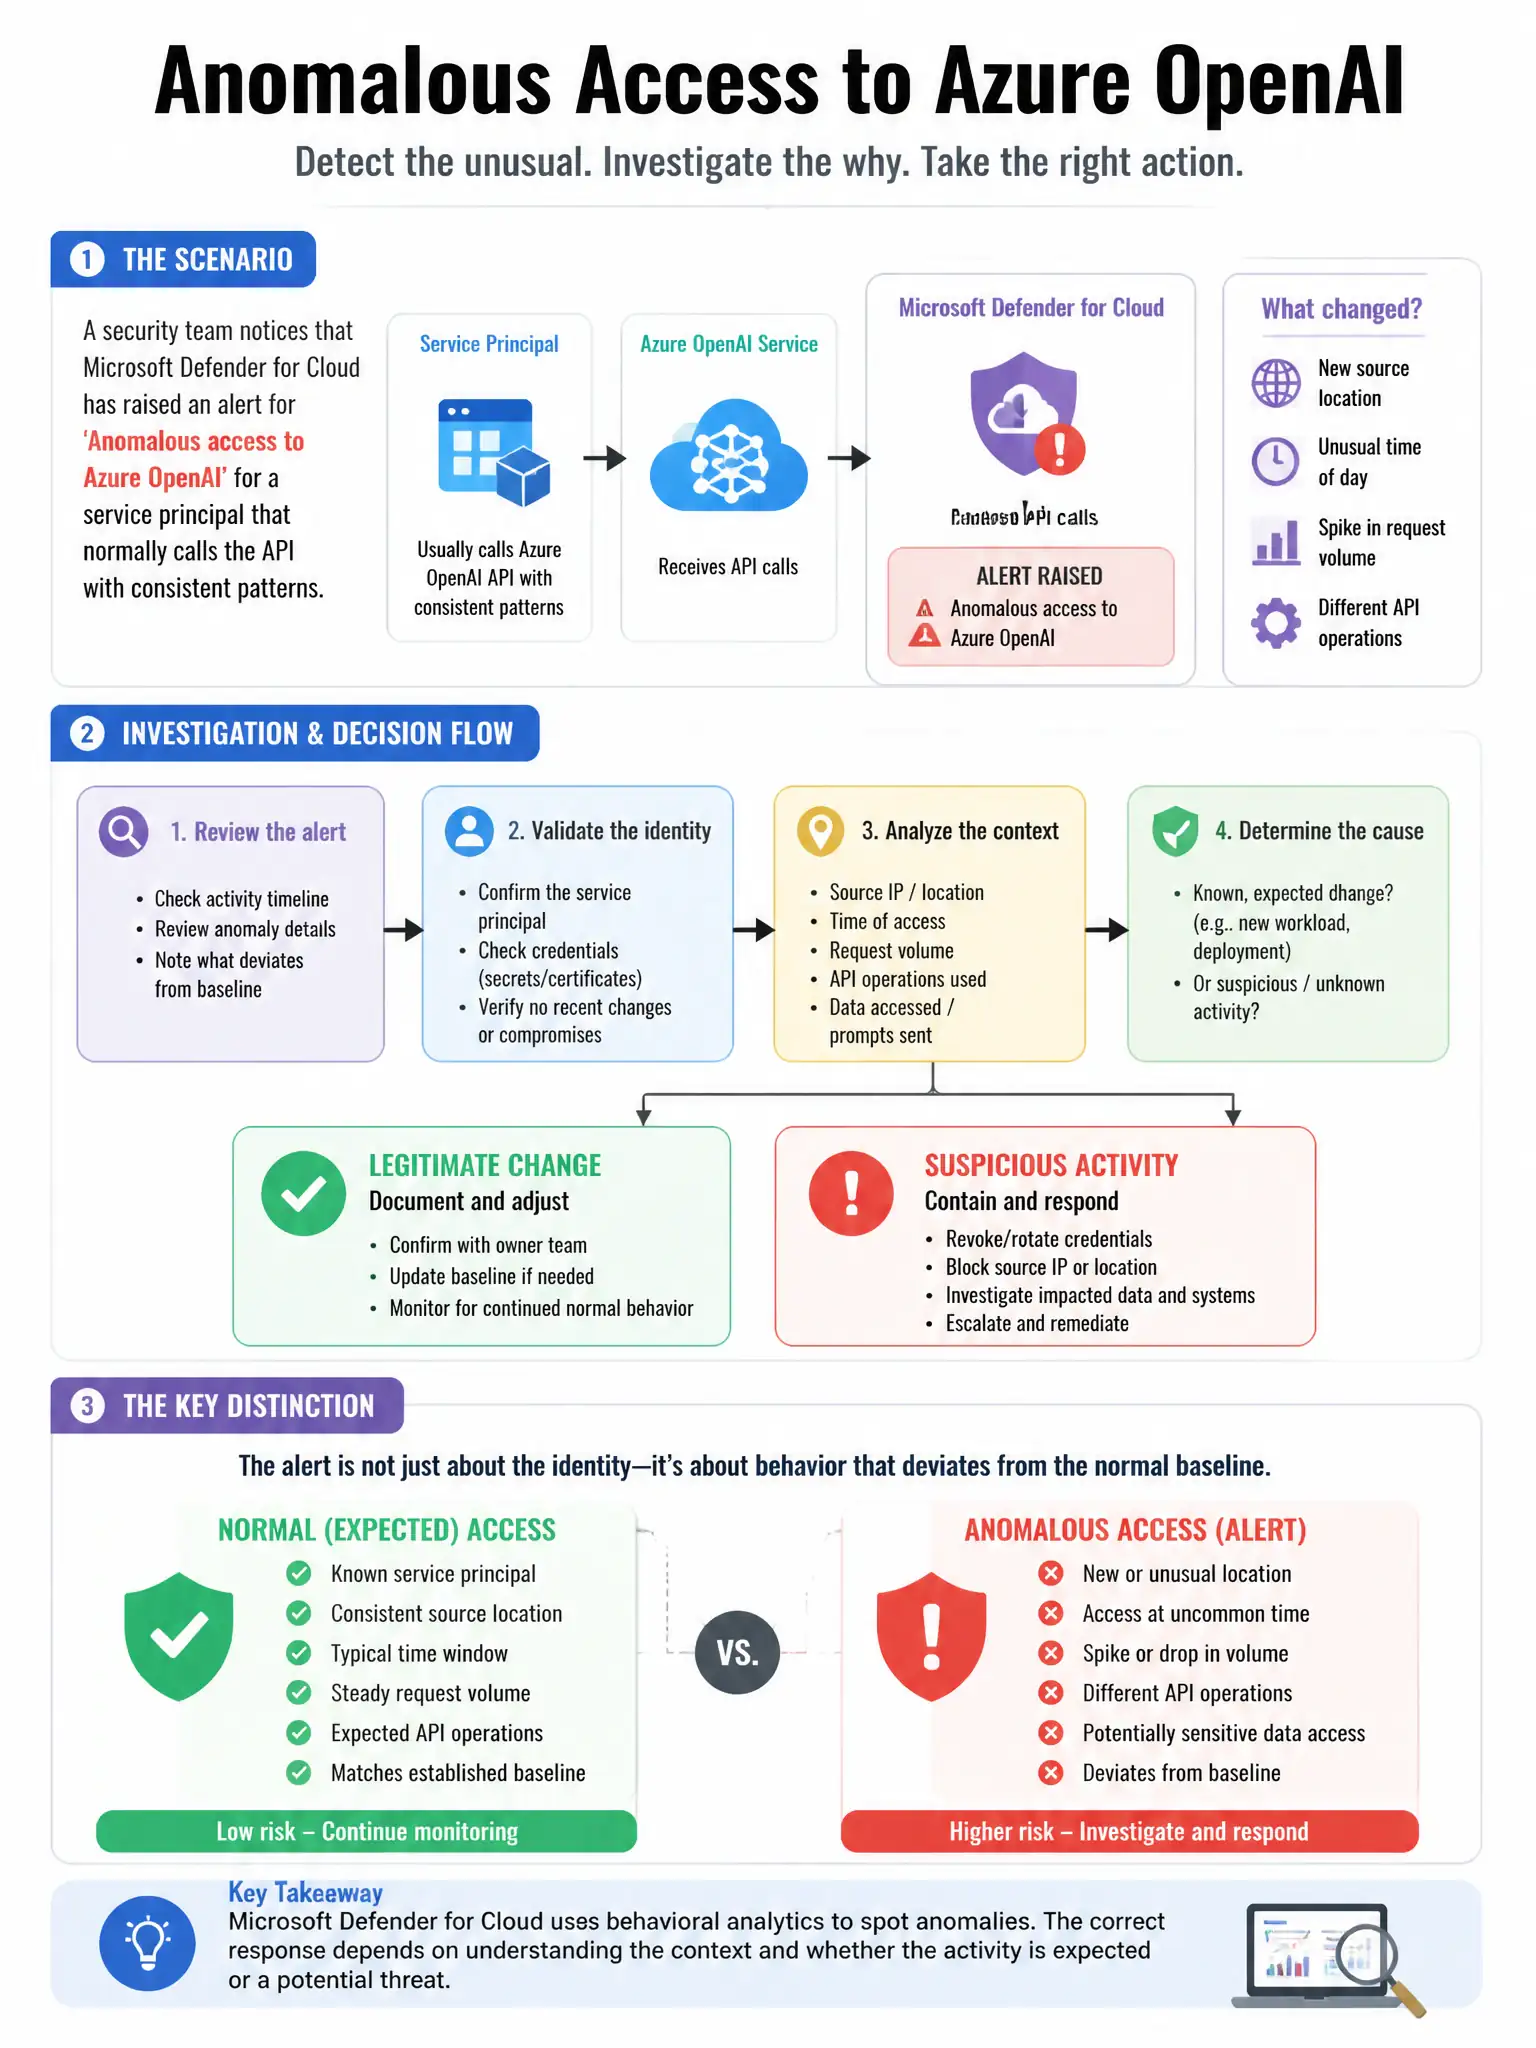
A security team notices that Microsoft Defender for Cloud has raised an alert for 'Anomalous access to Azure OpenAI' for a service principal that normally calls the API with consistent token counts between 500-1,000 per hour but suddenly made 50,000 calls in one hour. The team needs to determine whether this is a legitimate batch job or an attack. Which initial investigation step uses Microsoft Security Copilot most effectively?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — ask Security Copilot to summarize the alert and show the service principal's recent activity, associated risk detections, and whether the source IP is flagged in threat intelligence. That one prompt lets Copilot correlate Defender for Cloud, Sentinel, Entra ID, and threat intelligence at once, so you triage faster.
Full Explanation
The correct initial investigation step is to ask Security Copilot to summarize the alert and show the service principal's recent activity, any associated risk detections, and whether the IP used is flagged in threat intelligence. This works because Microsoft Security Copilot excels at multi-step investigation through natural language prompting. One prompt asking Copilot to summarize the alert, retrieve the service principal's recent activity, surface any associated risk detections from Entra ID Protection, and check the source IP against threat intelligence leverages Copilot's ability to query multiple data sources (Defender for Cloud, Sentinel, Entra ID, and Microsoft Defender Threat Intelligence) simultaneously and synthesize a coherent investigation summary, dramatically accelerating triage. Manually searching the Azure portal activity logs for the service principal is wrong because it is time-consuming, siloed to one data source, and misses the cross-platform correlation that Security Copilot provides. Running a PowerShell script to query Entra ID for the service principal details is wrong because it provides raw data but not the synthesized, correlated analysis that Security Copilot delivers for multi-source investigation. Opening a new Sentinel incident and assigning it to the AI security analyst is wrong because creating a Sentinel incident is a response action, not an investigation step; investigation should precede escalation.