
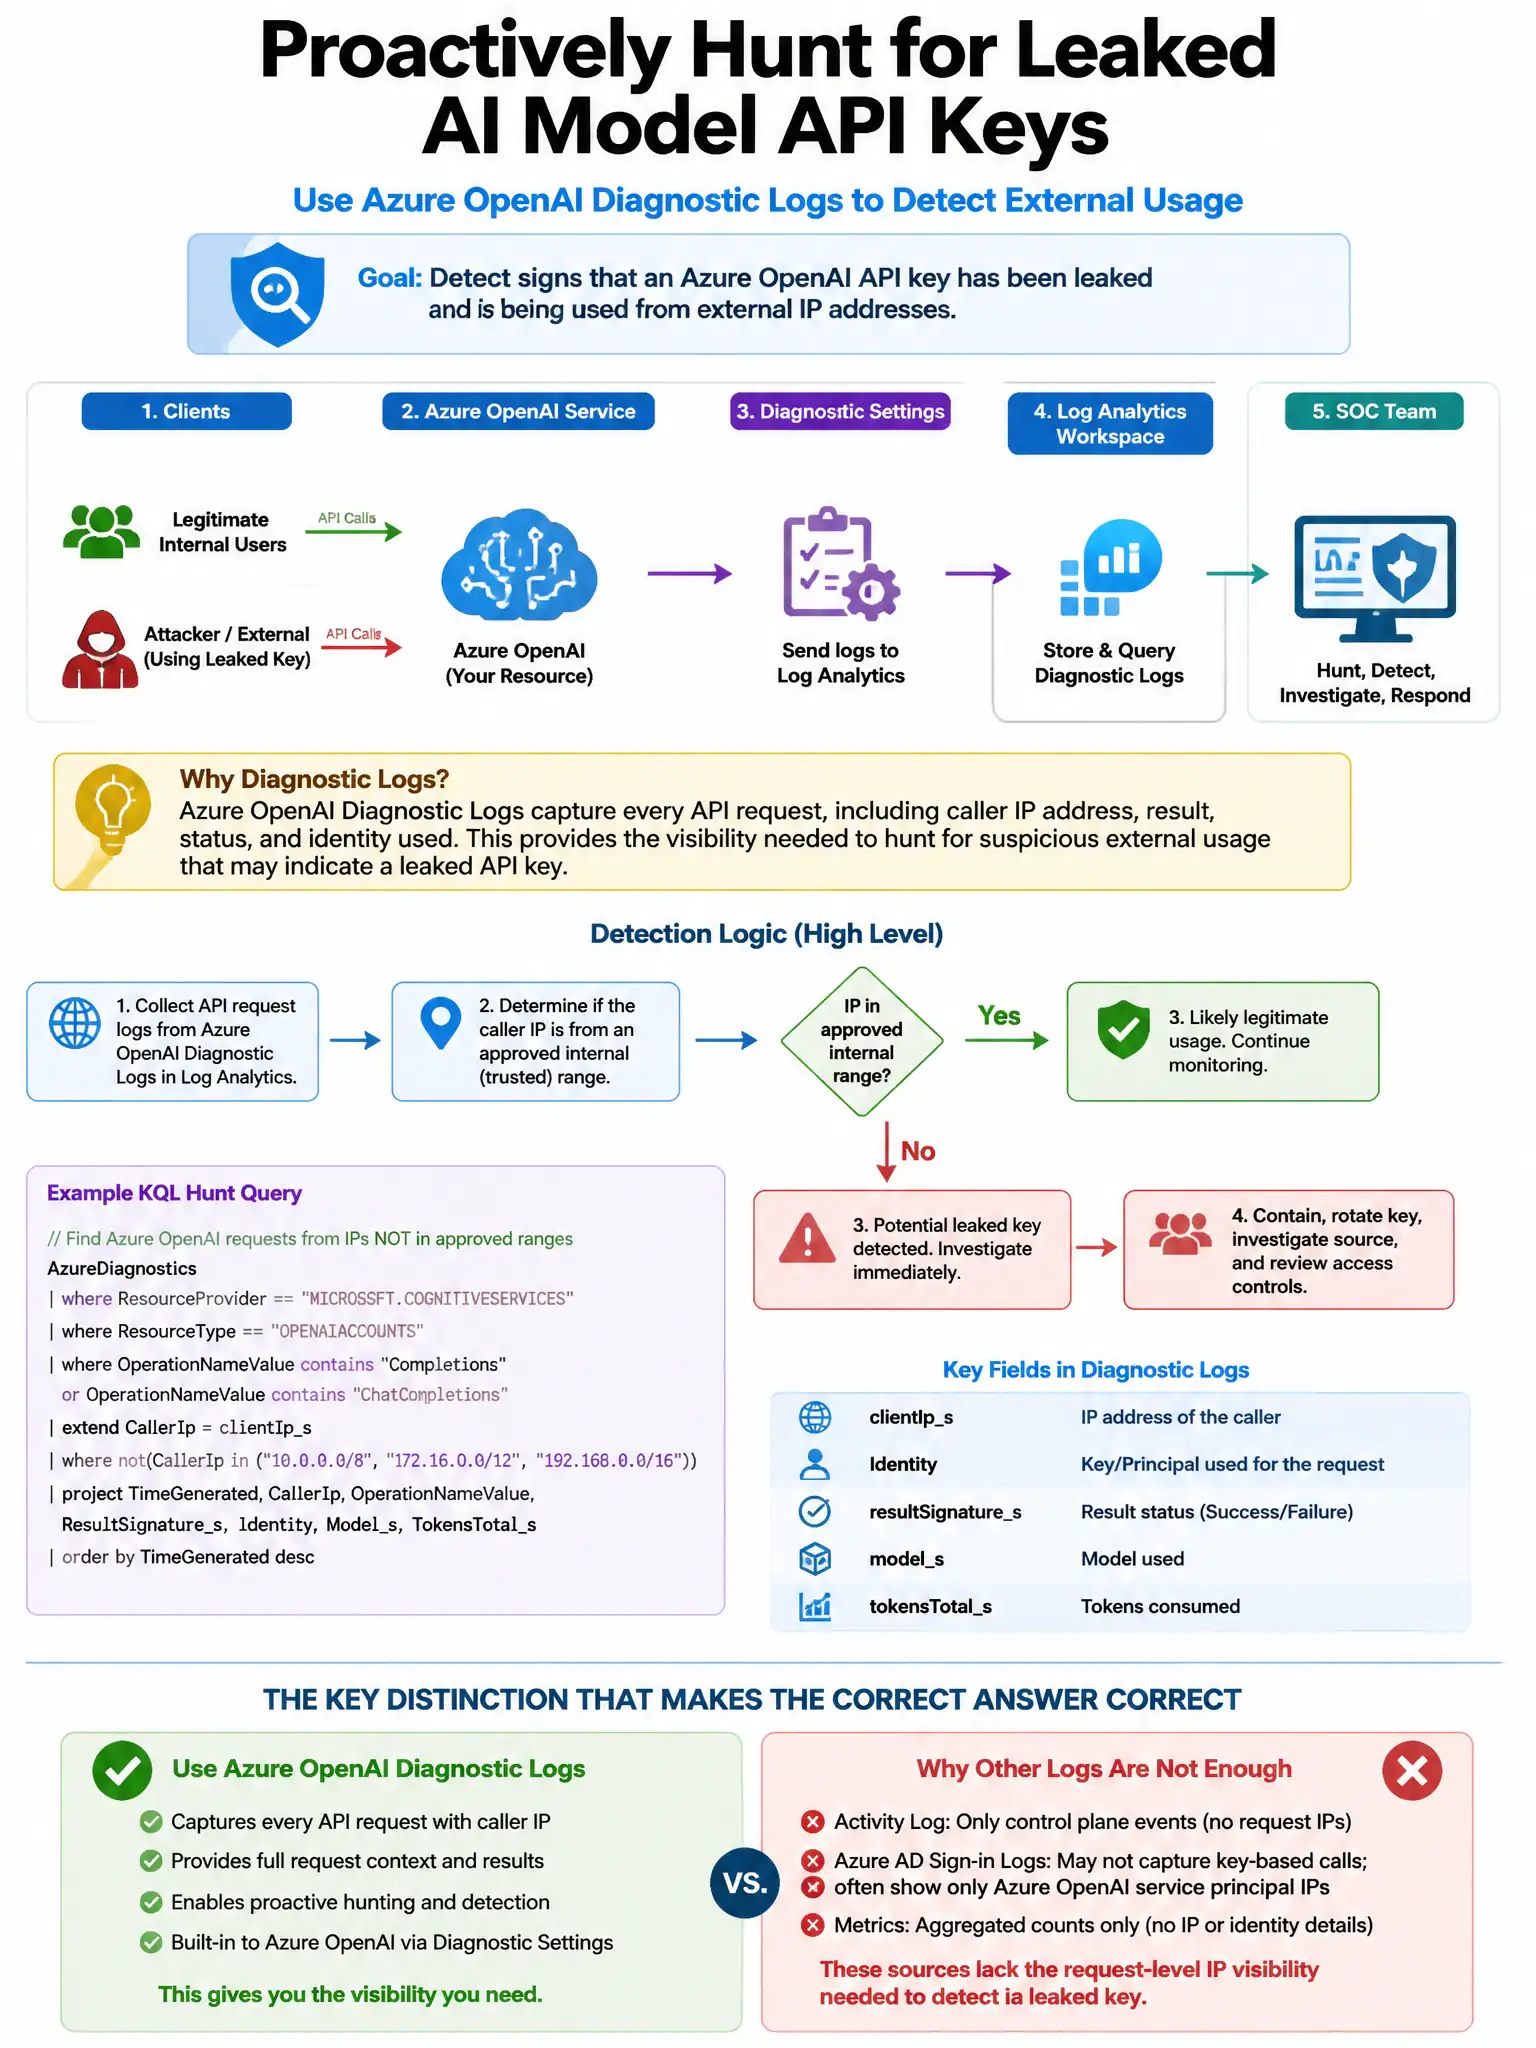
An organization's SOC team wants to proactively hunt for signs that an AI model API key has been leaked and is being used from external IP addresses. Azure OpenAI diagnostic logs are in Sentinel. Which KQL hunting query approach identifies calls from IPs not seen in the previous 30 days?
Select an answer to reveal the explanation.
Short Explanation
You want to compare the last 24 hours of Azure OpenAI caller IPs against the prior 30 days and surface anything new. That’s exactly what a KQL let statement with except or leftantisemi join does, so you catch fresh external callers that may mean a leaked API key.
Full Explanation
The correct approach is to query AzureDiagnostics for caller IPs in the last 24 hours that do not appear in the set of caller IPs from the prior 30 days, using a let statement and join/except logic. This uses KQL let statements to compute two sets: IPs seen in the last 24 hours and IPs seen in the 30 days before that. Using except or join kind=leftantisemi identifies IPs in the recent set that are not in the historical baseline, surfacing new, potentially unauthorized callers. This is a classic threat hunting pattern for detecting anomalous new access sources. The static watchlist approach is wrong because comparing against a static watchlist requires maintenance and does not automatically adapt to the organization's legitimate IP range over time—it would generate false positives as new legitimate IPs are added. The SecurityAlert approach is wrong because SecurityAlert contains security alert records, not raw diagnostic logs with caller IP details that haven't yet been alerted on; this approach misses new attacks not yet detected by rules. The AzureActivity approach is wrong because AzureActivity captures management plane operations, not data plane inference calls with source IPs.