
A security team is implementing a SOAR playbook to automatically enrich Microsoft Sentinel AI security incidents with threat intelligence. When a new incident is created involving an external IP address, the playbook should look up the IP in Microsoft Defender Threat Intelligence (MDTI) and add the result as a comment to the Sentinel incident. Which Logic Apps connector enables the MDTI lookup?
Select an answer to reveal the explanation.
Short Explanation
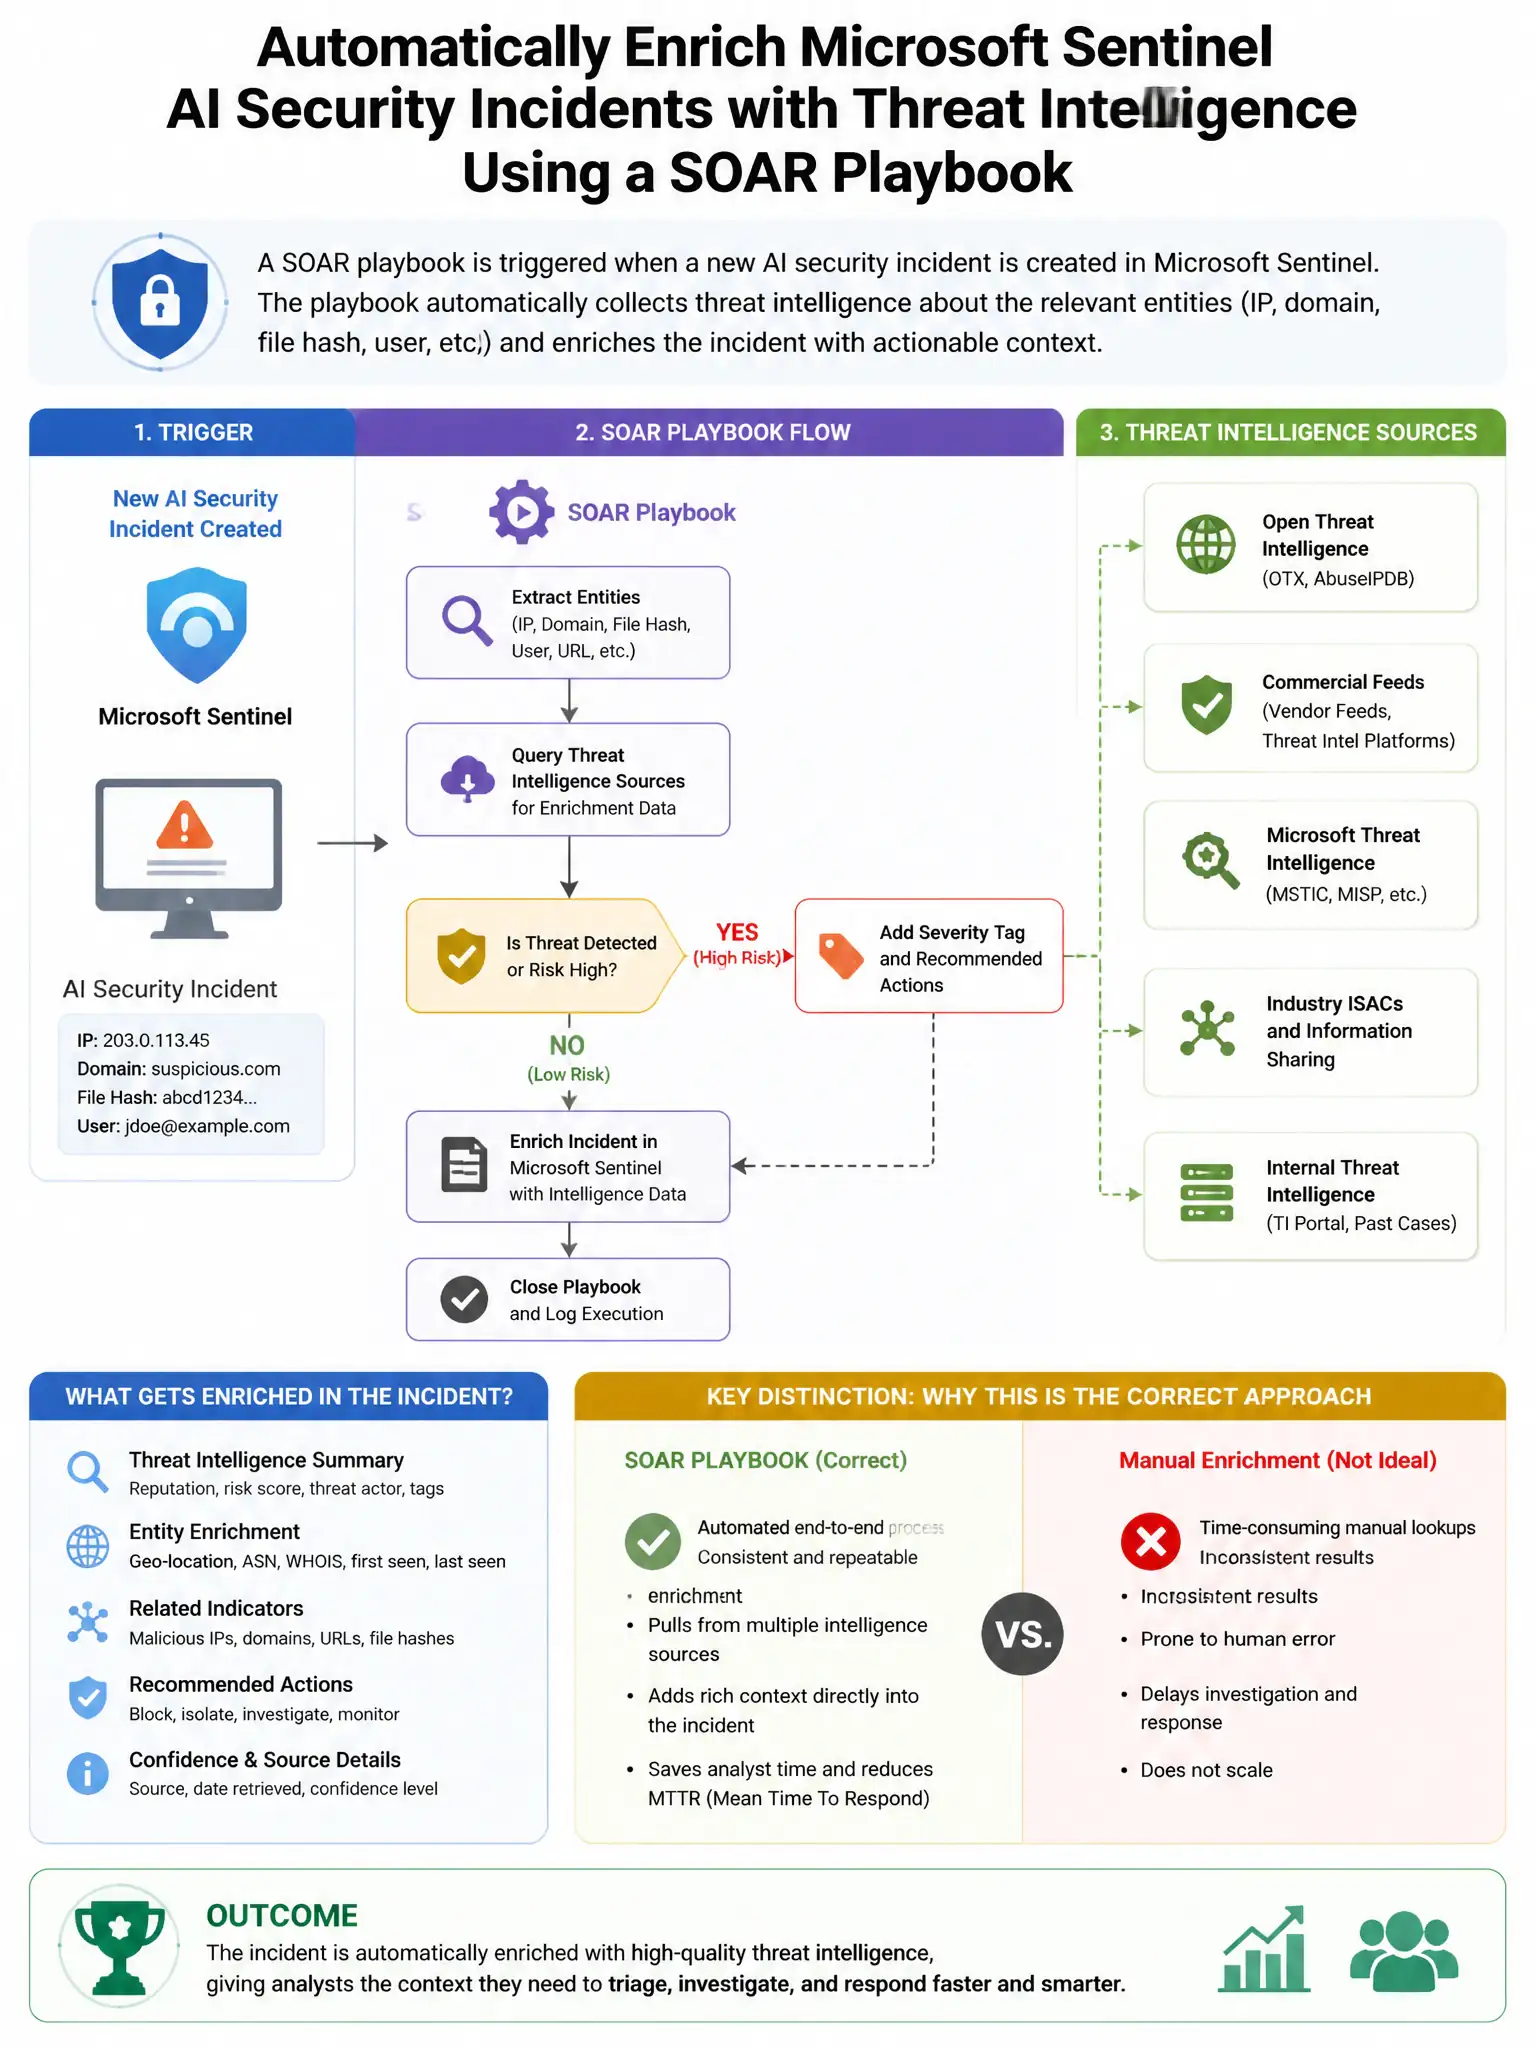
Here's the deal — you need the Microsoft Sentinel connector's 'Add comment to incident' action plus the Azure Logic Apps HTTP connector to call the Microsoft Defender Threat Intelligence API. That lets you look up the external IP and write the enrichment back to the Sentinel incident.
Full Explanation
The correct approach is to use the Microsoft Sentinel connector's 'Add comment to incident' action together with the Azure Logic Apps HTTP connector to call the Microsoft Defender Threat Intelligence API. This requires two steps: call the MDTI REST API via the HTTP connector, or the MDTI-specific connector if available, to look up the IP and get its reputation or context; then use the Sentinel connector's 'Add comment to incident' action to write the enrichment data back to the incident. This combination of the HTTP connector for external API calls and the Sentinel connector for incident updates is the standard pattern. The Microsoft Graph Security API connector for Defender Threat Intelligence alerts only is wrong because the Microsoft Graph Security API provides access to security alerts and incidents across Microsoft products but does not serve as a direct Threat Intelligence lookup interface for IP enrichment in the same way. The Azure Monitor connector for threat intelligence queries is wrong because Azure Monitor is for log analytics queries; it does not provide threat intelligence enrichment. The Microsoft Defender for Endpoint connector for IP reputation lookup is wrong because the Defender for Endpoint connector provides endpoint management actions, not general threat intelligence IP reputation lookup.