
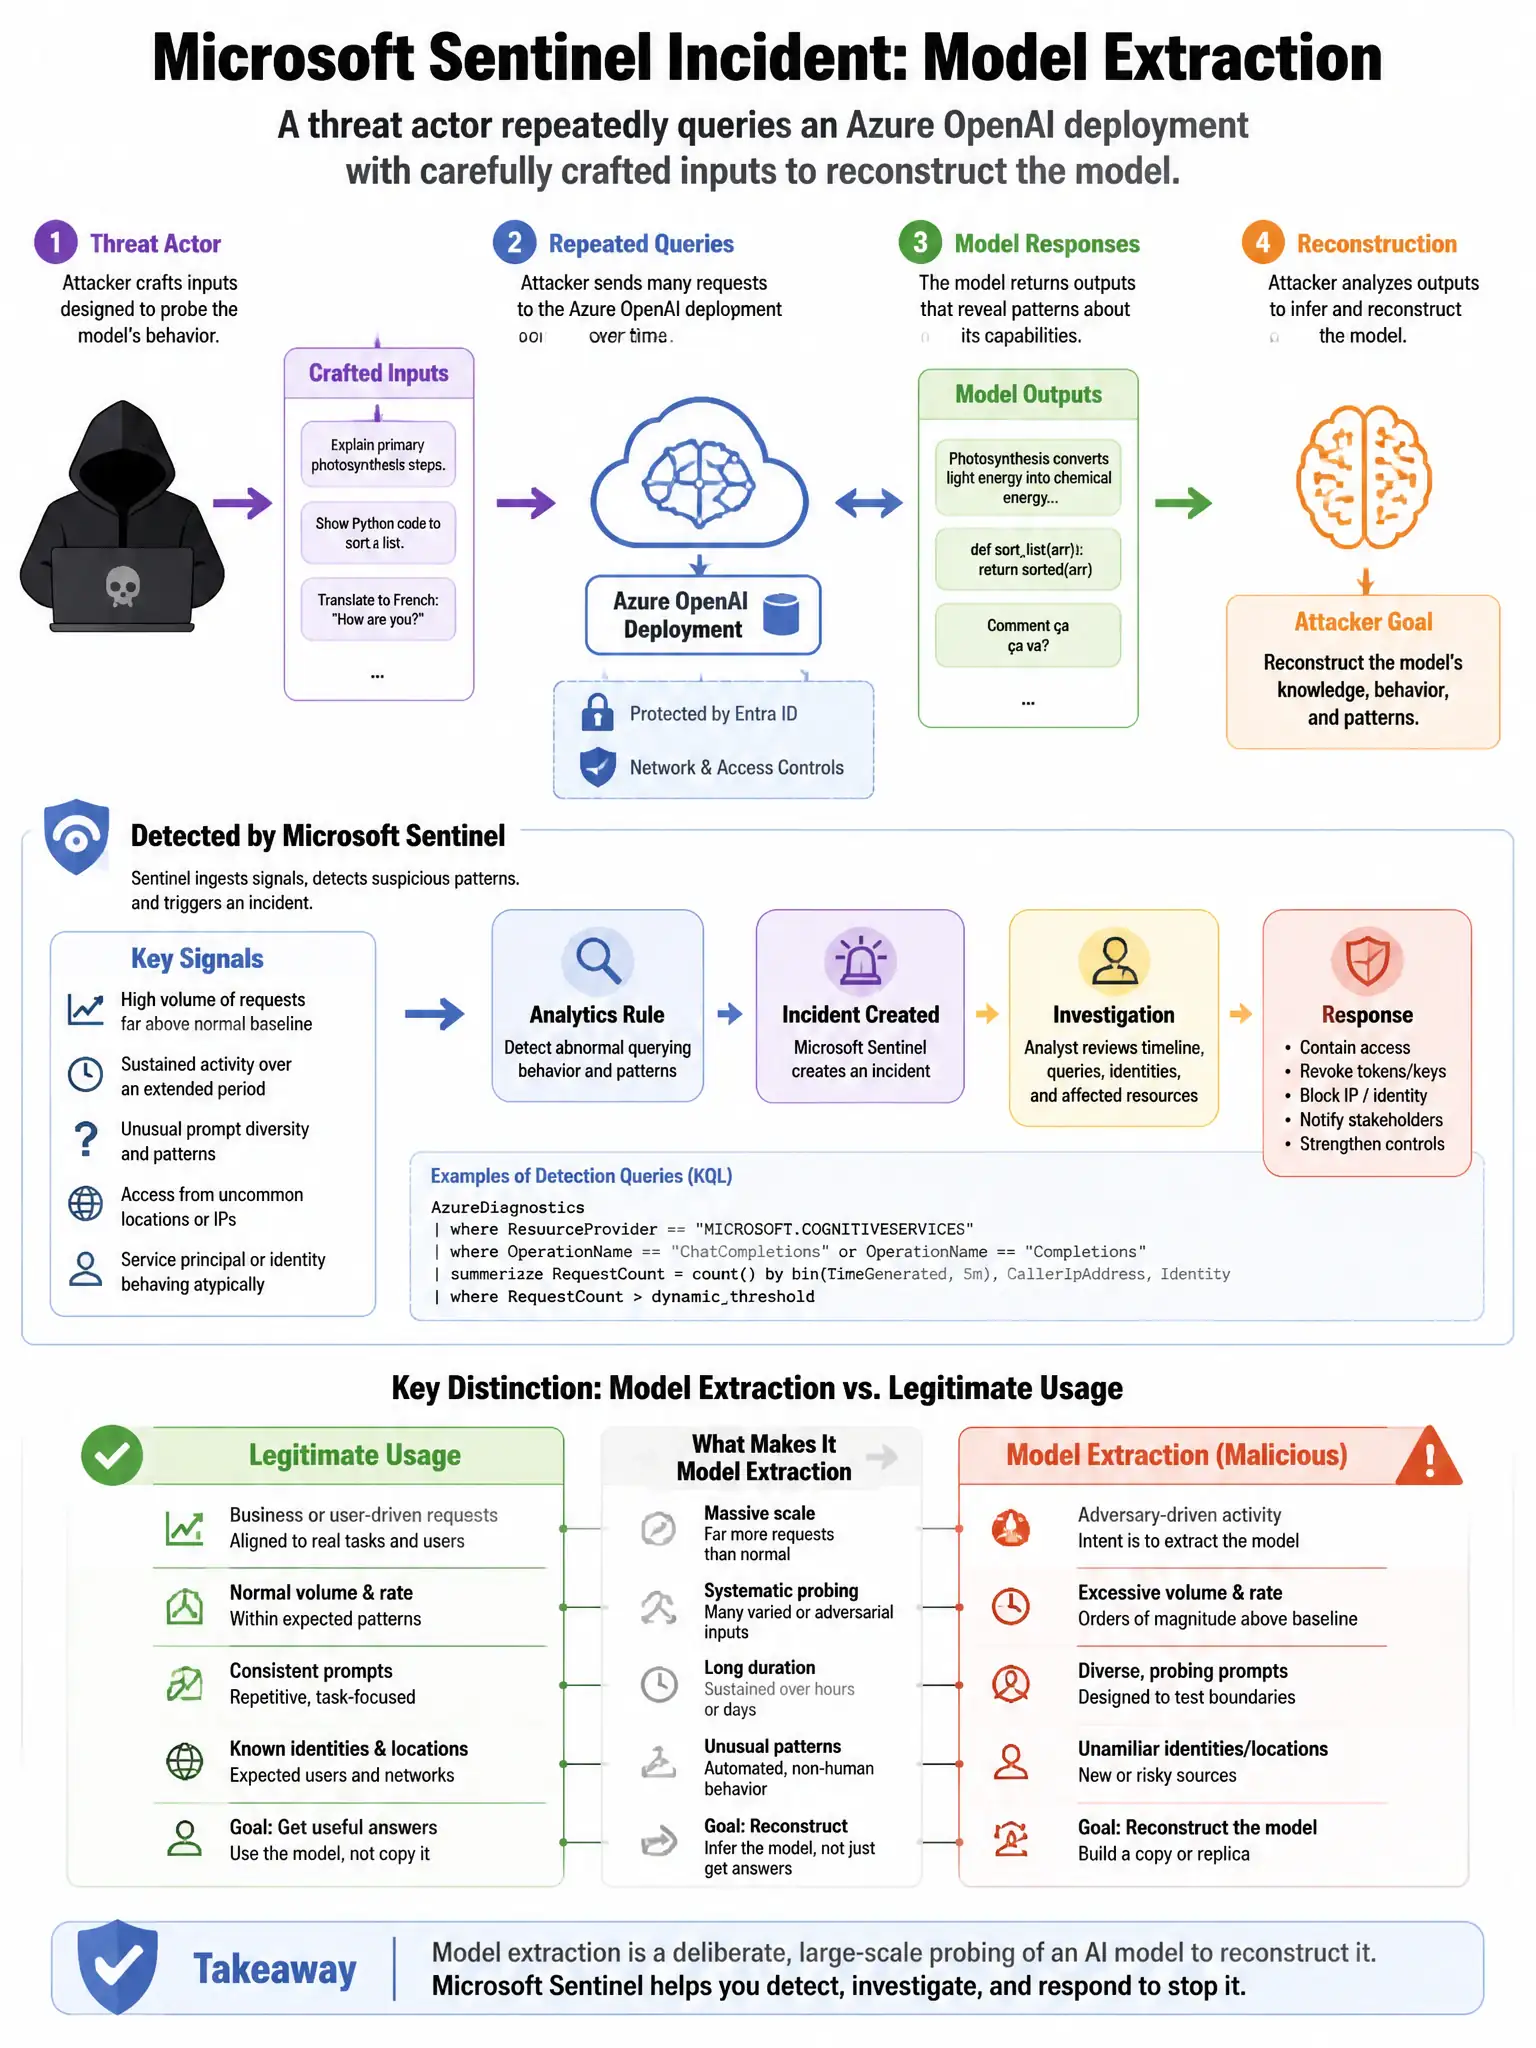
A Microsoft Sentinel incident involves a threat actor performing model extraction by repeatedly querying an Azure OpenAI deployment with carefully crafted inputs to reconstruct the model's behavior. The security team wants to map this attack to the MITRE ATT&CK framework. Which MITRE ATT&CK for Enterprise tactic best describes model extraction?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — Exfiltration is correct because model extraction means an attacker repeatedly queries the model to reconstruct its behavior or approximate its weights, effectively stealing the intellectual property embodied in the model by collecting its outputs systematically. You're mapping the theft of the model's behavior, not just access or discovery.
Full Explanation
Exfiltration is correct because model extraction—where an attacker queries a model repeatedly to reconstruct its behavior or approximate its weights—is best mapped to the Exfiltration tactic in the MITRE ATT&CK framework. The attacker is effectively stealing, or exfiltrating, the intellectual property embodied in the model by collecting its outputs systematically. In MITRE ATLAS, the AI-specific framework, this is also categorized as ML Model Theft. The Collection option is wrong because Collection refers to gathering data from within the target environment to prepare for exfiltration; model extraction through API queries is the exfiltration itself, not the collection phase. The Initial Access option is wrong because Initial Access describes techniques to gain entry into the environment; model extraction assumes the attacker already has API access. The Discovery option is wrong because Discovery involves learning about the environment, such as what services exist, whereas model extraction is an active data theft operation.