
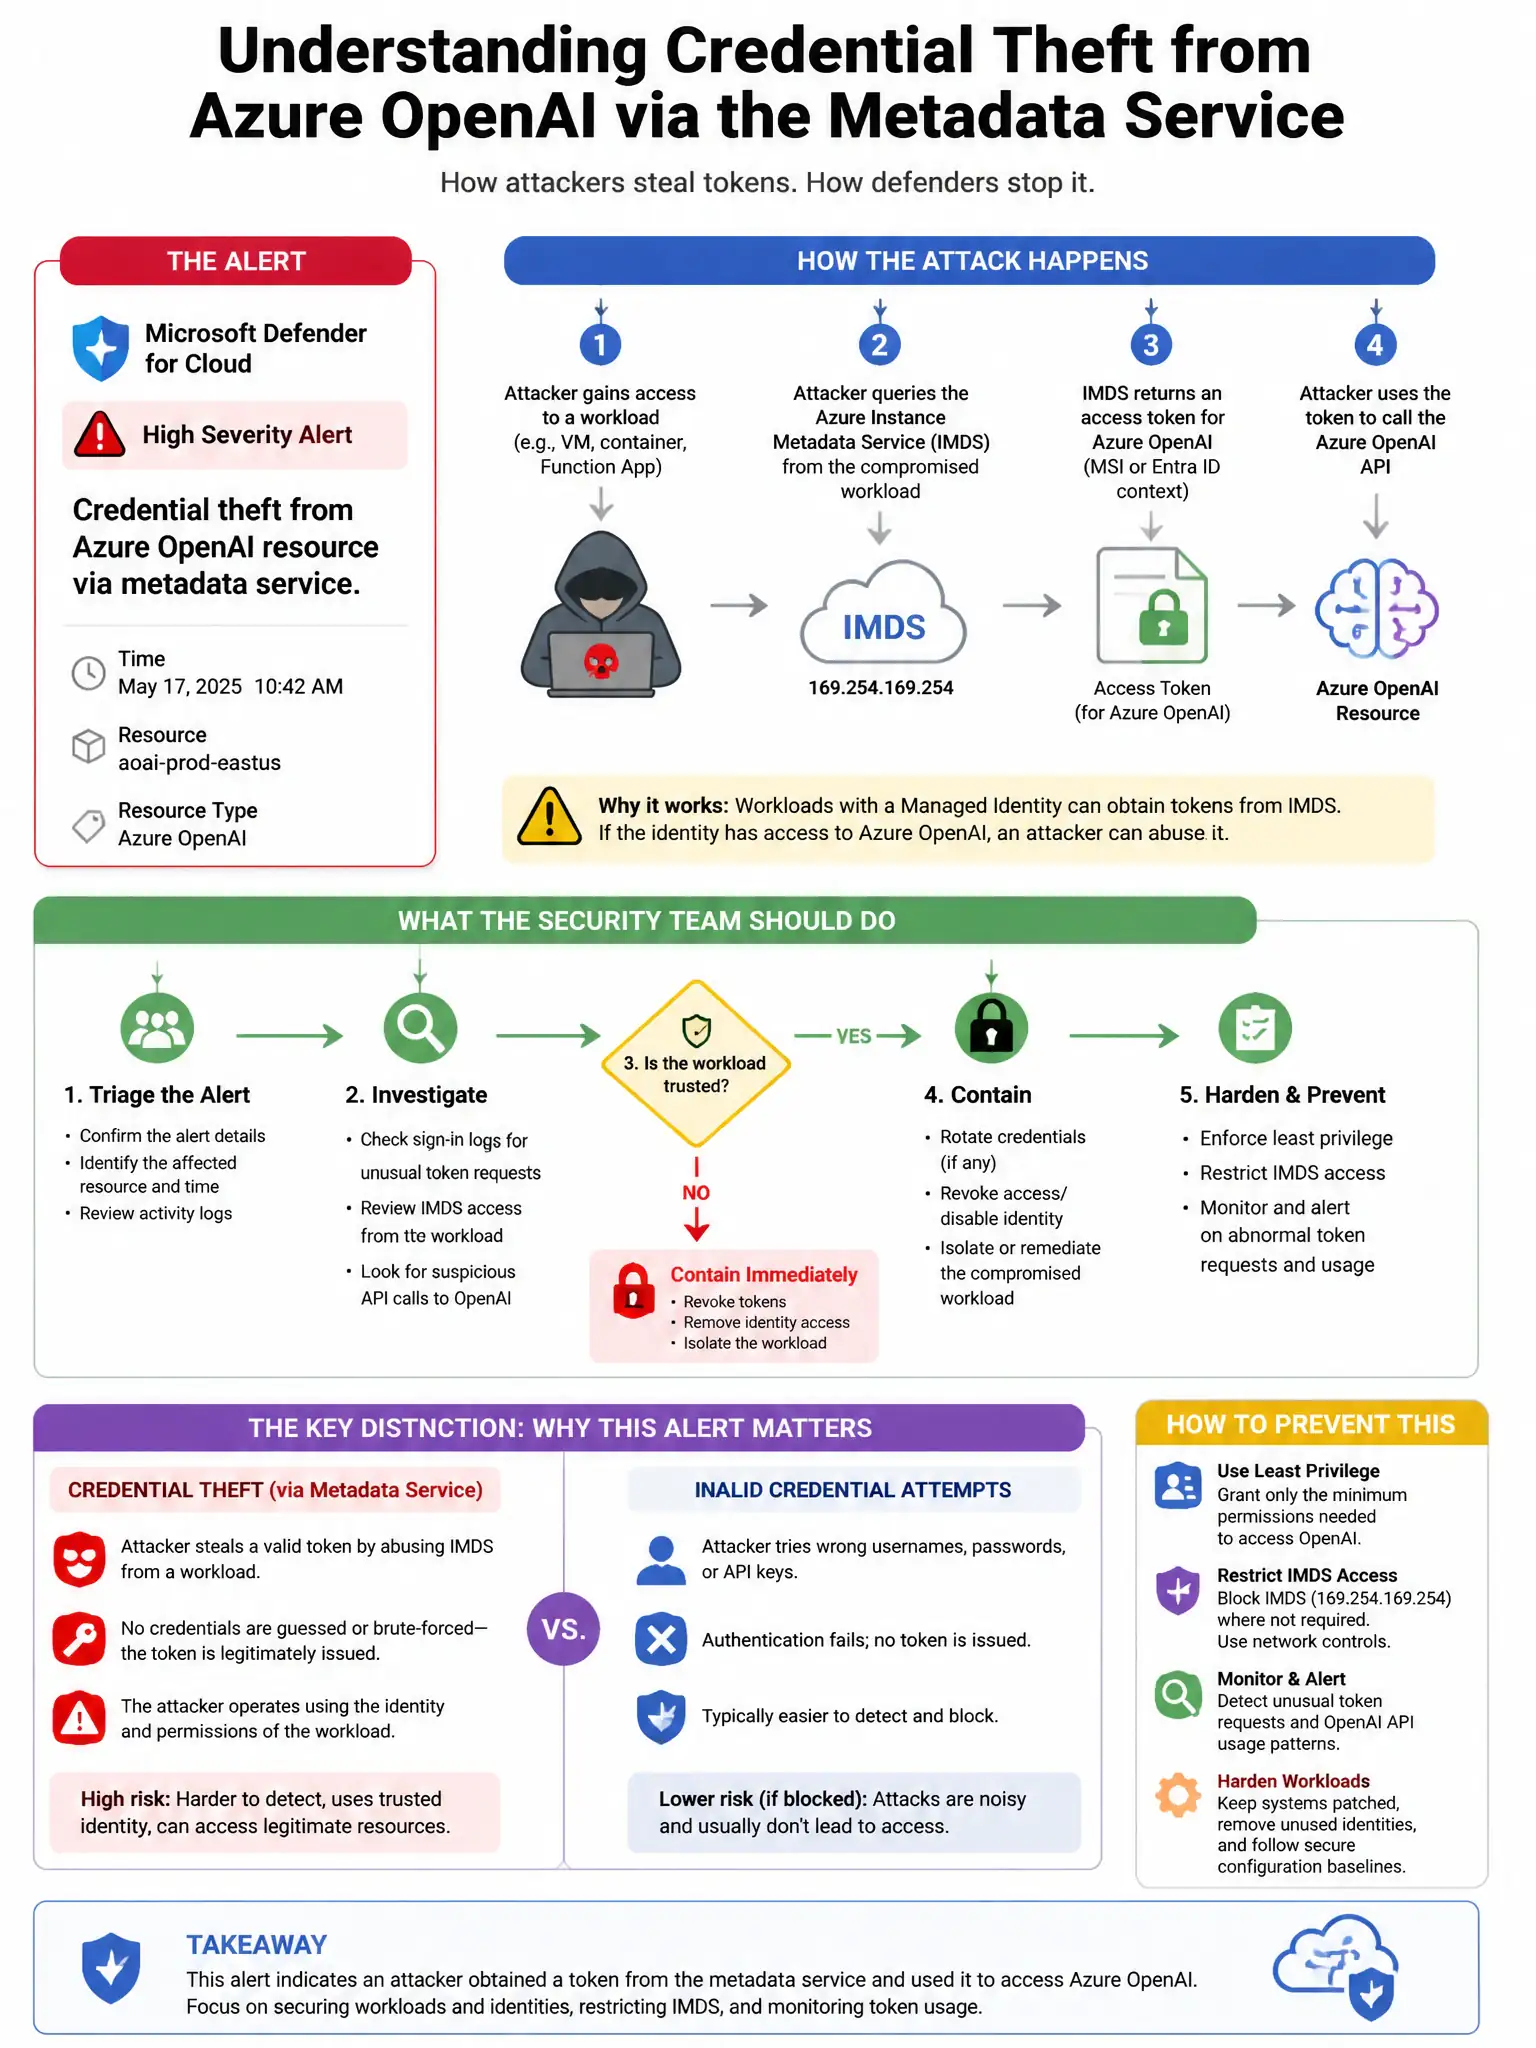
A security team using Microsoft Defender for Cloud receives an alert indicating 'Credential theft from Azure OpenAI resource via metadata service.' This alert suggests an attacker on a compute resource is attempting to steal the managed identity token to call Azure OpenAI. Which Defender for Cloud plan generates this AI workload security alert?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you're seeing this alert because Microsoft Defender for AI Services is the plan that watches Azure AI resources, including Azure OpenAI, for AI-specific threats. It catches suspicious managed identity token use, like credential theft via the metadata service, so you know an attacker is trying to call Azure OpenAI.
Full Explanation
The Microsoft Defender for AI Services plan is the right answer because it is the Defender for Cloud plan that monitors Azure AI resources, including Azure OpenAI Service, for threats. It generates security alerts specific to AI workloads, including suspicious token usage patterns that may indicate credential theft or misuse of managed identity tokens to authenticate to Azure OpenAI. The Microsoft Defender for Servers plan is wrong because it monitors server workloads for endpoint-level threats such as malware and privilege escalation; it does not generate AI service-specific alerts. The Microsoft Defender for Key Vault plan is wrong because it monitors suspicious access to Azure Key Vault, not Azure OpenAI credential theft via the metadata service. The Microsoft Defender for Resource Manager plan is wrong because it detects anomalous operations on the Azure management plane, not data-plane AI service credential theft.