
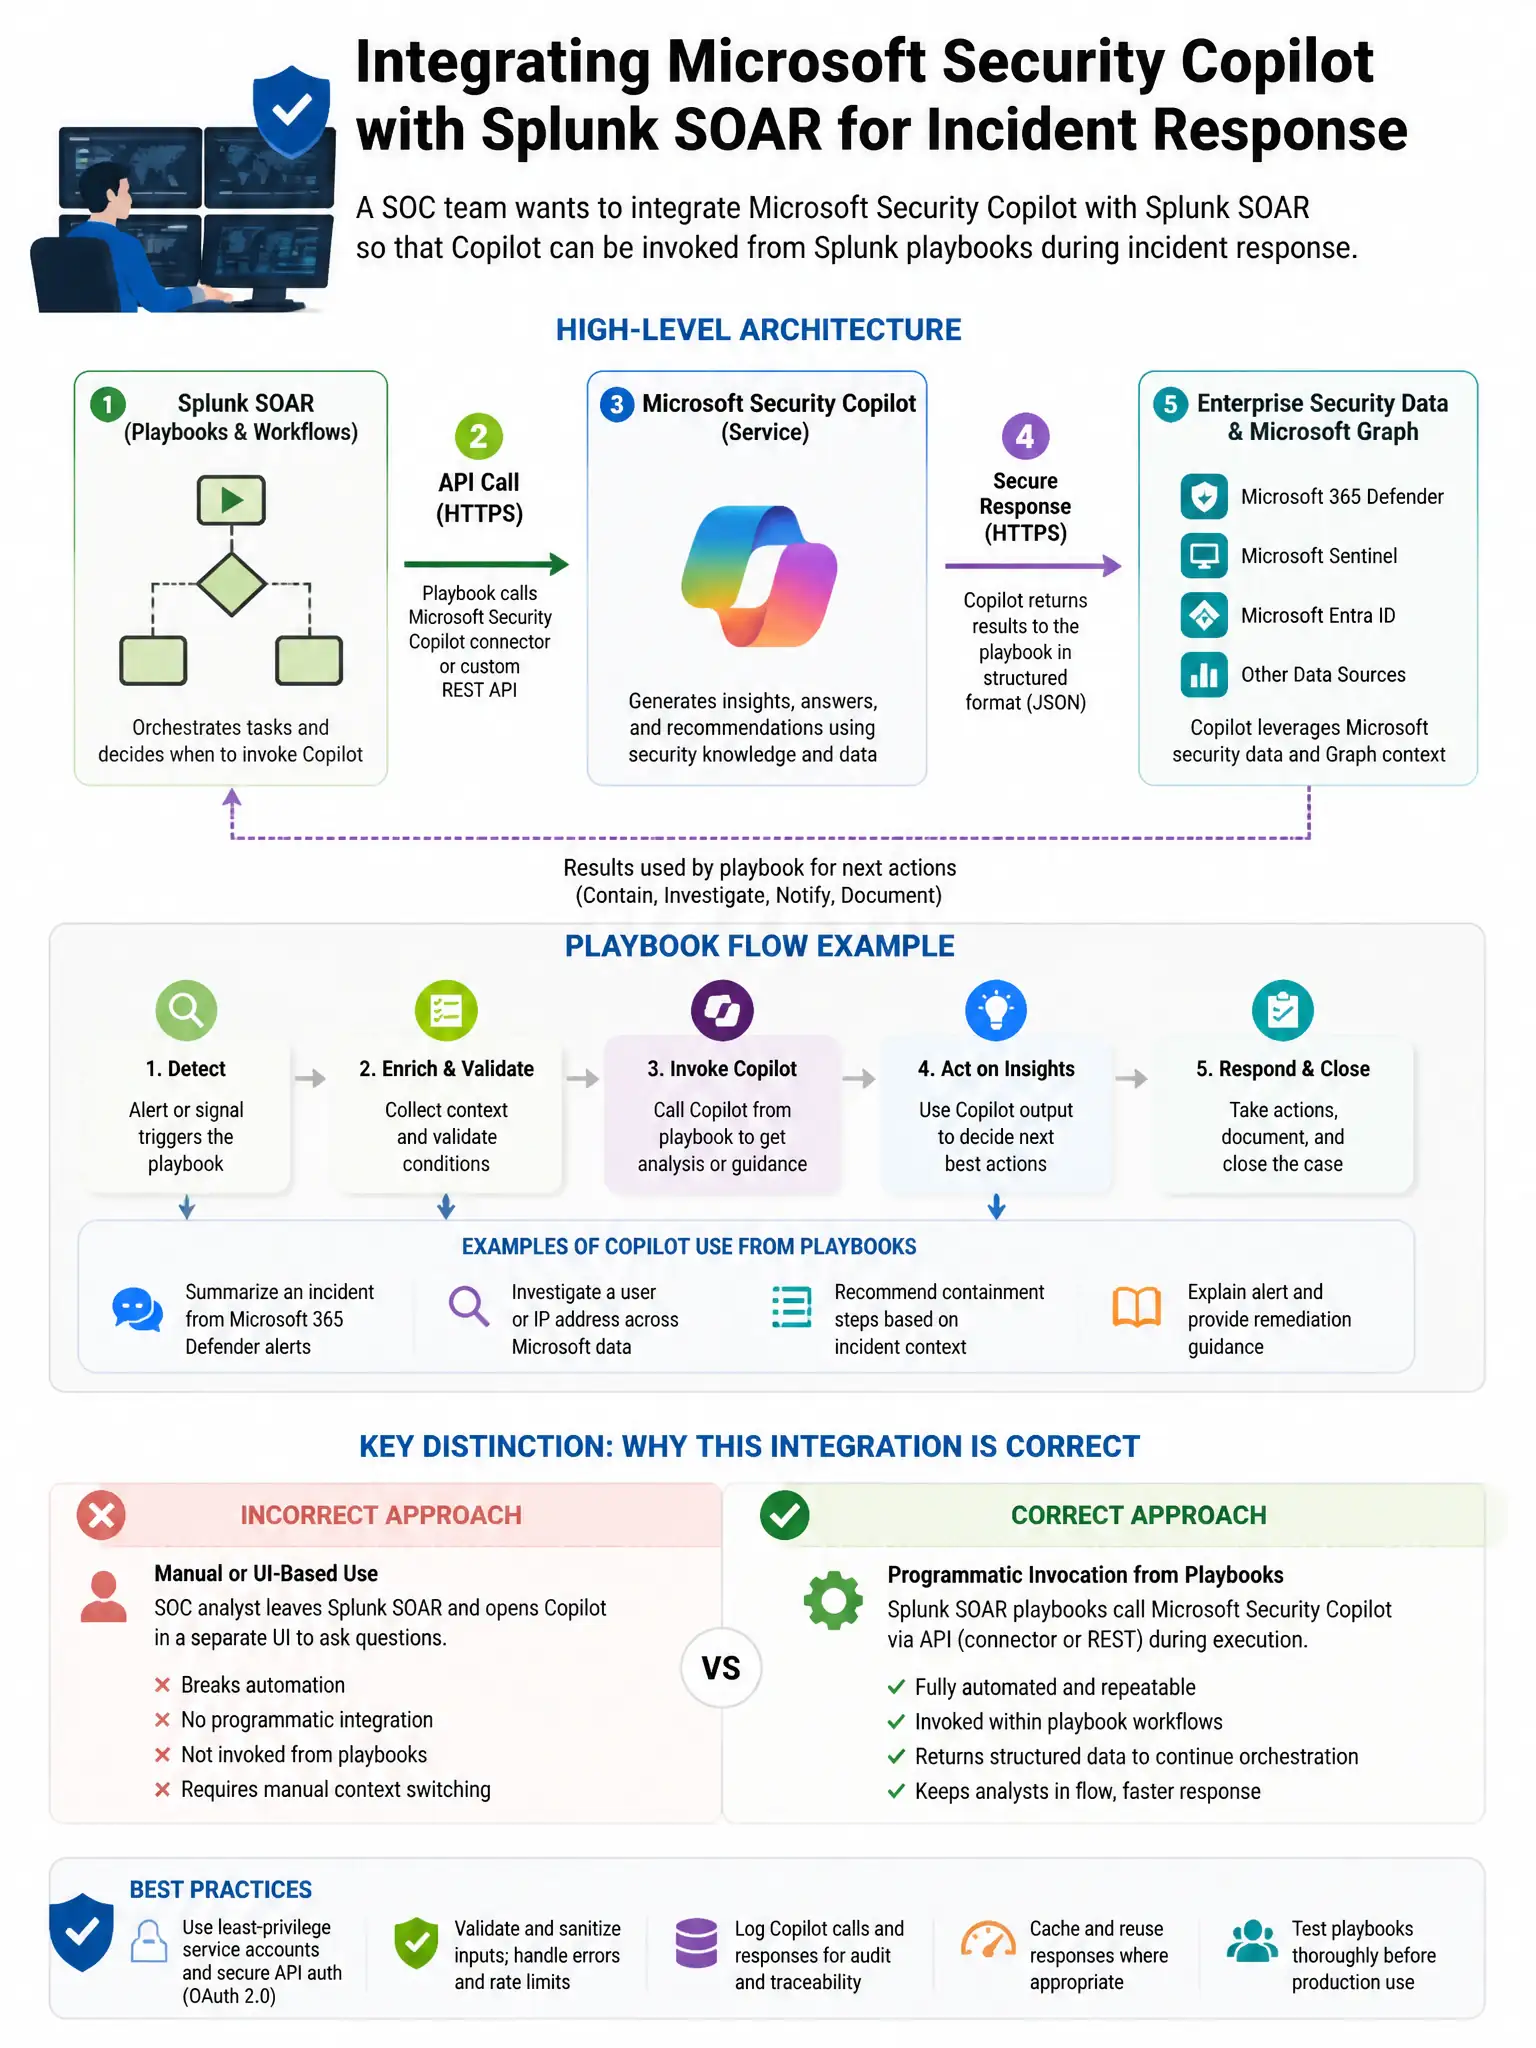
A SOC team wants to integrate Microsoft Security Copilot with a third-party SOAR platform (Splunk SOAR) so that Copilot can be invoked from Splunk playbooks during incident response. Which integration mechanism supports this?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you use the REST API with OAuth authentication because Security Copilot can be called programmatically from Splunk SOAR playbooks. You send prompts and get AI responses back for incident response.
Full Explanation
The REST API with OAuth authentication is correct because Microsoft Security Copilot exposes a REST API that external systems can call programmatically using OAuth 2.0 authentication. Splunk SOAR playbooks can make authenticated REST API calls to Security Copilot, passing prompts and receiving AI-generated responses to incorporate into automated incident response workflows. The Microsoft Security Copilot Logic Apps connector is wrong because while Microsoft Security Copilot may have future Logic Apps connectors, direct REST API integration is the documented approach for third-party SOAR integration. The Microsoft Sentinel playbook calling Splunk via webhook is wrong because it is a Sentinel-to-Splunk integration, the opposite of what is needed (Splunk invoking Copilot). The Microsoft Graph Security API is wrong because it provides access to security alerts and incidents across Microsoft products, not to the Security Copilot inference API.