
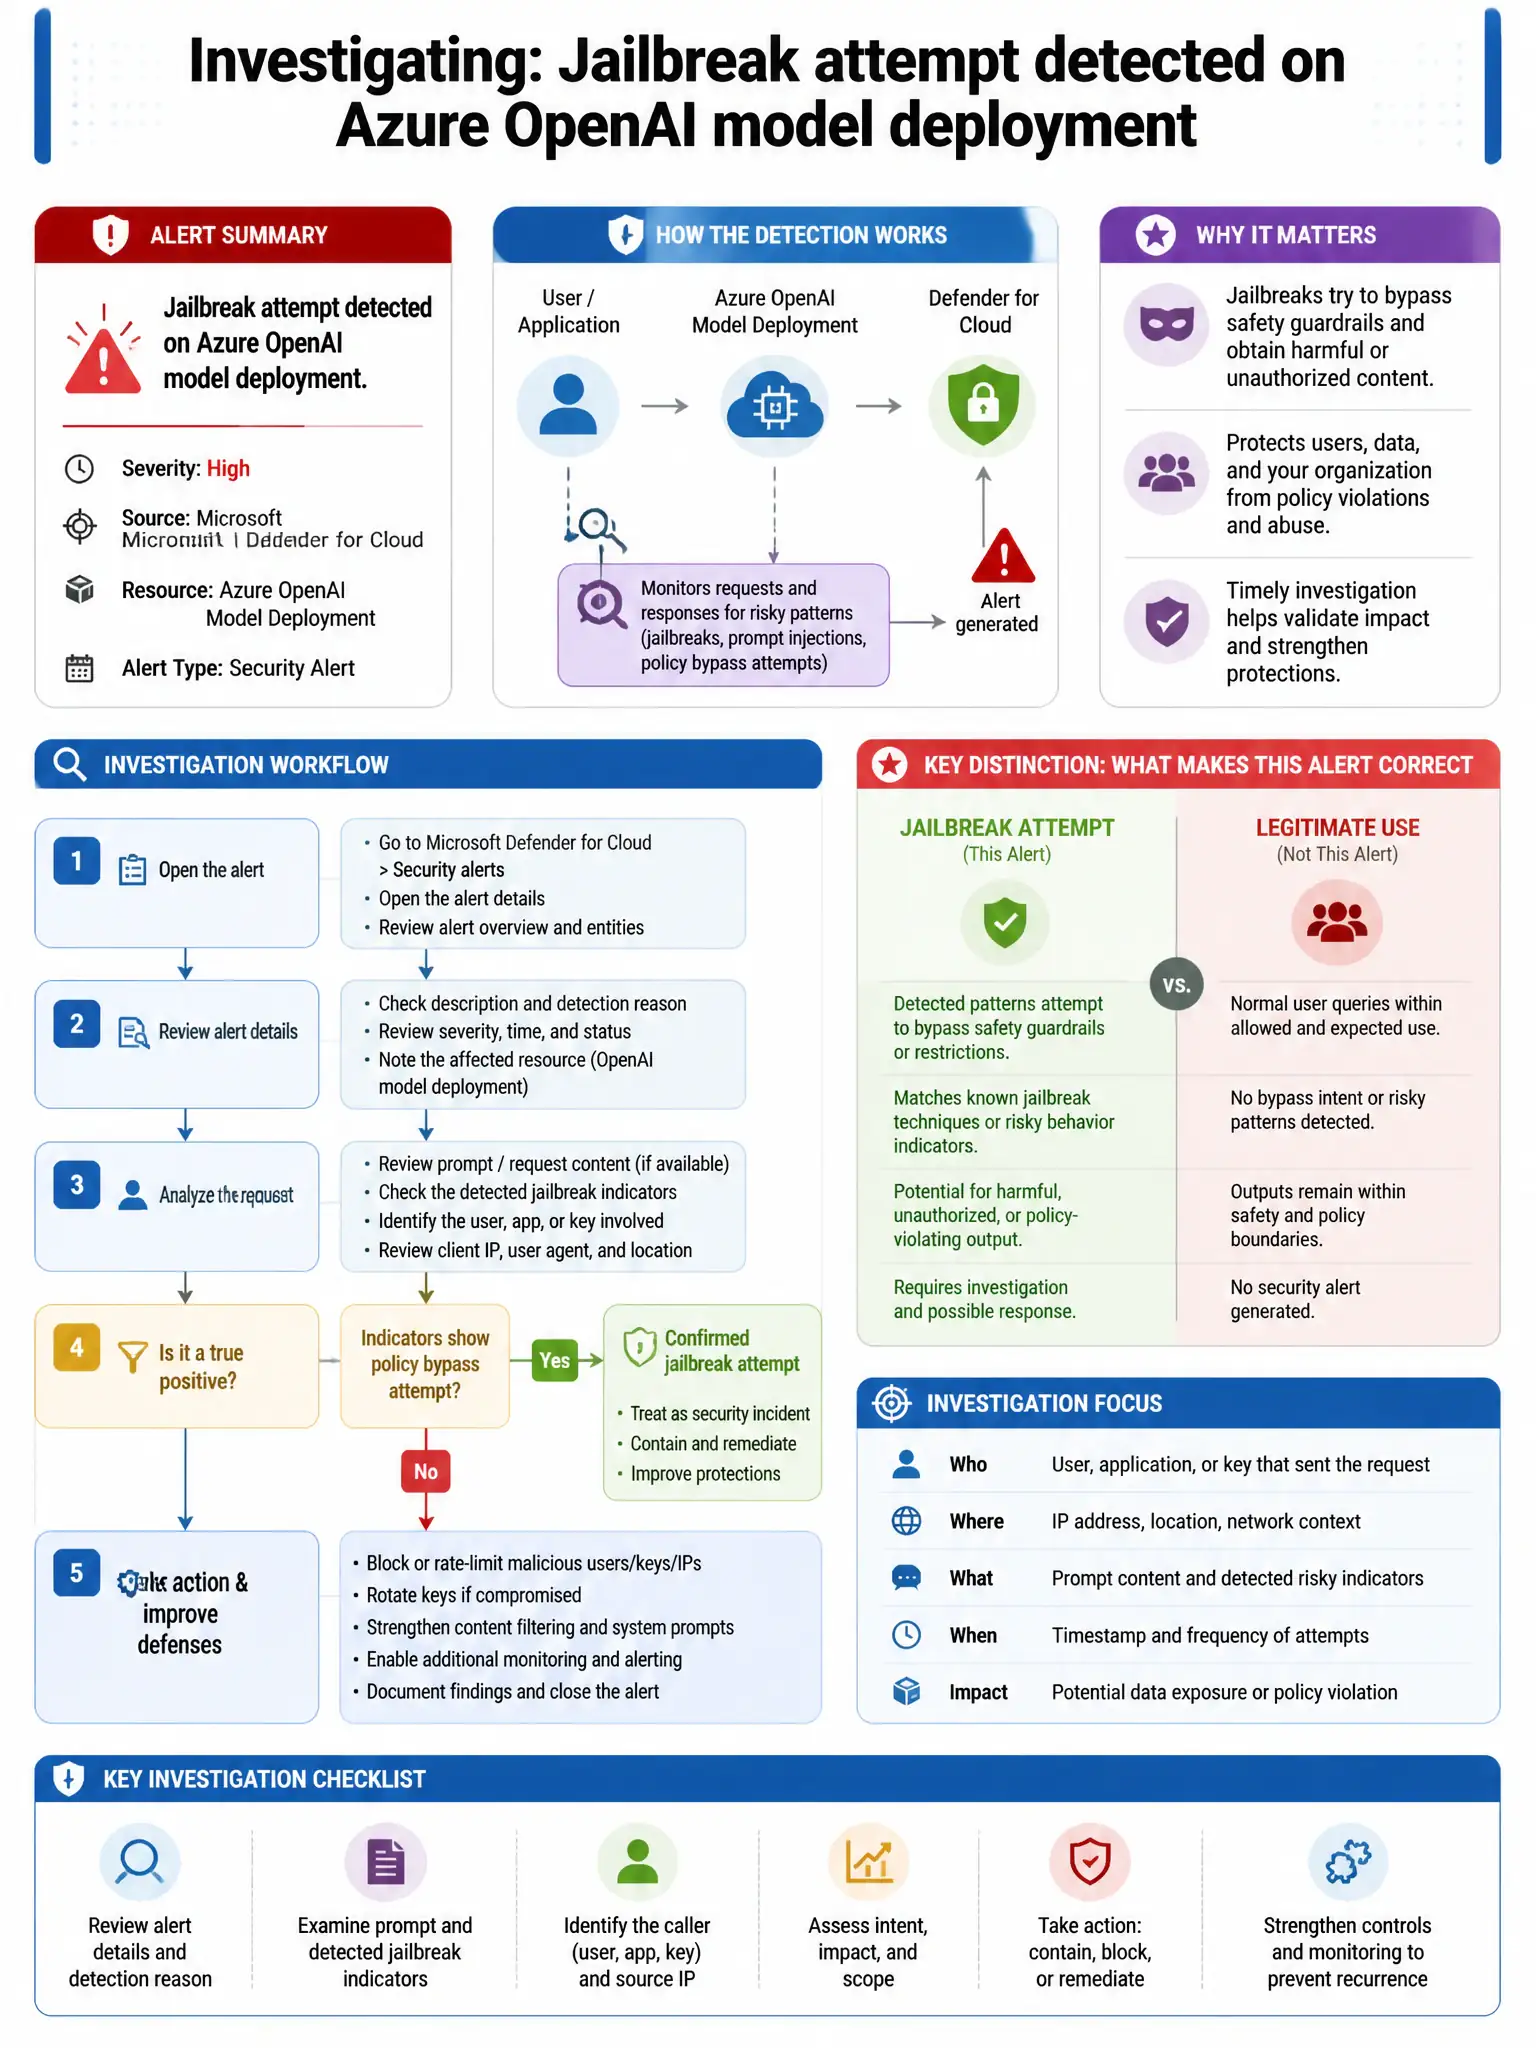
Microsoft Defender for Cloud has generated an alert titled 'Jailbreak attempt detected on Azure OpenAI model deployment.' A security engineer needs to investigate this alert. Which data source contains the full prompt content that triggered the alert?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you want the Azure OpenAI resource diagnostic logs, specifically the RequestResponse category sent to Log Analytics, because that's where the actual prompt content that triggered the jailbreak alert is captured.
Full Explanation
The Azure OpenAI resource diagnostic logs, specifically the RequestResponse category sent to a Log Analytics workspace, are correct because Azure OpenAI Service supports sending diagnostic logs to Log Analytics. The RequestResponse diagnostic category captures the actual API request and response content, including the prompts sent to the model. When Defender for Cloud detects a jailbreak attempt, the full prompt context for investigation is found in those RequestResponse diagnostic logs. The Azure Monitor Activity Log is wrong because it captures control plane operations, such as management API calls like resource creation, not data plane inference requests. Microsoft Defender for Endpoint Advanced Hunting is wrong because it contains endpoint telemetry, such as process events, file writes, and network connections, not Azure OpenAI API request content. Microsoft Entra ID Audit Logs are wrong because they capture identity and access management operations, not AI model inference request content.