
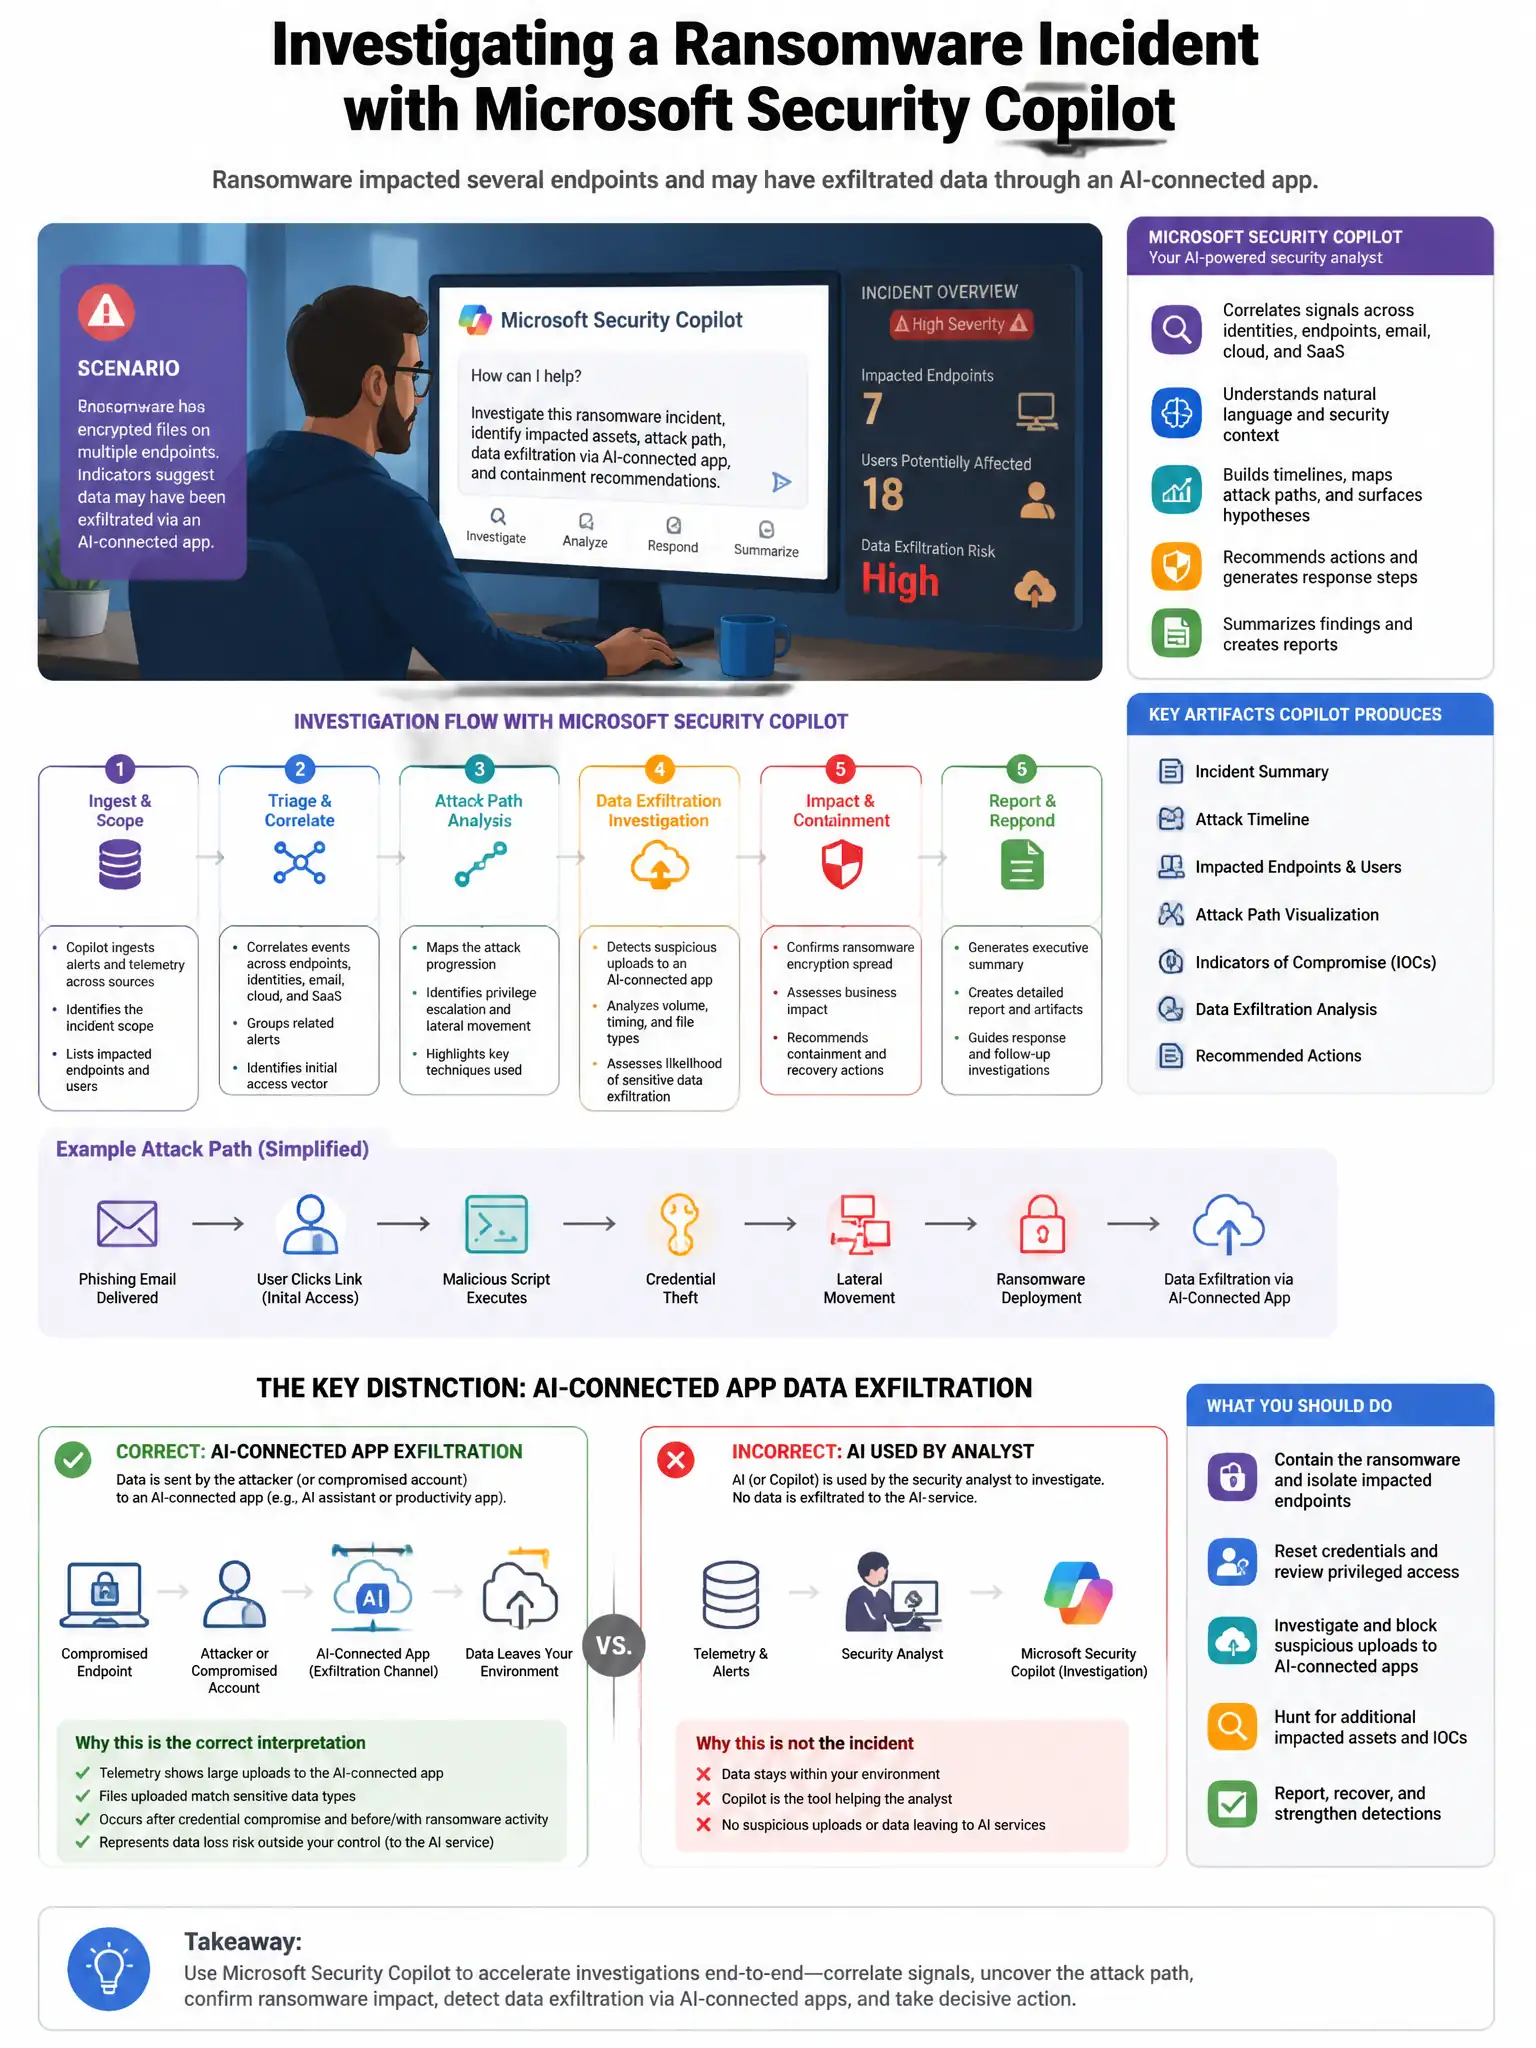
A security engineer is using Microsoft Security Copilot to investigate a ransomware incident that impacted several endpoints and may have exfiltrated data through an AI-connected pipeline. The engineer wants to use Security Copilot to generate a full incident summary, extract IOCs, and check threat intelligence in one workflow. Which Security Copilot feature should the engineer use to run this predefined multi-step investigation?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you want the promptbook designed for ransomware investigation because it chains the incident summary, IOC extraction, threat-intel checks, and remediation steps into one predefined workflow.
Full Explanation
A promptbook designed for ransomware investigation is correct because Promptbooks in Microsoft Security Copilot are pre-built sequences of prompts that automate multi-step security investigation workflows. A ransomware investigation promptbook would chain together prompts to summarize the incident, extract IOCs, query threat intelligence, and suggest remediation steps—all in a single workflow execution. A plugin from the Security Copilot plugin store is wrong because a plugin connects Copilot to a data source or tool, such as Sentinel or Defender threat intelligence, but is a data integration mechanism, not a multi-step investigation workflow. A custom skill built using the Security Copilot API is wrong because custom skills extend Copilot's reasoning capabilities for specific tasks; they do not orchestrate multi-step investigation sequences. The Defender XDR embedded Copilot experience is wrong because it provides AI assistance within the Defender portal for single-incident analysis, not a reusable multi-step promptbook workflow.