
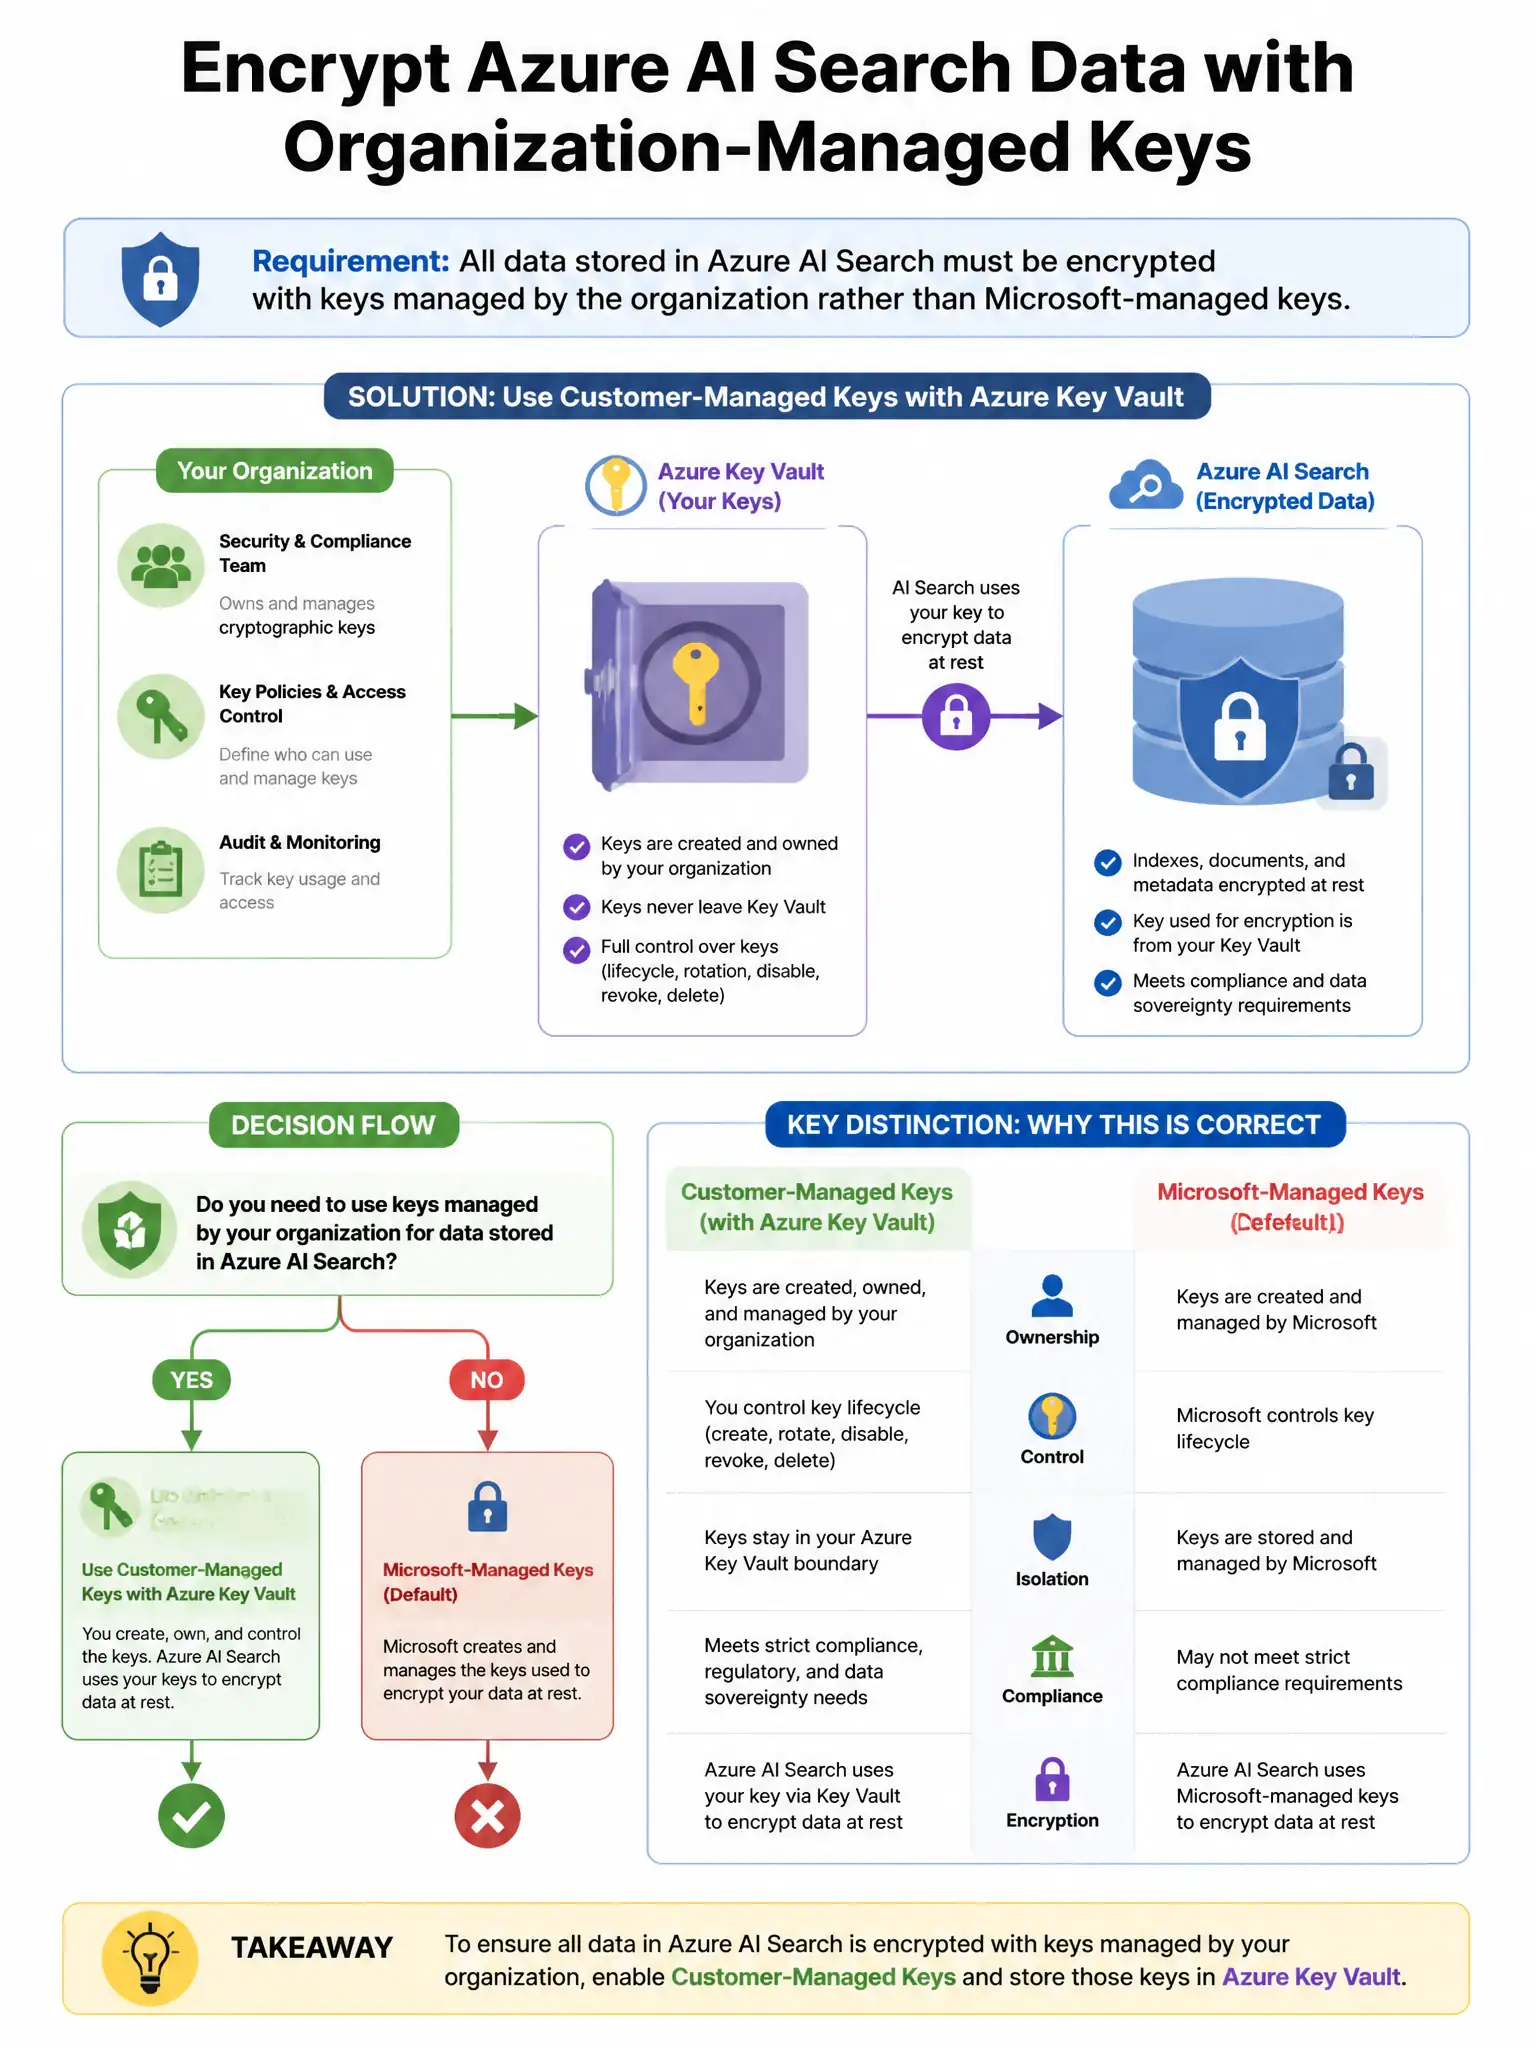
An organization requires that all data stored in Azure AI Search be encrypted with keys managed by the organization rather than Microsoft-managed keys. Which Azure feature provides this capability?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need Customer-managed keys (CMK) using Azure Key Vault for Azure AI Search because it lets you encrypt index data and synonym maps at rest with keys you control. You can revoke access, rotate keys, and keep cryptographic control, while Microsoft doesn't have access to your keys.
Full Explanation
Customer-managed keys (CMK) using Azure Key Vault for Azure AI Search is correct because Azure AI Search supports CMK through Azure Key Vault integration. When configured, index data and synonym maps are encrypted at rest using a key stored in your Key Vault that you control—you can revoke access, rotate keys, and maintain cryptographic control. Microsoft never has access to your keys. Azure Disk Encryption with BitLocker is wrong because it applies to IaaS VM disks, not PaaS service data storage like Azure AI Search. Azure Storage Service Encryption with customer-provided keys is wrong because it applies to Azure Blob and File storage operations; Azure AI Search has its own CMK mechanism at the service level. Transport Layer Security (TLS) 1.3 enforcement is wrong because it protects data in transit, not data at rest.