
A company stores Azure OpenAI Service API keys in Azure Key Vault. An automated pipeline needs to retrieve the key at runtime. The pipeline runs on an Azure Container Apps environment. What is the most secure method to grant the container app access to Key Vault?
Select an answer to reveal the explanation.
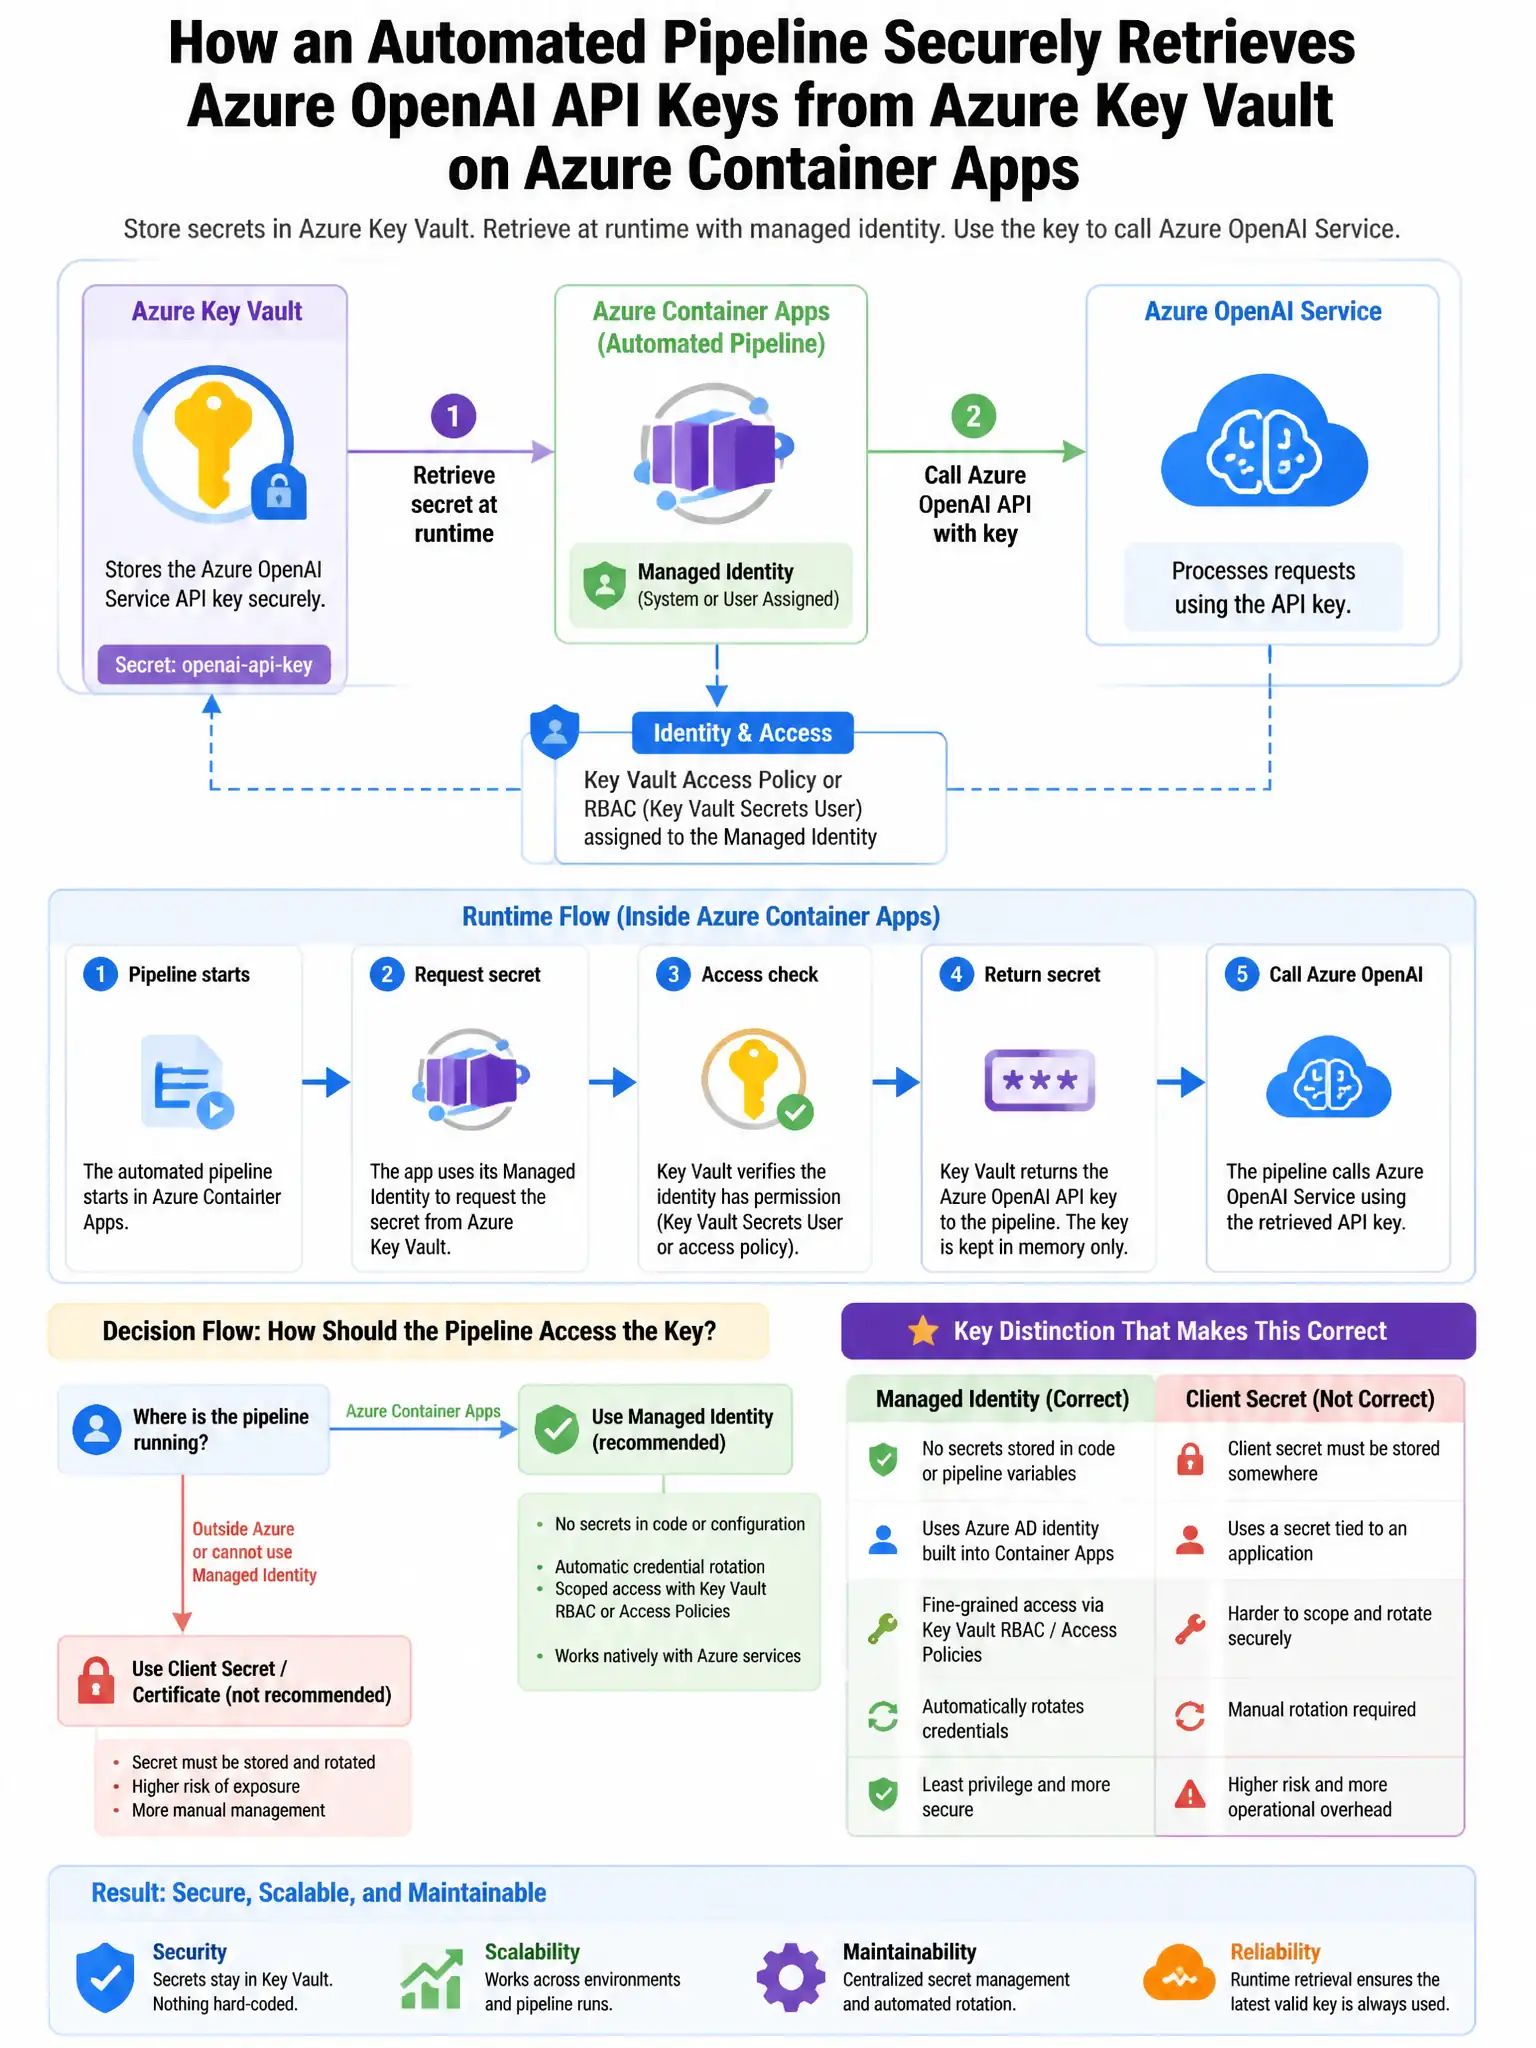
Short Explanation
Here's the deal — assign a user-assigned managed identity to the Container Apps environment and grant it the 'Key Vault Secrets User' role. That lets the app authenticate without storing credentials, and the role gives just enough permission to read secrets.
Full Explanation
The correct approach is to assign a user-assigned managed identity to the Container Apps environment and grant it the 'Key Vault Secrets User' role. This eliminates the need to store any credentials. The 'Key Vault Secrets User' role grants least-privilege read access to secrets. The container app authenticates to Key Vault using the managed identity's token from the Azure Instance Metadata Service, with no secrets in code or environment variables. Storing Key Vault access policy credentials in the container's environment variables is wrong because it risks exposure through container logs, environment variable enumeration, or image inspection. Using a service principal with a client certificate stored in the container image is wrong because the certificate is embedded in the image layer, which is accessible to anyone with image pull access. Enabling the Key Vault firewall to allow the Container Apps outbound IP range is wrong because IP allowlisting controls network access but does not authenticate the caller or eliminate credential storage.