
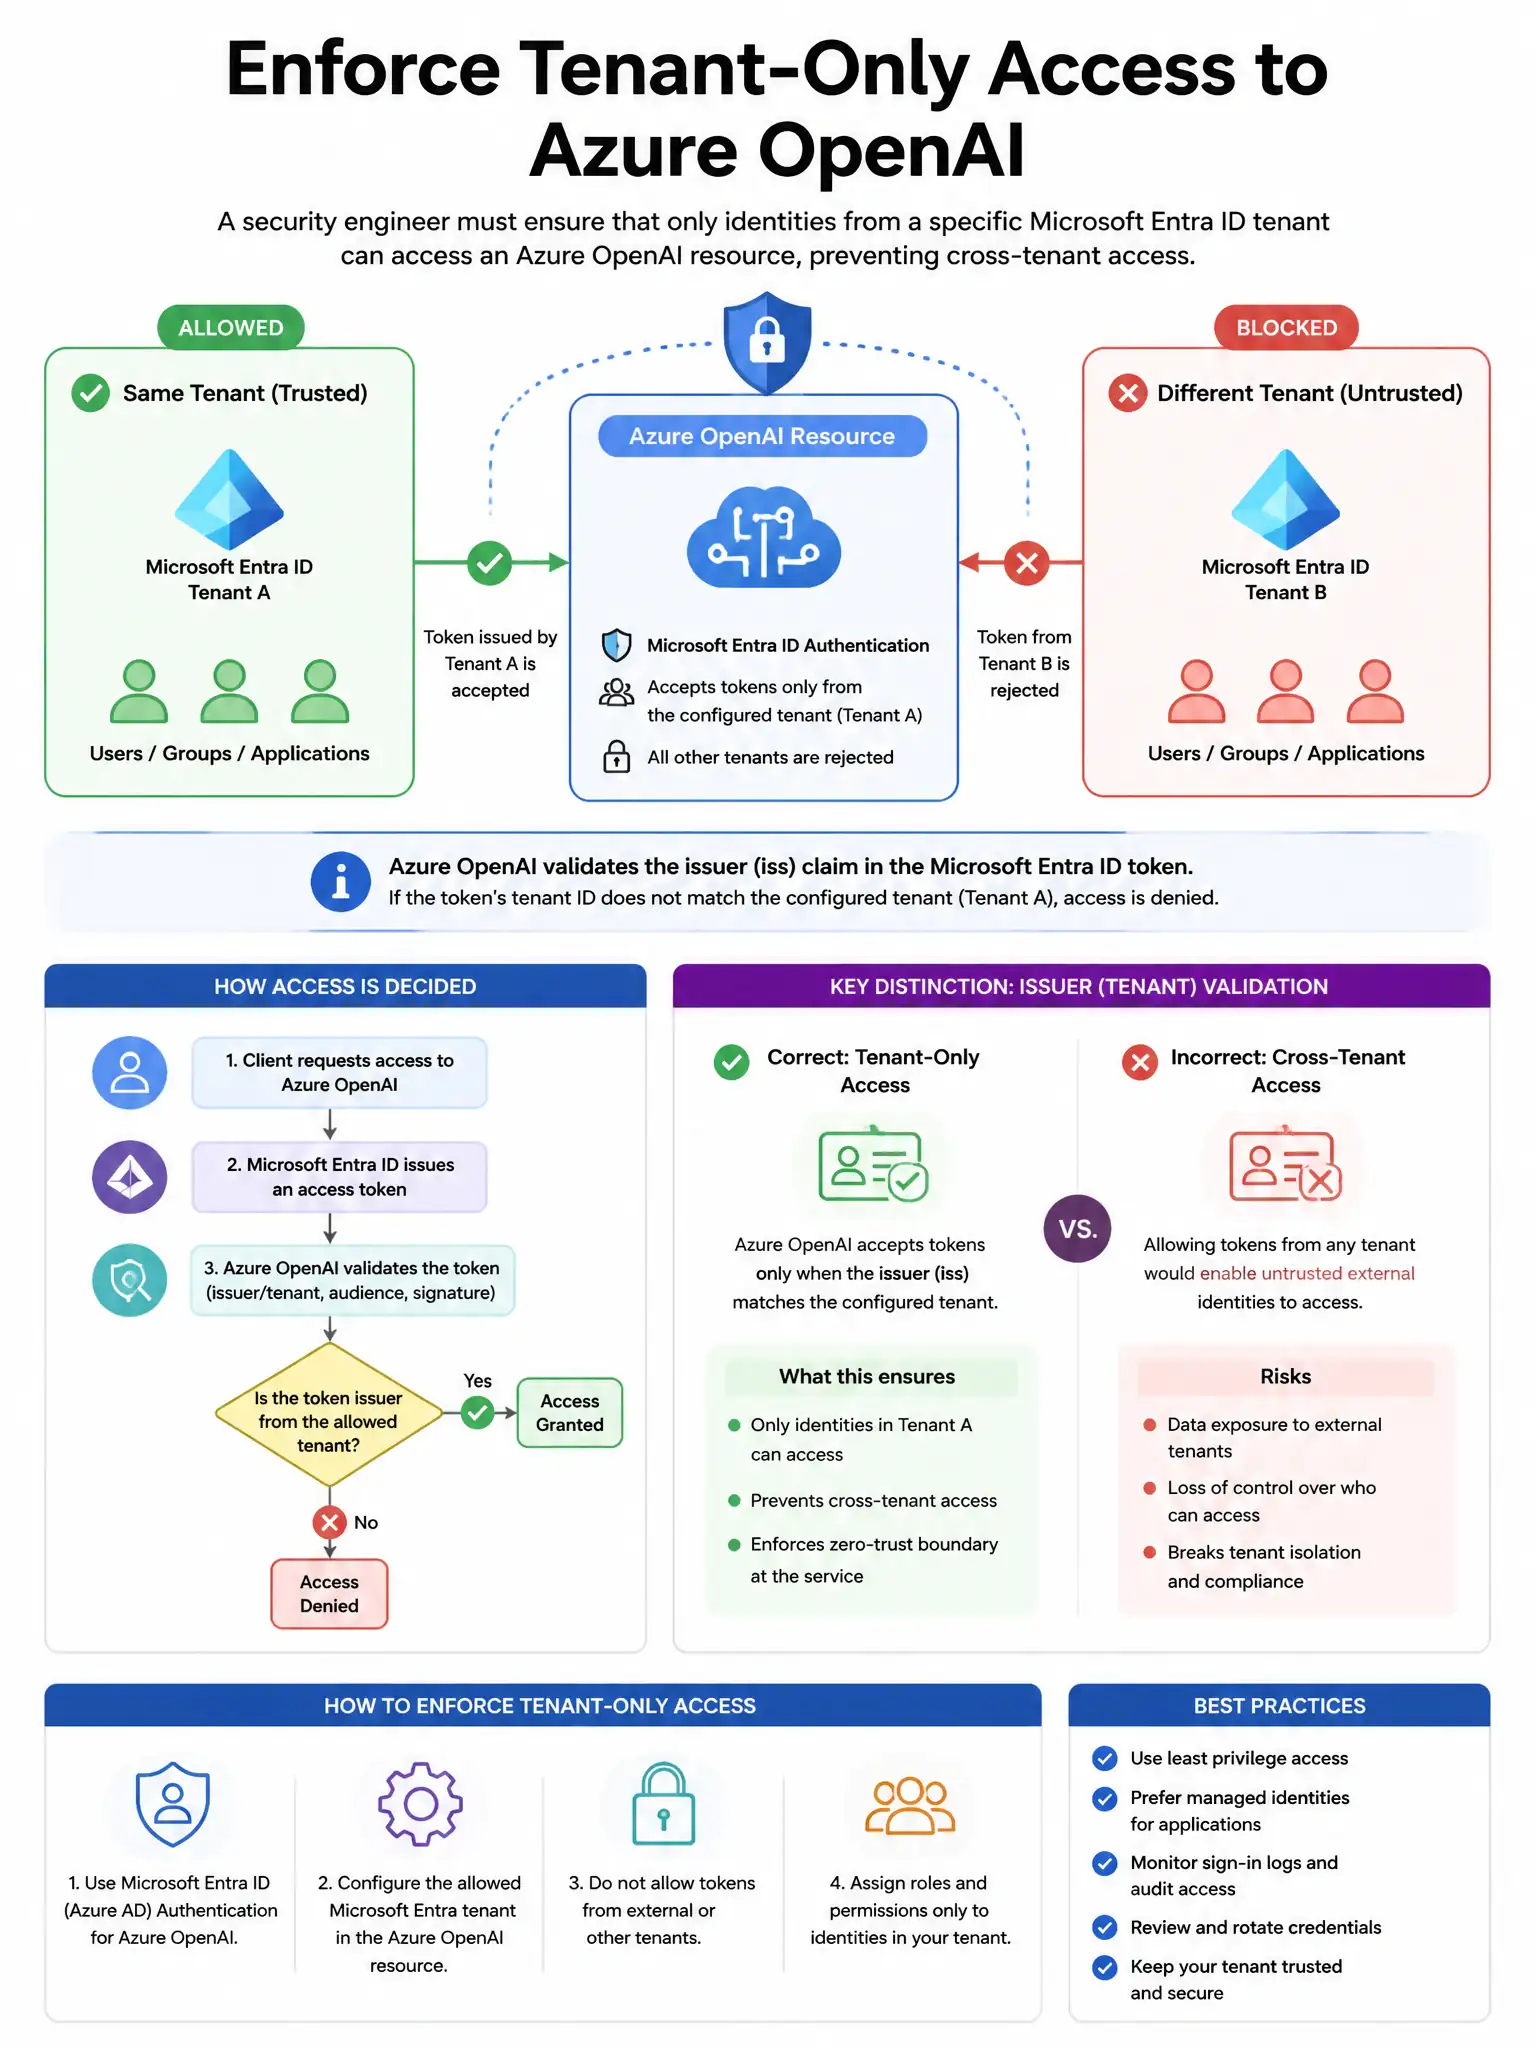
A security engineer needs to enforce that only identities within a specific Microsoft Entra ID tenant can access an Azure OpenAI resource. The organization wants to prevent cross-tenant token misuse. Which Azure OpenAI network and identity control should be implemented?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — requiring Microsoft Entra authentication and scoping a Conditional Access policy to the Azure OpenAI Service application is the right move. It makes calls use Entra identities and lets you limit token issuance to your tenant and required conditions, blocking cross-tenant token misuse.
Full Explanation
Requiring Microsoft Entra authentication and configuring tenant restriction with a Conditional Access policy scoped to the Azure OpenAI Service application is correct because disabling key-based authentication ensures that only authenticated Microsoft Entra identities can call the API. Conditional Access scoped to the Azure OpenAI Service application restricts which tenant's identities and which conditions, such as compliant devices or a specific tenant, can obtain a token for the service, preventing cross-tenant token misuse. The corporate IP firewall option is wrong because IP firewall rules block by network location, not by identity tenant; an attacker with a key and access from an allowed IP would still succeed. The API key rotation option is wrong because key-based authentication is credential-based and does not enforce tenant identity, while cross-tenant control requires identity-based authentication. The Azure Front Door geo-filtering option is wrong because geo-filtering blocks by geography, not by Microsoft Entra tenant identity.