
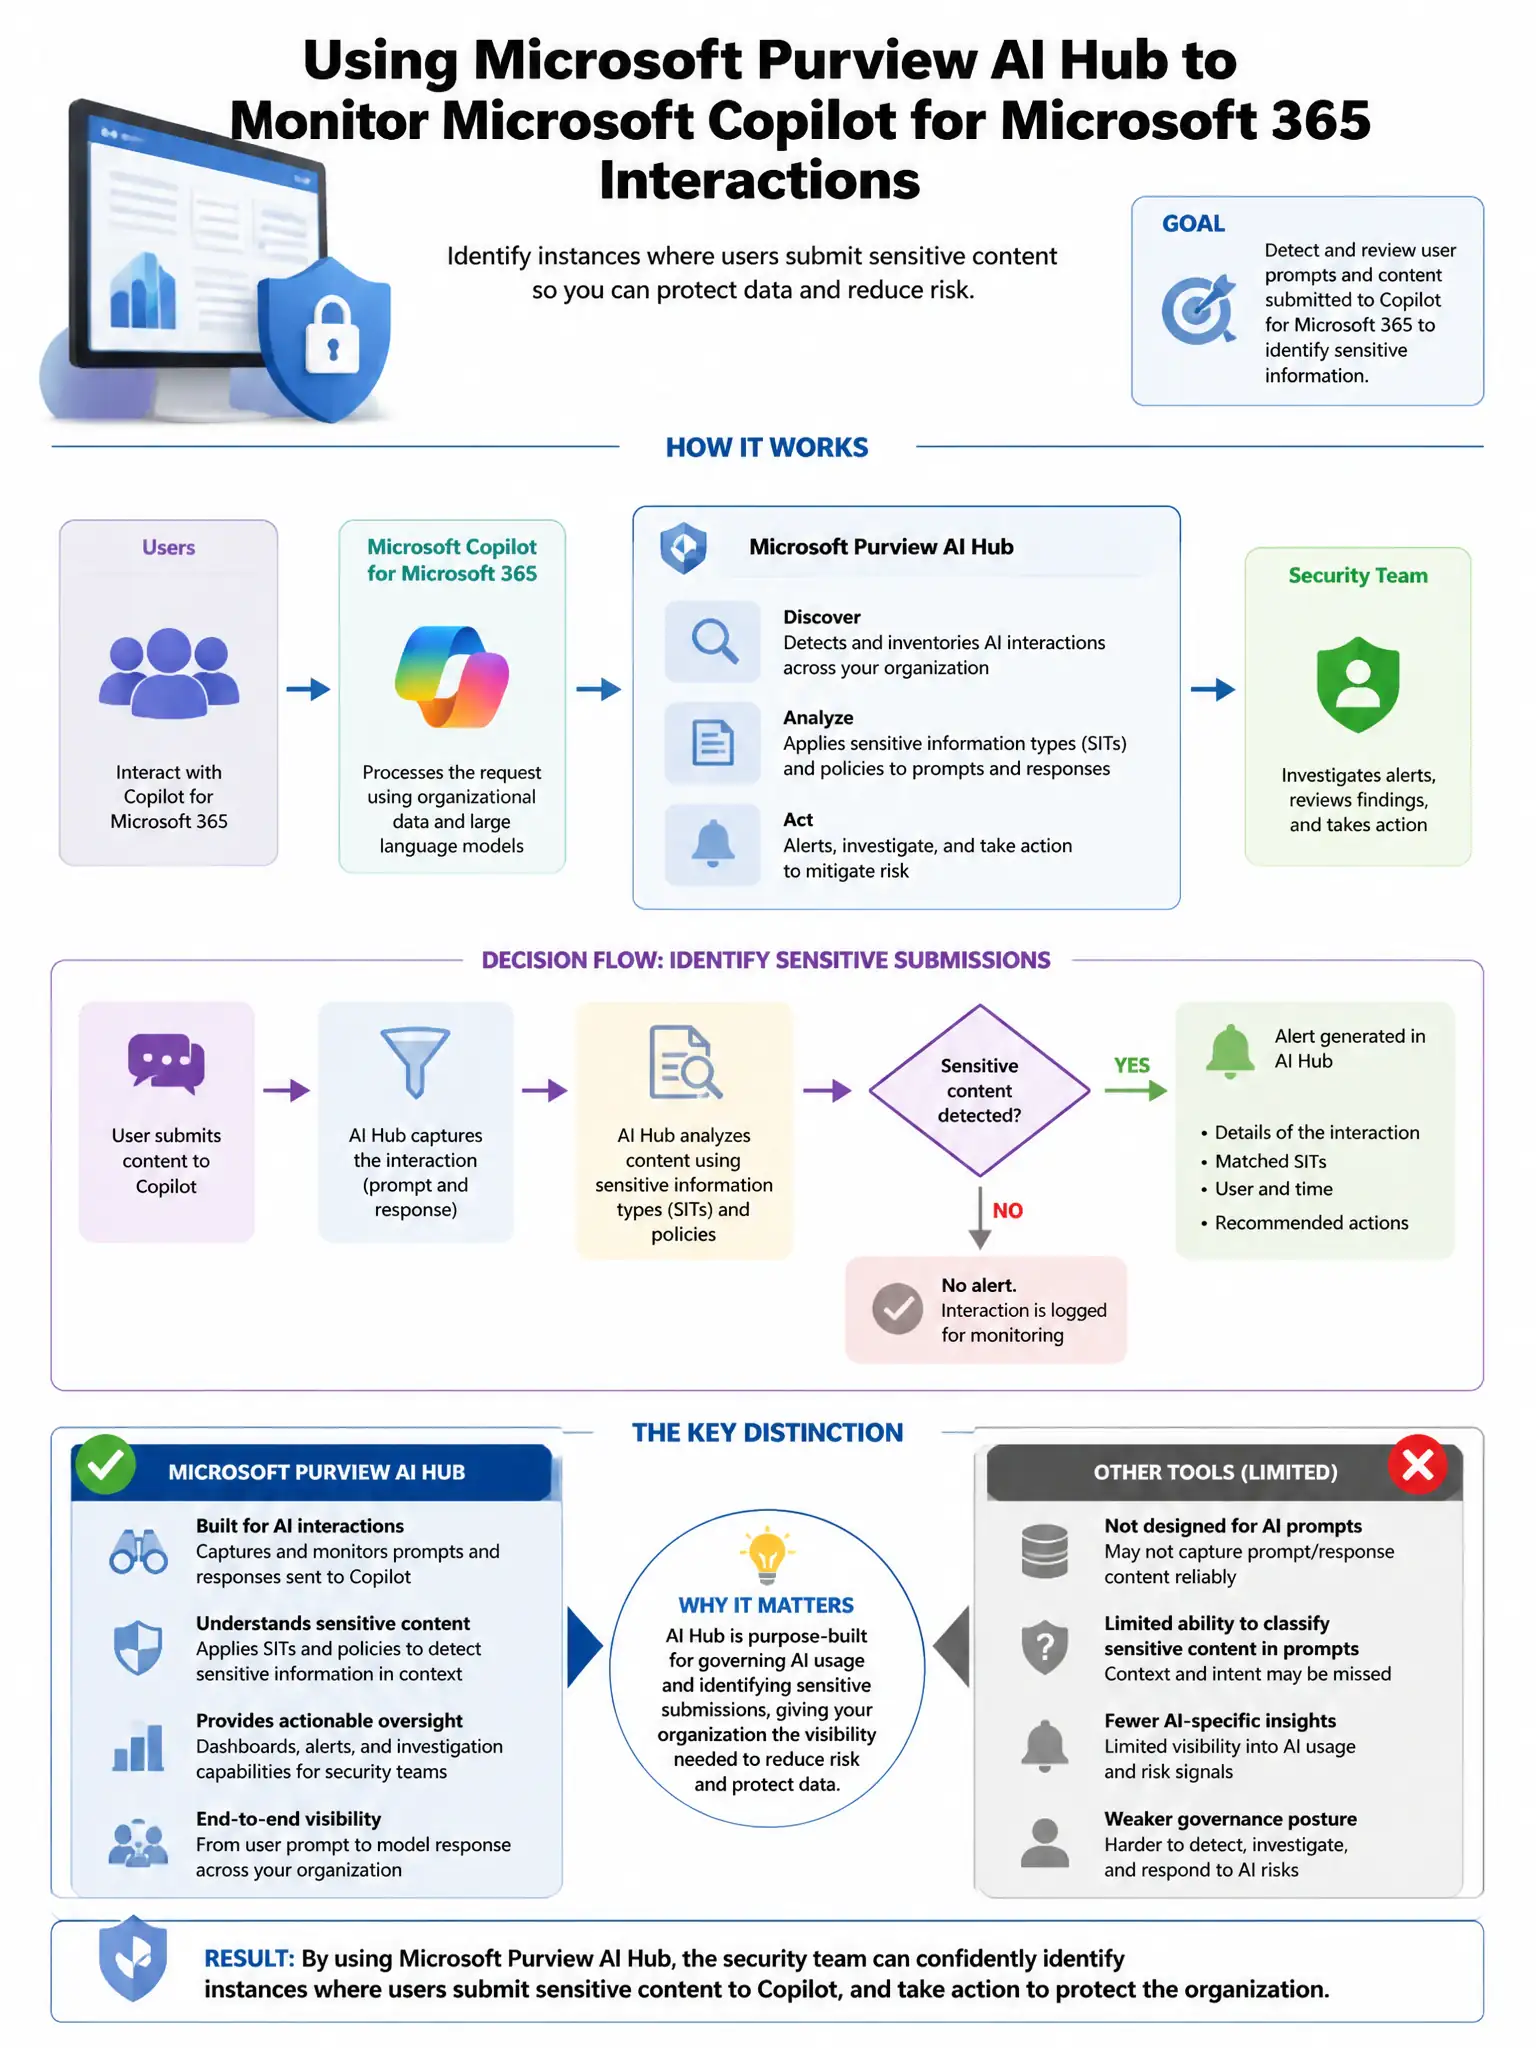
An organization is using Microsoft Purview AI Hub to monitor Microsoft Copilot for Microsoft 365 interactions. The security team wants to identify instances where users are submitting prompts that contain credit card numbers. Which Purview capability within AI Hub provides this detection?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you'll want the sensitive information type detection in AI Hub analytics because it looks at Copilot prompts for things like credit card numbers. The AI Hub dashboard surfaces those detections so you can spot data exposure risks in AI usage.
Full Explanation
The sensitive information type detection in AI Hub analytics is correct because Microsoft Purview AI Hub provides analytics specifically for AI interactions, including detection of sensitive information types (such as credit card numbers) in user prompts submitted to Copilot. The AI Hub dashboard surfaces these detections so security teams can identify data exposure risks in AI usage. Communication compliance policies are wrong because they analyze Teams messages and emails for policy violations, not specifically Copilot prompt content through the AI Hub. Microsoft Defender for Cloud Apps anomaly detection policies are wrong because they focus on app-level behavioral anomalies, not sensitive data classification within AI prompts. Data Loss Prevention endpoint policies are wrong because they prevent sensitive data from leaving endpoints via files, not from being typed into Copilot prompts (though DLP can also apply to Copilot in some configurations, AI Hub provides the specific monitoring analytics).