
A company is implementing Microsoft Entra External Identities to allow partner organizations' researchers to access an AI experimentation portal. The security team requires that partner users must satisfy the home organization's MFA before accessing the portal. Which Entra External Identities trust setting achieves this?
Select an answer to reveal the explanation.
Short Explanation
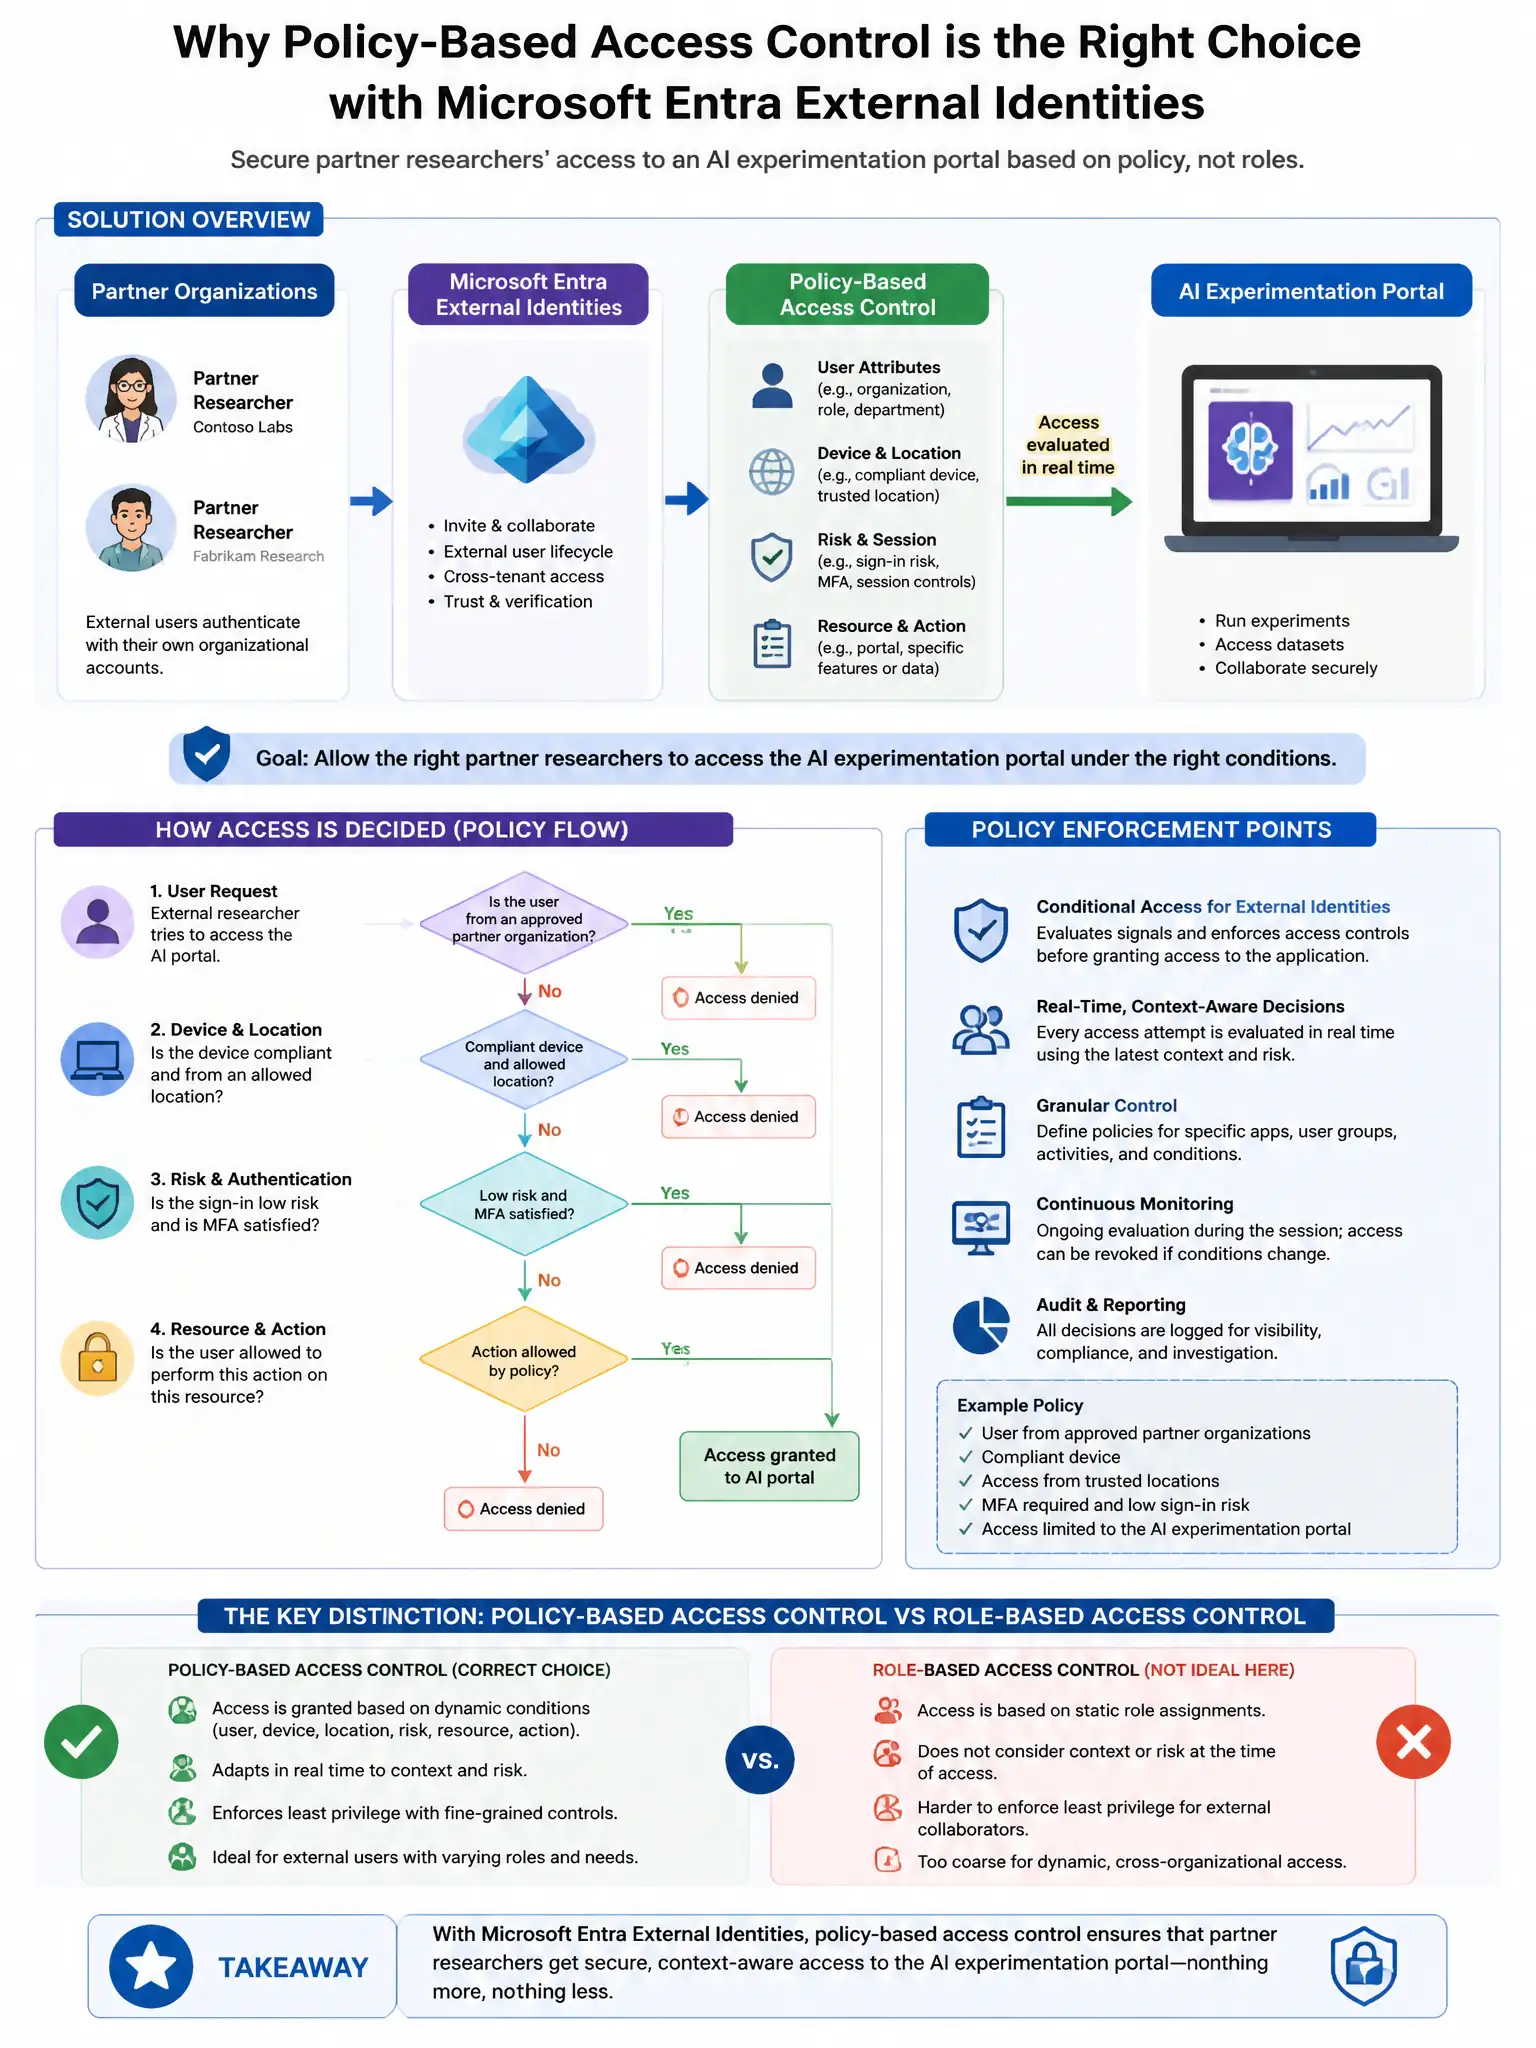
You need to configure cross-tenant access settings to trust MFA claims from the partner tenant. That way, when a partner user has already satisfied MFA at their home organization, your tenant trusts that claim and doesn't re-challenge them.
Full Explanation
The correct setting is configuring cross-tenant access settings to trust MFA claims from the partner tenant. In Entra External Identities cross-tenant access settings for inbound access, you can configure trust settings per partner tenant. Enabling trust for MFA from Microsoft Entra tenants means that when a partner user has already satisfied MFA at their home tenant, your tenant trusts that claim and does not re-challenge them. This lets the partner organization manage its own MFA policies while ensuring MFA was performed. Requiring MFA from the resource tenant for all guest users is wrong because it would force re-authentication in your tenant, overriding the home organization's MFA, which is not the requirement. The consumer-facing user-flow option is wrong because it is for consumer-facing identity scenarios, not business partner federation. The guest invitation option with one-time passcode fallback is wrong because one-time passcode is a fallback for guests without a Microsoft or social account, not an MFA trust mechanism.