
A developer needs to authenticate an application to Azure AI Search without storing credentials. The application runs on an Azure VM. Which identity approach should be used, and which Azure AI Search role grants read-only index query access?
Select an answer to reveal the explanation.
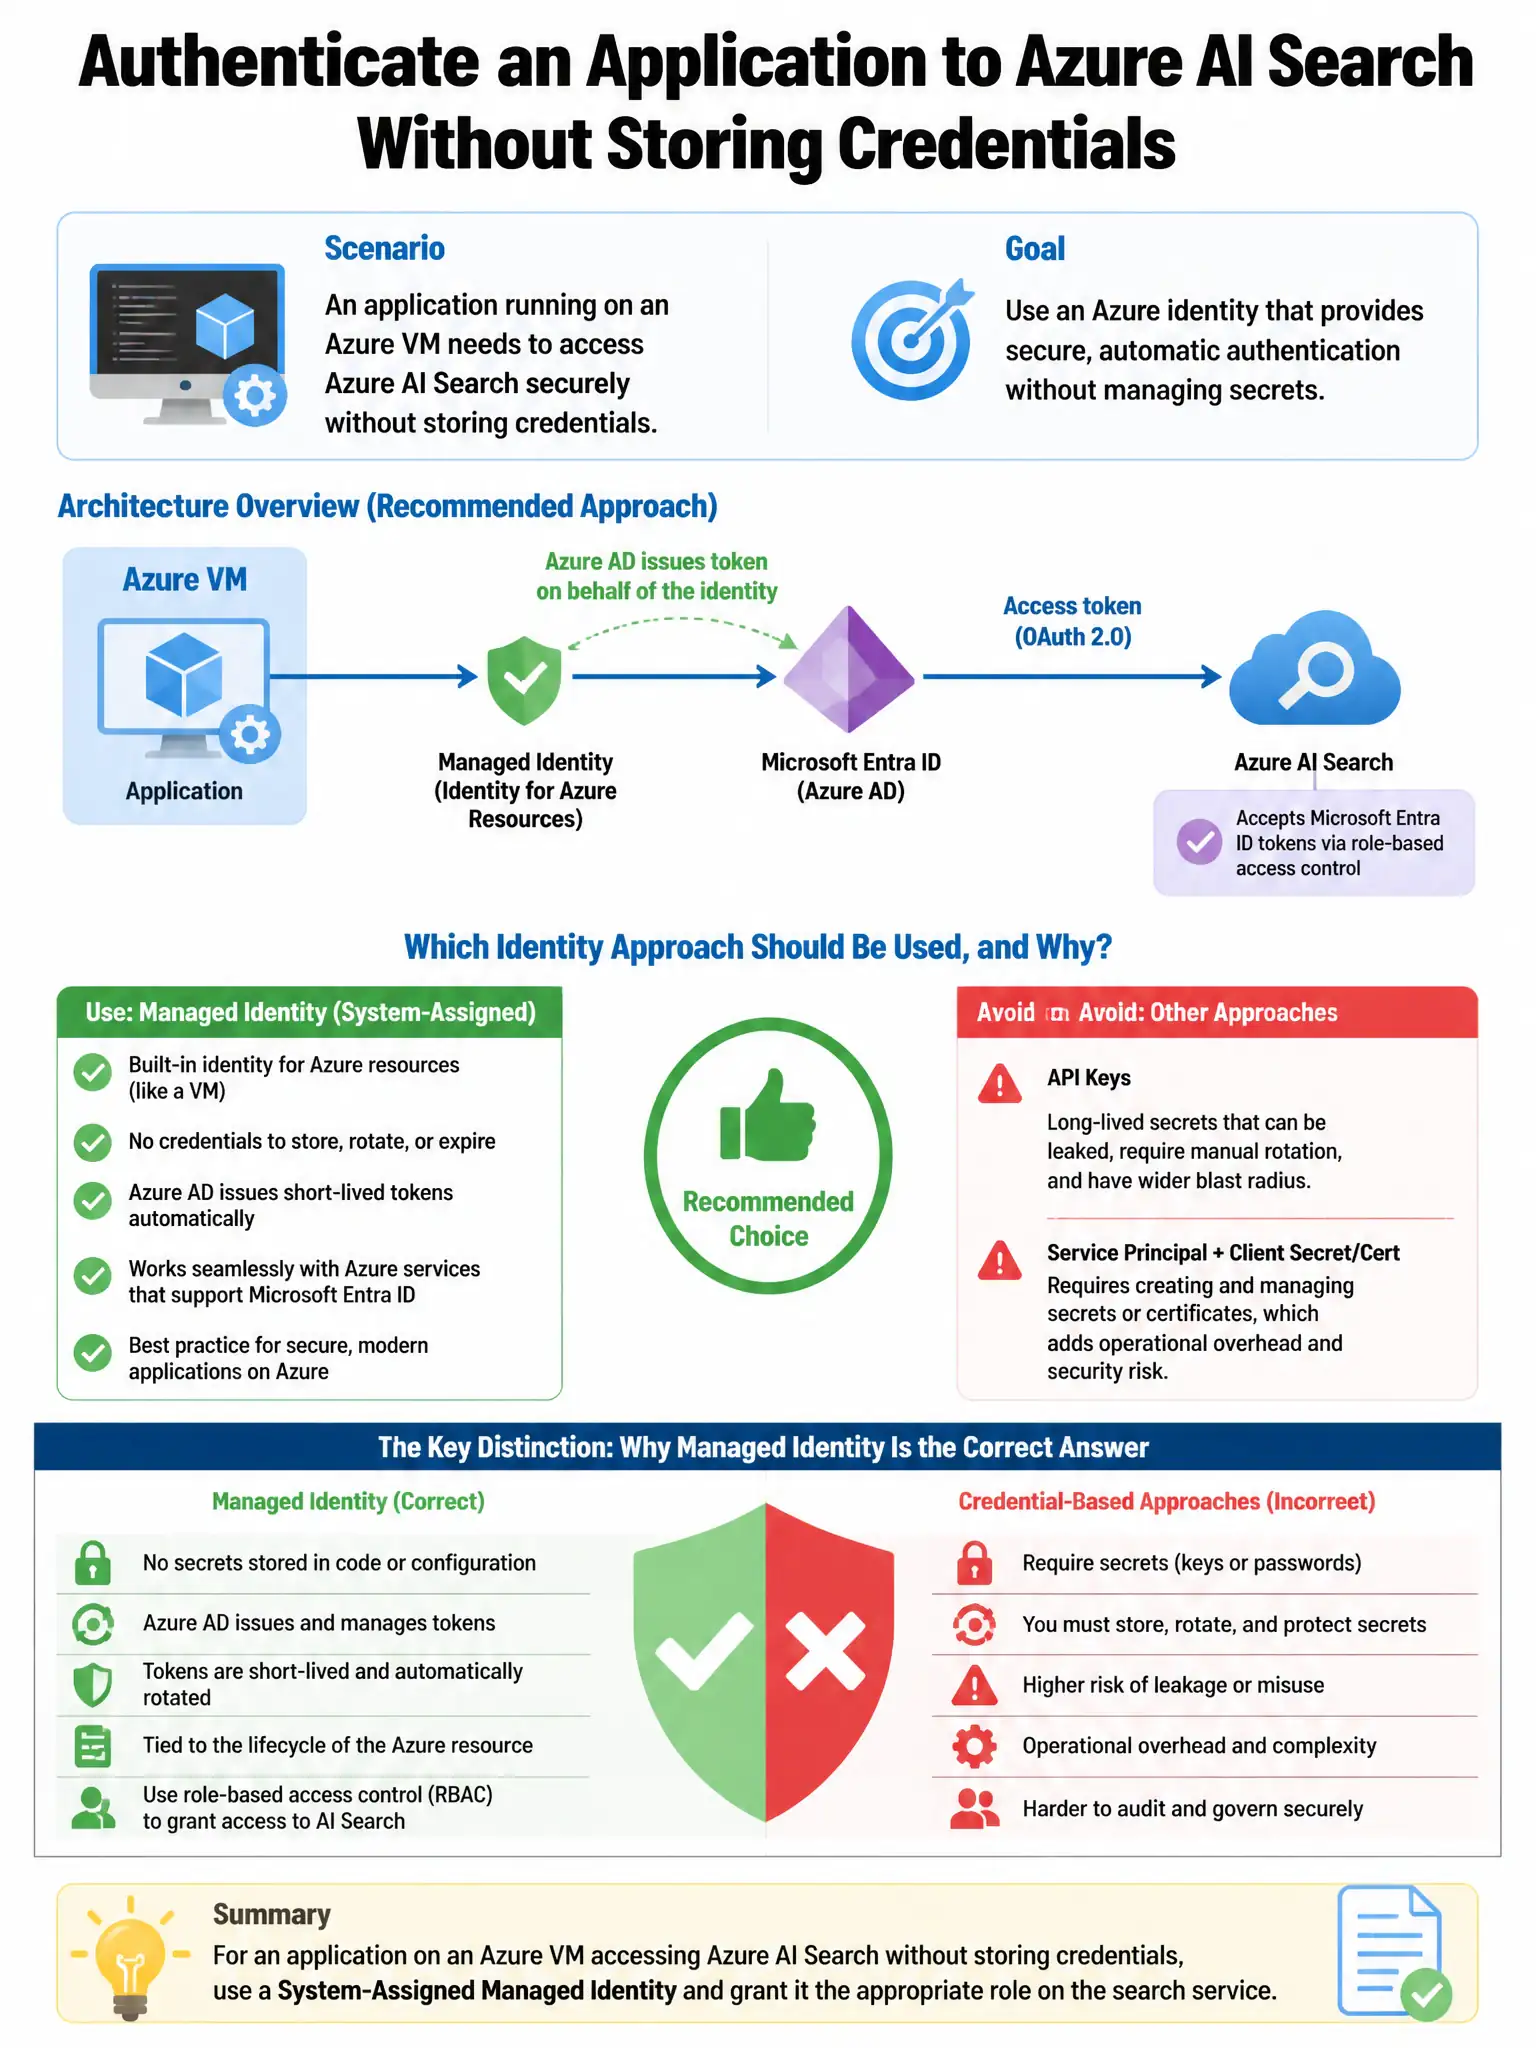
Short Explanation
Here's the deal — you want the system-assigned managed identity on the Azure VM and the Search Index Data Reader role. The managed identity removes stored credentials, and Search Index Data Reader gives read-only query access to the index.
Full Explanation
The correct approach is the system-assigned managed identity on the Azure VM paired with the Search Index Data Reader role. The system-assigned managed identity eliminates the need to store credentials because the identity is tied to the VM lifecycle and authenticates automatically using the Azure Instance Metadata Service. Search Index Data Reader grants query (read) access to an Azure AI Search index without allowing modifications. The service principal with client secret and Search Service Contributor approach is wrong because service principals with client secrets require storing and rotating secrets, violating the no-credentials requirement, and Search Service Contributor is not the read-only data query role. The user-assigned managed identity with Search Service Owner approach is wrong because Search Service Owner is an overprivileged administrative role, violating least privilege. The workload identity federation with Search Index Data Contributor approach is wrong because Workload Identity Federation is used for non-Azure workloads, like GitHub Actions, to trust external identity providers, not for Azure VM workloads, and Search Index Data Contributor does not provide read-only query access.