
An organization wants to implement periodic reviews of which users have access to an AI model access group in Microsoft Entra ID. If a reviewer does not respond, access should be automatically removed. Which feature implements this?
Select an answer to reveal the explanation.
Short Explanation
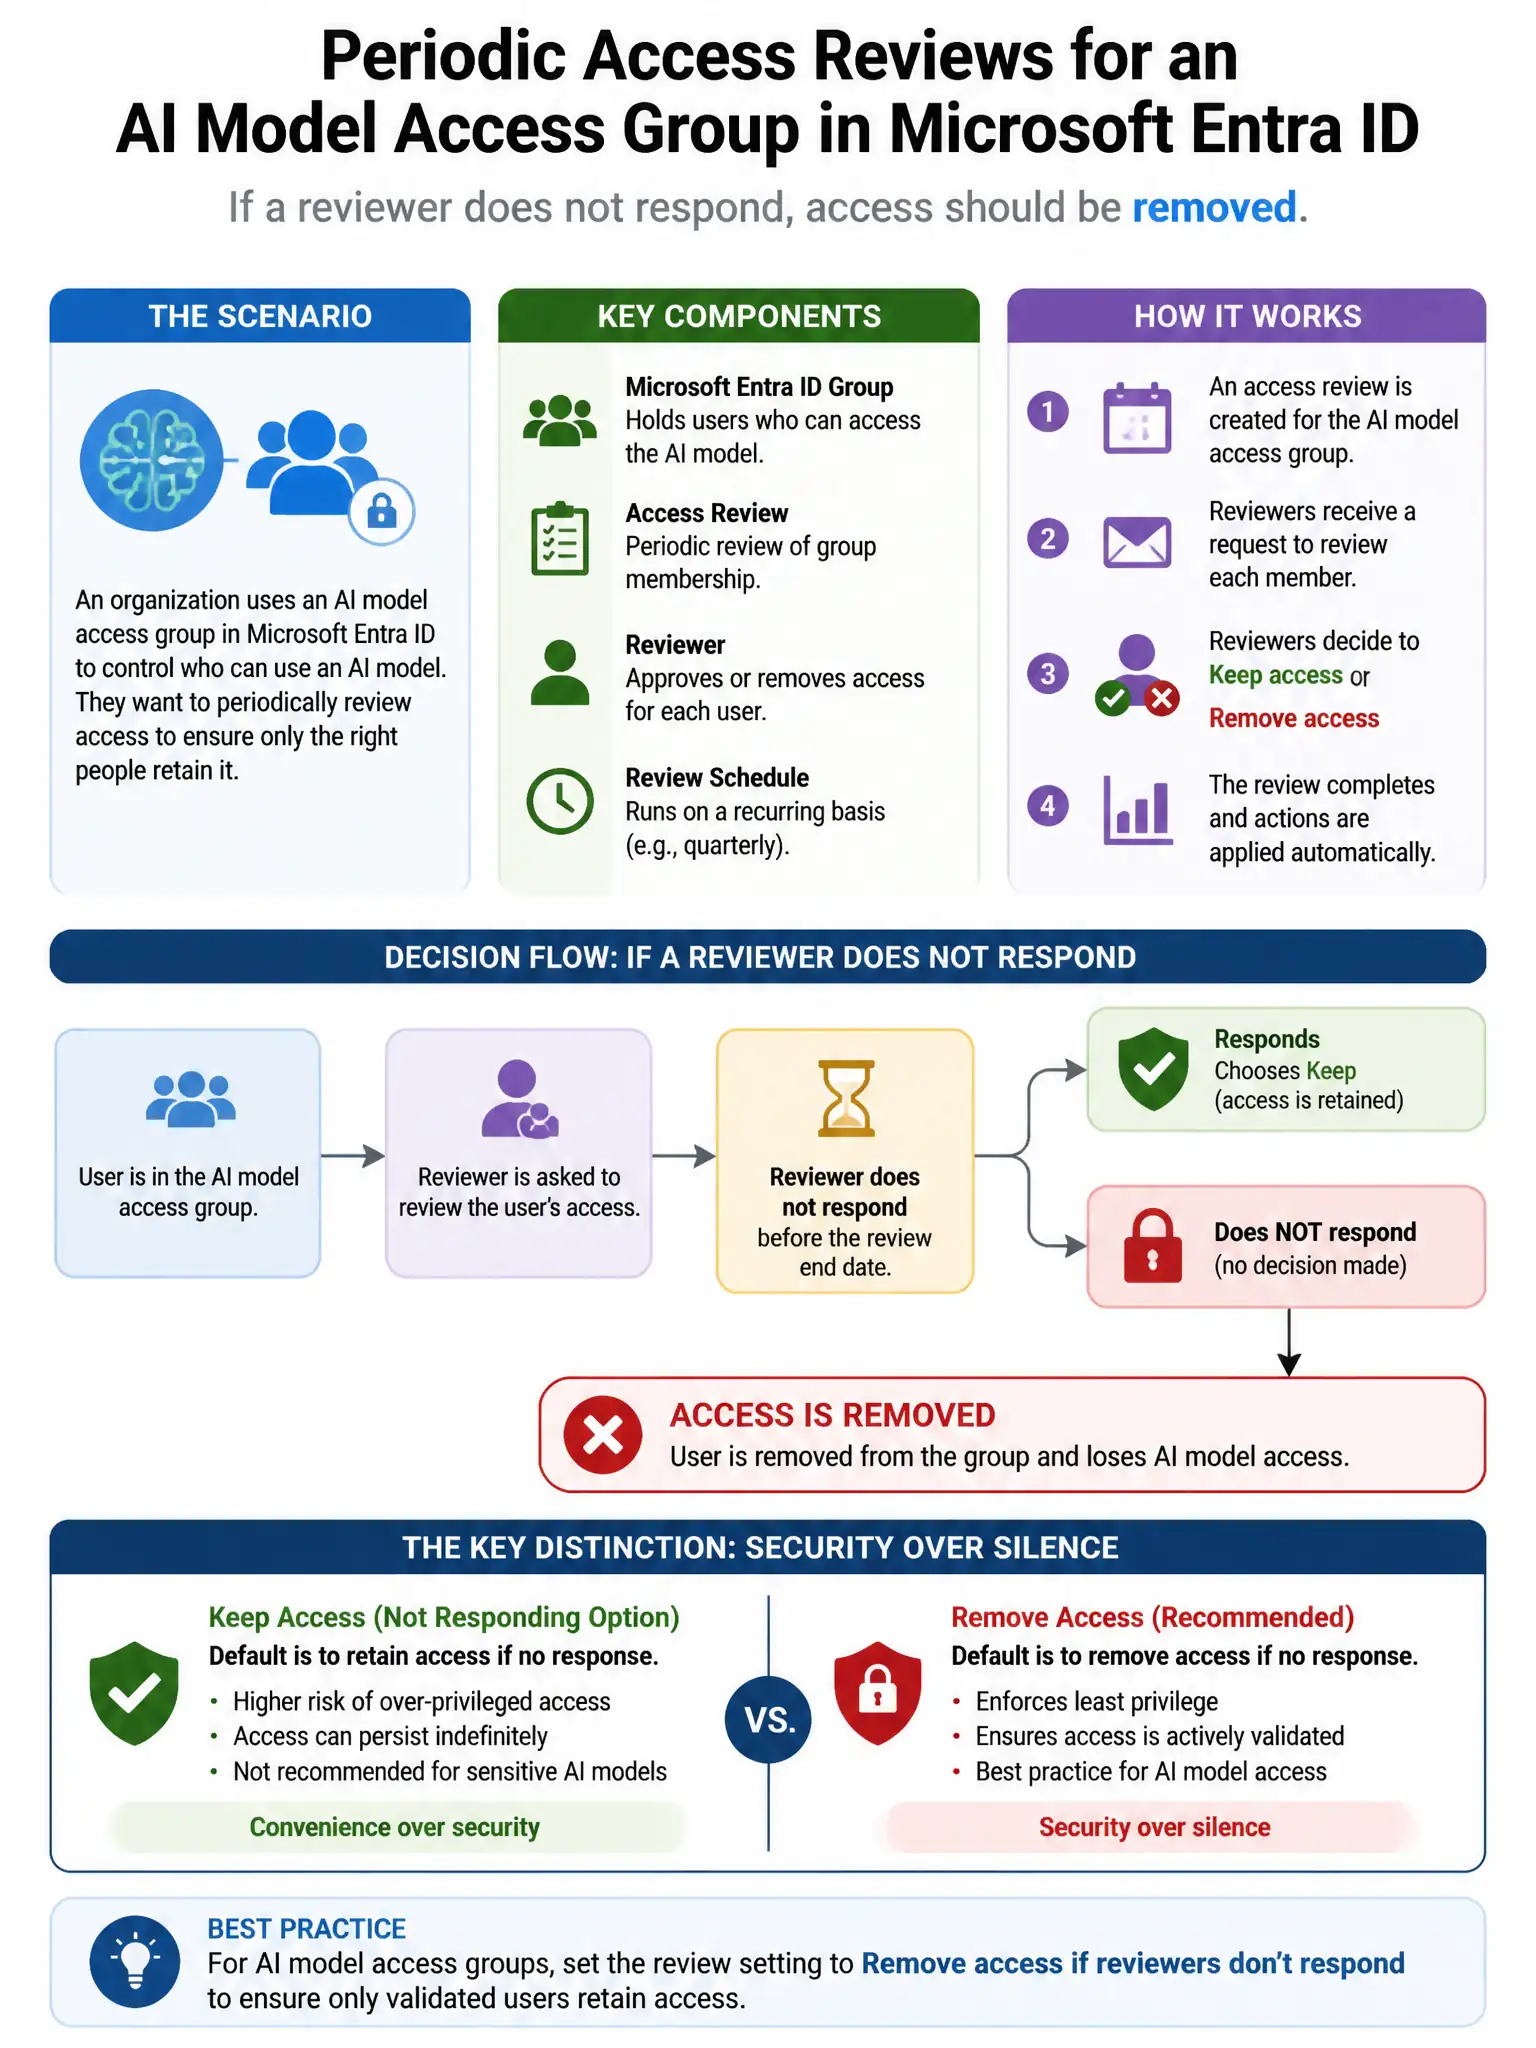
Here's the deal — you want Microsoft Entra ID Governance access reviews with 'Remove access' configured for no-response. It lets you schedule periodic reviews, and if nobody approves a user, that access gets pulled automatically.
Full Explanation
The correct feature is Microsoft Entra ID Governance access reviews with 'Remove access' configured for no-response, because Access Reviews allow administrators to schedule periodic reviews where resource owners or managers certify user access. When configured with the 'Apply results to resource' setting and 'Remove access' for non-respondents, users whose access is not explicitly approved are automatically removed after the review period. The Microsoft Entra ID Protection user risk policy option is wrong because user risk policies block sign-ins based on risk signals, not scheduled access certification. The Microsoft Entra PIM role expiration settings option is wrong because PIM expiration applies to eligible or active role assignments, not general group memberships. The Conditional Access authentication context option is wrong because authentication context steps up authentication requirements for specific scenarios; it does not certify group membership.