
An organization's AI platform team uses a user-assigned managed identity to authenticate Azure Functions to Azure OpenAI Service. A security review finds that the managed identity also has Contributor access at the subscription level from a previous misconfiguration. What is the correct remediation?
Select an answer to reveal the explanation.
Short Explanation
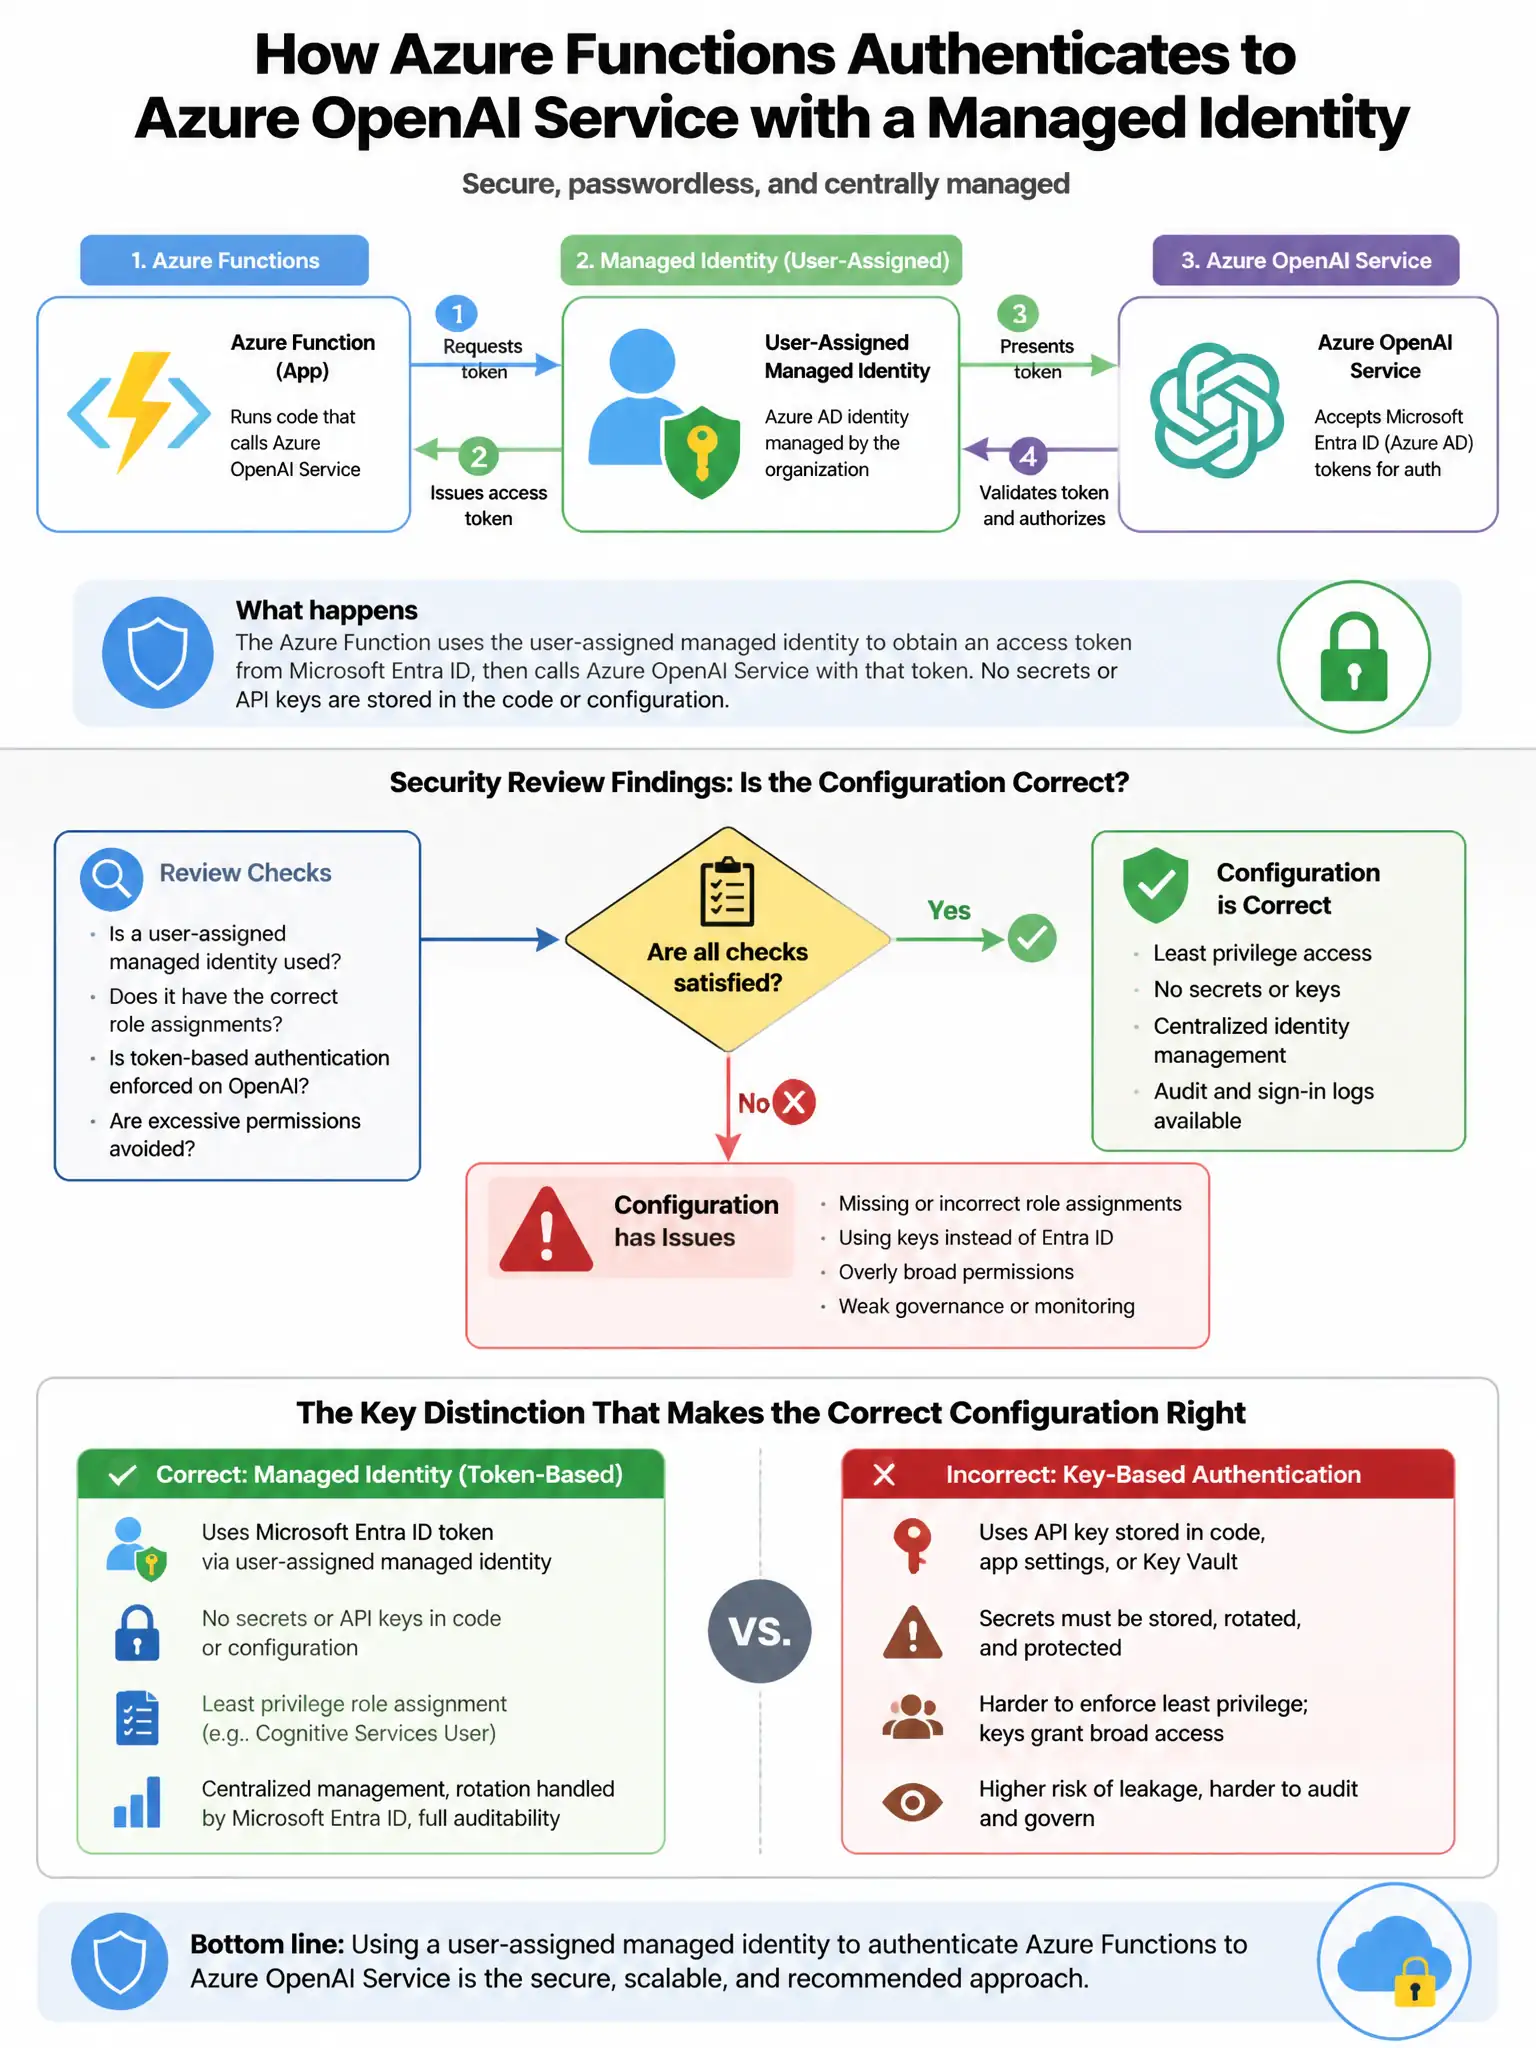
Here's the deal — you should remove the subscription-level Contributor role and scope the managed identity to only the Cognitive Services OpenAI User role on the specific Azure OpenAI resource. That follows least privilege and stops the identity from creating, modifying, or deleting resources across the subscription.
Full Explanation
The correct remediation is to remove the Contributor role assignment at the subscription level and restrict the managed identity to only the Cognitive Services OpenAI User role on the specific Azure OpenAI resource. The principle of least privilege requires removing excessive permissions. The managed identity should have only the 'Cognitive Services OpenAI User' role scoped to the specific Azure OpenAI resource, not Contributor at the subscription level, which would allow it to create, modify, or delete any resource in the subscription. Rotating the managed identity credentials is wrong because managed identities do not have credentials to rotate—their tokens are issued automatically by the Azure platform; the problem is the role assignment, not a credential. Converting the user-assigned managed identity to a system-assigned managed identity is wrong because it changes the lifecycle management but does not fix the excessive role assignment. Enabling Conditional Access for managed identities is wrong because Conditional Access does not apply to managed identity service principal token requests.