
Microsoft Entra ID Protection has flagged a high-risk sign-in for a user who regularly accesses Azure Machine Learning Studio. The security engineer wants to automatically block high-risk sign-ins without requiring manual intervention. Which policy type in Entra ID Protection achieves this?
Select an answer to reveal the explanation.
Short Explanation
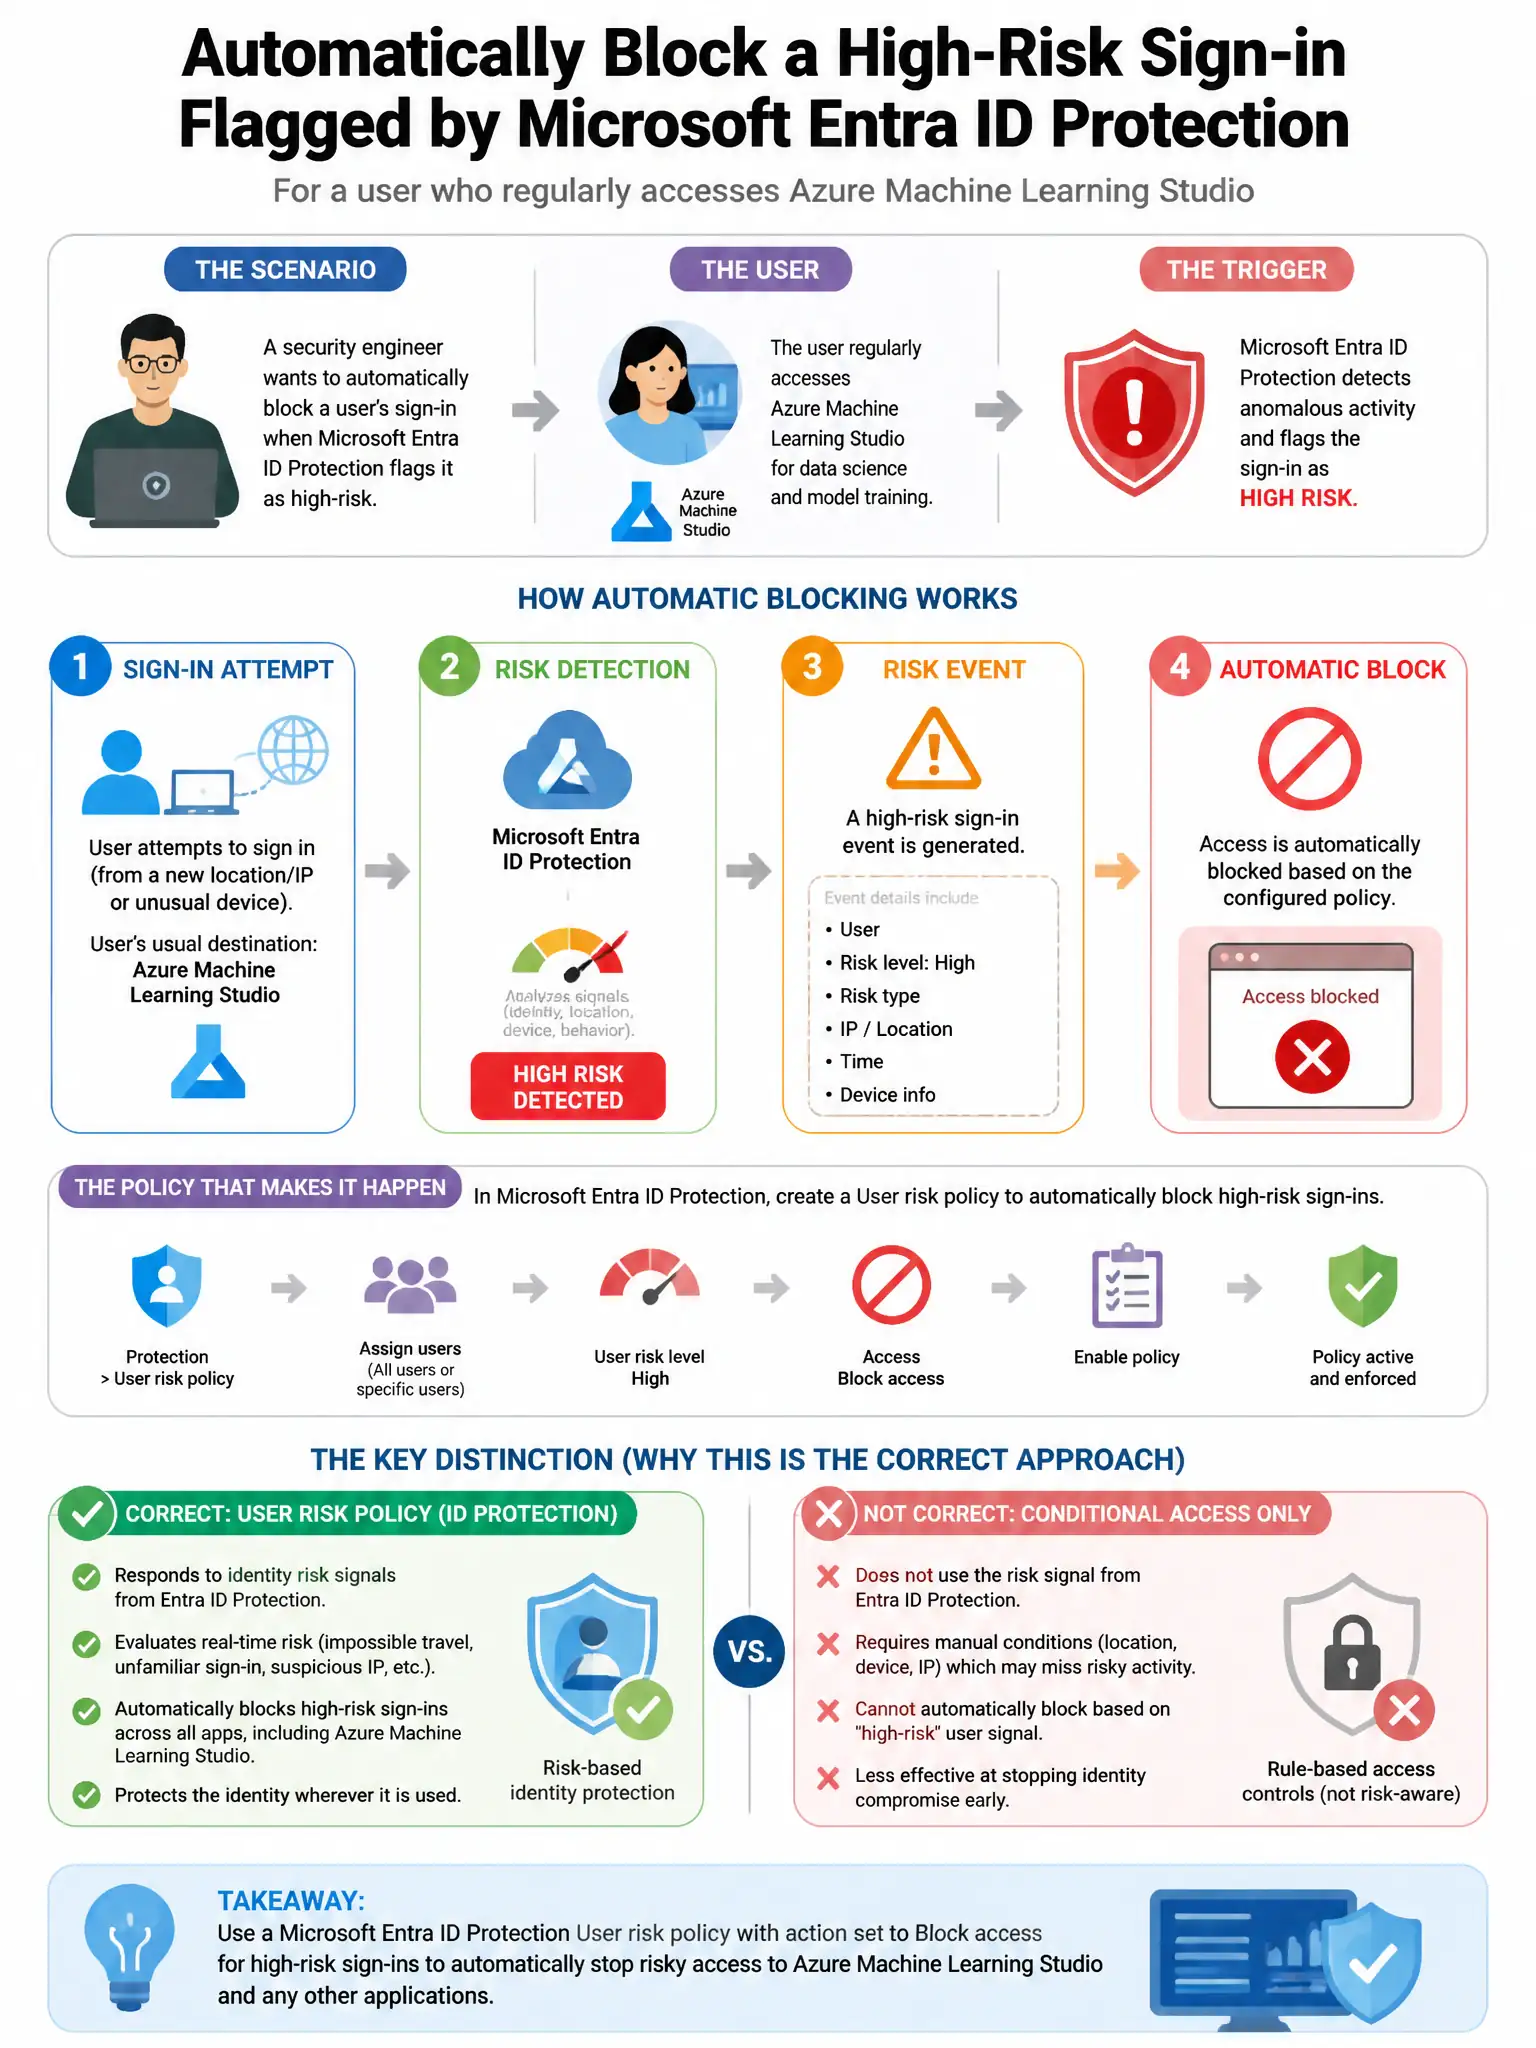
Here's the deal — you want the sign-in risk policy that blocks access at high risk, because it automatically stops the risky sign-in without an analyst stepping in. That's the direct fix for a high-risk sign-in hitting Azure Machine Learning Studio.
Full Explanation
The correct choice is the sign-in risk policy blocking access at high risk, because Entra ID Protection can evaluate each sign-in and automatically block access when the sign-in risk level is 'High,' providing automated remediation without requiring an analyst to manually intervene. This directly addresses the high-risk sign-in scenario. The user risk policy requiring password change at medium risk is wrong because a user risk policy evaluates the user's overall risk accumulated from multiple events, not a single high-risk sign-in event, and it remediates via password change rather than blocking. The conditional access policy requiring multi-factor authentication for all sign-ins is wrong because requiring multi-factor authentication for all sign-ins does not block high-risk sessions; it requires multi-factor authentication and would allow access after authentication, not block it. The access review triggered by high-risk detection is wrong because access reviews periodically validate role memberships and do not respond to real-time risk detections.