
An organization uses Azure OpenAI Service and wants to ensure that only specific service principals can call the Azure OpenAI API. The developer team should be blocked from accessing the API key directly. Which combination of controls achieves this?
Select an answer to reveal the explanation.
Short Explanation
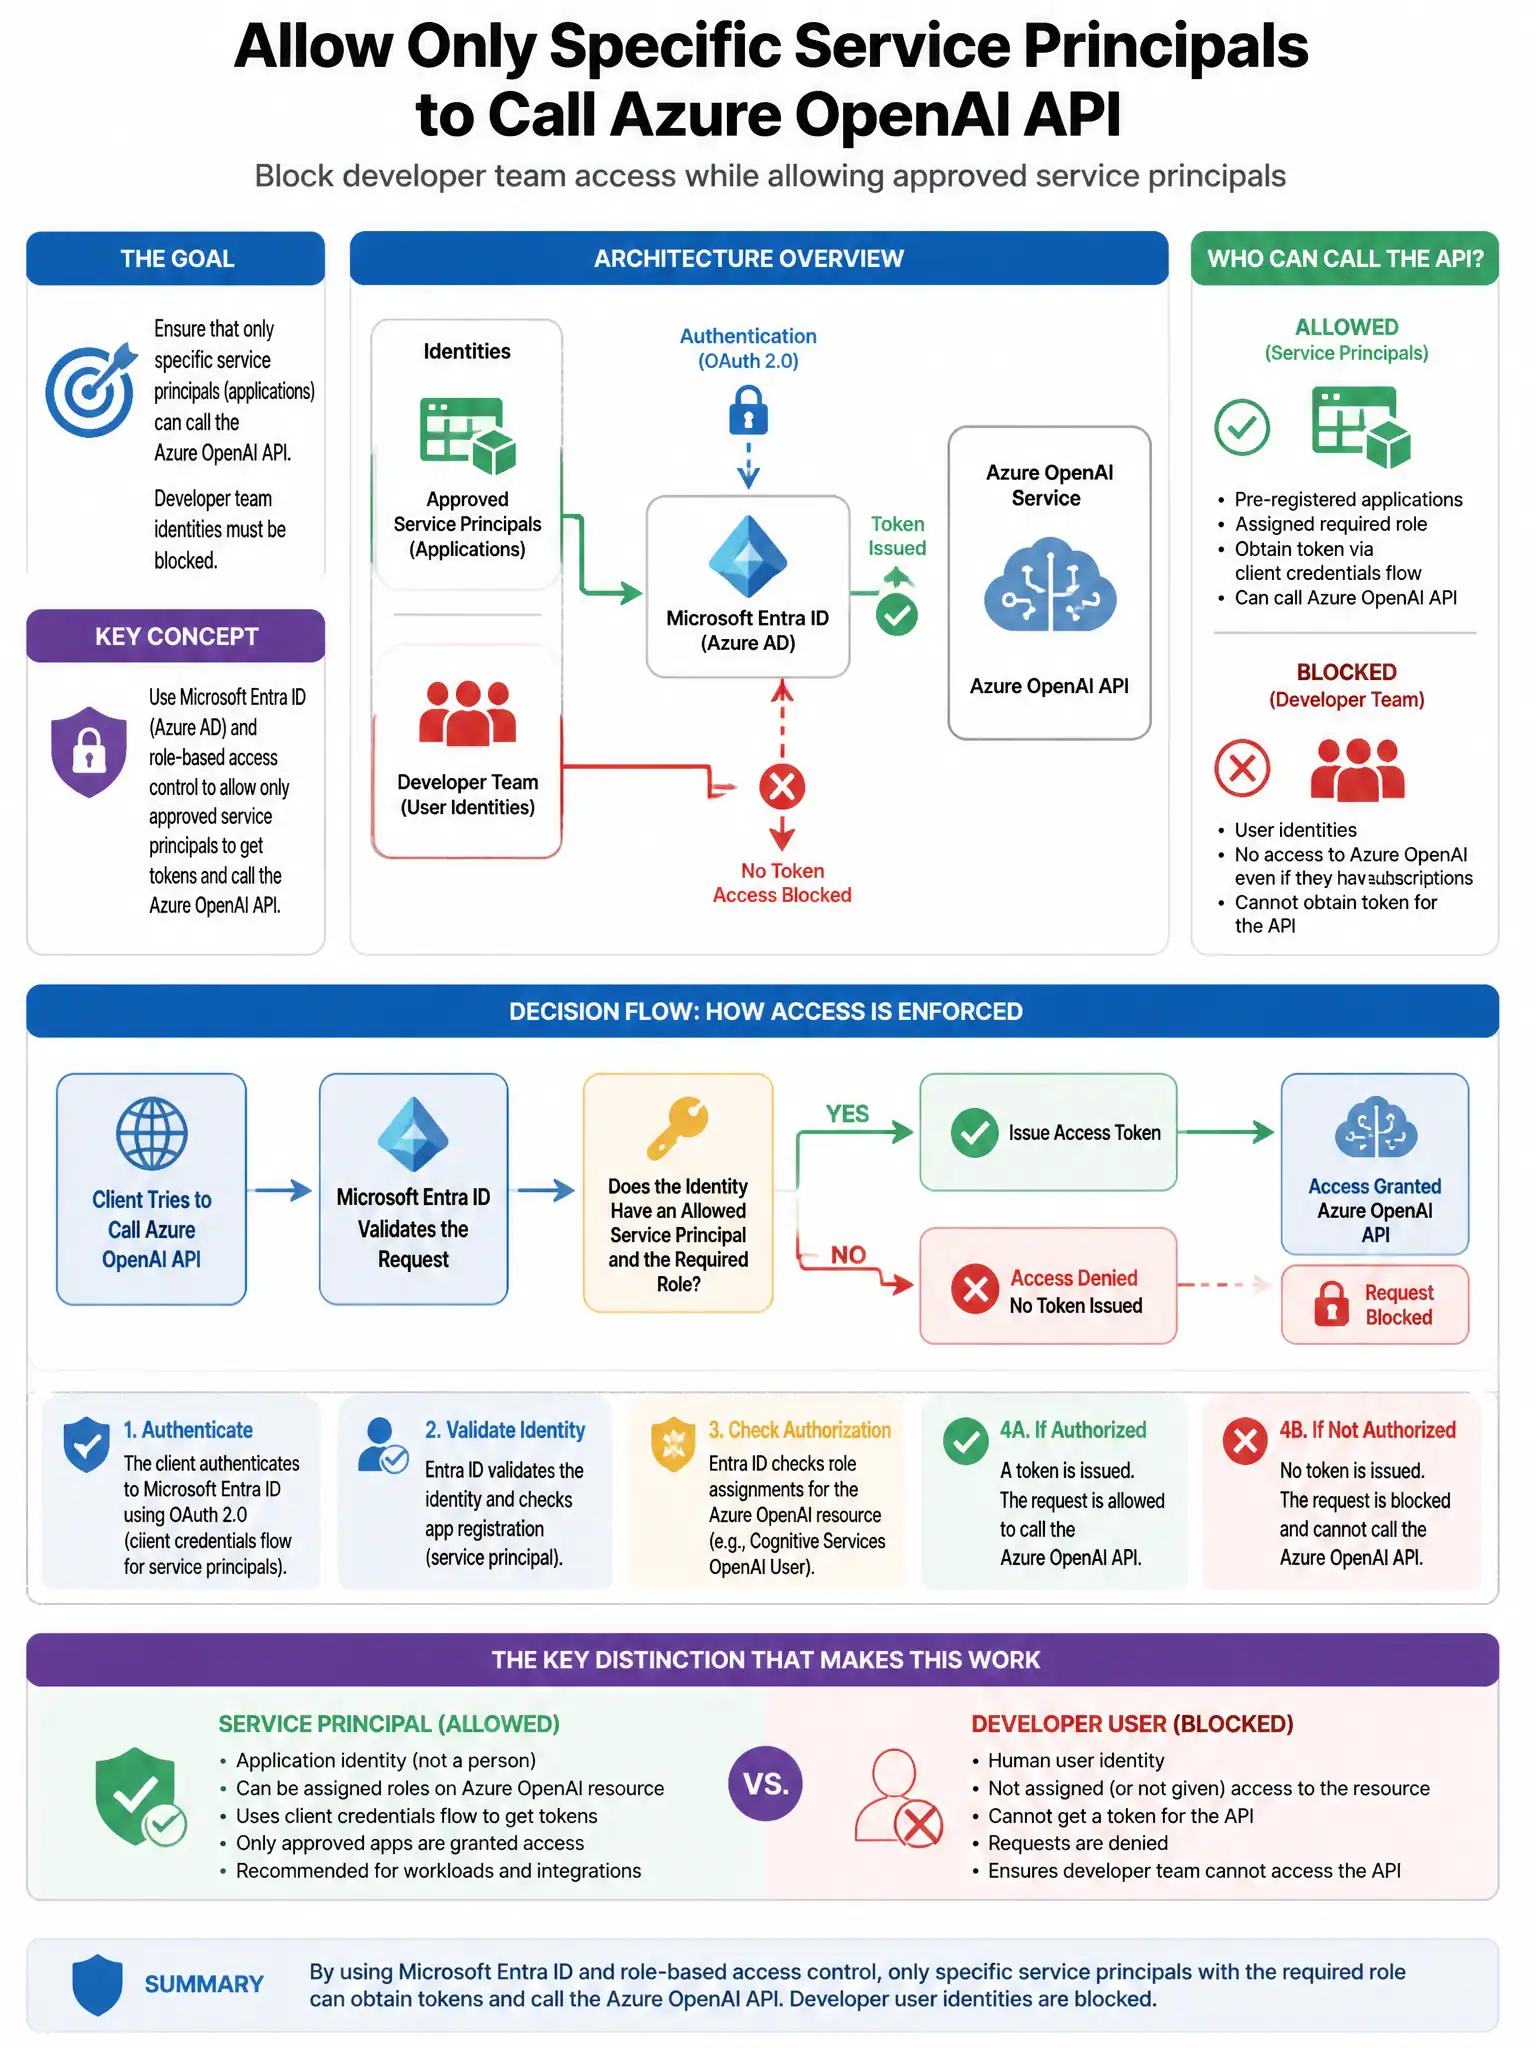
You want to kill API-key access at the resource level and let only approved service principals use Entra ID tokens with the Cognitive Services OpenAI User role. That blocks developers from grabbing keys and gives least-privilege API access.
Full Explanation
The correct combination is disabling API key access at the resource level and assigning the Cognitive Services OpenAI User role to approved service principals. Azure OpenAI Service supports disabling key-based authentication at the resource level (setting 'disable local authentication' to true), forcing all callers to use Microsoft Entra ID tokens. Assigning the Cognitive Services OpenAI User role to only approved service principals ensures least-privilege token-based access. The option about rotating API keys weekly and storing them in Azure Key Vault is wrong because rotating API keys and using Key Vault still allows key-based access; it does not block developers from using keys if they have Key Vault access. The option about using Conditional Access to block developer sign-in to Azure OpenAI is wrong because Conditional Access does not apply to API calls made by service principals, only to interactive user sign-ins. The option about enabling Microsoft Entra ID authentication and assigning the Cognitive Services Contributor role to service principals is wrong because the Cognitive Services Contributor role is an administrative role that grants management plane access, not just API inference access.