
A global enterprise wants to enforce Multi-Factor Authentication for all users accessing Azure AI Studio. The policy must exclude break-glass emergency accounts. The company uses Microsoft Entra ID. Which Conditional Access policy configuration is correct?
Select an answer to reveal the explanation.
Short Explanation
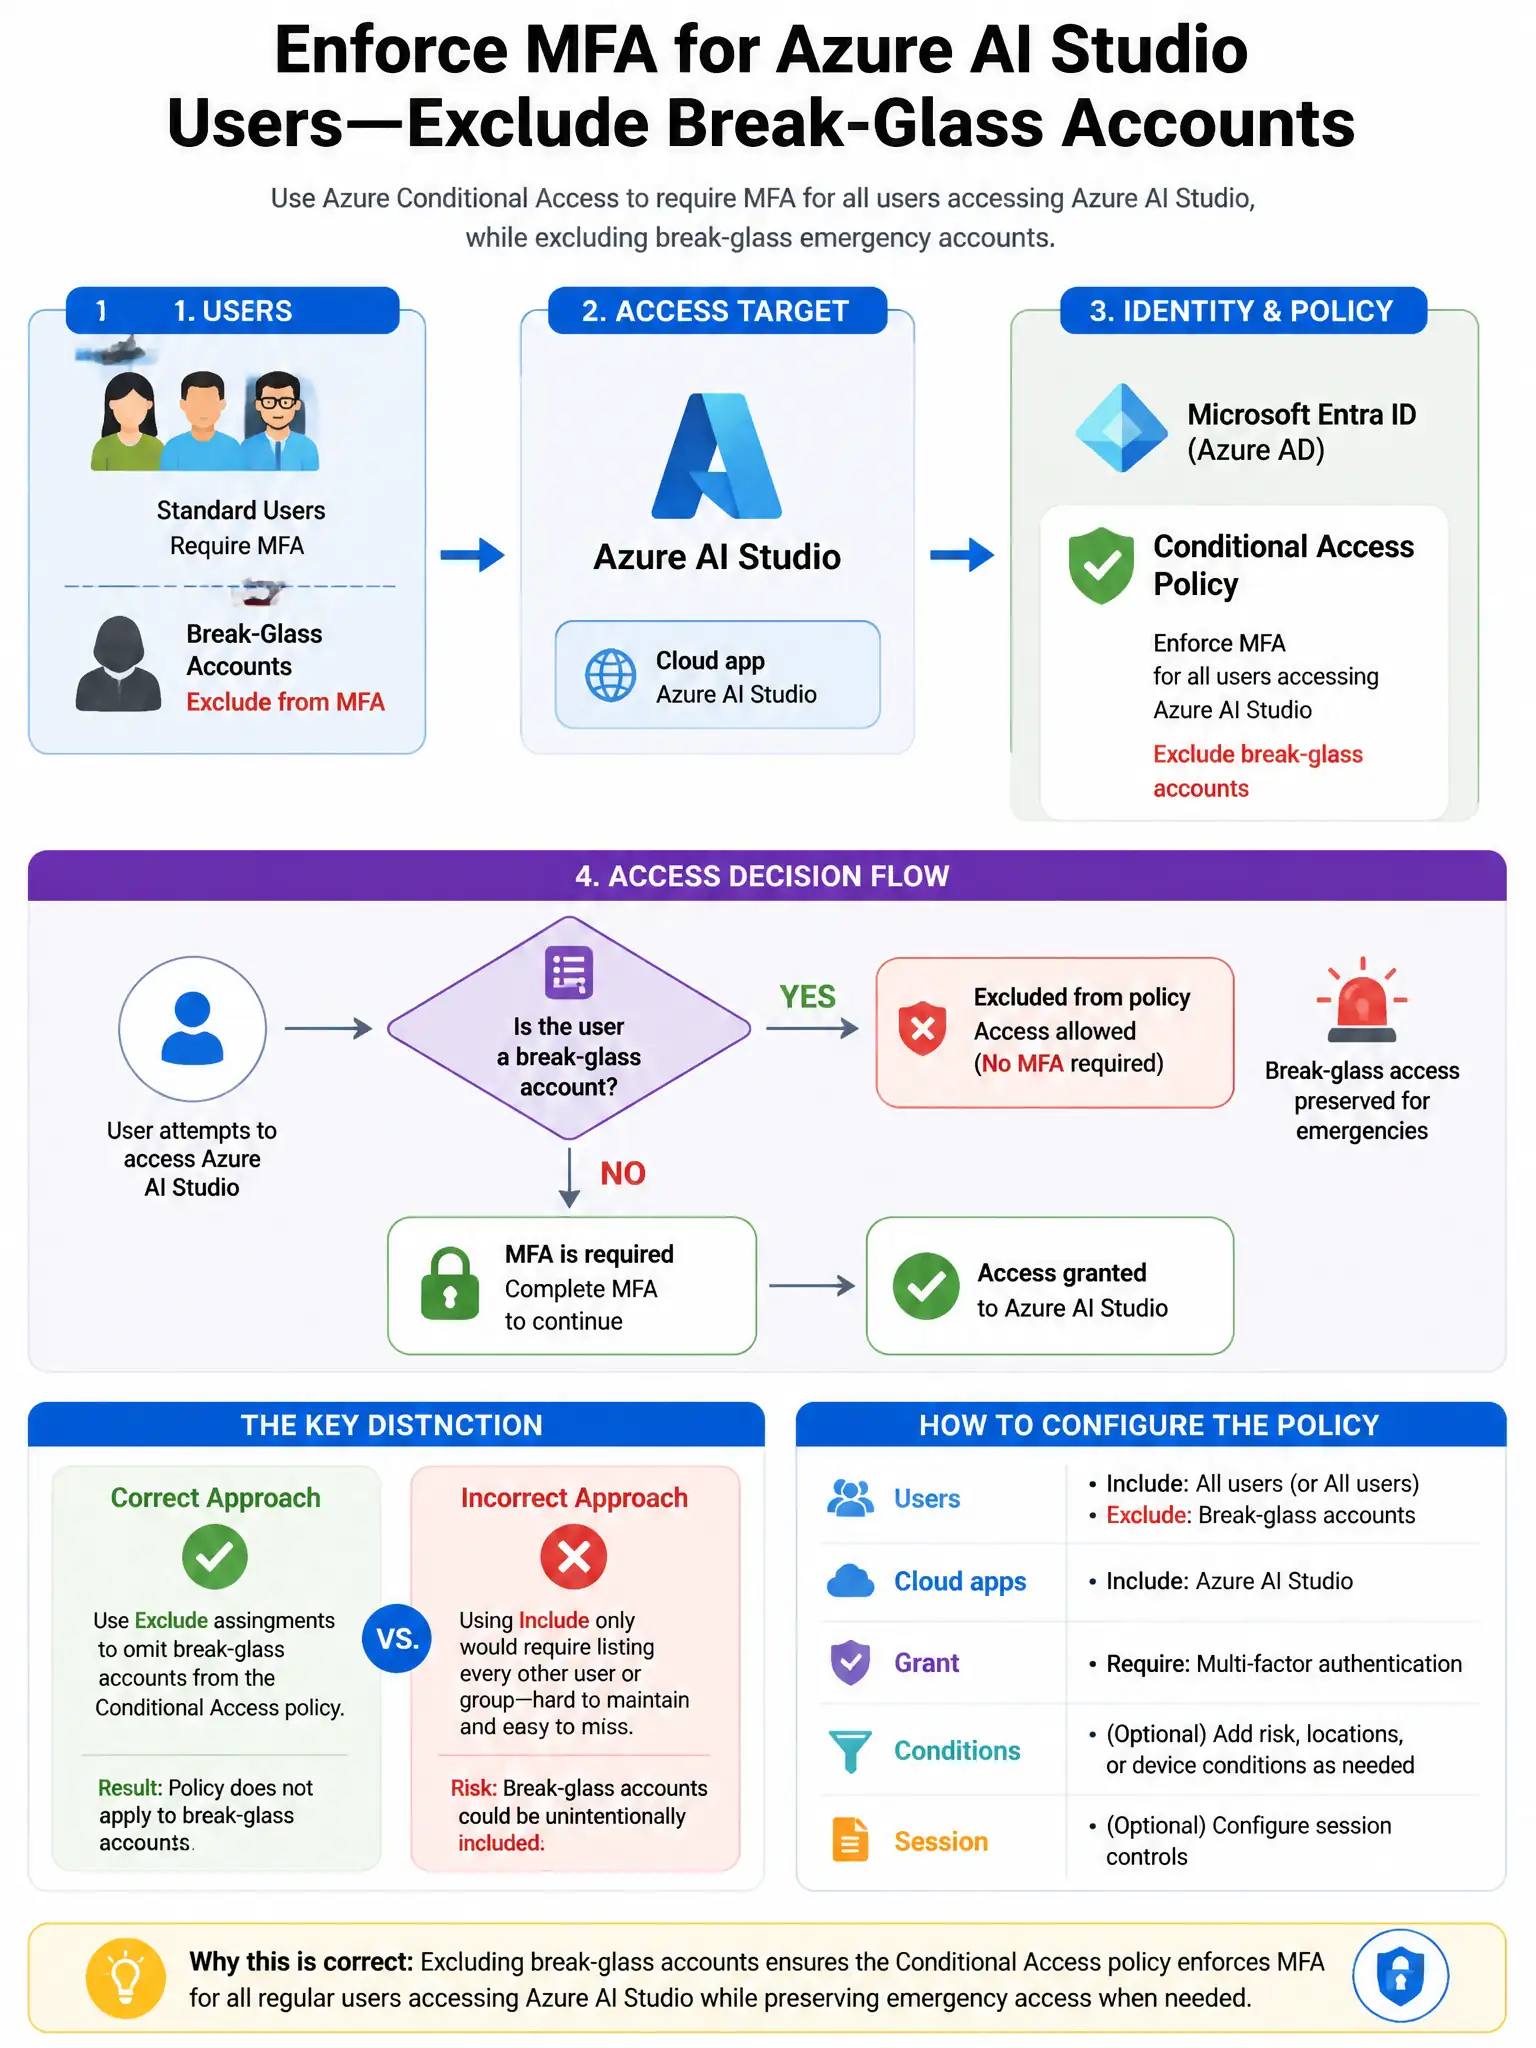
Here's the deal — you need a policy that targets all users, scopes to Azure AI Studio, requires MFA, and excludes break-glass accounts so they stay accessible during lockouts.
Full Explanation
The correct configuration targets all users, includes the Azure AI Studio application, requires MFA as the grant control, and explicitly excludes the break-glass accounts or a dedicated break-glass group so those accounts remain accessible during lockout scenarios. The configuration targeting all users, all cloud apps, requiring MFA, and no exclusions is wrong because targeting all cloud apps is too broad—the question specifically requires scoping to Azure AI Studio. The configuration targeting all users, including Azure AI Studio, requiring a compliant device, and excluding the break-glass group is wrong because requiring a compliant device is a different access control and may not be required; the question asks about MFA enforcement. The configuration targeting only the AI-Users group, including Azure AI Studio, and requiring MFA is wrong because limiting the policy to an AI-Users group means other users without the group assignment could still access Azure AI Studio without MFA.