
A bank's security policy requires that every call to its Foundry project and model endpoints stay entirely on the corporate private network, with no traffic ever traversing the public internet. Which Foundry network configuration satisfies this requirement?
Select an answer to reveal the explanation.
Short Explanation
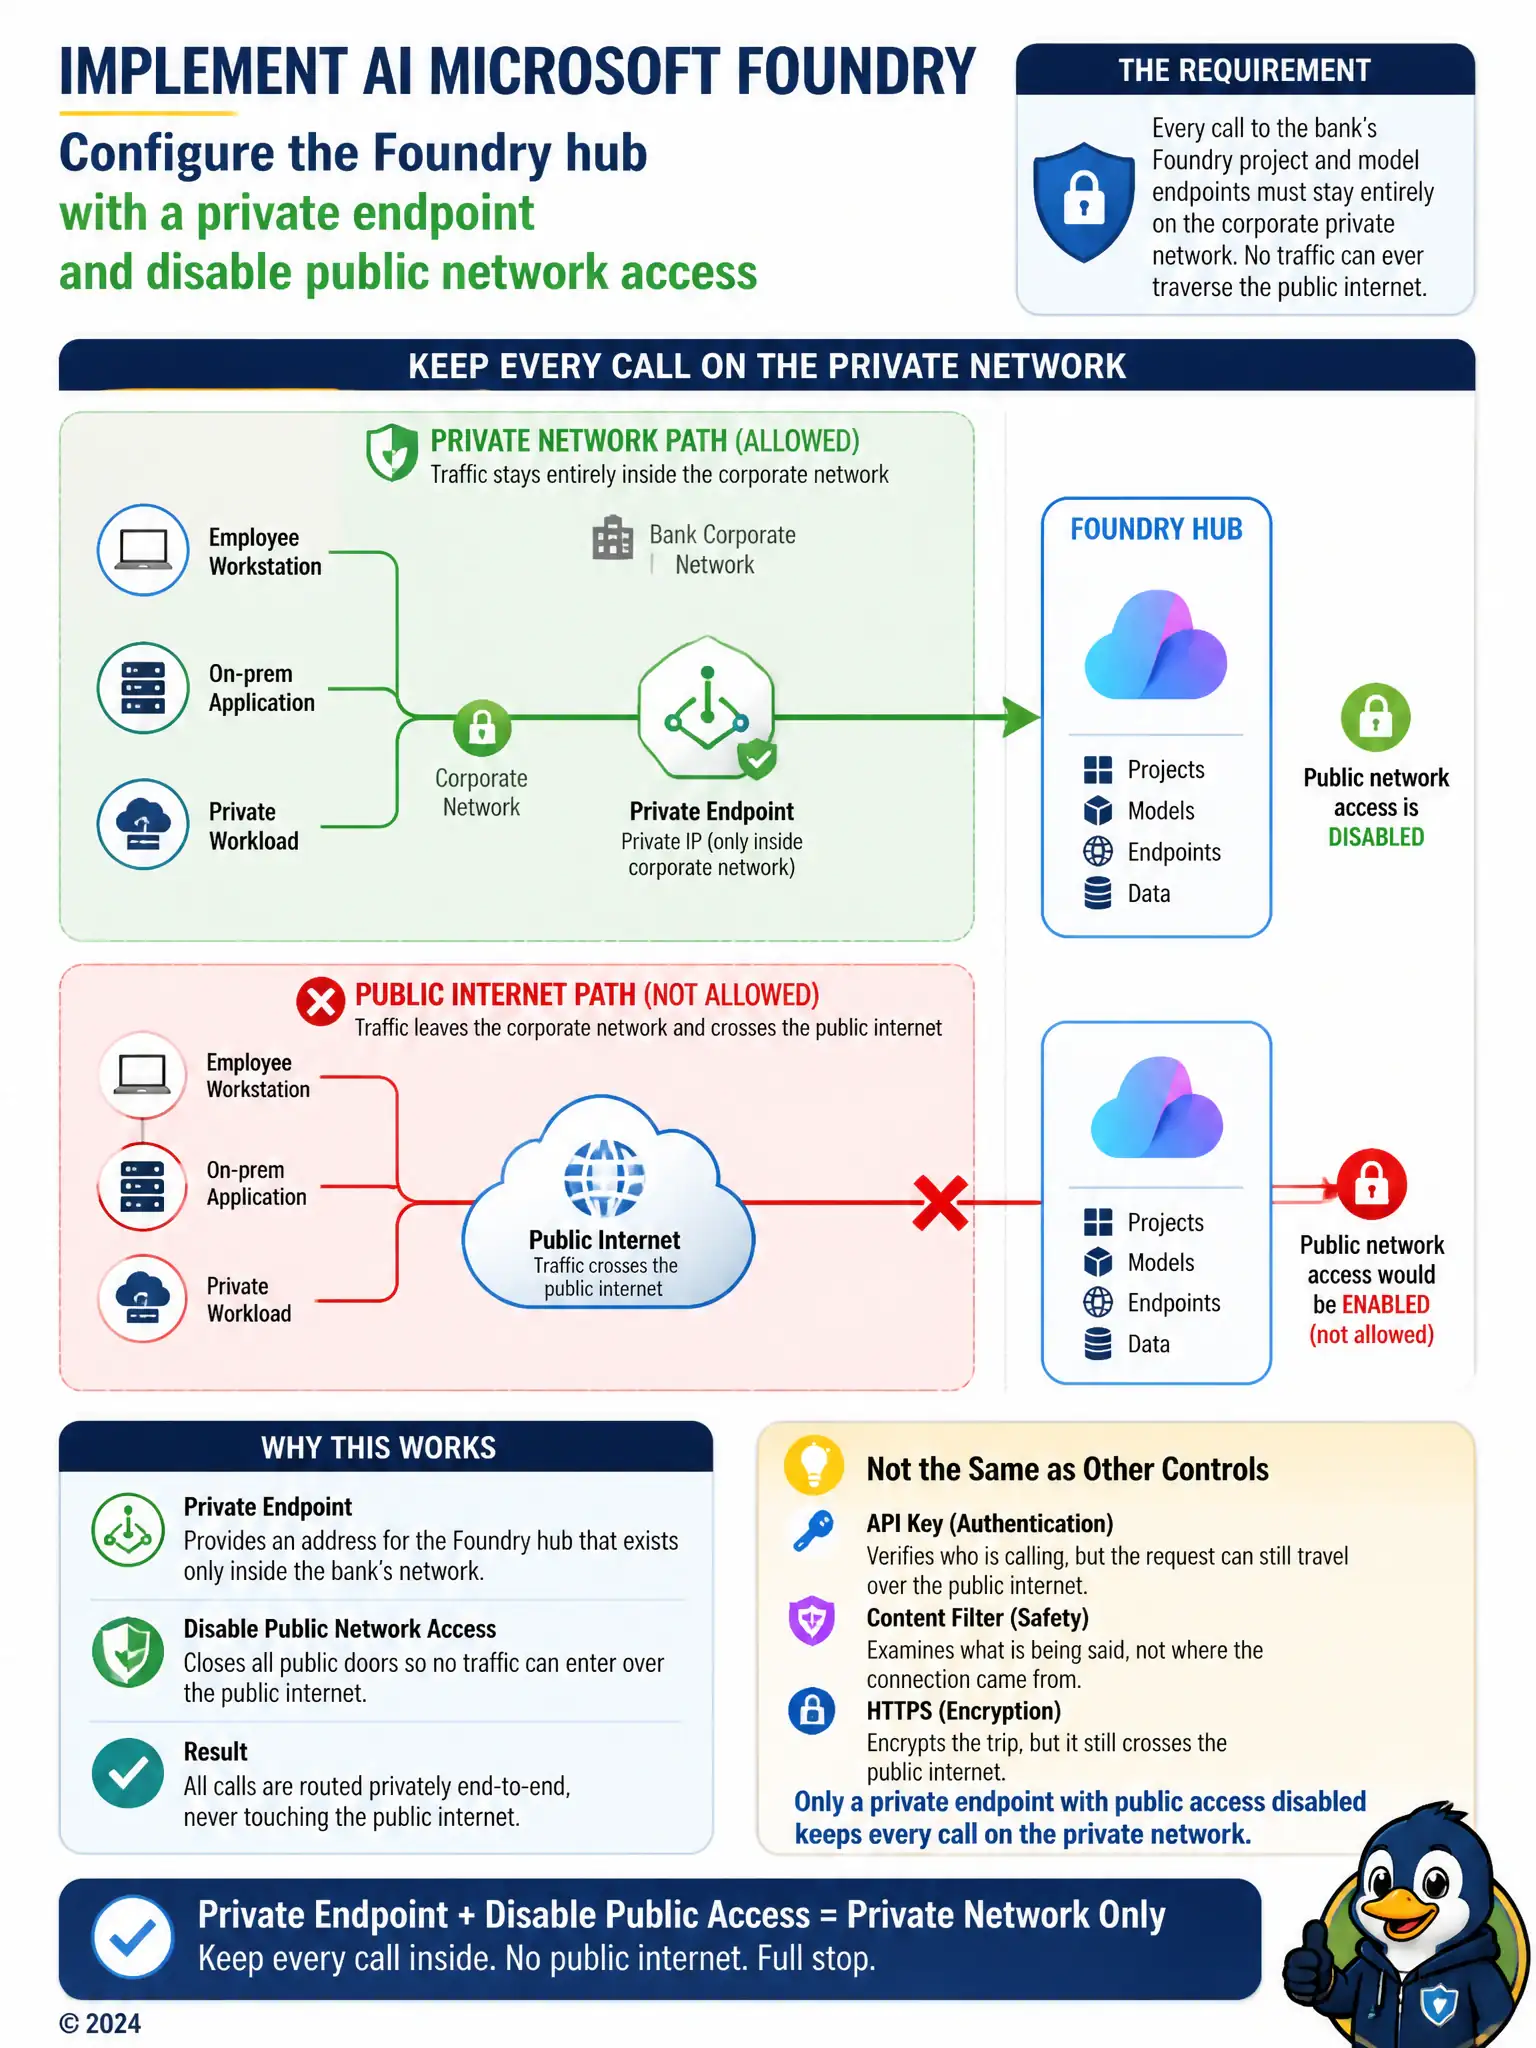
The bank needs traffic that never touches the public internet, so you need a private endpoint for the Foundry hub and you need public network access turned off. An API key, content filter, or HTTPS can protect or inspect a call, but they don't change the wires it travels over.
Full Explanation
The correct configuration is to configure the Foundry hub with a private endpoint and disable public network access. A private endpoint gives the Foundry hub a private IP address inside the bank's virtual network, and disabling public network access ensures that the only path to the hub and its model endpoints is through that private connection, which is the configuration that actually keeps traffic off the public internet as the policy requires. The configuration that keeps public network access enabled but requires an API key on every request is incorrect because an API key controls authentication and authorization for a request, not the network path that request travels; a correctly authenticated call can still cross the public internet before it ever reaches the endpoint. The configuration that relies on the content safety filter to reject requests from unrecognized callers is incorrect because content safety filtering screens the content of a request or response for policy violations, it does not control or restrict which network a connection is routed over, so it does nothing to keep traffic private. The configuration that enables public network access but requires all traffic to use HTTPS is incorrect because HTTPS encrypts traffic in transit but does not change its path; an encrypted request over the public internet is still public internet traffic, which does not meet a requirement that traffic never traverse it at all. Only a private endpoint paired with disabling public access actually removes the public internet from the path between callers and the Foundry project.