
A financial services firm is deploying a Foundry-hosted model for an internal analyst tool. Compliance requires that inference traffic never traverse the public internet and that data at rest in the deployment be encrypted using keys the firm controls rather than Microsoft-managed keys. (Select TWO.) Which two configurations satisfy these requirements?
Select all correct answers, then click Submit.
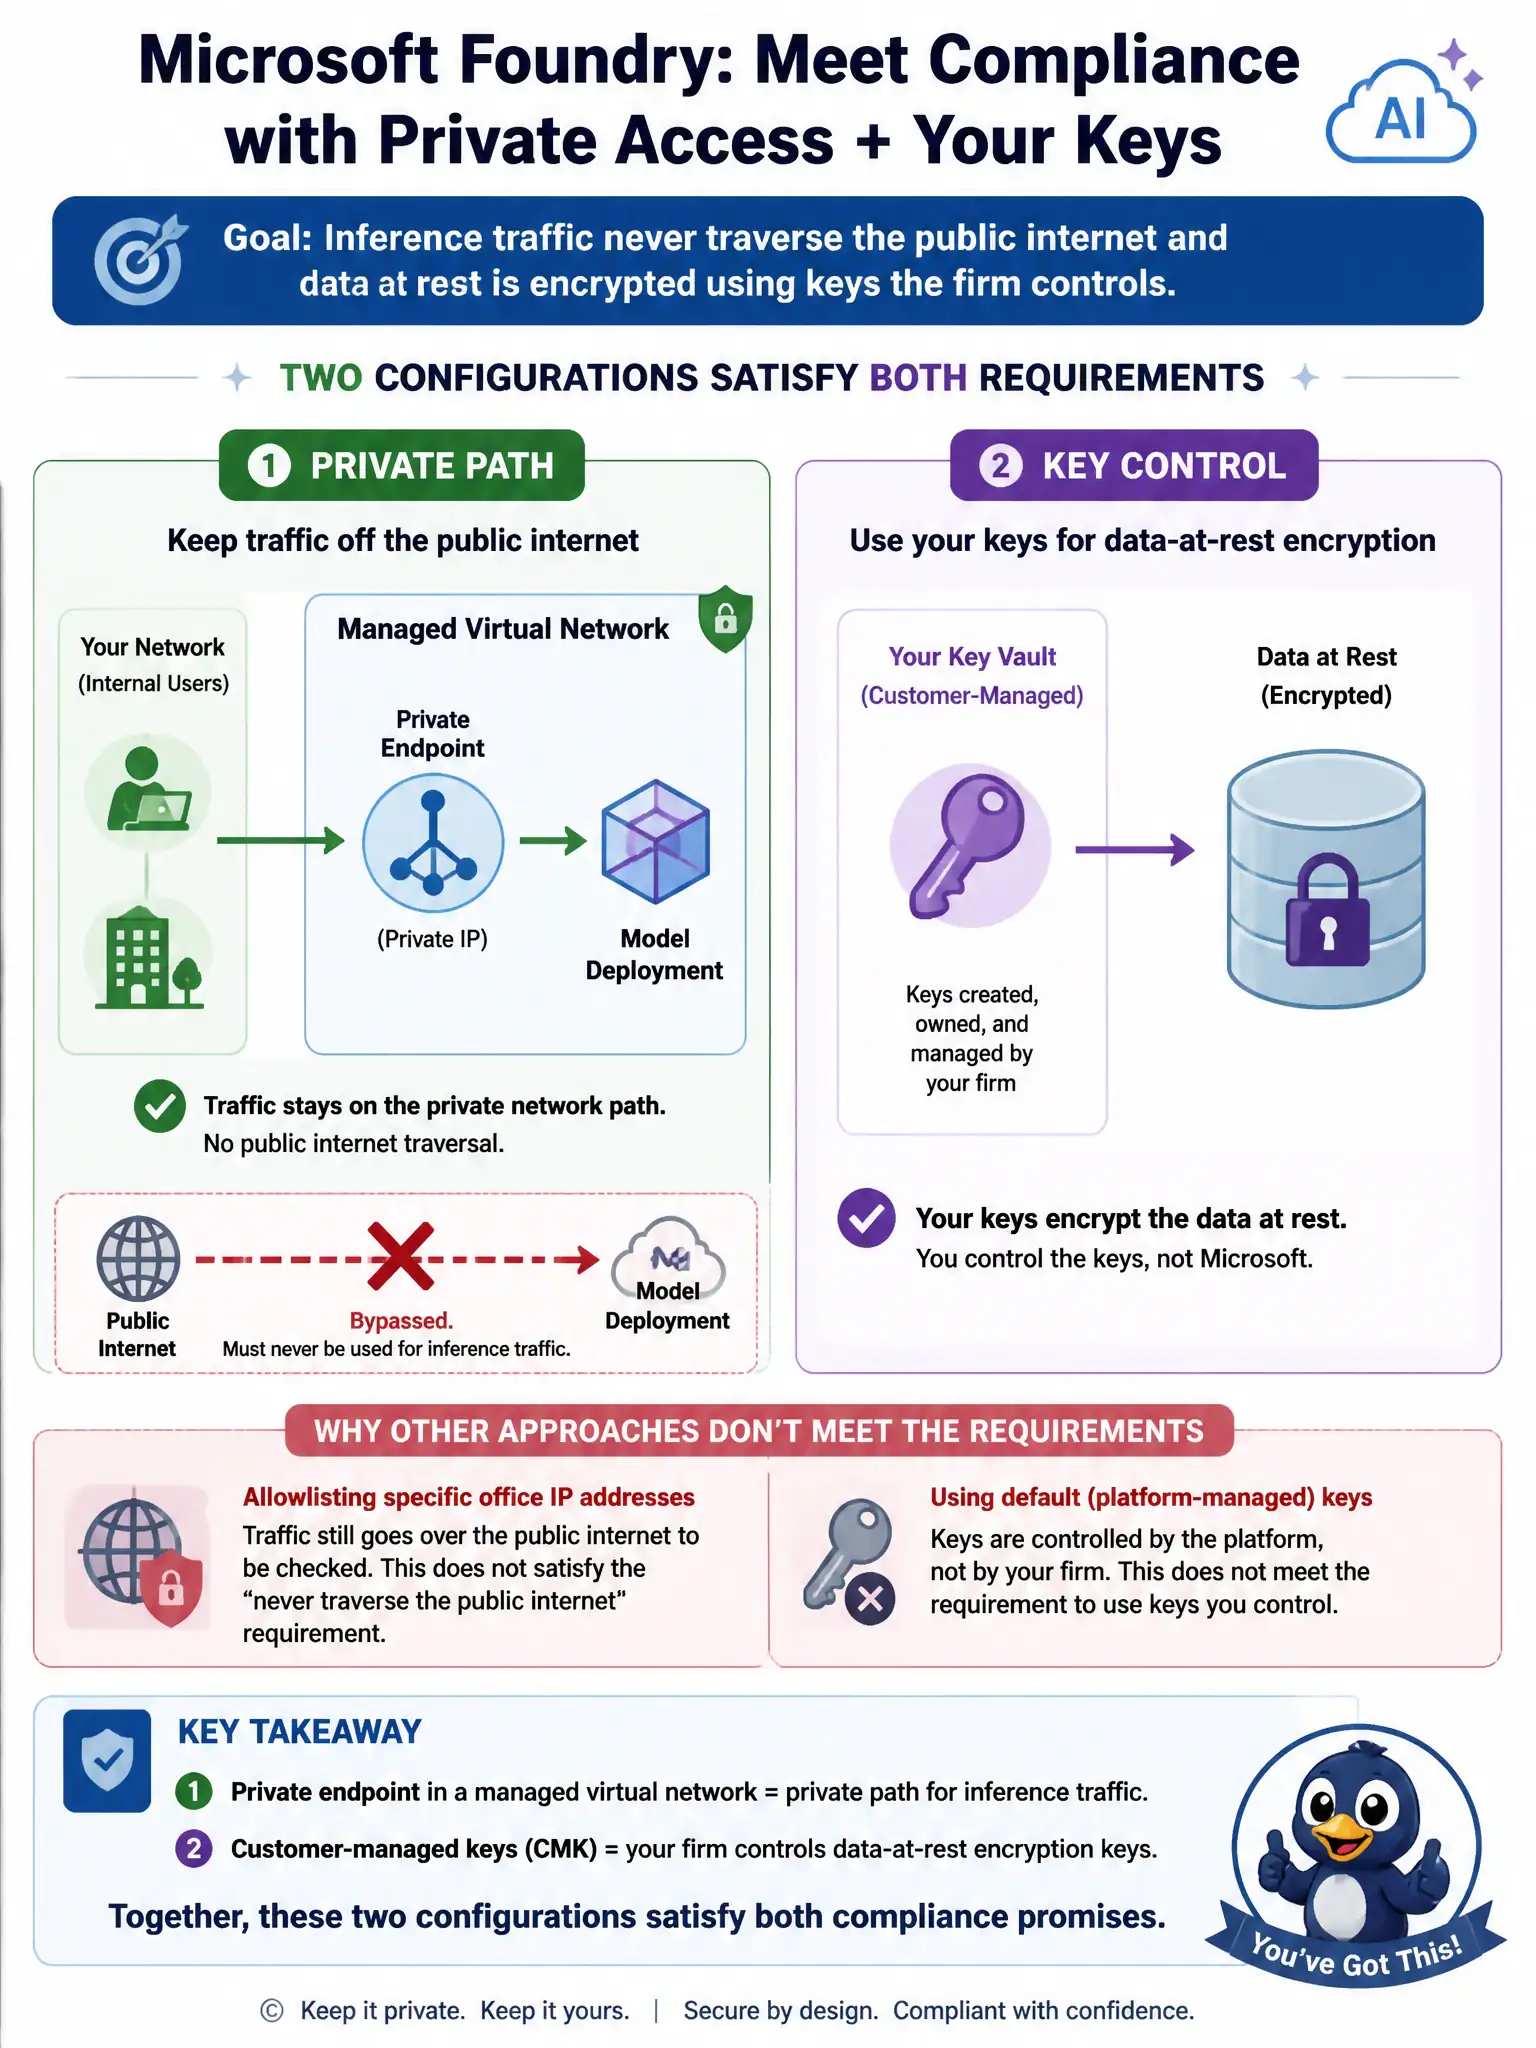
Short Explanation
You need two fixes: put the deployment behind a private endpoint in a managed virtual network so inference traffic stays on the private path, and enable customer-managed keys so the firm controls data-at-rest encryption. IP allowlisting still uses the public internet, and default Microsoft-managed keys don't give the firm key control.
Full Explanation
The correct configurations are the private endpoint deployment and customer-managed keys. A private endpoint inside a managed virtual network keeps inference traffic on a private network path rather than the public internet, satisfying the network isolation requirement. Customer-managed keys let the firm hold and rotate the encryption keys used to protect data at rest, satisfying the key-ownership requirement. Together, these two configurations directly address both stated compliance conditions. The public network access with IP allowlisting restricted to the office's outbound IP range is incorrect because enabling public network access, even with allowlisting, still means traffic traverses the public internet before reaching the allowlist check; it narrows who can connect but does not keep traffic off the public path, which the requirement explicitly rules out. Relying on default Microsoft-managed encryption keys is incorrect because Microsoft-managed keys mean Microsoft controls the encryption keys, not the firm, which directly contradicts the requirement that the firm control its own keys, regardless of which compliance frameworks those managed keys satisfy in general. Meeting both stated constraints requires combining private network access with customer-controlled encryption, which is exactly what the private endpoint and customer-managed key configurations provide, while the public access with allowlisting and default managed keys each fail one of the two requirements.