
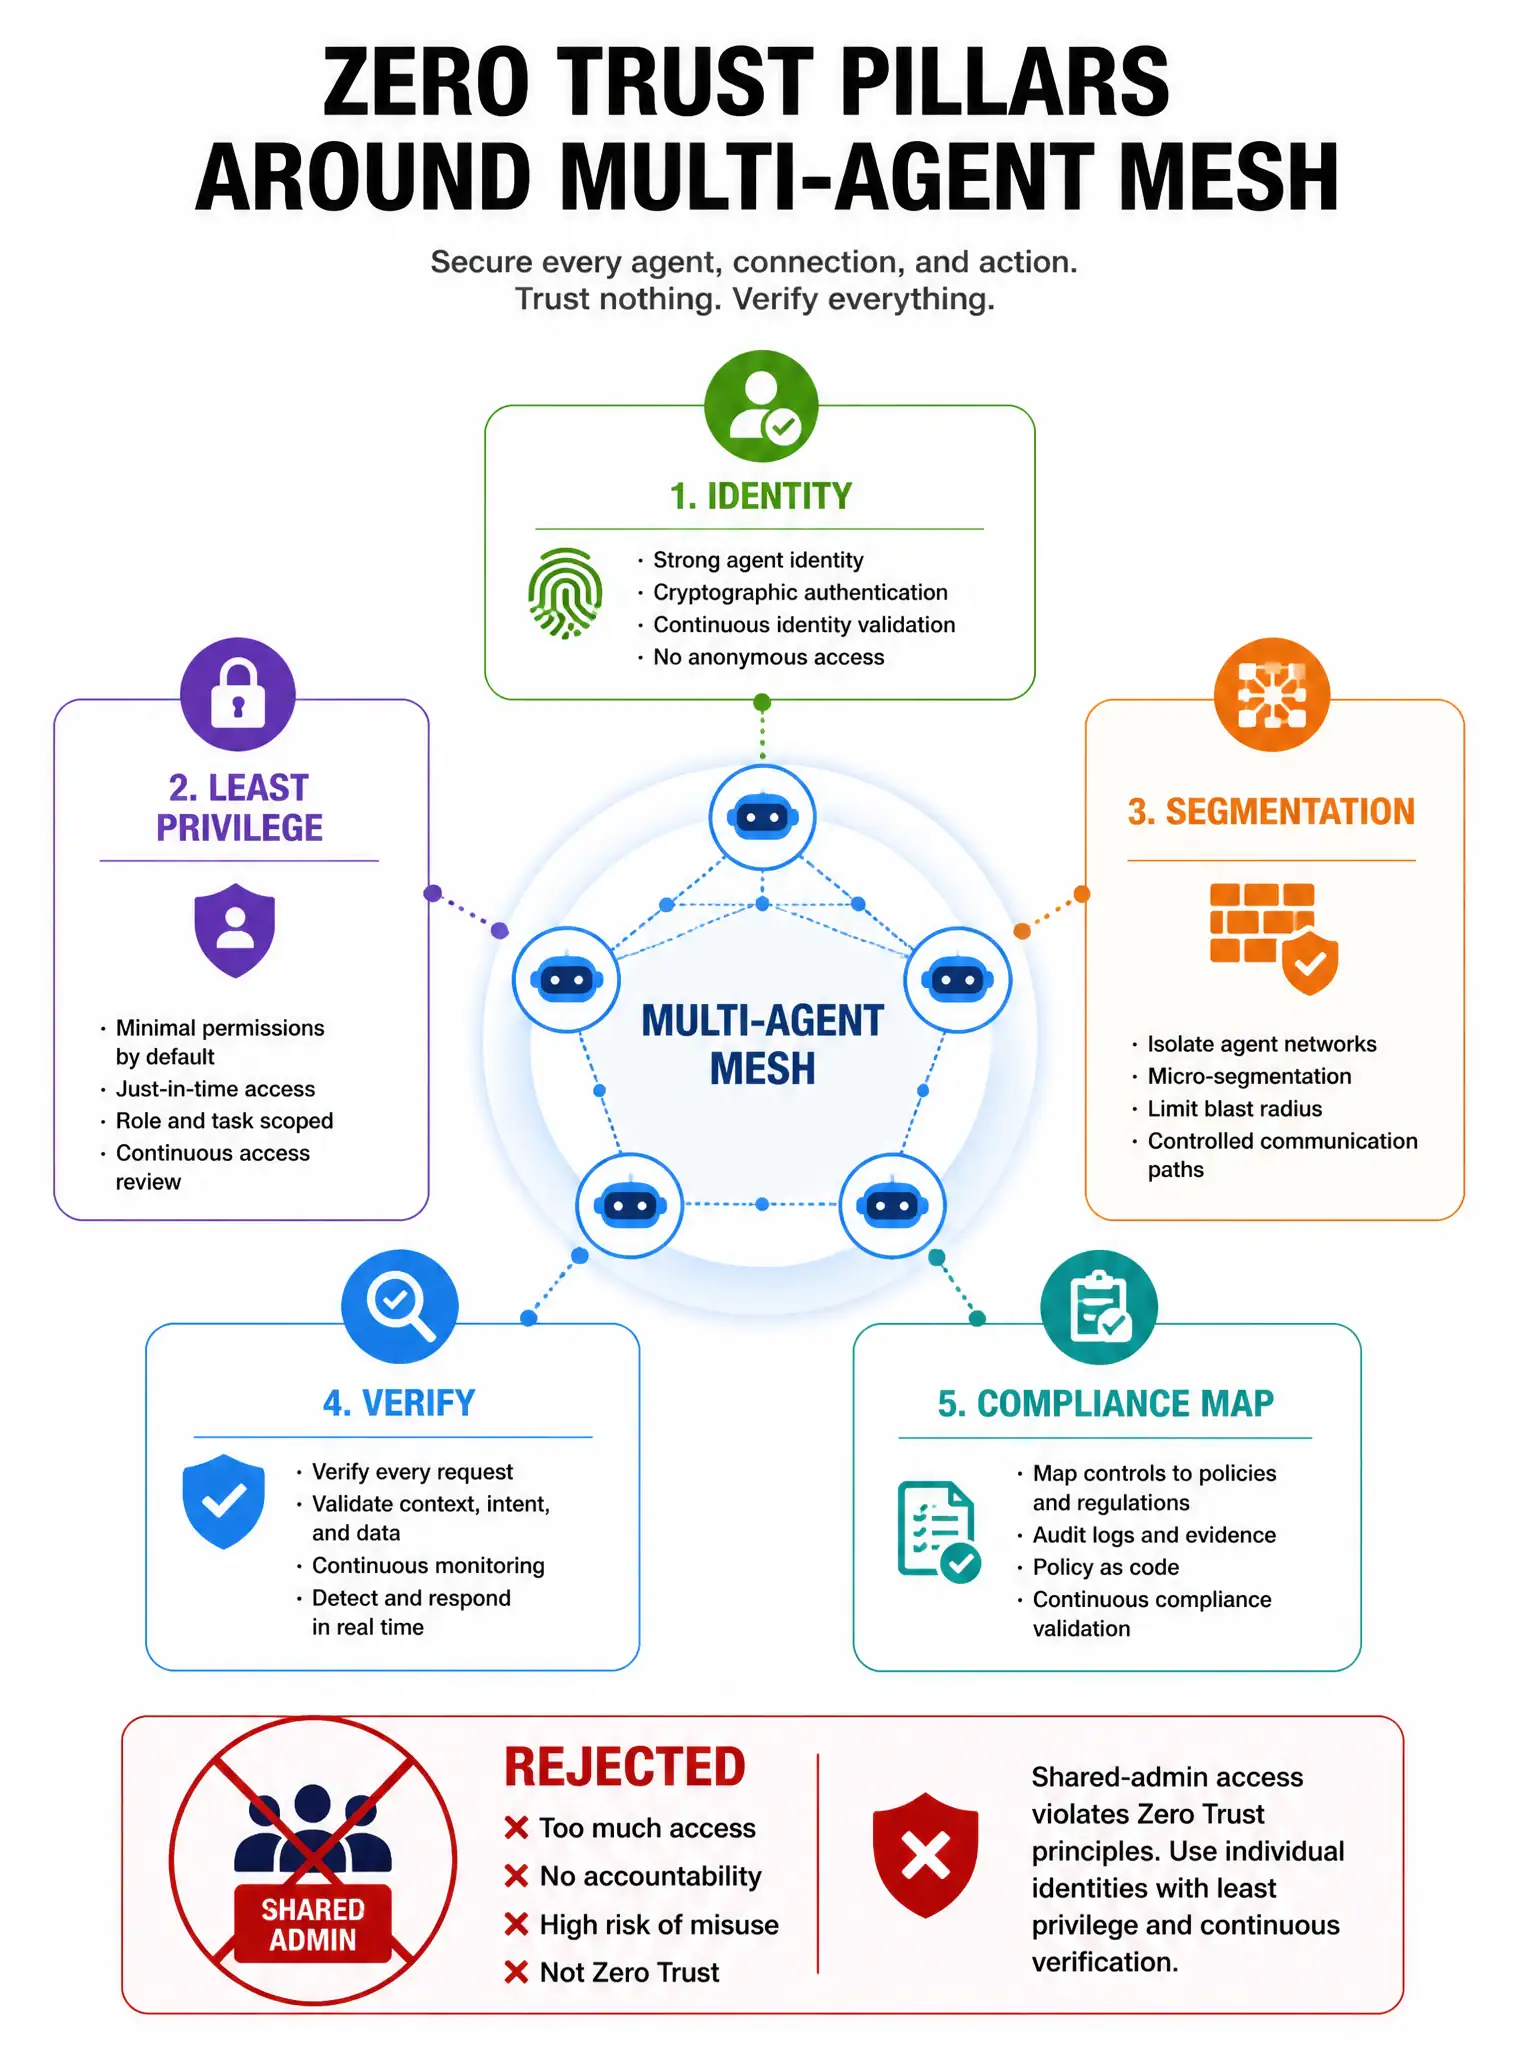
A regulated multi-agent architecture review asks which components must be specified to prevent lateral movement and map controls to compliance frameworks. Which answer is most complete?
Select an answer to reveal the explanation.
Short Explanation
You need per-agent identity scoping, least-privilege tool and data access, network segmentation, continuous verification, and explicit compliance control mapping. That stops lateral movement and gives auditors control mapping. Shared admin identities, public anonymous endpoints, and whiteboard-only compliance won't pass review.
Full Explanation
The correct answer specifies per-agent identity scoping, least-privilege tool and data access, network segmentation, continuous verification, and explicit compliance control mapping. Those Zero Trust elements prevent lateral movement and map controls for regulated deployments. Shared admin identities and public anonymous endpoints maximize lateral movement and exposure; whiteboard-only compliance lacks enforcement. Produce an architecture decision record linking each regulatory control to concrete Azure and application mechanisms, and test them in red-team exercises.