
A bank is preparing to launch a multi-agent customer assistant. Security wants shift-left adversarial testing of prompt injection, tool abuse, and jailbreak attempts before production. Which Foundry-aligned practice should they adopt?
Select an answer to reveal the explanation.
Short Explanation
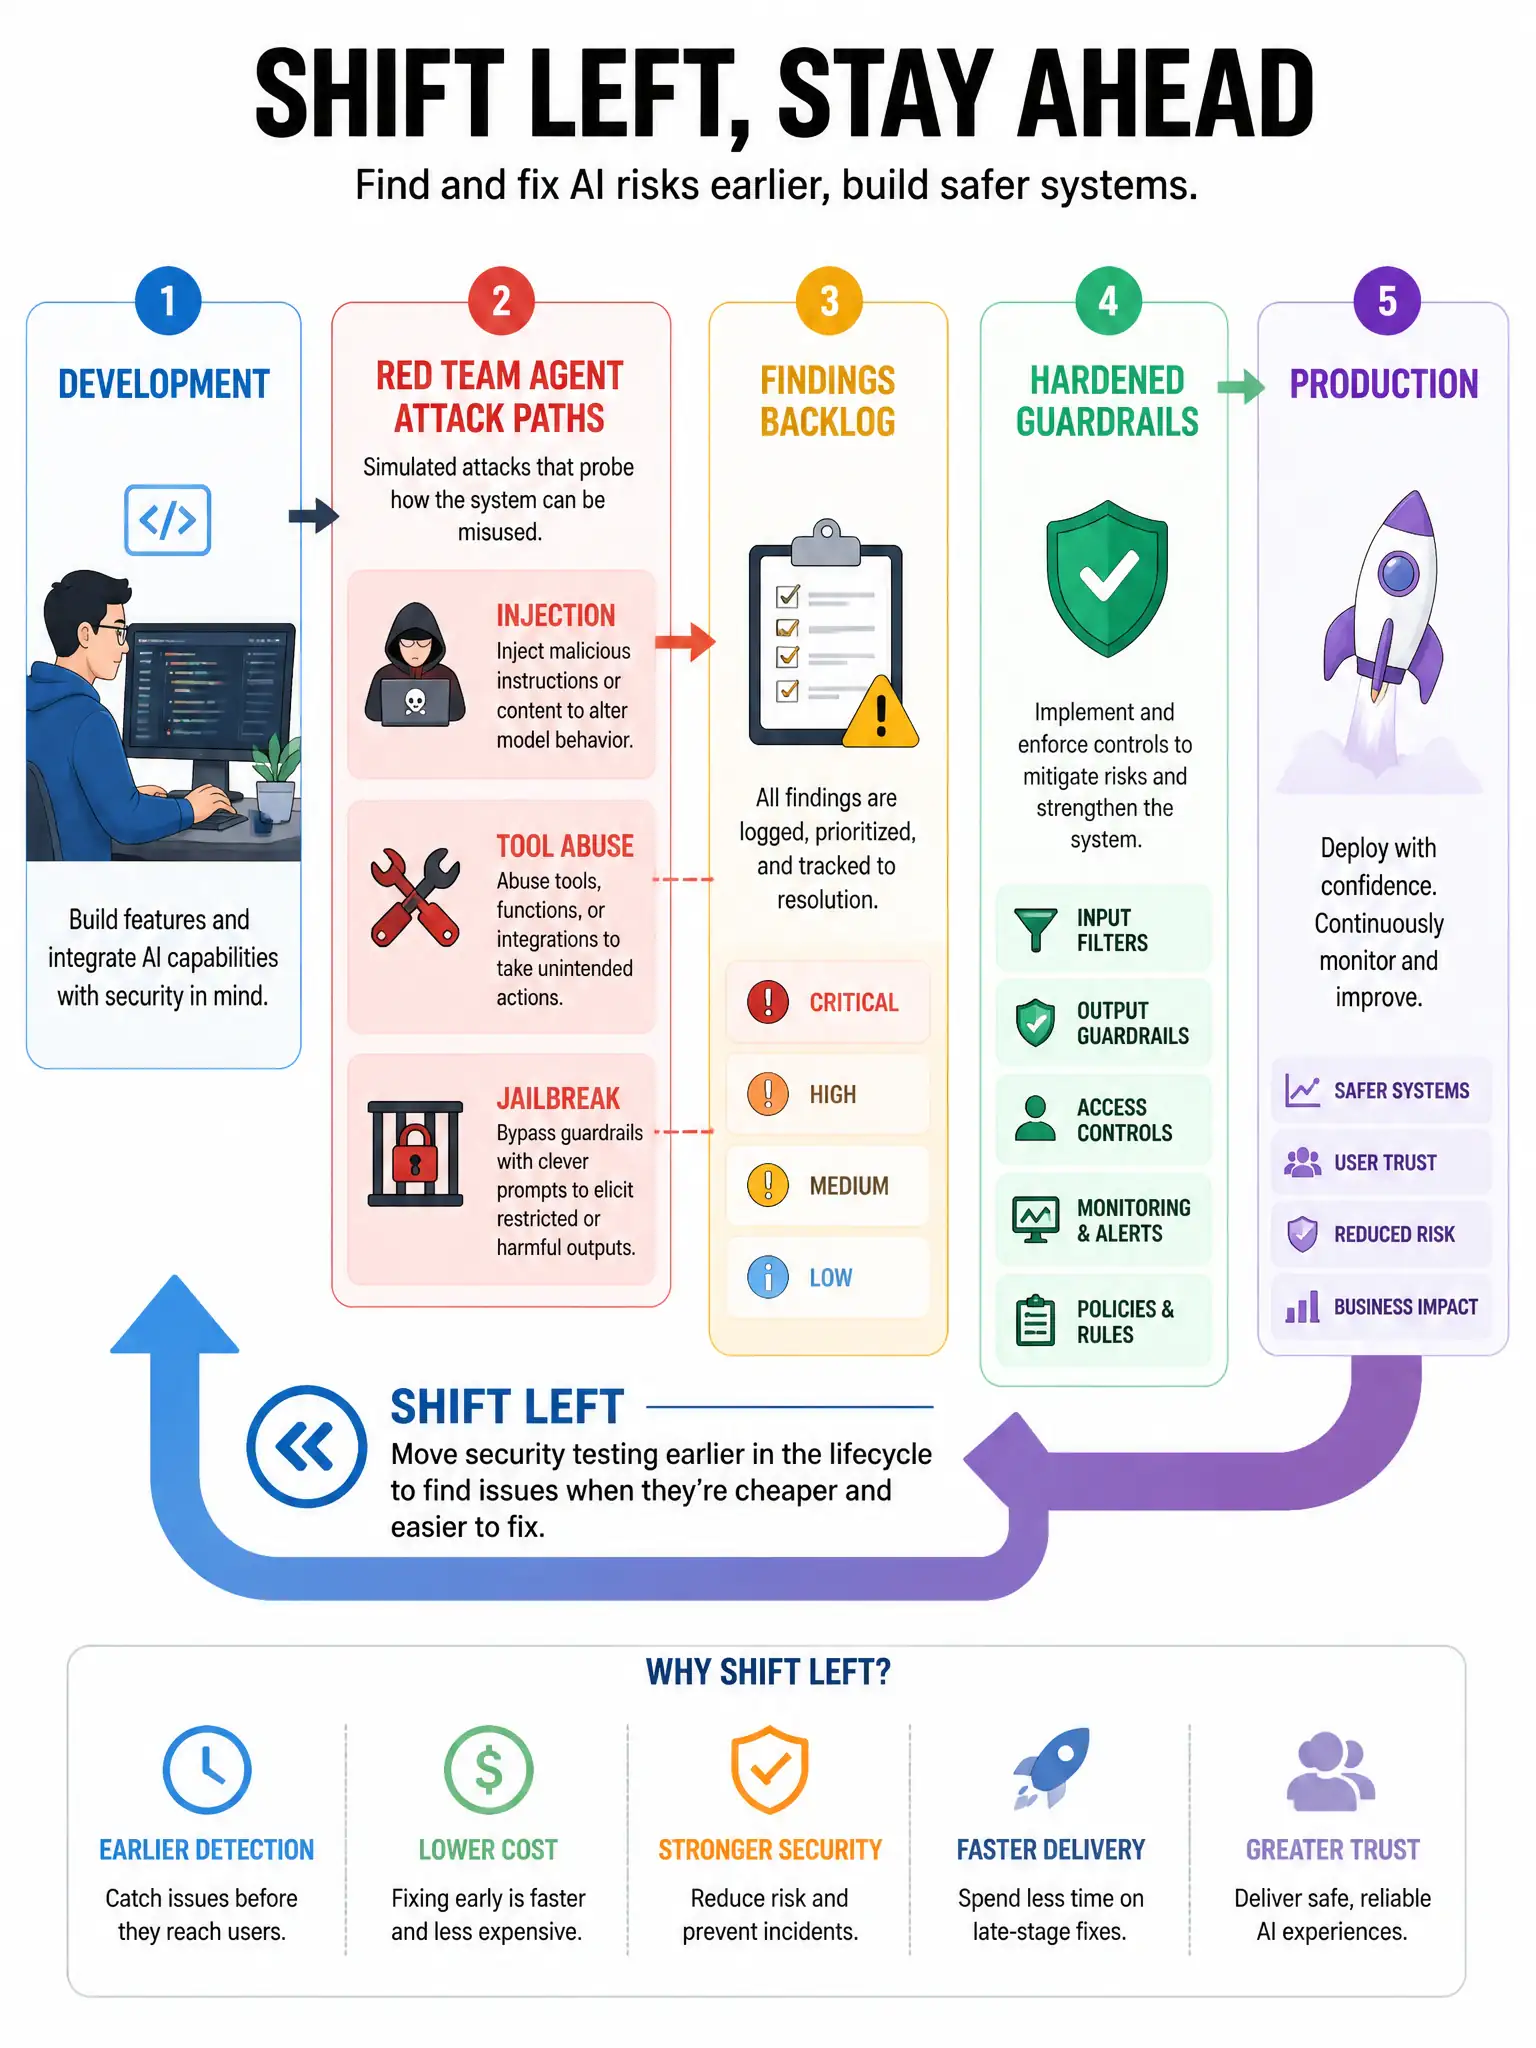
Shift-left security means you test for prompt injection, tool abuse, and jailbreaks before go-live. Use the AI Red Teaming Agent in Foundry and related adversarial evaluations during development and pre-production, then fix what you find before release.
Full Explanation
Shift-left security, including the AI Red Teaming Agent in Foundry, is a stated skill for securing multi-agent solutions. The correct practice places adversarial testing in development and pre-production, then remediates findings before release. Postponing testing until public launch delays discovery until customer impact. Port scans of AKS nodes cover only traditional infrastructure attack surface. Disabling content safety filters weakens controls. Integrate red-team scenarios into CI, track residual risk, and re-run after major prompt or tool changes.