
Multiple agents need database credentials and third-party API secrets. Developers currently paste secrets into agent environment variables in plain text and rarely rotate them. Which approach meets security requirements for multi-agent solutions on Azure?
Select an answer to reveal the explanation.
Short Explanation
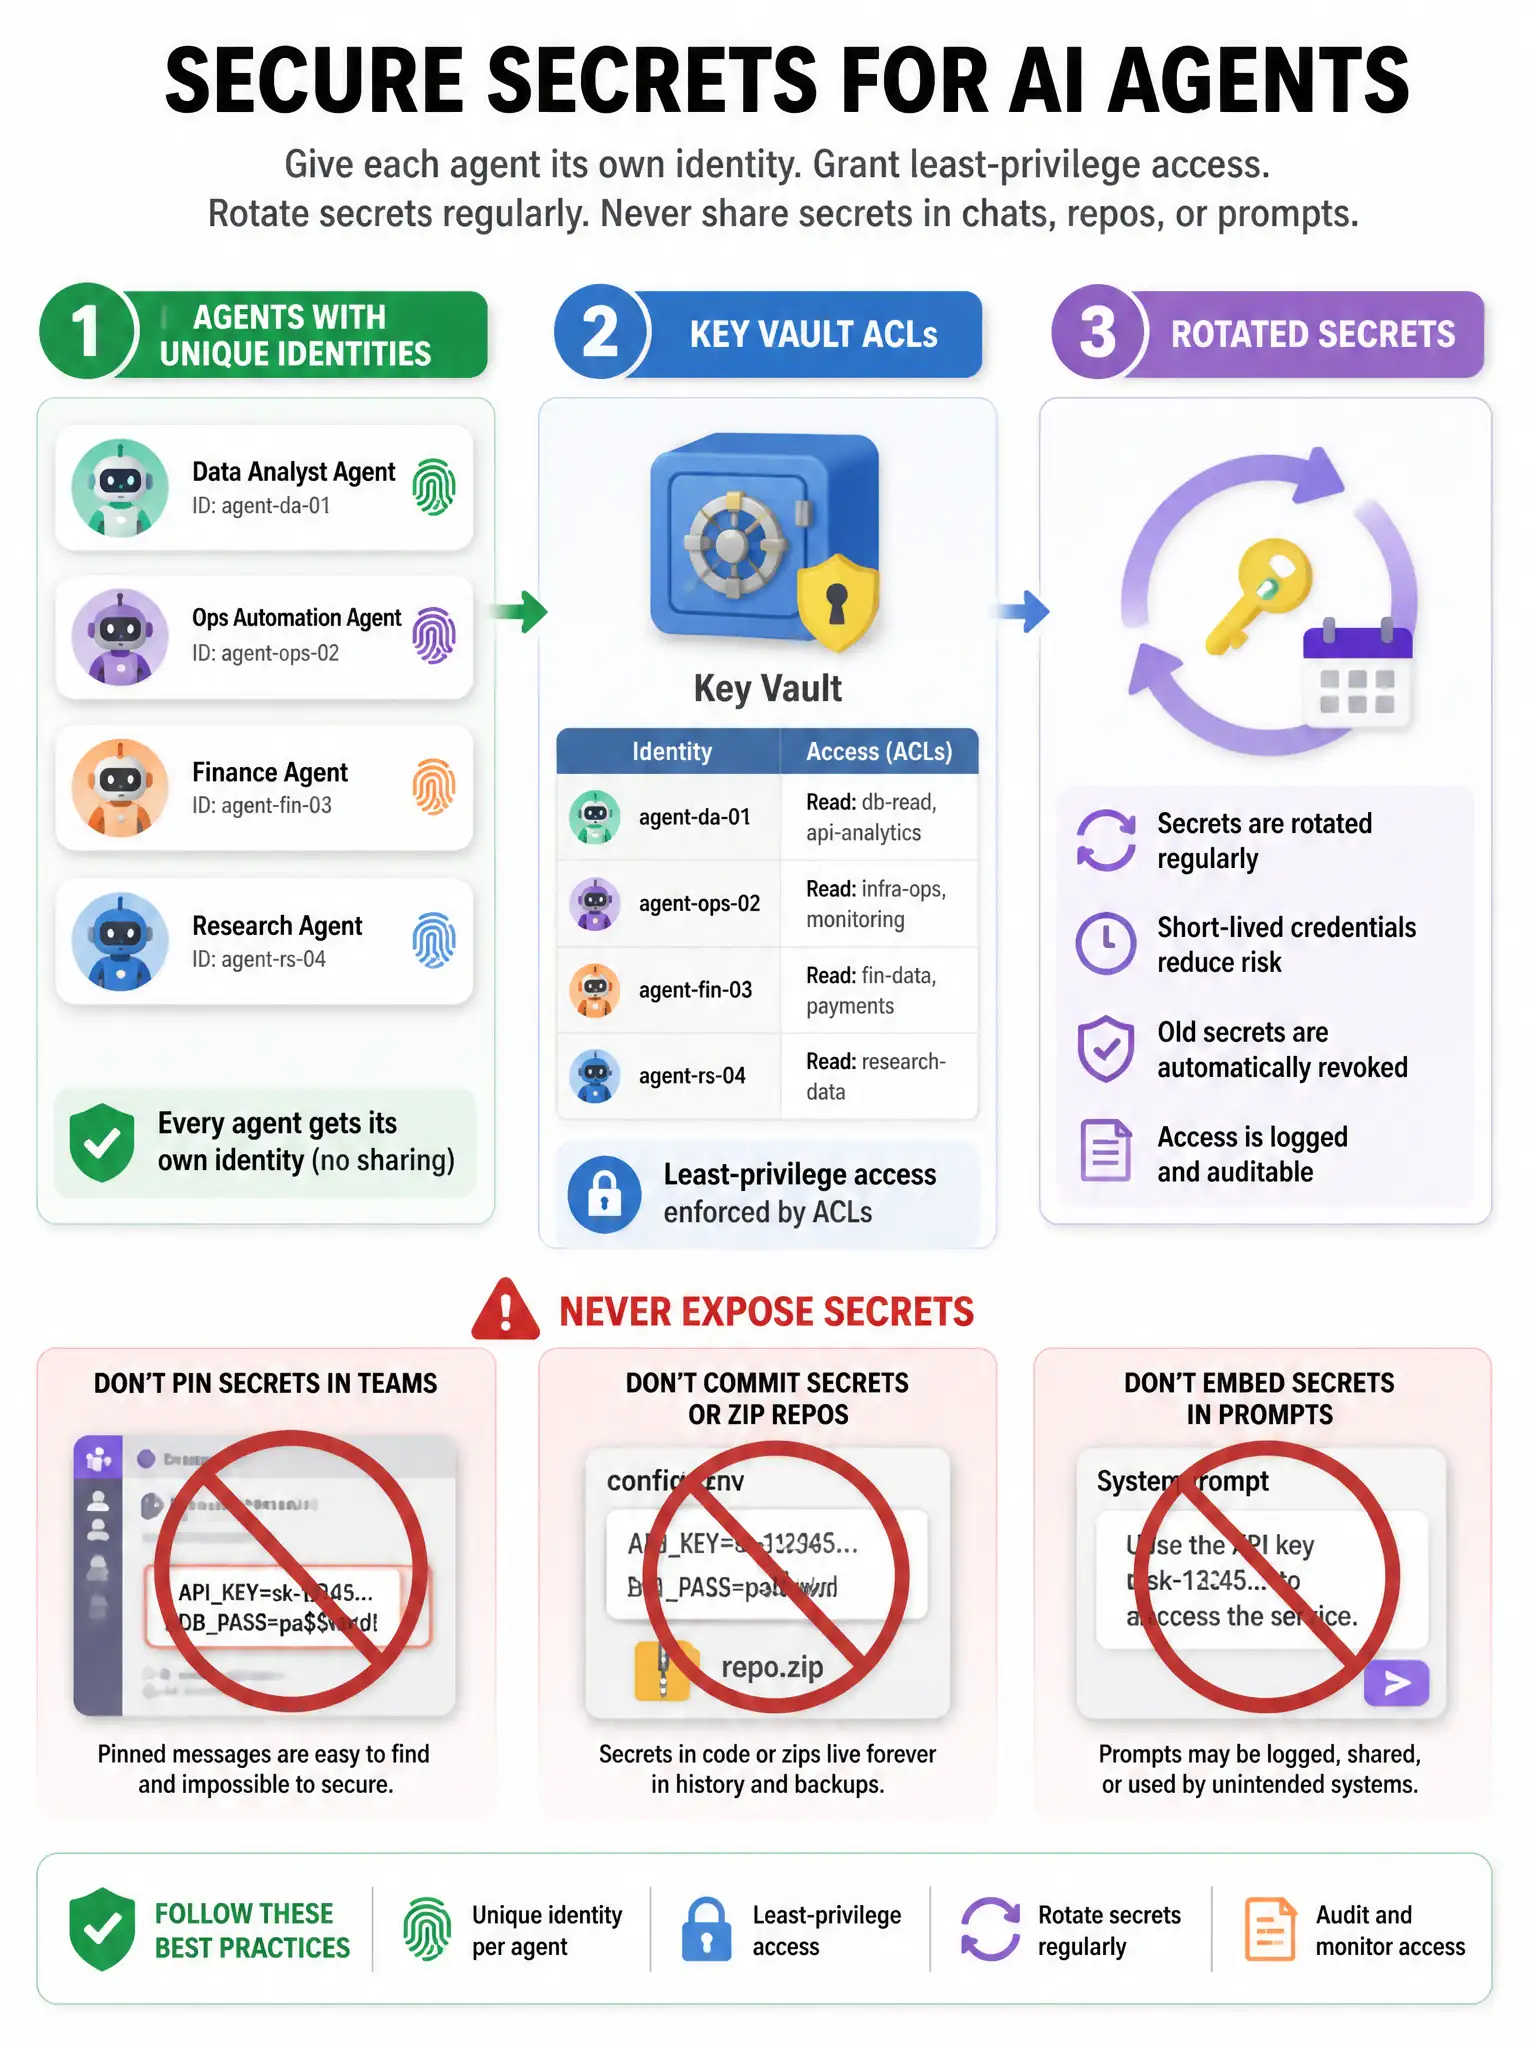
You need secrets in Azure Key Vault, not in plain text. Give each agent least-privilege access to only what it needs, rotate secrets, and fetch them at runtime. That keeps credentials out of prompts, configs, and casual sharing.
Full Explanation
Secrets management for multi-agent solutions on Azure centers on Key Vault: secrets/certificates, rotation, RBAC to secrets, encryption, and runtime retrieval. The Key Vault approach with per-agent identity, least privilege, rotation, and runtime retrieval matches that pattern and prevents prompt or config leakage. An encrypted zip in public docs, a pinned Teams message, and secrets in the orchestrator system prompt distribute secrets through insecure channels or model context, creating exfiltration and audit failures. Combine Key Vault with managed identities per agent, deny broad secret-list permissions, and monitor access. Rotate on schedule and after suspected exposure.