
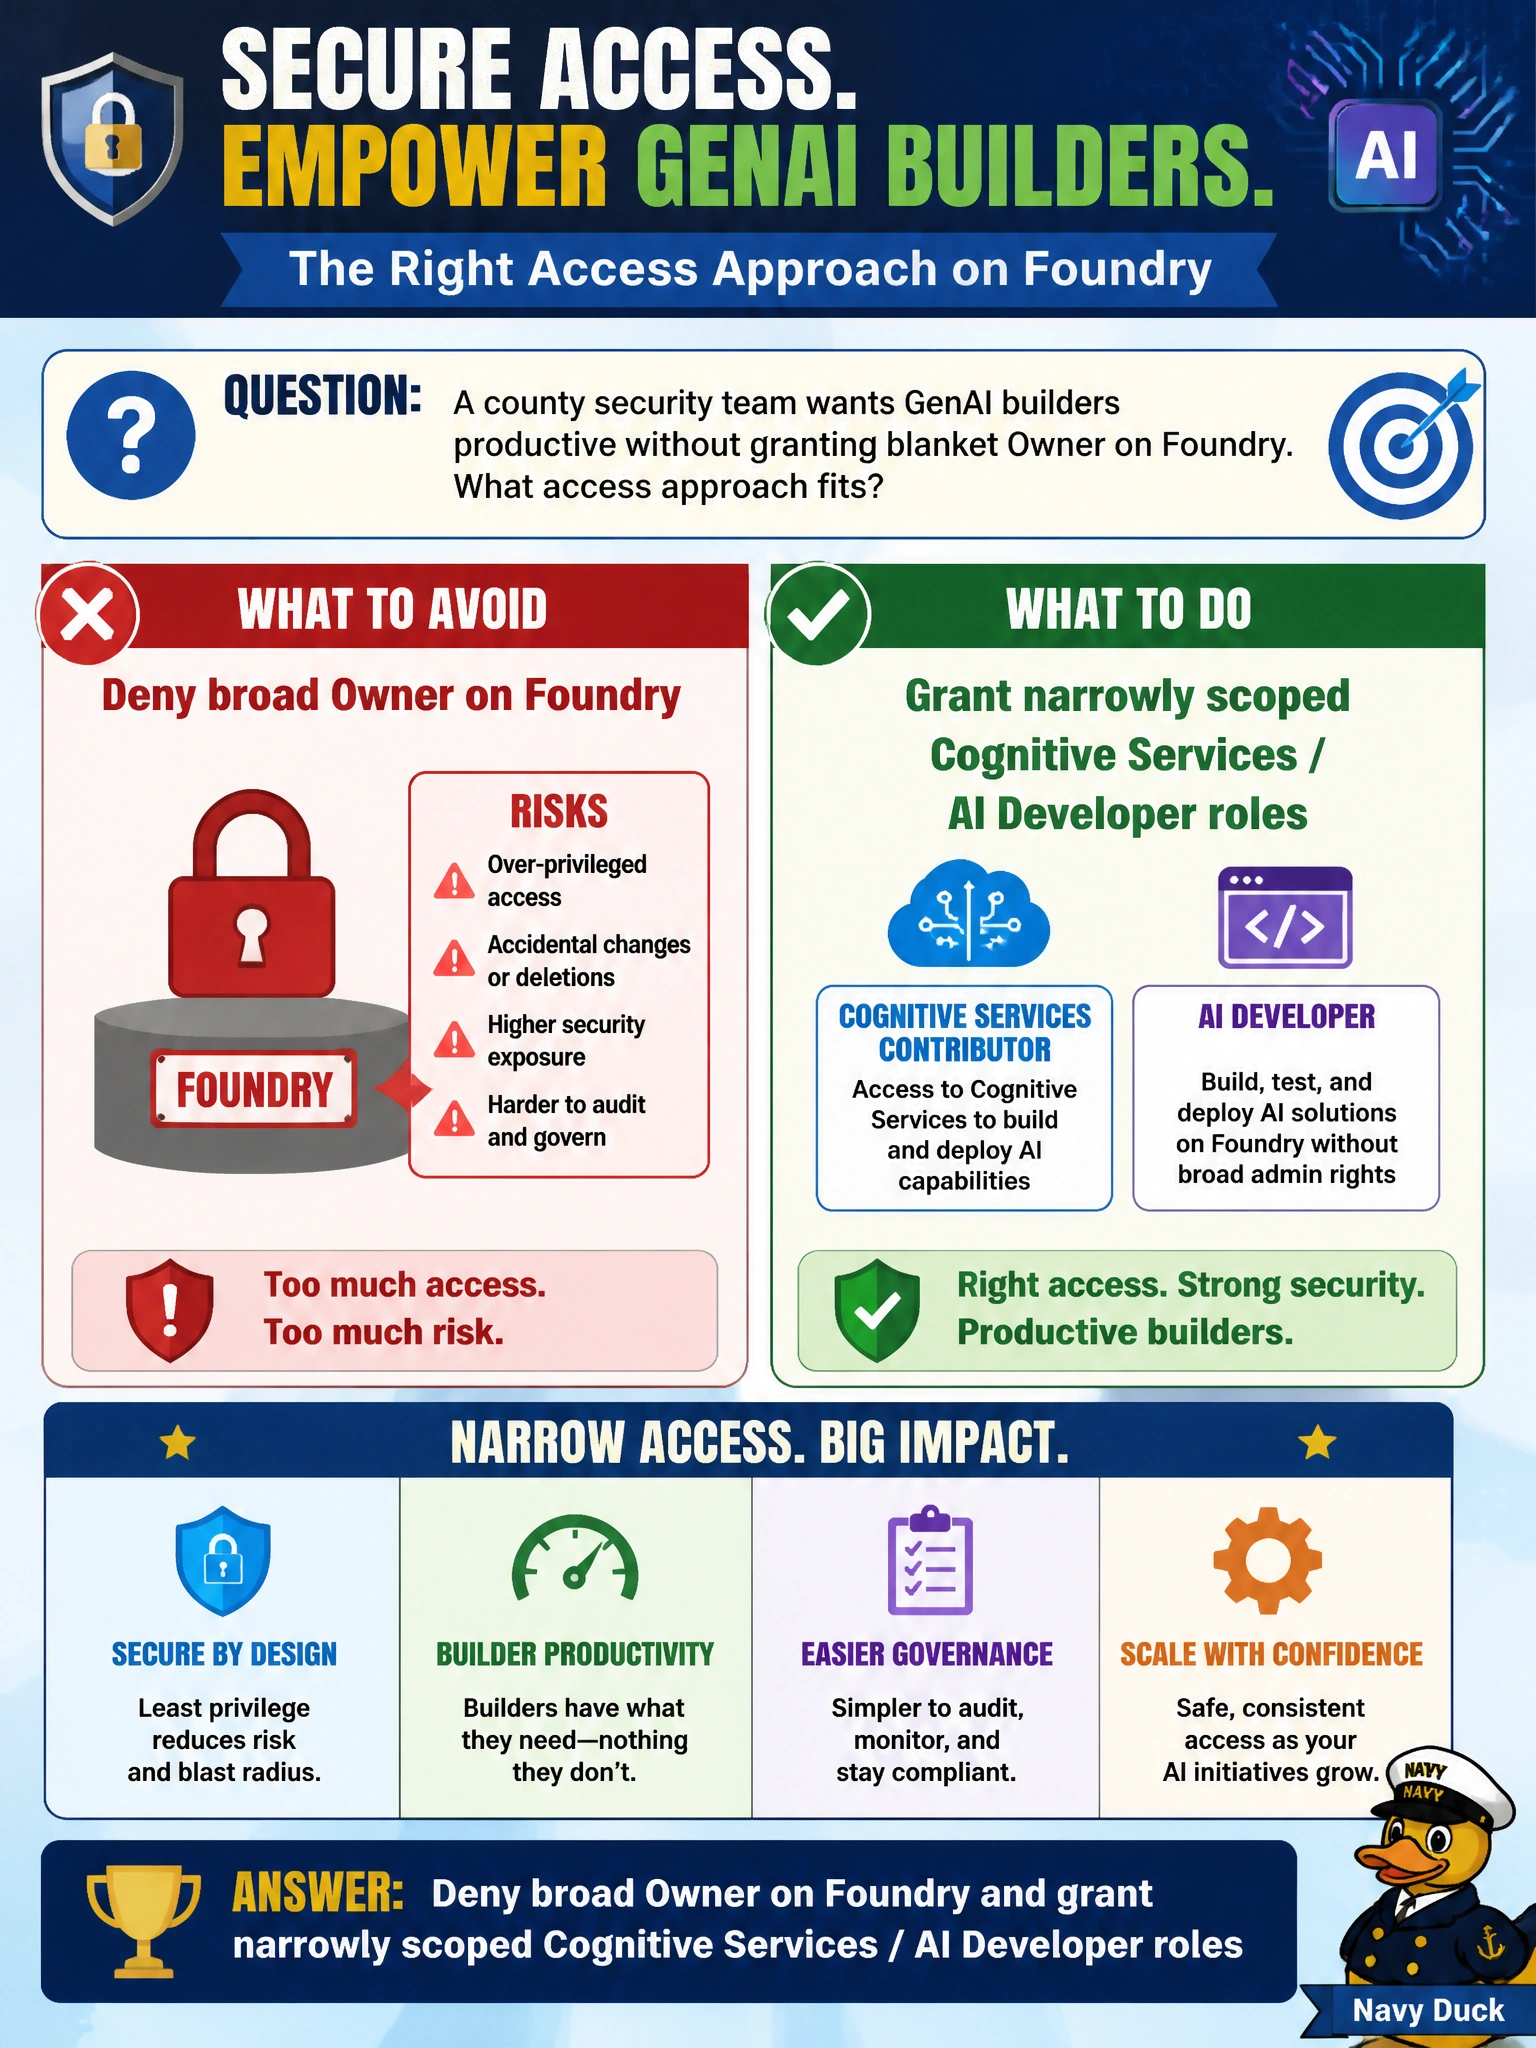
A county security team wants GenAI builders productive without granting blanket Owner on Foundry. What access approach fits?
Select an answer to reveal the explanation.
Short Explanation
Owner is a sledgehammer. Give builders narrow Cognitive Services or AI Developer-style roles so the county stays secure and people can still ship.
Full Explanation
Denying broad Owner on Foundry and granting narrowly scoped Cognitive Services / AI Developer roles is the correct access approach when a county security team wants GenAI builders productive without blanket Owner. Built-in Azure AI / Cognitive Services developer-oriented roles (and related project roles) allow builders to create and iterate GenAI assets inside approved boundaries while withholding subscription-wide or resource Owner powers such as unrestricted RBAC changes, deletion, or policy bypass. This keeps county GenAIOps moving without expanding the blast radius of contractors and staff.
Denying broad Owner on Foundry and granting narrowly scoped Cognitive Services Usages Auditor roles fails because the Usages Auditor role only permits auditing usage and does not allow builders to create, deploy, or iterate GenAI assets, so productivity is lost. Denying broad Owner on Foundry and granting narrowly scoped Azure AI Inference Deployment Operator roles fails because the Inference Deployment Operator role is limited to operating inference deployments and does not provide the full developer actions needed to build and test agents in Foundry. Denying broad Owner on Foundry and granting narrowly scoped AzureML Data Scientist roles per project fails because, even when scoped per project, the AzureML Data Scientist role targets classic machine-learning experimentation rather than the Foundry GenAI builder actions covered by Cognitive Services / AI Developer roles.
Exam caveat: “productive without Owner” almost always points to least-privilege AI/Cognitive Services developer roles rather than similarly worded Auditor, Inference Deployment Operator, or AzureML Data Scientist grants. Match the stem’s deny-Owner language to narrow Developer role grants and verify the role name.
Operational check: remove blanket Foundry Owner from builders, assign the narrow Cognitive Services / AI Developer-style roles required for their projects, and confirm builders can deploy/test agents while privileged platform actions remain with platform admins.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.