
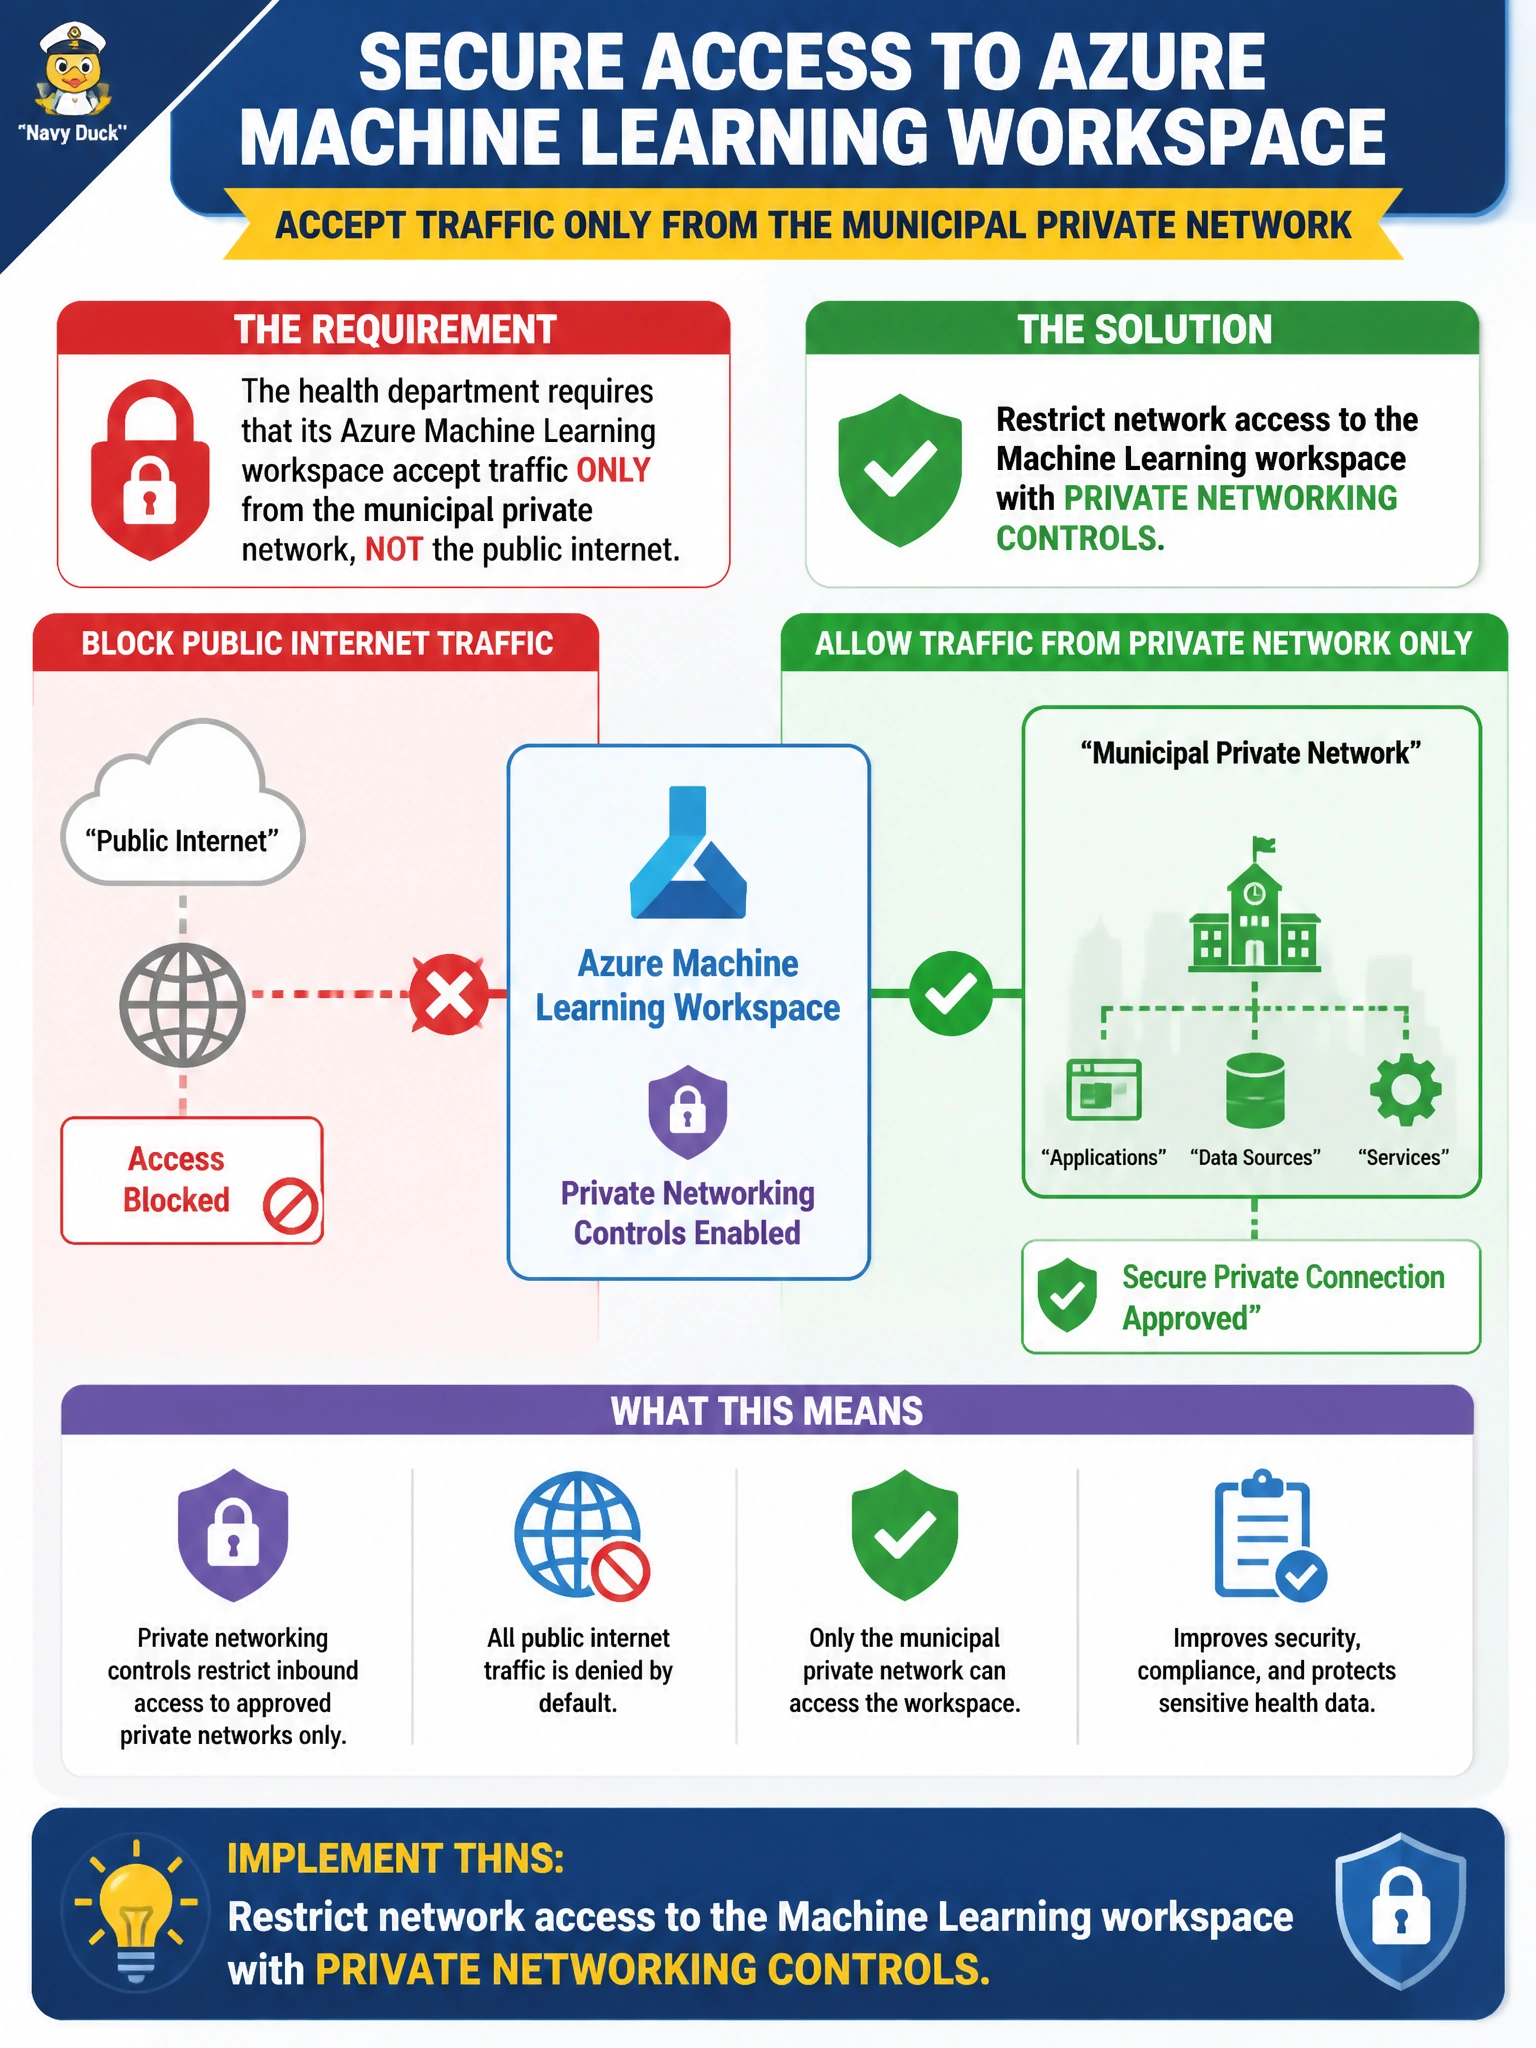
A health department requires that its Azure Machine Learning workspace accept traffic only from the municipal private network, not the public internet. What should the team implement?
Select an answer to reveal the explanation.
Short Explanation
Sensitive health data should not wave at the public internet. Lock the Azure ML workspace behind private networking so only the municipal network path reaches it. Using service firewall IP rules still leaves you reaching the workspace over the public internet, so it's not a private-only boundary.
Full Explanation
Restricting network access to the Azure Machine Learning workspace with private networking controls—typically private endpoints plus disabling public network access—keeps health-department traffic on the municipal private path. Training data, models, and studio endpoints then resolve through private DNS and hub/spoke or vWAN connectivity rather than a public IP. This is the Domain 1 control set for sensitive civic workloads where service firewall IP rules still leave a public endpoint, not a private network boundary.
Restricting network access to the Machine Learning workspace with service firewall IP rules fails by concept: IP-based firewall rules still expose a reachable endpoint on the public internet; the stem requires private networking only, not merely narrowing which public sources can reach it. Restricting network access to the Machine Learning workspace with compute virtual network integration fails the stem — securing training compute into a virtual network controls compute networking but does not make the workspace endpoint itself private-only; the department requires the workspace to be reachable only over the municipal private path, not merely VNet-integrated compute. Restricting network access to the Machine Learning workspace with outbound data exfiltration controls fails the stem outright: exfiltration controls govern outbound egress from the workspace, not whether the workspace endpoint is reachable over the public internet; they do not restrict inbound network access to the municipal private path.
Exam caveat: AI-300 expects candidates to know that private networking for Azure ML includes controlling public network access, not merely adding service firewall IP rules, integrating compute into a virtual network, or adding outbound exfiltration controls; answers that leave the workspace reachable over the internet are incorrect when the stem requires municipal private-network-only access.
Operational check: from a jump box on the municipal network, verify workspace connectivity over the private endpoint; from an internet host without VPN, confirm public access is denied; review workspace network settings for publicNetworkAccess Disabled and approved private endpoint connections.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.