
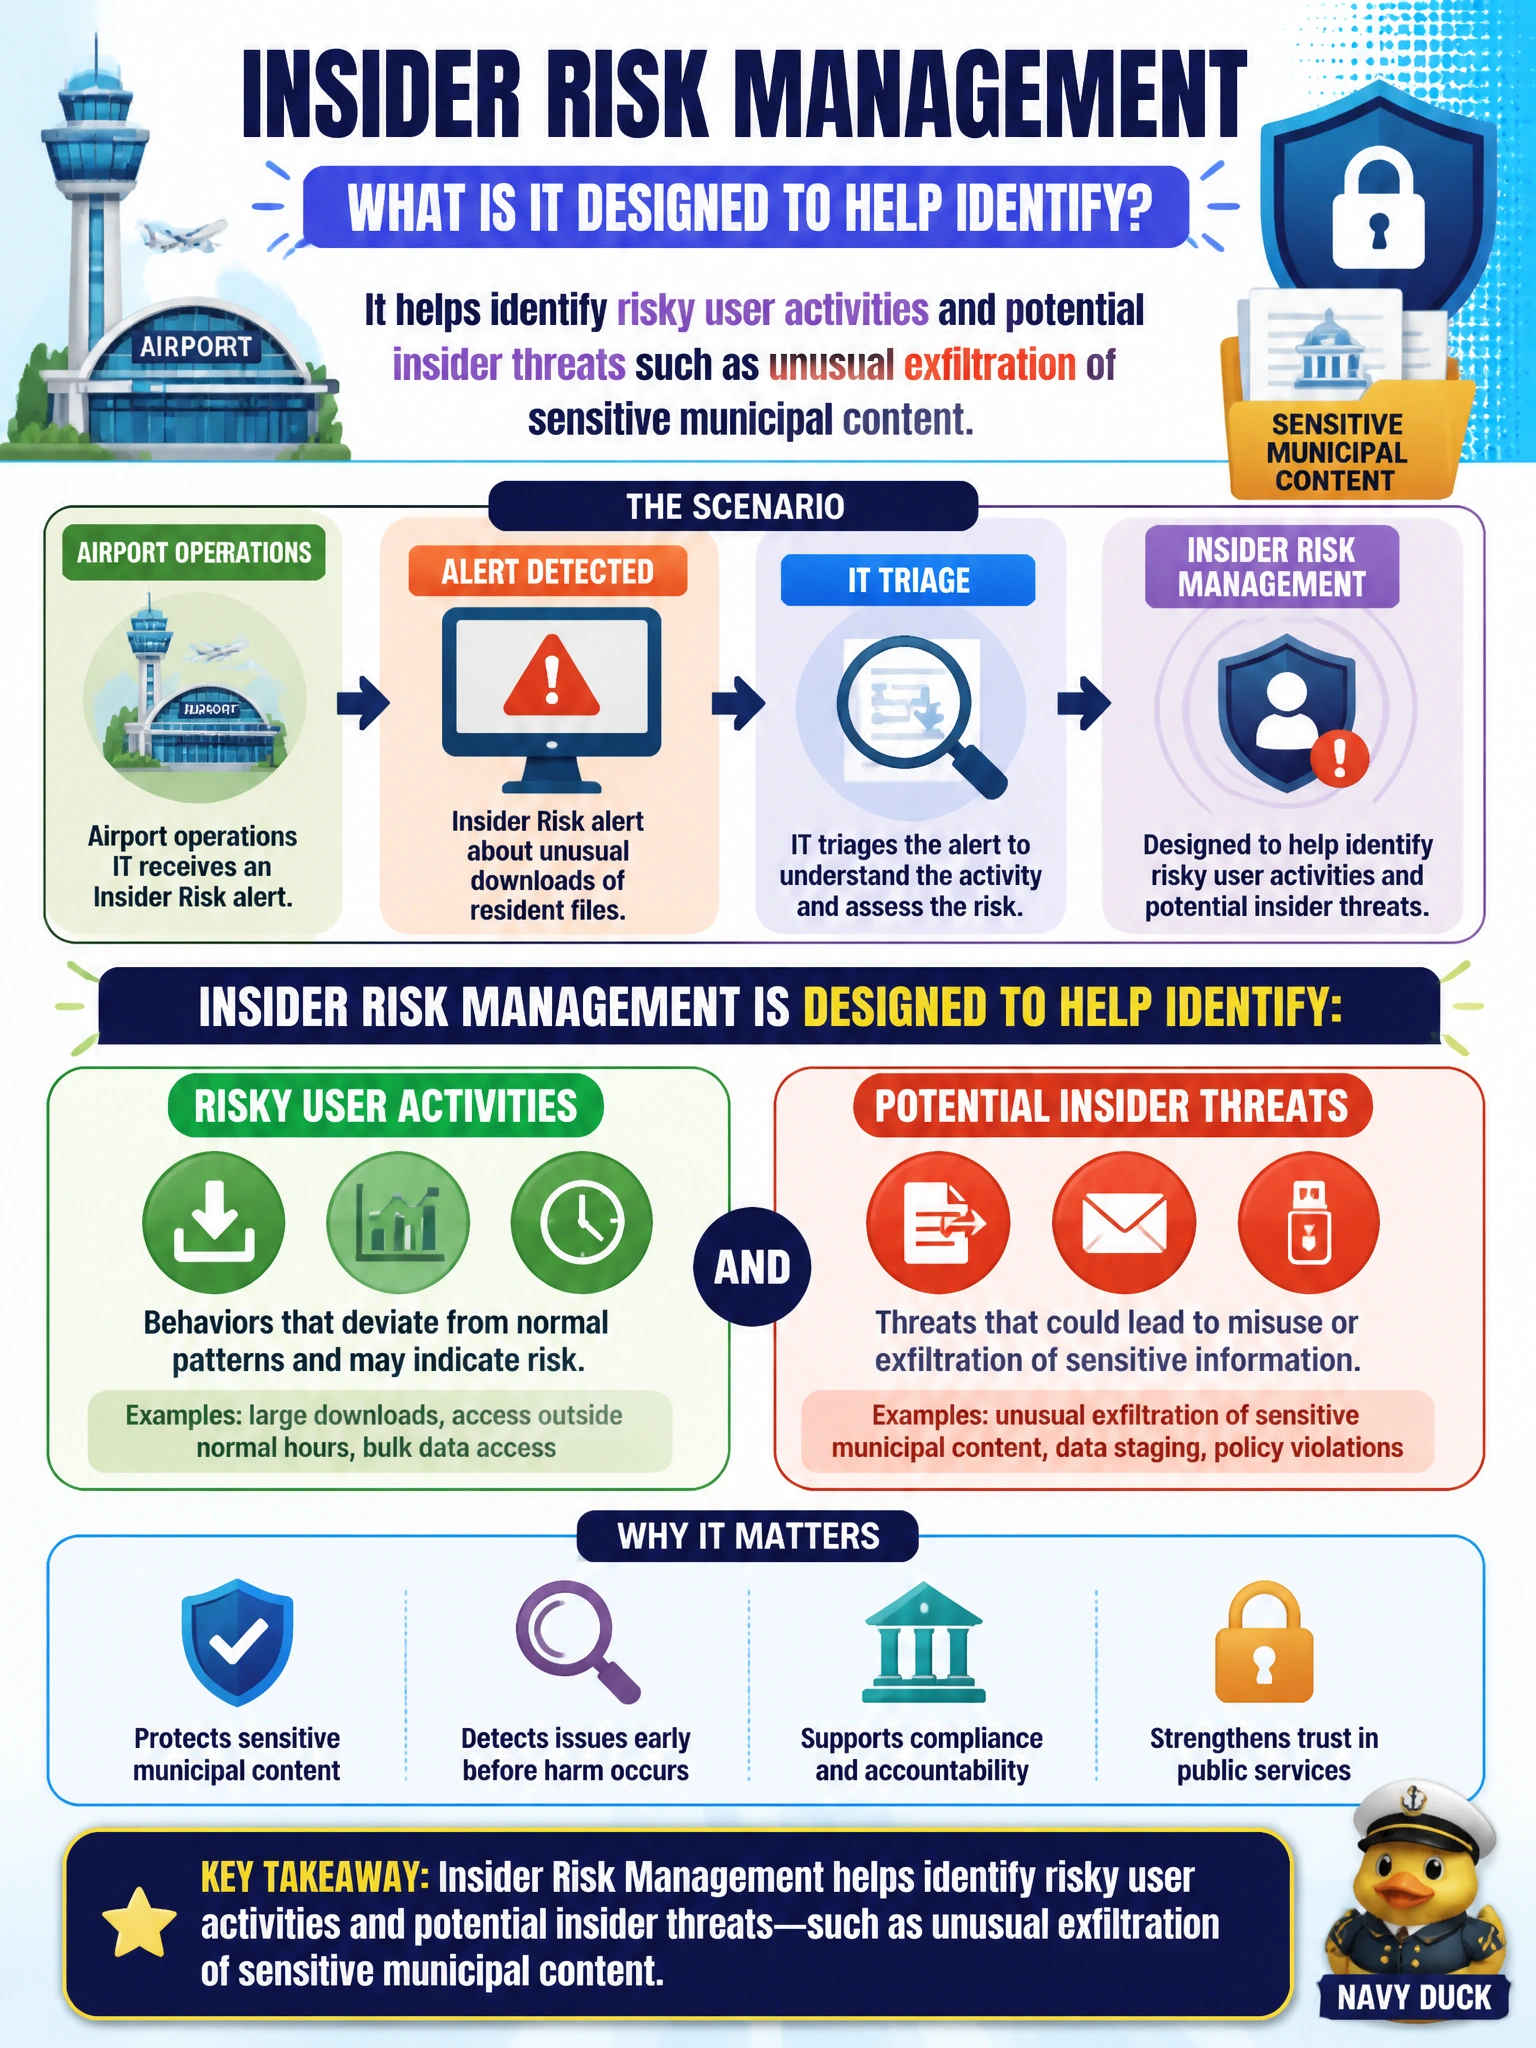
Airport operations IT triages an Insider Risk alert about unusual downloads of resident files. What is Insider Risk Management designed to help identify?
Select an answer to reveal the explanation.
Short Explanation
You'll see Insider Risk as the unusual-download smoke alarm for resident files—not external sharing flagged by data loss prevention, not inappropriate language in workplace chat and email, and not preserved custodial documents for municipal litigation review. Airport IT triages risky user activity that might mean exfiltration. That's the Purview signal family.
Full Explanation
Insider Risk Management is designed to help airport operations IT identify risky user activities and potential insider threats such as unusual exfiltration of sensitive municipal content. An alert about unusual downloads of resident files fits that purpose: the capability correlates user activity patterns that may indicate data theft, misuse, or policy-violating exfiltration—distinct from malware signature detection alone.
Risky user activities and potential insider threats such as external sharing flagged by data loss prevention fails the insider-risk concept: DLP-flagged external sharing is a data-movement policy match but doesn't correlate user behavior patterns to identify insider threats. Risky user activities and potential insider threats such as inappropriate language in workplace chat and email fails similarly: detecting inappropriate workplace language is communication compliance, a separate governance lane, not Insider Risk Management's user-activity correlation. Risky user activities and potential insider threats such as preserved custodial documents for municipal litigation review fails entirely: preserving custodial documents for litigation is an eDiscovery legal hold process, not a capability that identifies risky user activities or insider threats.
Exam caveat: AB-900 expects identify-level understanding that Insider Risk Management focuses on potentially risky user activities and insider threats. It does not require building custom risk indicators from scratch. Do not confuse it with Defender malware detection or with external sharing flagged by data loss prevention framed as insider-threat identification—these are adjacent but different Purview/security lanes.
Operational check: When an unusual-download alert fires, confirm the user, scope of files, and timeframe in Insider Risk Management; preserve evidence; engage the appropriate security/HR path; and verify that legitimate ops export jobs are documented so true anomalies stand out.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.