
Tailwind Toys' security team is hardening their Microsoft 365 environment. They want the Exchange Administrator role to follow a zero-standing-access model: no one should have the role active at all times. When someone needs it, they must submit a business justification and get approved by the security team lead before the role activates. Which configuration in Microsoft Entra Privileged Identity Management (PIM) achieves this?
Select an answer to reveal the explanation.
Short Explanation
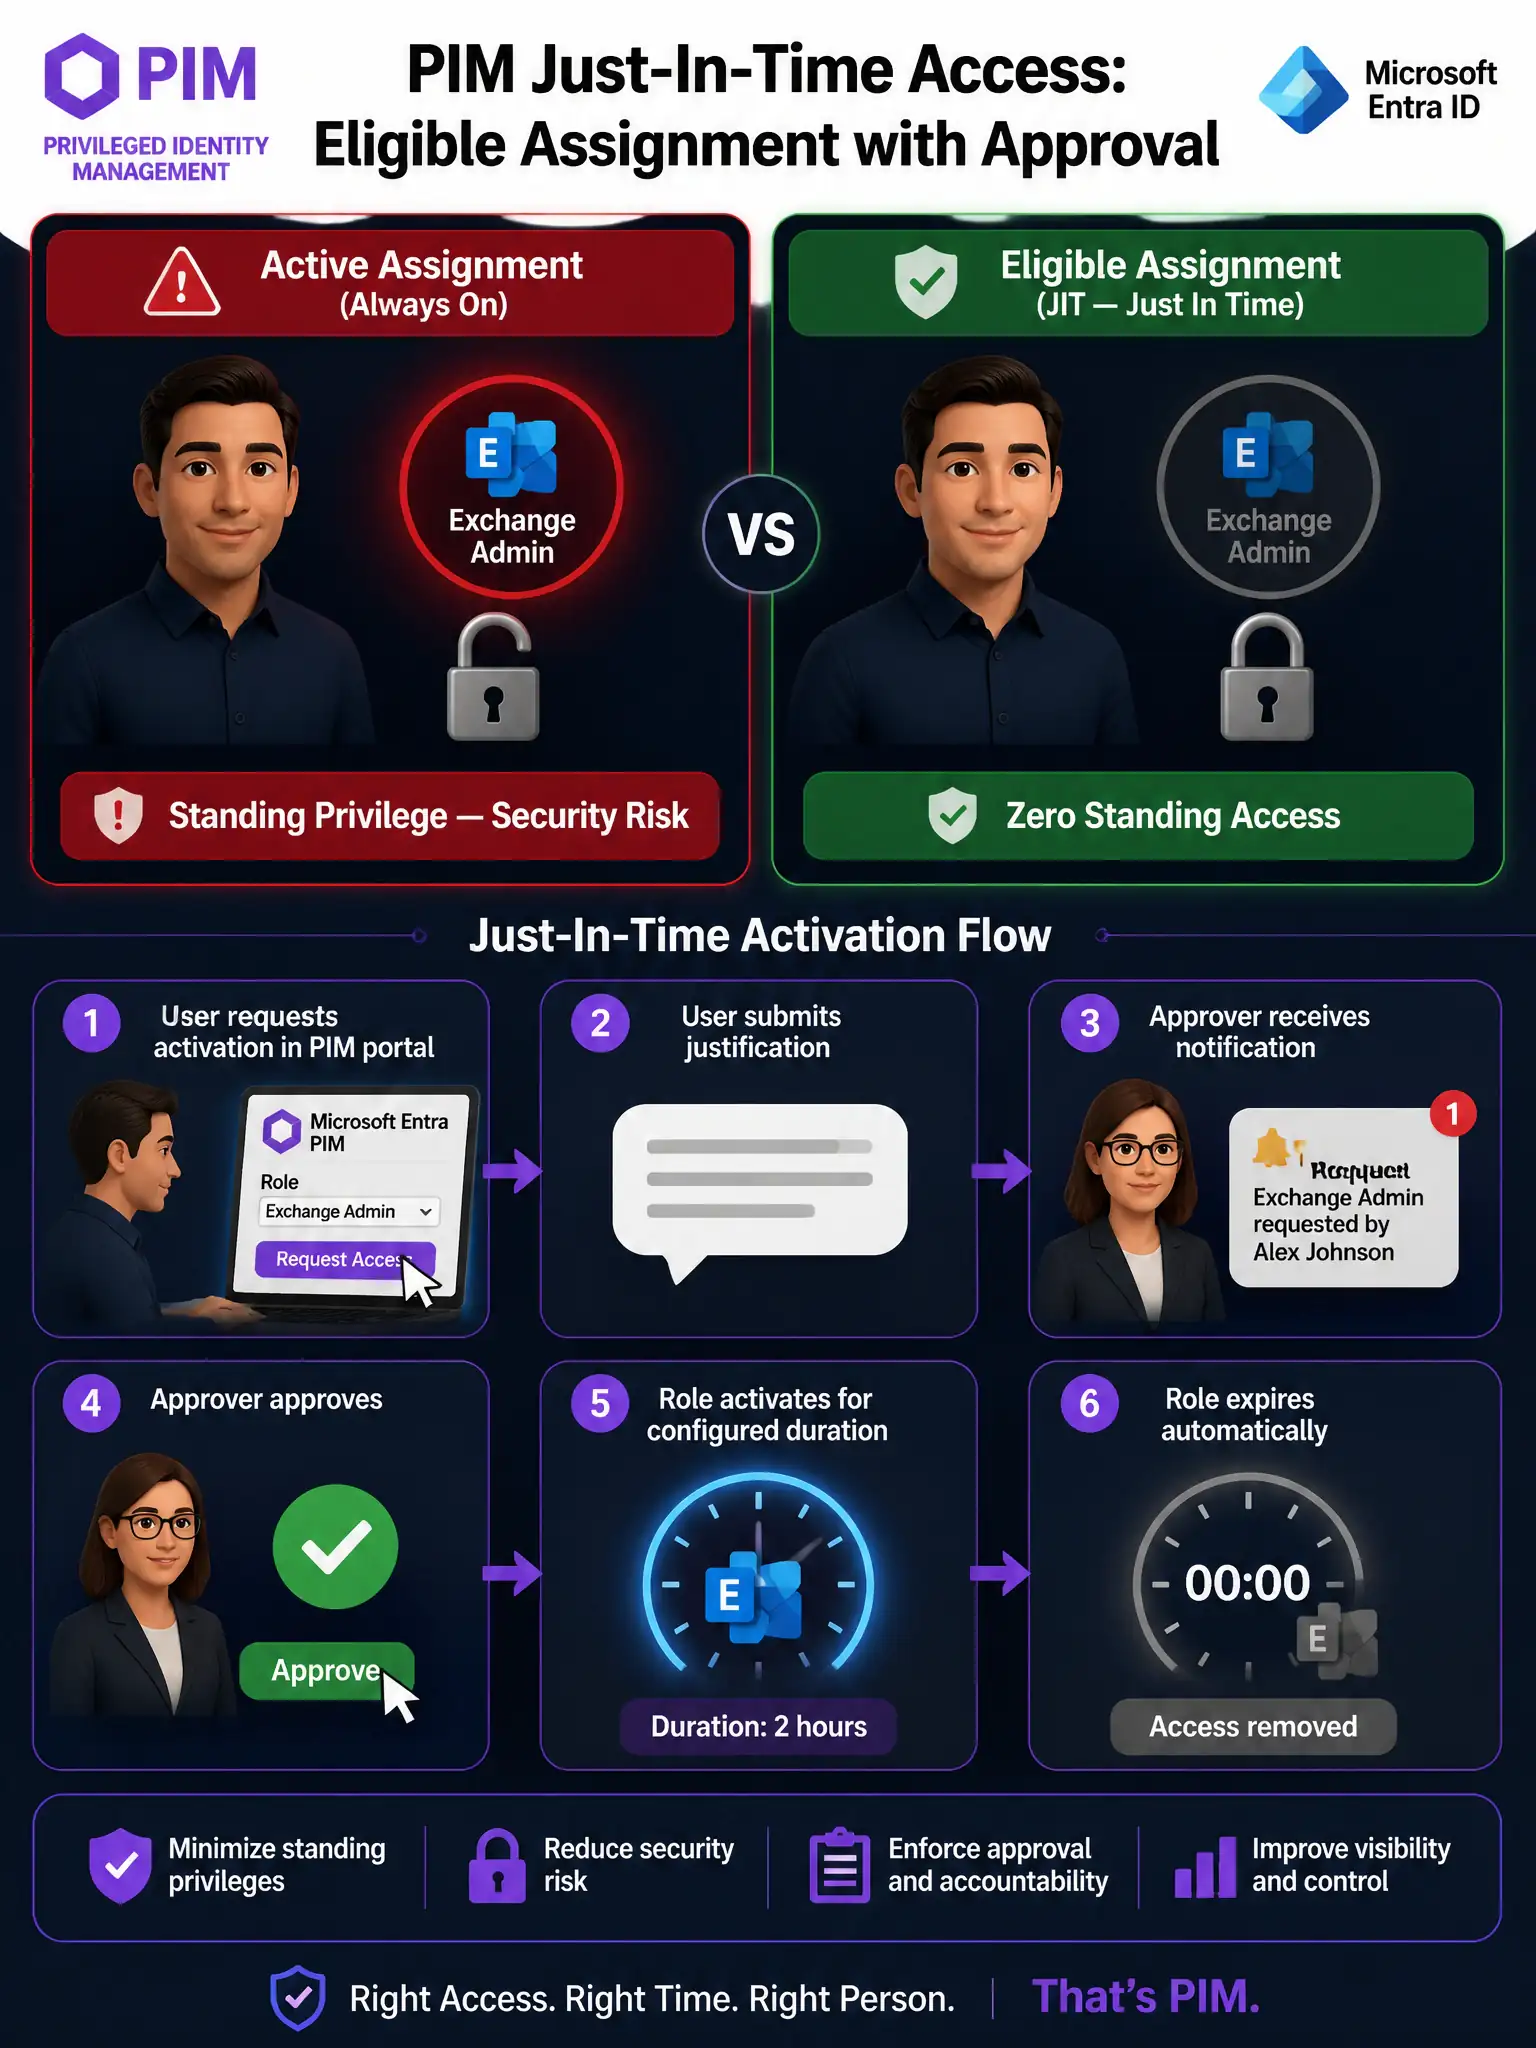
Eligible is like a spare car key locked in a safe — you have the right to use it, but you don't drive until approval comes through. Requiring justification and approval before activation gives you zero standing access with an auditable trail.
Full Explanation
The correct configuration is to configure the Exchange Administrator role in Microsoft Entra Privileged Identity Management (PIM) as an Eligible assignment, then enable Require approval to activate and Require justification on activation in the role settings. PIM supports two assignment types for Entra roles: Active, where the role is always on, and Eligible, where the user can activate the role when needed, subject to configured requirements. For a zero-standing-access model, Eligible is the right assignment type. Within PIM role settings for Exchange Administrator, Require justification on activation makes the user type a business reason, and Require approval to activate makes a designated approver — the security team lead in this case — approve the request before activation occurs. This creates a full, auditable just-in-time access workflow. The permanently active PIM assignment paired with a Conditional Access MFA requirement is wrong because an Active assignment means the role is permanently enabled, so the user always has Exchange Administrator rights. That is the opposite of zero-standing-access. Adding a Conditional Access MFA requirement only adds an authentication step; it does not remove the standing privilege, and the role is still always on. The Conditional Access policy that blocks access to the Exchange Admin Center unless the user is a member of a specific security group, with users added when access is needed, is wrong because Conditional Access policies control access to applications and resources based on conditions such as device compliance, location, and MFA, but they do not manage privileged role activation. Security-group-based access to the Exchange Admin Center is a coarse, unaudited workaround; it doesn't integrate with PIM's approval workflow, activation limits, or audit logs the way proper PIM eligible assignments do. The Azure Bastion just-in-time access approach with a 4-hour session window is wrong because Azure Bastion is a secure remote access service for connecting to Azure virtual machines via the browser. It has nothing to do with Microsoft Entra role management or Exchange Administrator. It is a distractor designed to test whether you confuse Azure PaaS services with Entra identity governance features. Exam tip: PIM questions almost always hinge on the Active vs. Eligible distinction. Memorize this: Eligible = just-in-time, where the user requests activation; Active = always on, which is standing privilege. Any scenario mentioning 'only when needed,' 'temporary,' 'request-based,' or 'zero standing access' points to Eligible with appropriate activation settings.