
A Dataverse plug-in must read a signing key from Azure Key Vault each time it runs. The security team prohibits client secrets or certificates stored in plug-in configuration, environment variables or code, and wants access granted through Microsoft Entra ID role assignments. Which approach should the developer use?
Select an answer to reveal the explanation.
Short Explanation
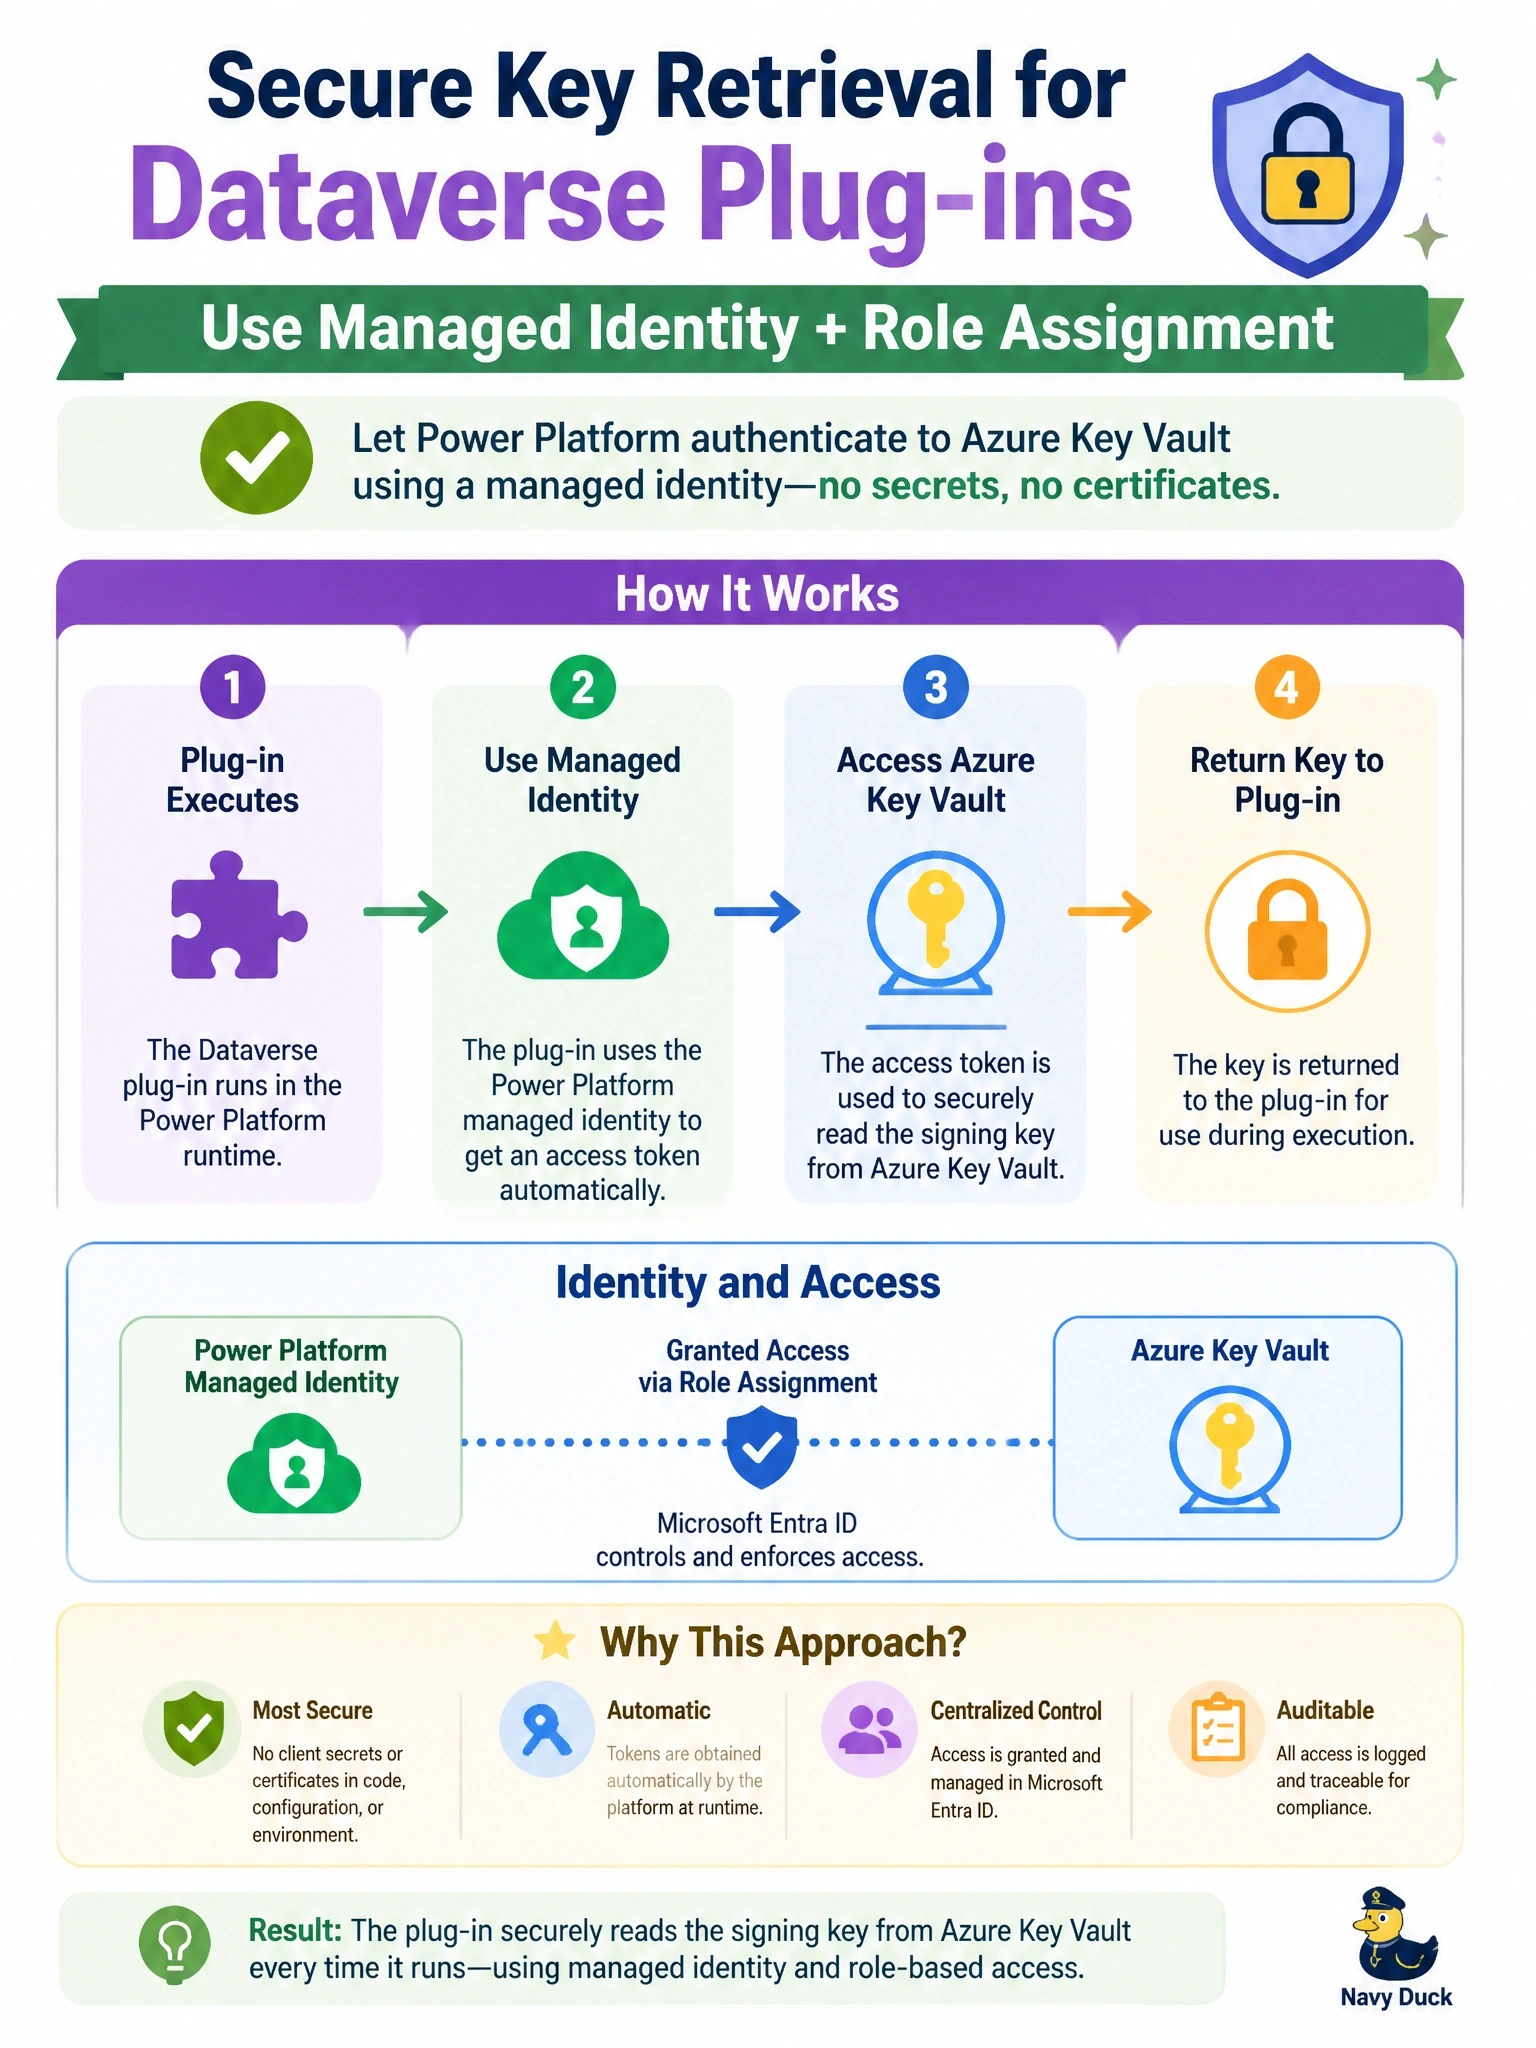
Managed identity gives your plug-in its own Entra ID badge, so there's no password to store anywhere. You grant the badge access to the vault and the plug-in asks for tokens on demand. The trap is secure configuration, which feels safe but is still a stored secret.
Full Explanation
Power Platform managed identity lets Dataverse plug-ins and plug-in packages obtain Microsoft Entra ID tokens without managing credentials. The plug-in assembly is linked to a managed identity record in Dataverse that represents an Entra app registration or user-assigned managed identity, trust is established through a federated identity credential, and the identity is granted access to the target resource, here Key Vault, through Azure role assignments. At runtime the plug-in requests a token through IManagedIdentityService and calls Key Vault with it, so no secret exists in configuration or code. Secure configuration is encrypted storage on the step, but it still holds a client secret, which the security team prohibits, and secrets must be rotated manually. Placing the app registration's certificate in an environment variable stores a credential in configuration, which is explicitly prohibited, and anyone able to read the variable could impersonate the app. Anonymous access to Key Vault is not possible, because every Key Vault data-plane request requires an Entra ID token, and IP restrictions do not authenticate a caller. Exam caveat: the plug-in assembly or package must be signed with a certificate for managed identity. Operational check: trigger the plug-in and confirm in the trace log that a token is acquired and Key Vault returns the key without any configured secret.