
A Chief Risk Officer is implementing an AI governance structure. She proposes that AI risk oversight be embedded within the existing Three Lines of Defense model. How should AI risk oversight MOST appropriately map to this model?
Select an answer to reveal the explanation.
Short Explanation
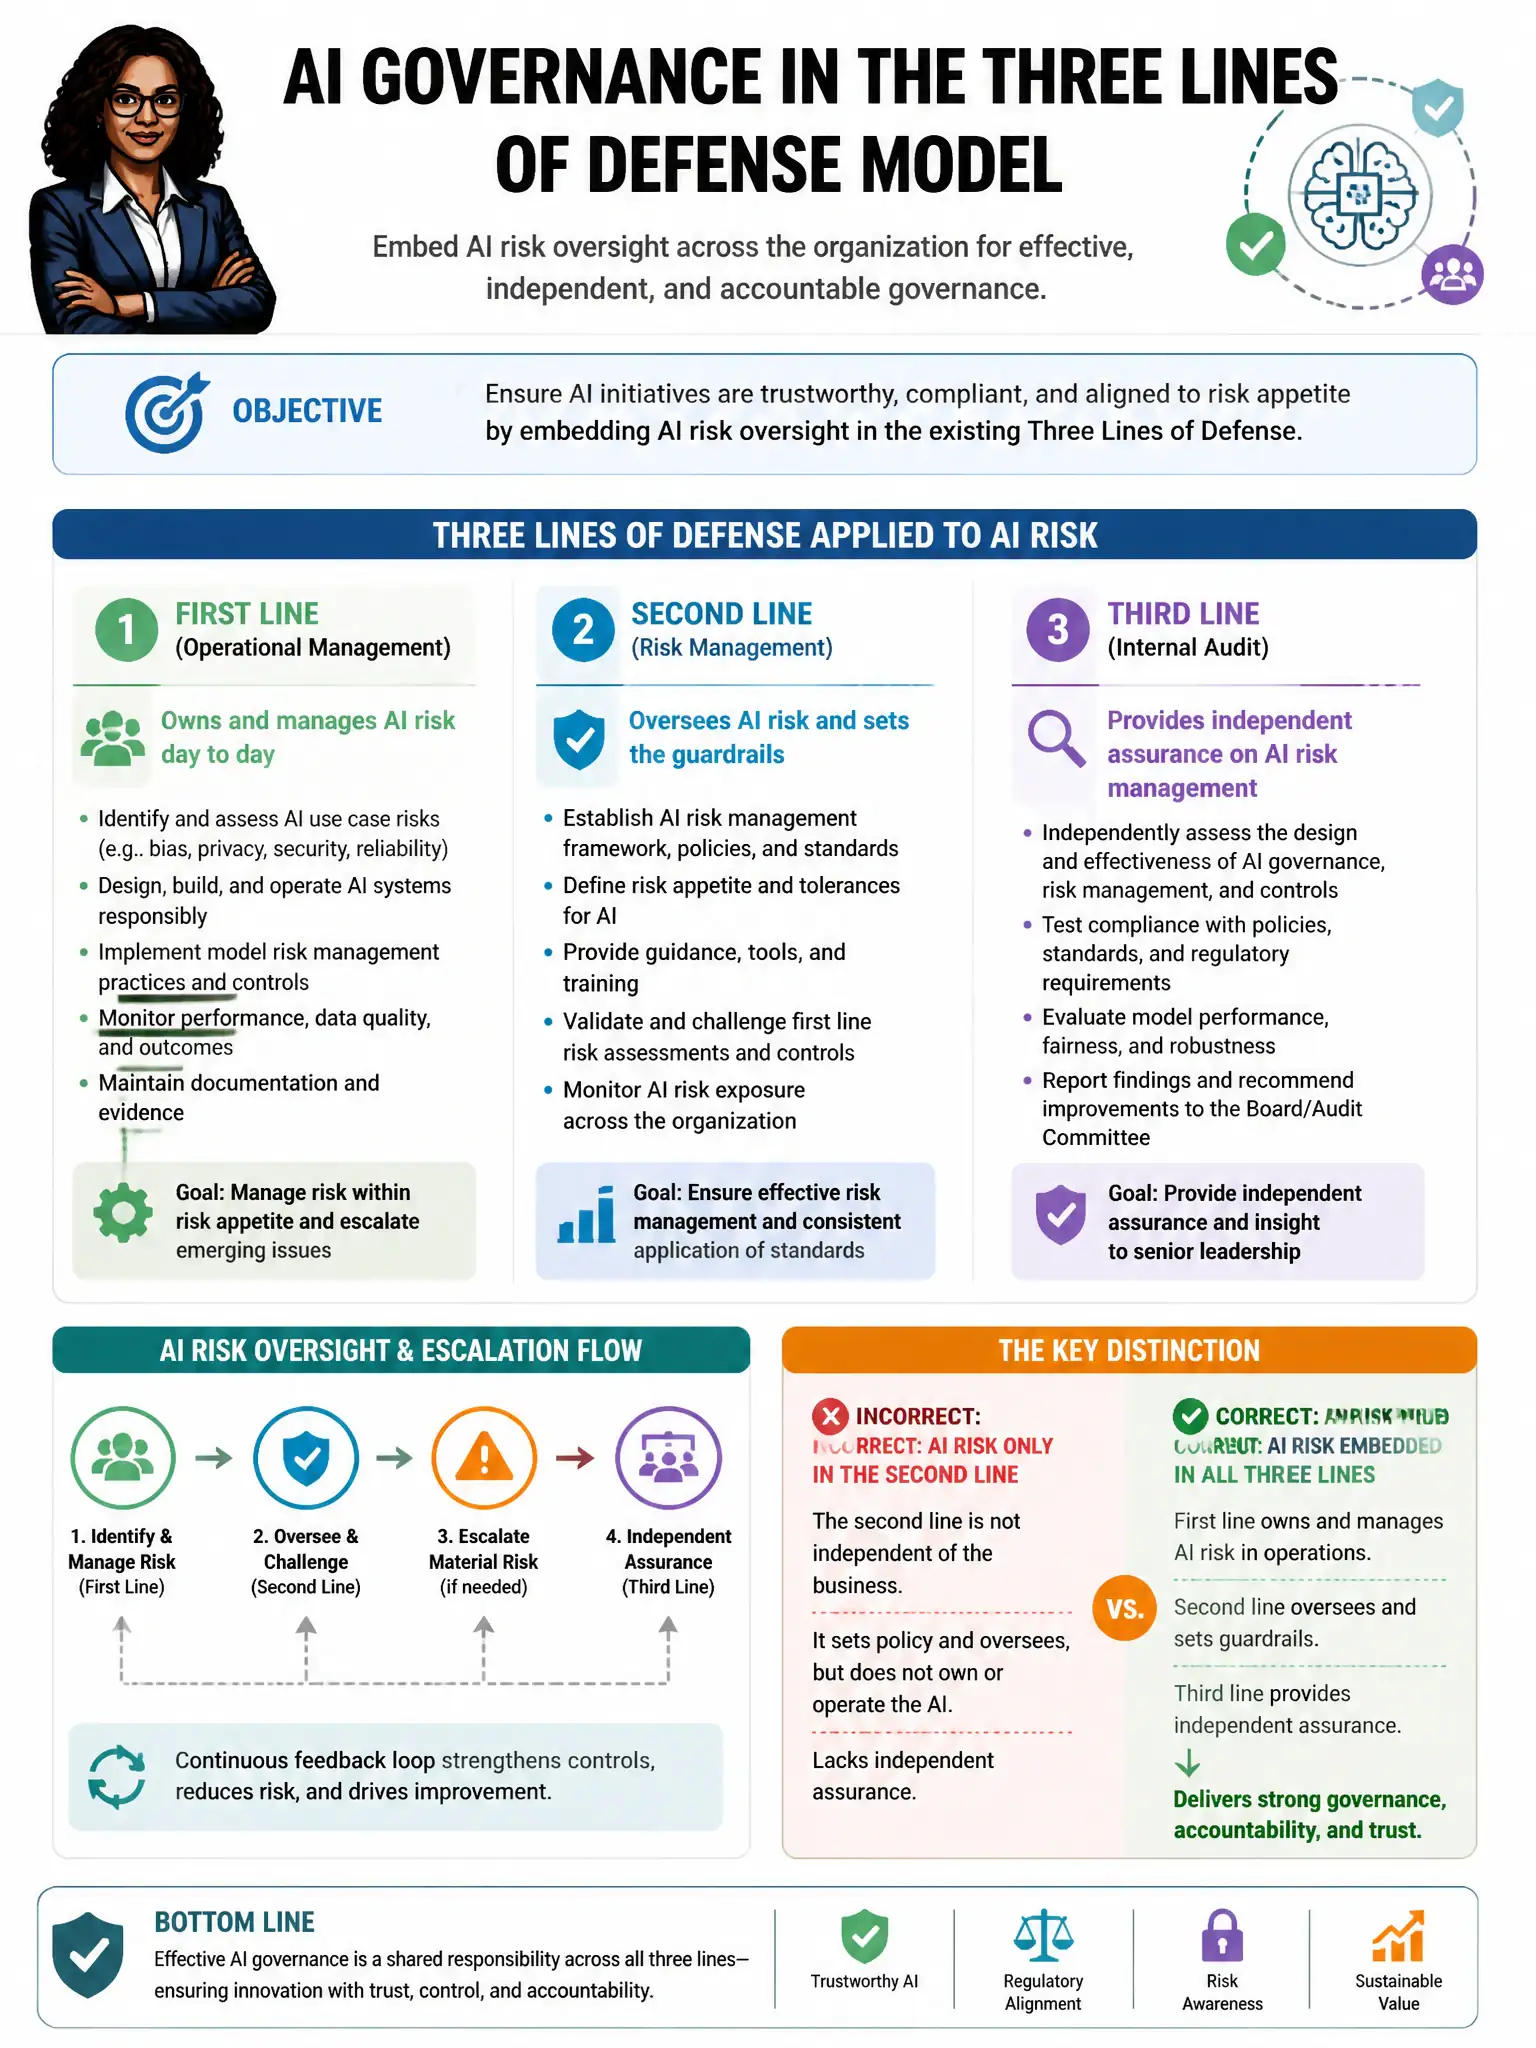
Here's the deal — you map AI risk oversight across all three lines: business units own AI risk day-to-day, the risk function sets frameworks and oversight, and internal audit independently validates controls. Centralizing it all in the risk function strips accountability from the teams using the systems.
Full Explanation
The correct mapping is that first-line business units own AI risk day-to-day; the second-line risk function provides AI risk frameworks, policies, and independent oversight; and third-line internal audit independently validates AI controls. The centralized second-line approach removes day-to-day accountability from business units. The continuous-monitoring-by-internal-audit approach would compromise audit independence. The separate fourth-line approach is not a recognized governance structure and would create confusion about accountability.