
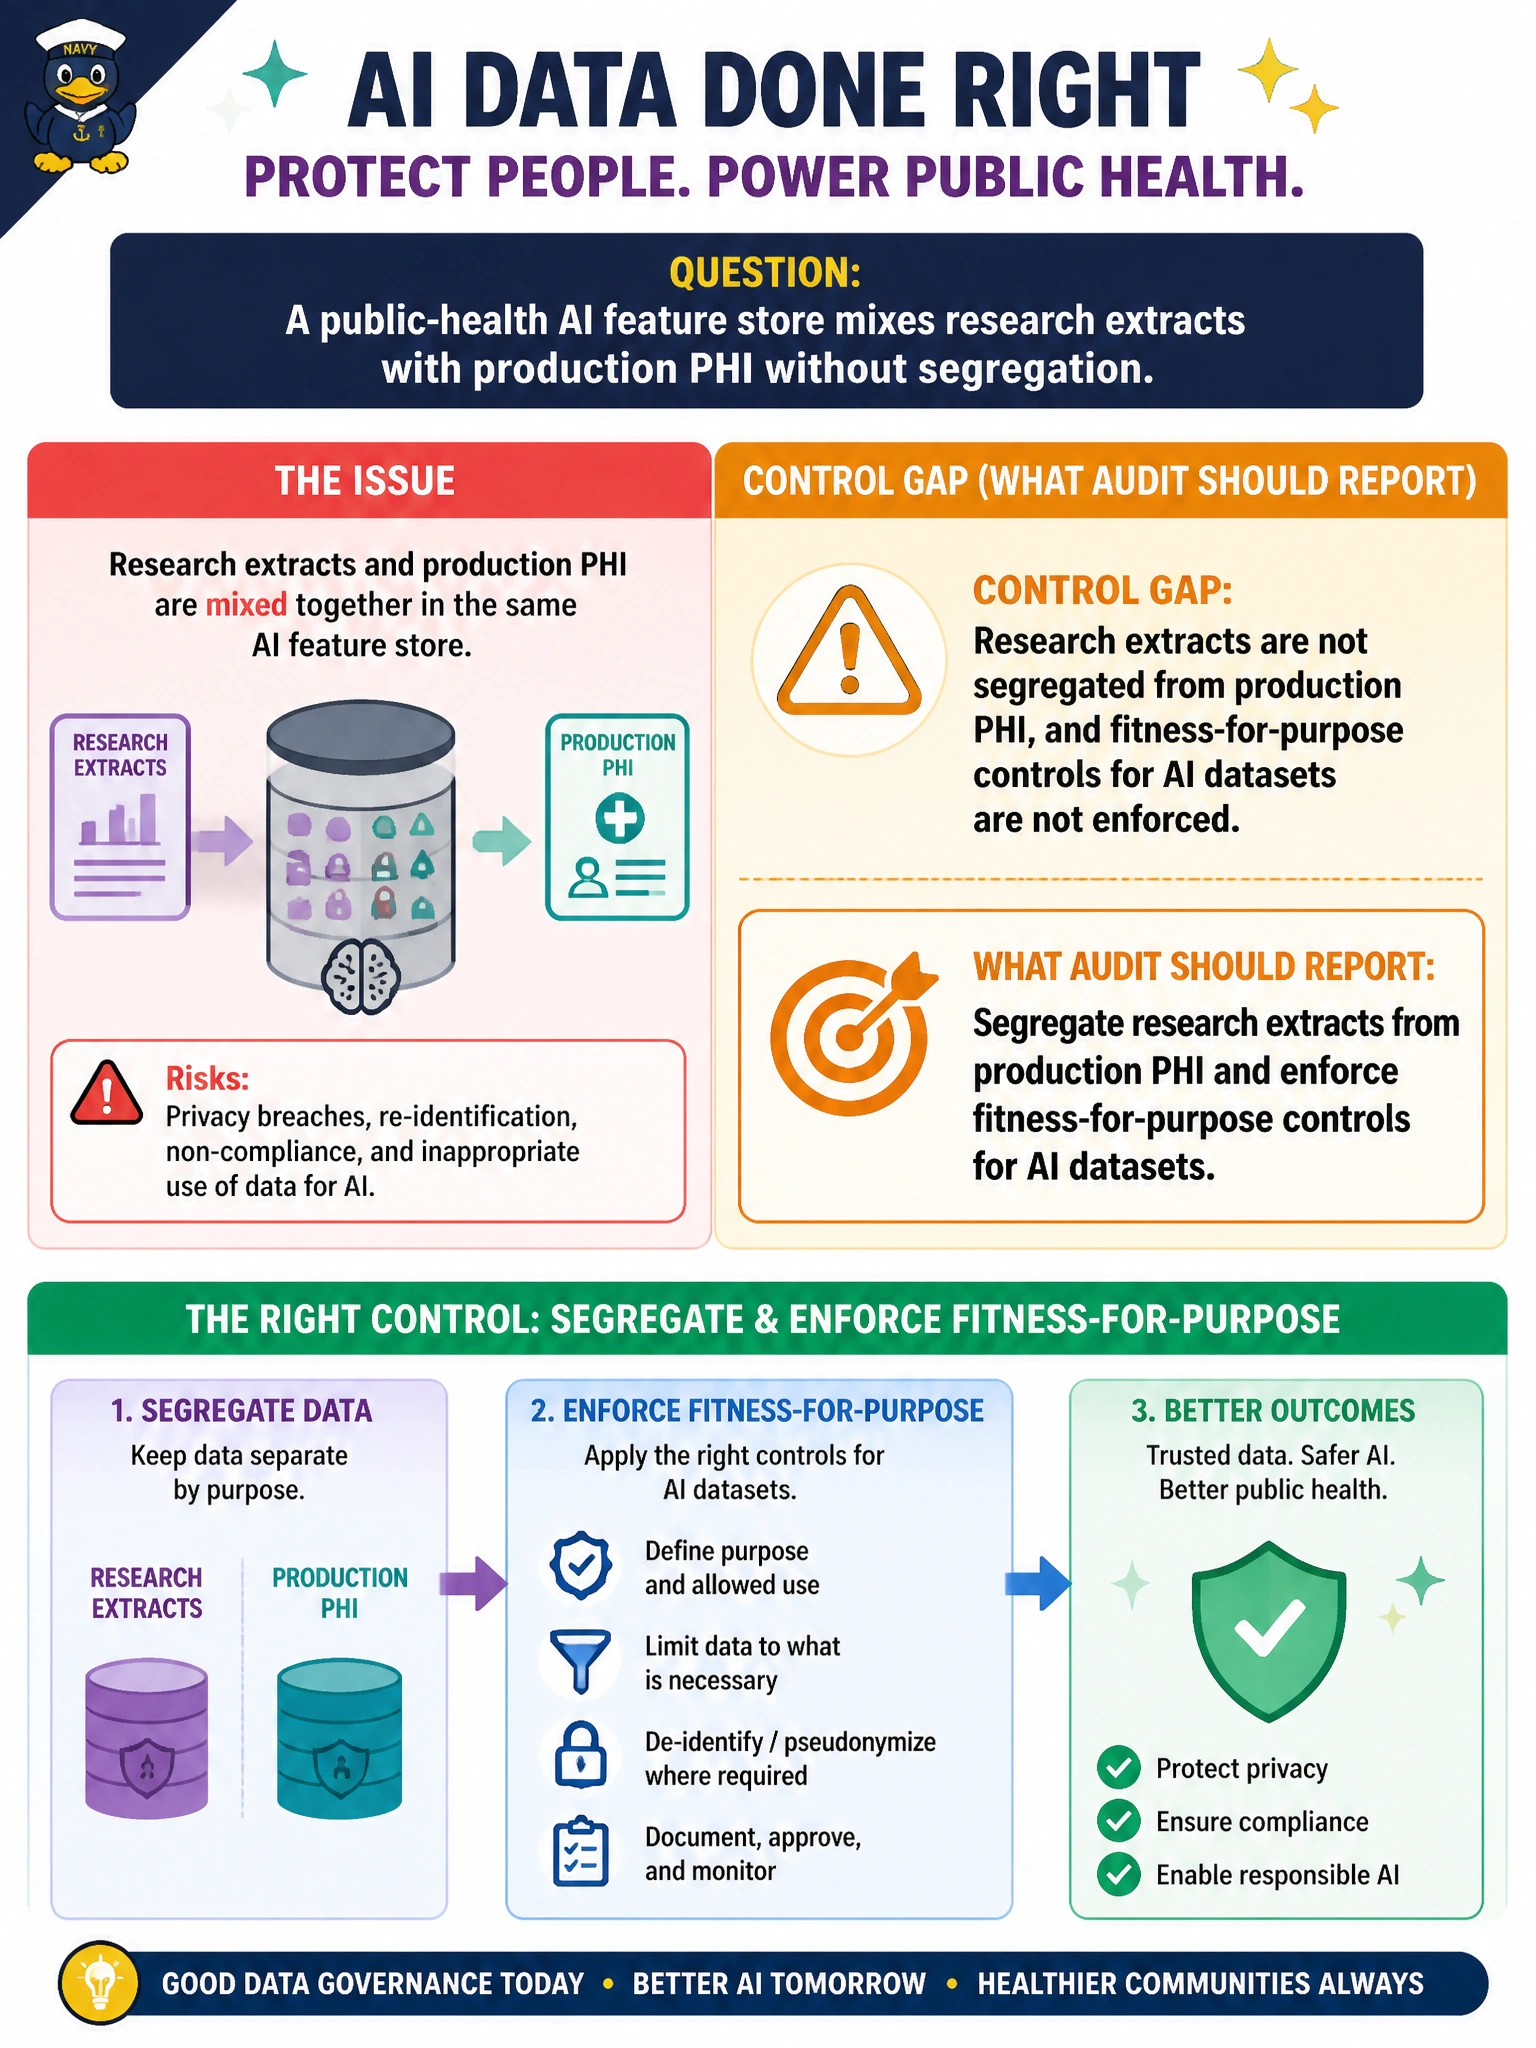
A public-health AI feature store mixes research extracts with production PHI without segregation. What control gap should audit report?
Select an answer to reveal the explanation.
Short Explanation
Research leftovers and live PHI do not belong in the same AI blender. Separate them and prove each dataset is fit for its purpose. Encrypting the unified store at rest doesn't enforce purpose limitation.
Full Explanation
A public-health AI feature store that mixes research extracts with production PHI without segregation expands privacy and misuse risk by blurring allowable-use boundaries. Audit should report the gap and require segregating research extracts from production PHI and enforcing fitness-for-purpose controls for AI datasets so each cohort is used only for authorized research or production purposes with appropriate access, retention, and monitoring. Encrypting the unified feature store at rest and relying on encryption for dataset purpose limitation fails by concept: encryption protects confidentiality but does not enforce purpose-based segregation or prevent research extracts from being used as production PHI. Standardizing feature schemas and relying on data quality checks for research-to-production governance fails by concept: schema alignment and data-quality checks do not authorize research PHI for production inference or enforce fitness-for-purpose controls. Cataloging detailed lineage for mixed extracts and reviewing dataset fitness during scheduled model performance reviews fails by concept: lineage and periodic performance reviews are detective and periodic, not preventive, and they do not segregate research extracts from production PHI. Exam caveat: AAIA AI data-management items on health data reward segregation and fitness-for-purpose enforcement—not encryption as a purpose substitute, schema standardization and data-quality checks as governance shortcuts, or lineage cataloging and scheduled reviews in place of access segregation. Operational check: separate research and production feature spaces, tag datasets with purpose and PHI classification, enforce access policies per purpose, restore comprehensive access logging, and sample jobs for cross-purpose leakage.