
A program manager pilots a coding agent that drafts release notes and customer emails from internal GitHub issues for a healthcare client. Legal requires no personal health data leaves the workspace, auditability of AI suggestions, and human approval before sending. Which Responsible AI safeguard should the program manager require first for agent use?
Select an answer to reveal the explanation.
Short Explanation
You stay in charge when the agent shows its work and waits for you. Guardrails plus human oversight are like seatbelts for speedy helpers. That combo keeps data inside bounds and decisions reviewable.
Full Explanation
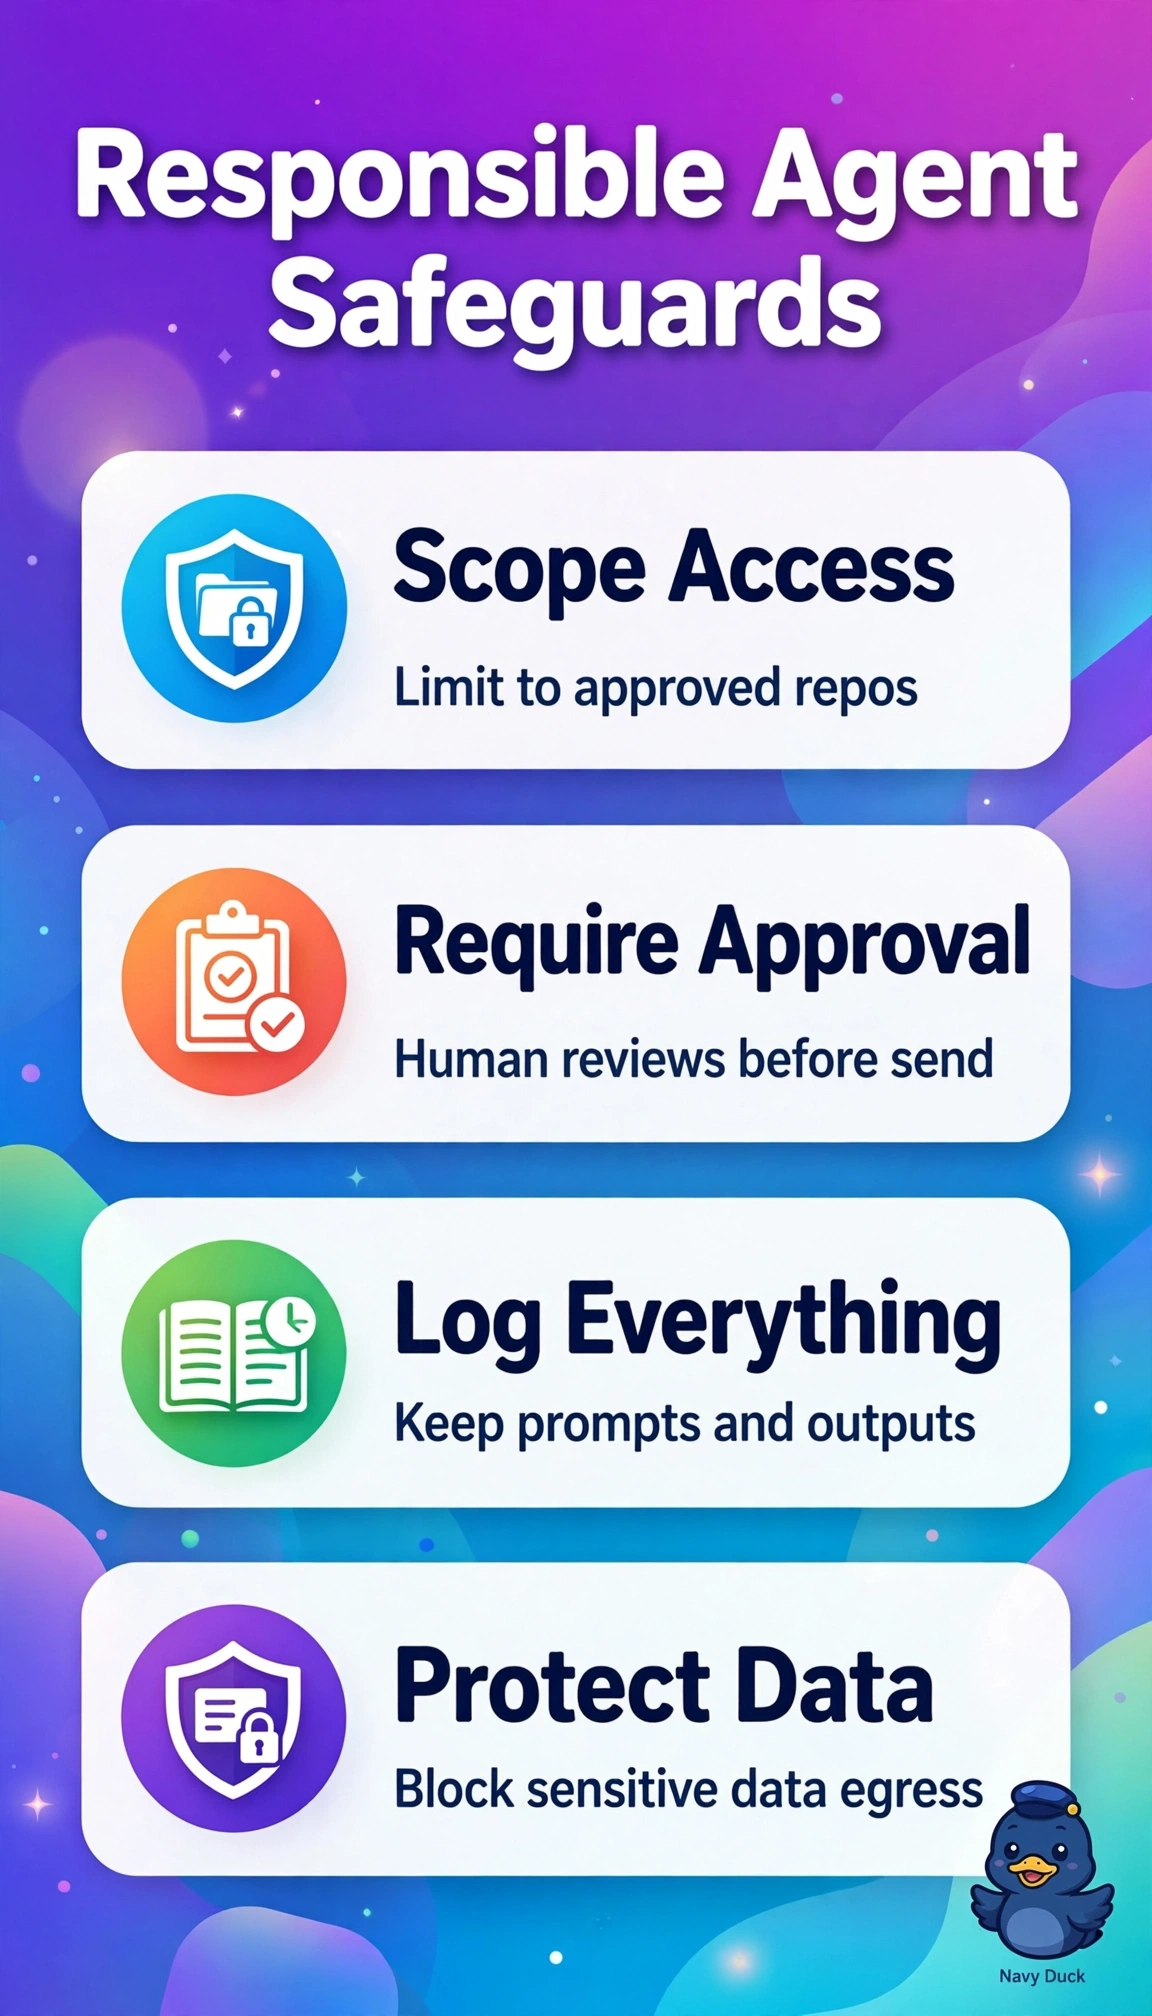
The correct safeguard is required first because it simultaneously enforces all three legal constraints for healthcare content: containment of personal health data within approved repositories, complete auditability of AI suggestions, and human approval before any customer communication, which together prevent unlawful disclosure while preserving traceability and accountability for drafts derived from internal GitHub issues. Allowing the agent to access all linked workspaces fails by data containment because even with strong approval and logging, expanded scope increases the risk that personal health data leaves the controlled workspace through retrieval, context sharing, or drafting in external services. Enabling automatic sending for routine emails fails by human oversight because efficiency for low-risk messages still violates the explicit requirement for human approval before sending, and routine healthcare communications can still contain sensitive context or errors that require review. Logging only final sent messages fails by auditability because retaining outcomes without prompts, draft suggestions, edits, and rejections prevents reconstruction of what the agent proposed and why the human decided as they did, which legal review requires. An exam caveat is that plausible productivity trade-offs do not override explicit legal constraints, so any choice that weakens containment, oversight, or traceability is incorrect even when it reflects a common enterprise pattern. A practical check is to verify in the pilot that the agent cannot select unapproved repositories, that every suggestion and approval action is immutably logged, and that sending remains technically disabled until documented human approval is recorded.