
A university research program manager enables Copilot and coding agents for 40 graduate assistants documenting open-source lab tools in public repositories. The university mandates approved data handling, license attribution, and audit trails for AI assistance. Which governance practice adheres to organizational standards when using Copilot and agents?
Select an answer to reveal the explanation.
Short Explanation
You’re setting lab safety rules before experiments begin. Policy controls plus audit logs keep AI help inside university standards.
Full Explanation
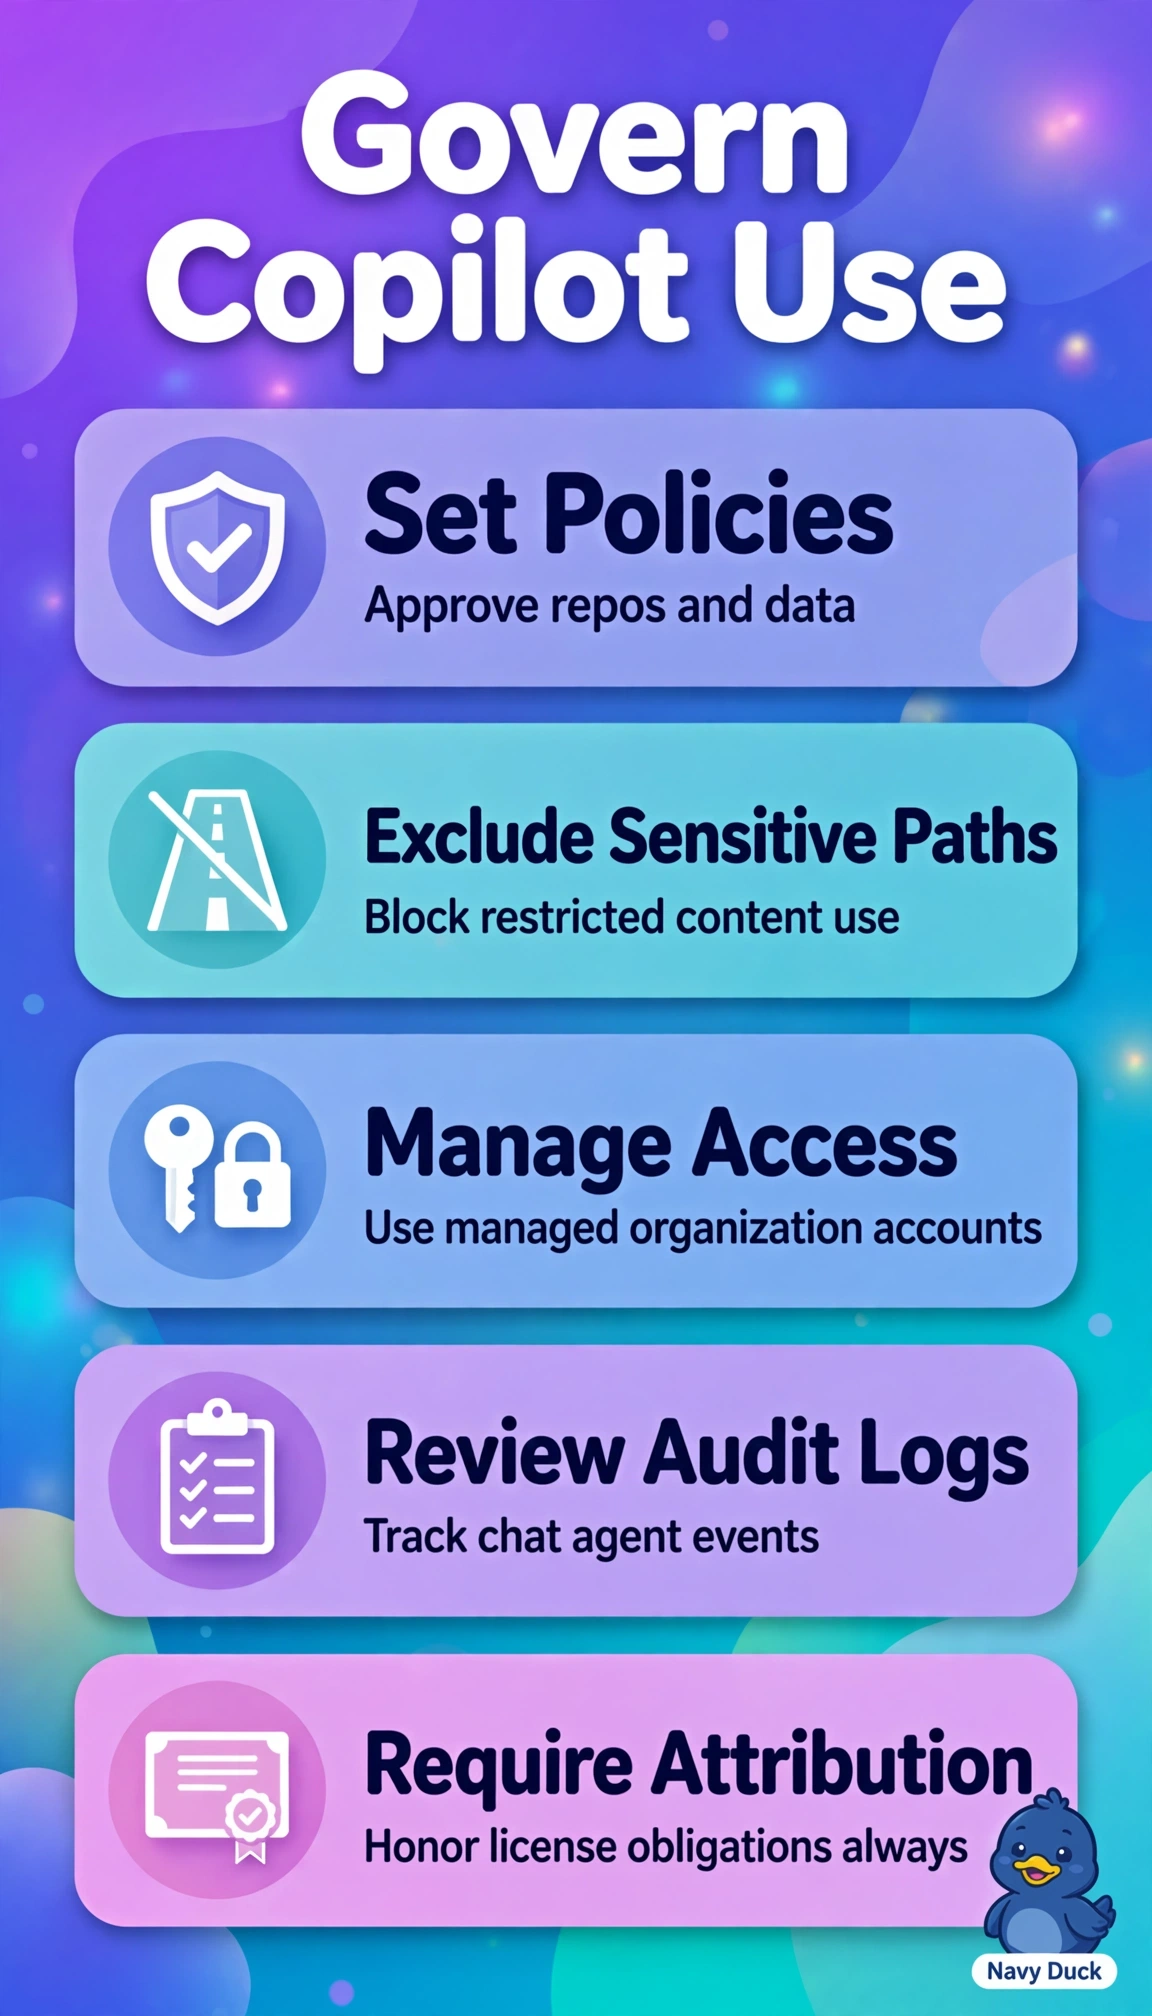
The correct practice is right because it combines all three mandated governance layers for university use of Copilot and coding agents in public repositories: Copilot content exclusion enforces approved data handling by preventing specified files or sensitive paths from informing suggestions, approved repository policies control where agents may operate and how open-source license attribution must be preserved in documentation, and audit log review for agent and chat activity provides the required detective trail linking AI assistance to human authors across 40 assistants. The enterprise accounts with audit approach fails on preventive data-boundary control because centralized identity and logging without content exclusion still allows proprietary or restricted content to enter the model context and leak into public suggestions. The exclusion with audit on approved repositories approach fails on intellectual-property compliance because it secures boundaries and traceability but omits systematic license attribution checks, which is critical when documenting open-source lab tools where unattributed reuse creates legal risk. The exclusion with handling guidance and training approach fails on verifiable accountability because guidance and training without centralized audit log review leaves no durable record of prompts, suggestions, and agent actions to satisfy university audit mandates. Exam caveat: do not select a choice that satisfies two pillars very well but drops the third, as governance questions require the complete set of data handling, attribution, and auditability. Practical check: verify in admin settings that exclusion rules cover sensitive paths, repository policy permits public AI-assisted contributions with attribution workflow, and audit logs capture both chat and agent events for periodic review.