
A product leader is enabling Copilot and agents across three departments that handle customer data, contracts, and billing code. Legal requires data boundaries, audit trails, and control over third-party use. Which evaluation should the leader perform first to confirm governance, privacy, usage, and risk controls for GitHub use?
Select an answer to reveal the explanation.
Short Explanation
You're checking locks before opening more doors. A governance-first audit protects customer data while you scale AI help. It's like reviewing the building's security plan before adding new entrances.
Full Explanation
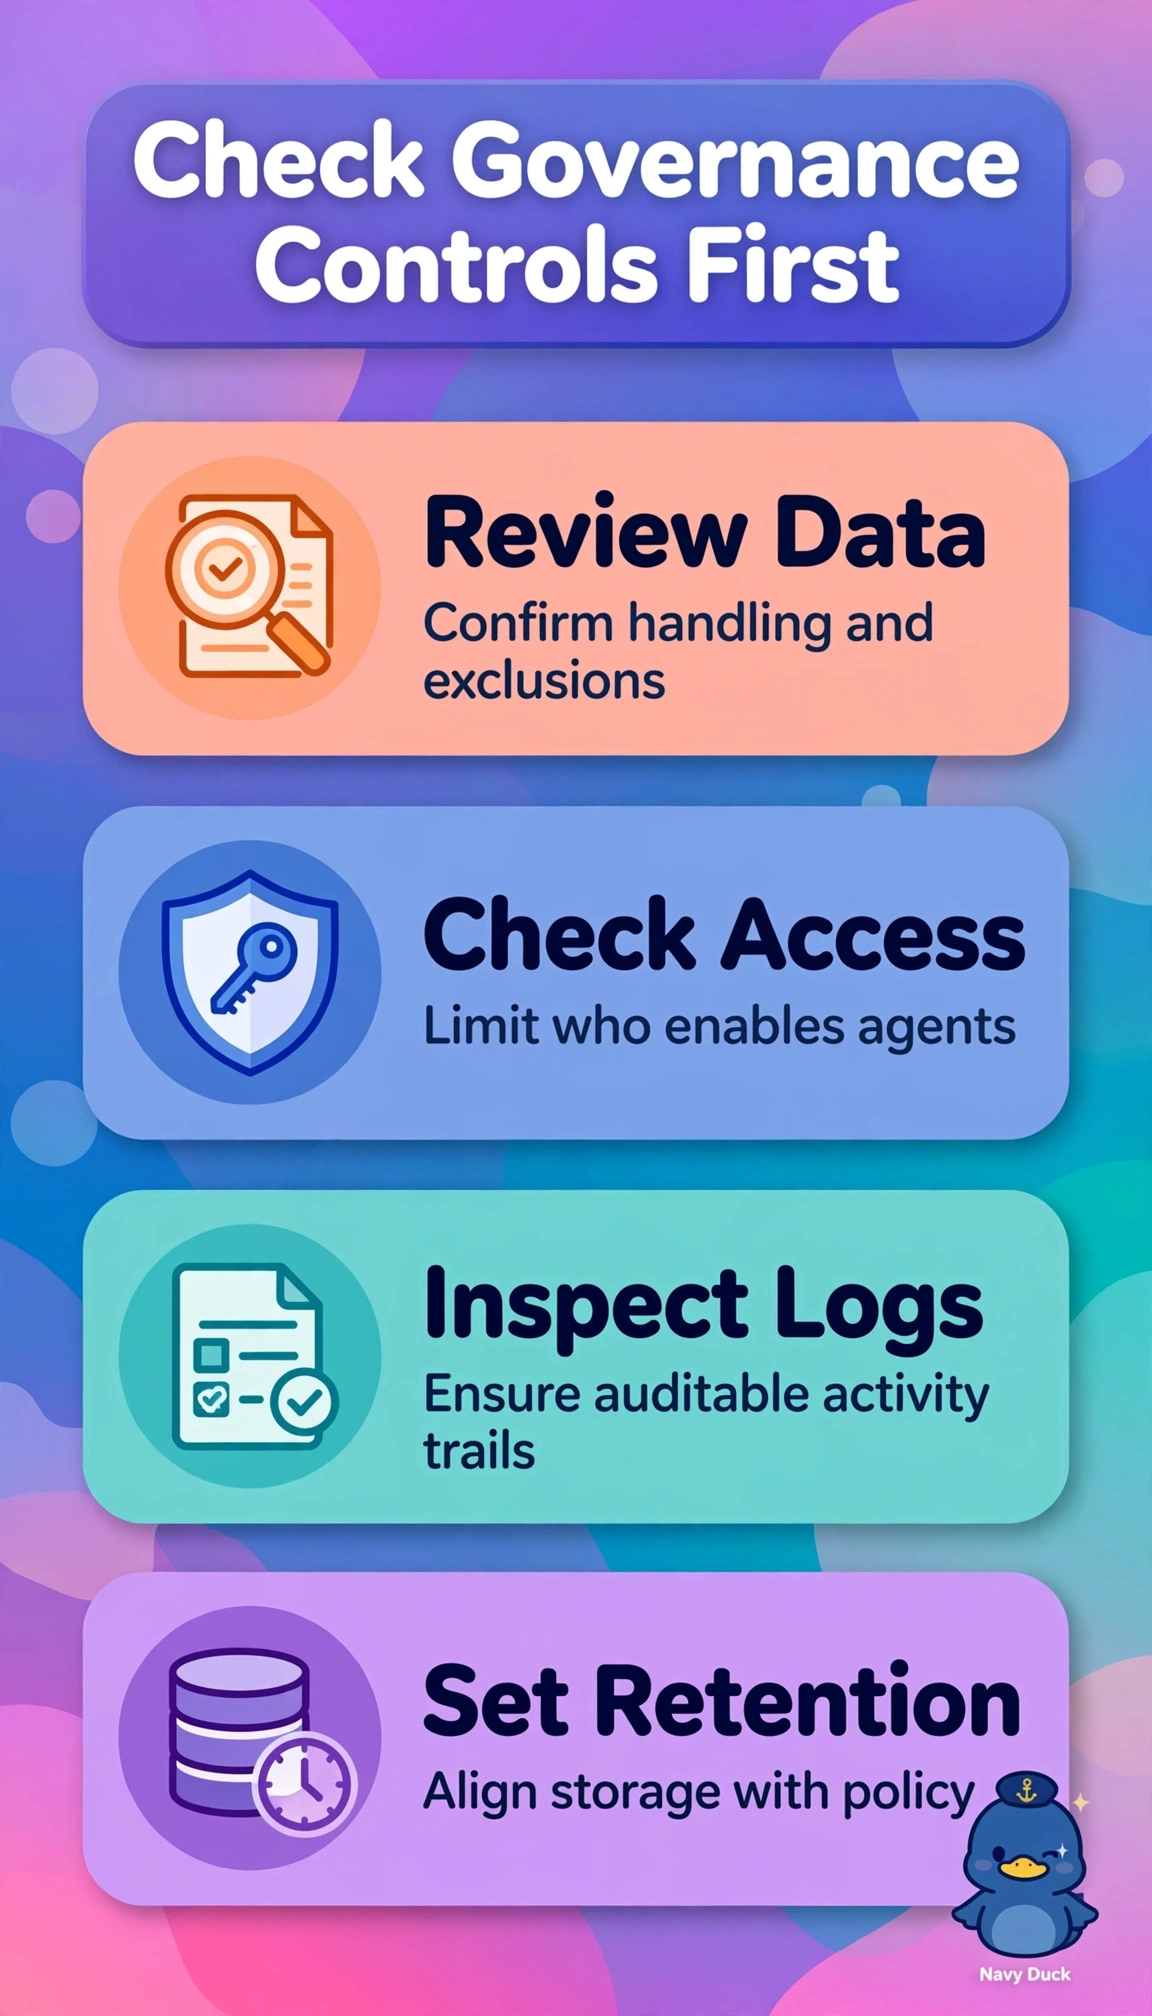
The correct evaluation comes first because Copilot and agents over customer data, contracts, and billing code create AI data flows that repository controls alone do not govern, requiring joint confirmation of data handling and exclusions, departmental access policies, audit logging of AI actions, and enterprise retention to satisfy boundaries, traceability, third-party control, privacy, and usage oversight for Legal. Auditing SSO, repository permissions, and IP allow lists strengthens departmental boundaries and is sound identity governance, but it fails because it secures access to GitHub without verifying what Copilot retains, logs, or shares, leaving AI-specific risk unaddressed. Reviewing audit logs and content exclusion for sensitive data supports traceability and privacy, but it fails because detection without preventive access policy review, retention validation, and third-party flow control cannot establish a complete compliance baseline. Assessing third-party agent integrations and sharing settings with Legal addresses vendor risk and external-use control, but it fails because outward sharing review without internal access, logging, and retention leaves core governance gaps. An exam caveat is to avoid choosing a familiar partial security task that uses governance terms and instead select the comprehensive first check spanning lifecycle, access, auditability, and retention. A practical check is to open enterprise Copilot policies, audit-log streaming, exclusion and retention settings, and data-handling documentation and confirm Legal sign-off before wider rollout.