
A product team wants Copilot to check live inventory in Postgres, file Jira bugs, and read Confluence specs during planning, without hardcoding credentials in prompts and with IT able to revoke access centrally. When should the team recommend using Model Context Protocol servers to support this scenario?
Select an answer to reveal the explanation.
Short Explanation
You're adding safe plugs, not rewiring the house, and standardized access keeps IT happy. Like using one universal adapter, MCP connects tools with permissions intact.
Full Explanation
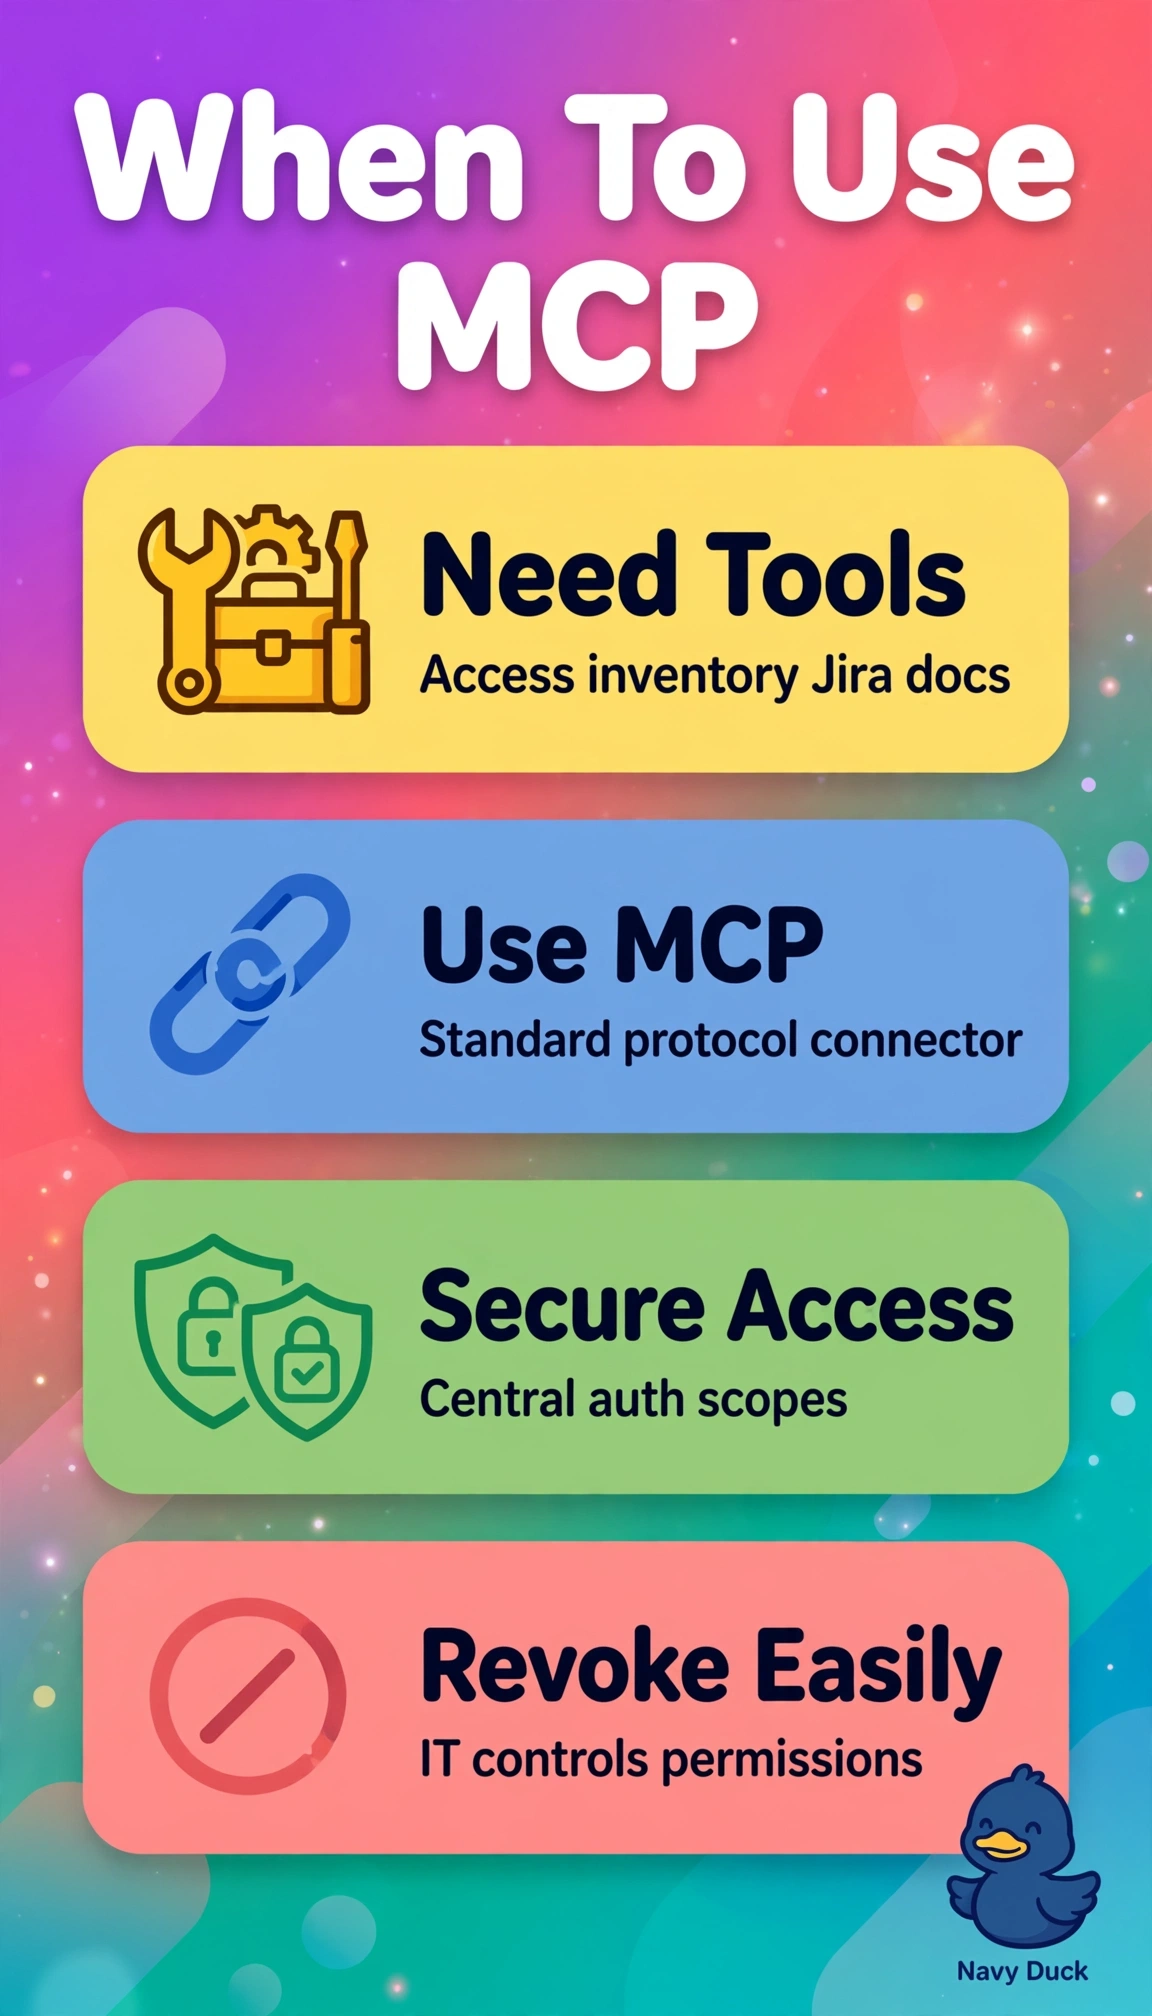
The scenario requires live operational access with mixed read and write actions under enterprise governance, which is exactly what standardized Model Context Protocol servers provide when configured with centrally managed, revocable permissions and no credentials in prompts. Copilot must read current inventory from Postgres, create issues in Jira, and read specifications from Confluence during planning, so the correct pattern combines live connectivity, appropriate read and write scopes, and IT-controlled identity and authorization. The high-performance nightly snapshot variant is a sound analytics pattern for reporting and search, but it fails the freshness concept because inventory decisions require current stock rather than yesterday's copy even though governance and write scopes look correct. The live read-only summaries variant is a sound planning-assistant pattern for standups and reviews, but it fails the action concept because search and summarization scopes do not include Jira issue creation needed to file bugs. The team-managed local vault variant is a sound small-team integration pattern that avoids prompt-embedded secrets, but it fails the enterprise control concept because developer-rotated workstation storage does not give IT single-place disablement, audit, and least-privilege enforcement. Exam caveat: match liveness, effective permissions, and control plane together rather than selecting any plausible integration alone. Practical check: inspect each registered server for allowed tools and OAuth scopes and confirm that disabling the service principal in the identity provider immediately blocks test calls to Postgres, Jira, and Confluence.