
You are an operations lead at an 80-person payments company where analysts use GitHub Copilot to draft automations that touch transaction records. Company policy forbids secrets in prompts or code, and auditors require documented human validation of AI assistance. Suggestions sometimes include insecure patterns despite built-in filters. Which human-review practice best addresses GitHub Copilot security considerations?
Select an answer to reveal the explanation.
Short Explanation
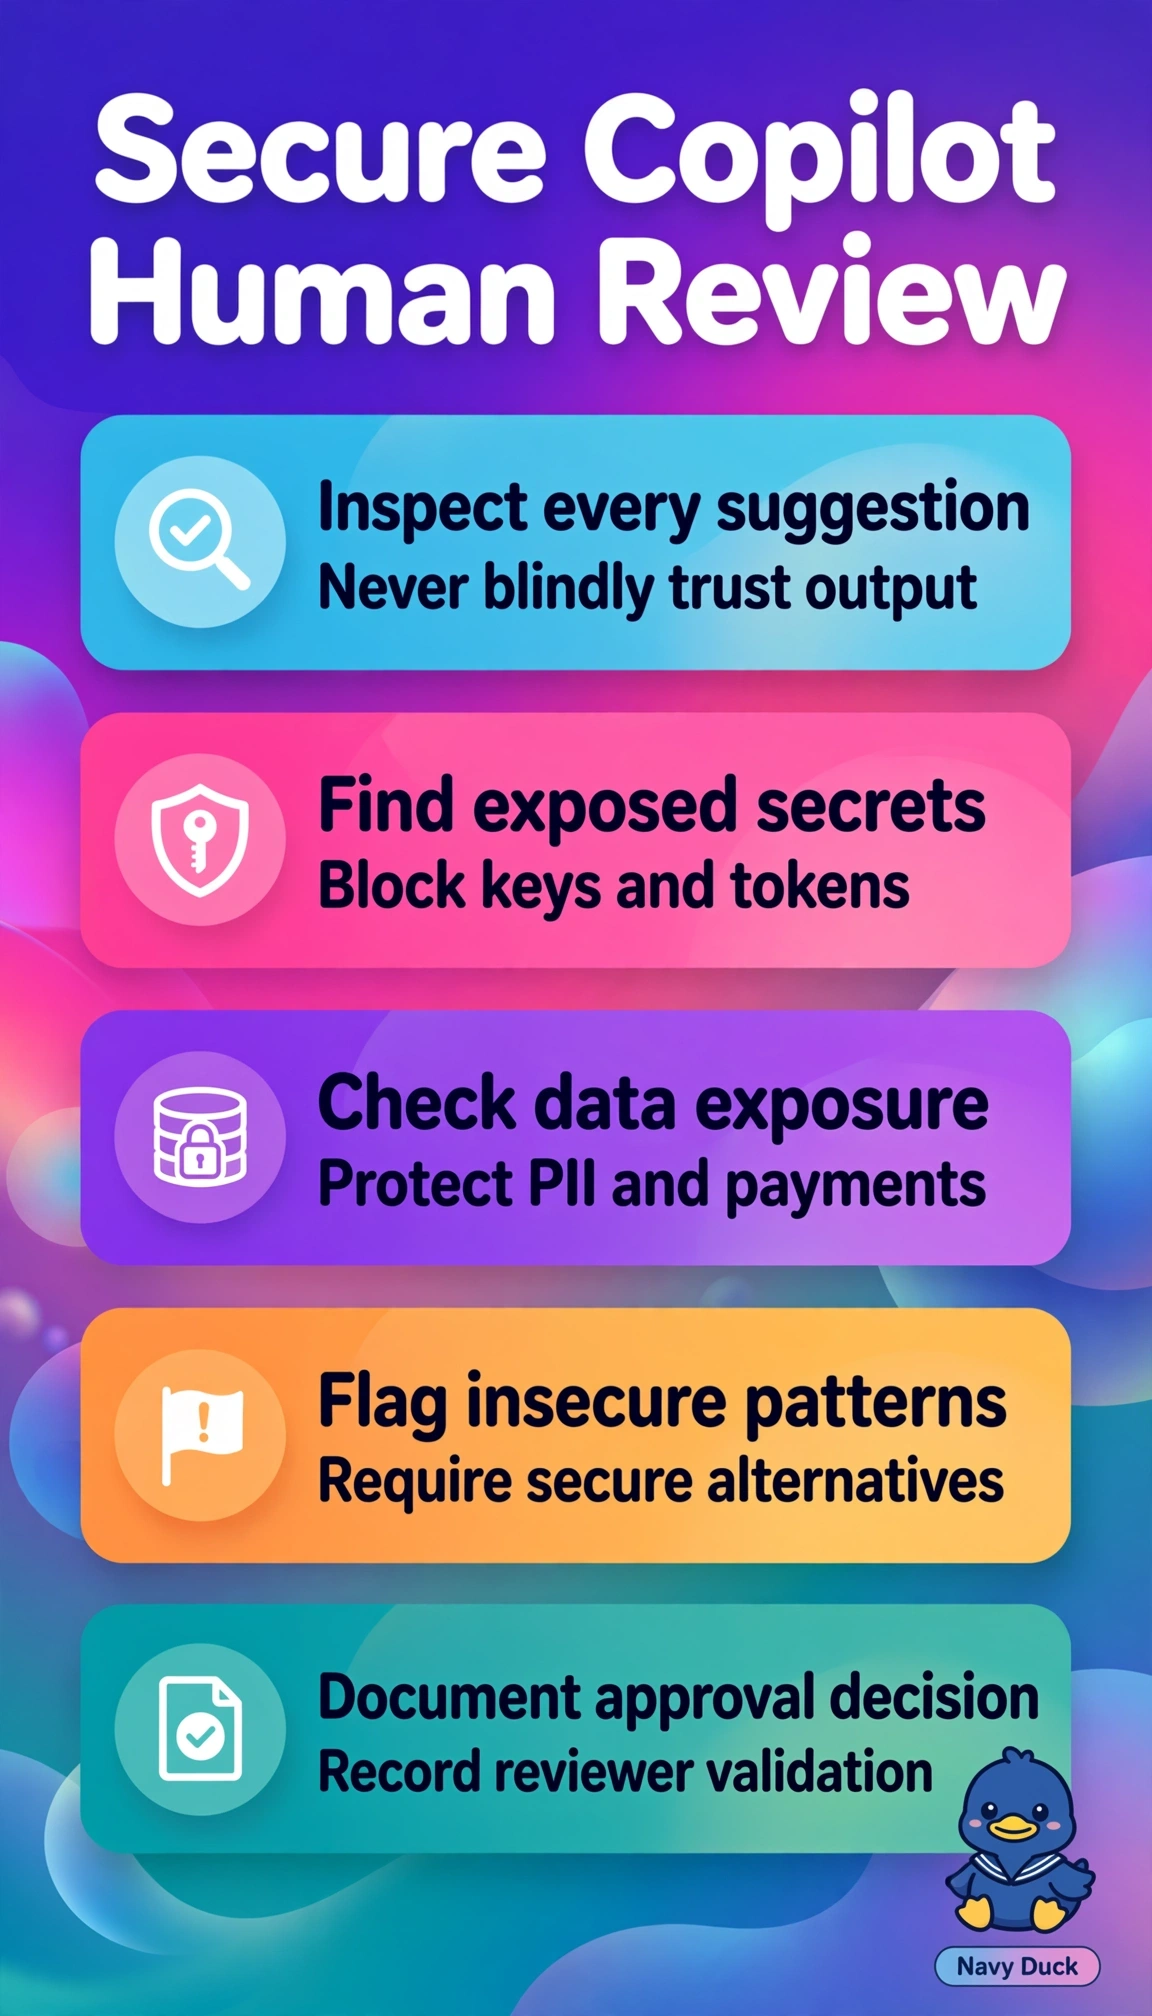
You're the final filter Copilot can't replace, so you've got to look for what slipped through. Always inspect suggestions for leaks and weak spots before they ship, since human validation is your audit trail and safety check.
Full Explanation
The correct practice succeeds because it directly enforces all three stated controls in a payments environment handling transaction records: explicit policy prohibition on secrets in prompts and code, auditor demand for documented human validation, and recognition that model safeguards are imperfect. A mandatory pre-merge review that specifically hunts for hardcoded secrets, exposed customer or transaction data, and insecure coding patterns closes the gap filters leave open while creating an auditable human checkpoint. The automation-only scanning approach fails by substitution concept, since secret scanners and static analysis are valuable detective controls but provide no documented human judgment about AI assistance that auditors explicitly require. The accuracy-focused validation approach fails by scope omission, since confirming transaction logic and recording approval satisfies audit traceability yet never inspects for leaked secrets or vulnerable patterns the stem warns still occur. The filter-reliant approval approach fails by misplaced trust, since it treats built-in content filters as sufficient despite the stated fact they sometimes allow insecure suggestions, reducing human review to functionality only. Exam caveat: when the stem emphasizes imperfect filters plus mandatory human validation, eliminate any choice relying solely on tooling or functionality sign-off even if it sounds mature. Practical check: require reviewers to use a short merge checklist covering no secrets, no unnecessary data exposure, and no known insecure pattern, then sign with date and Copilot usage noted.