
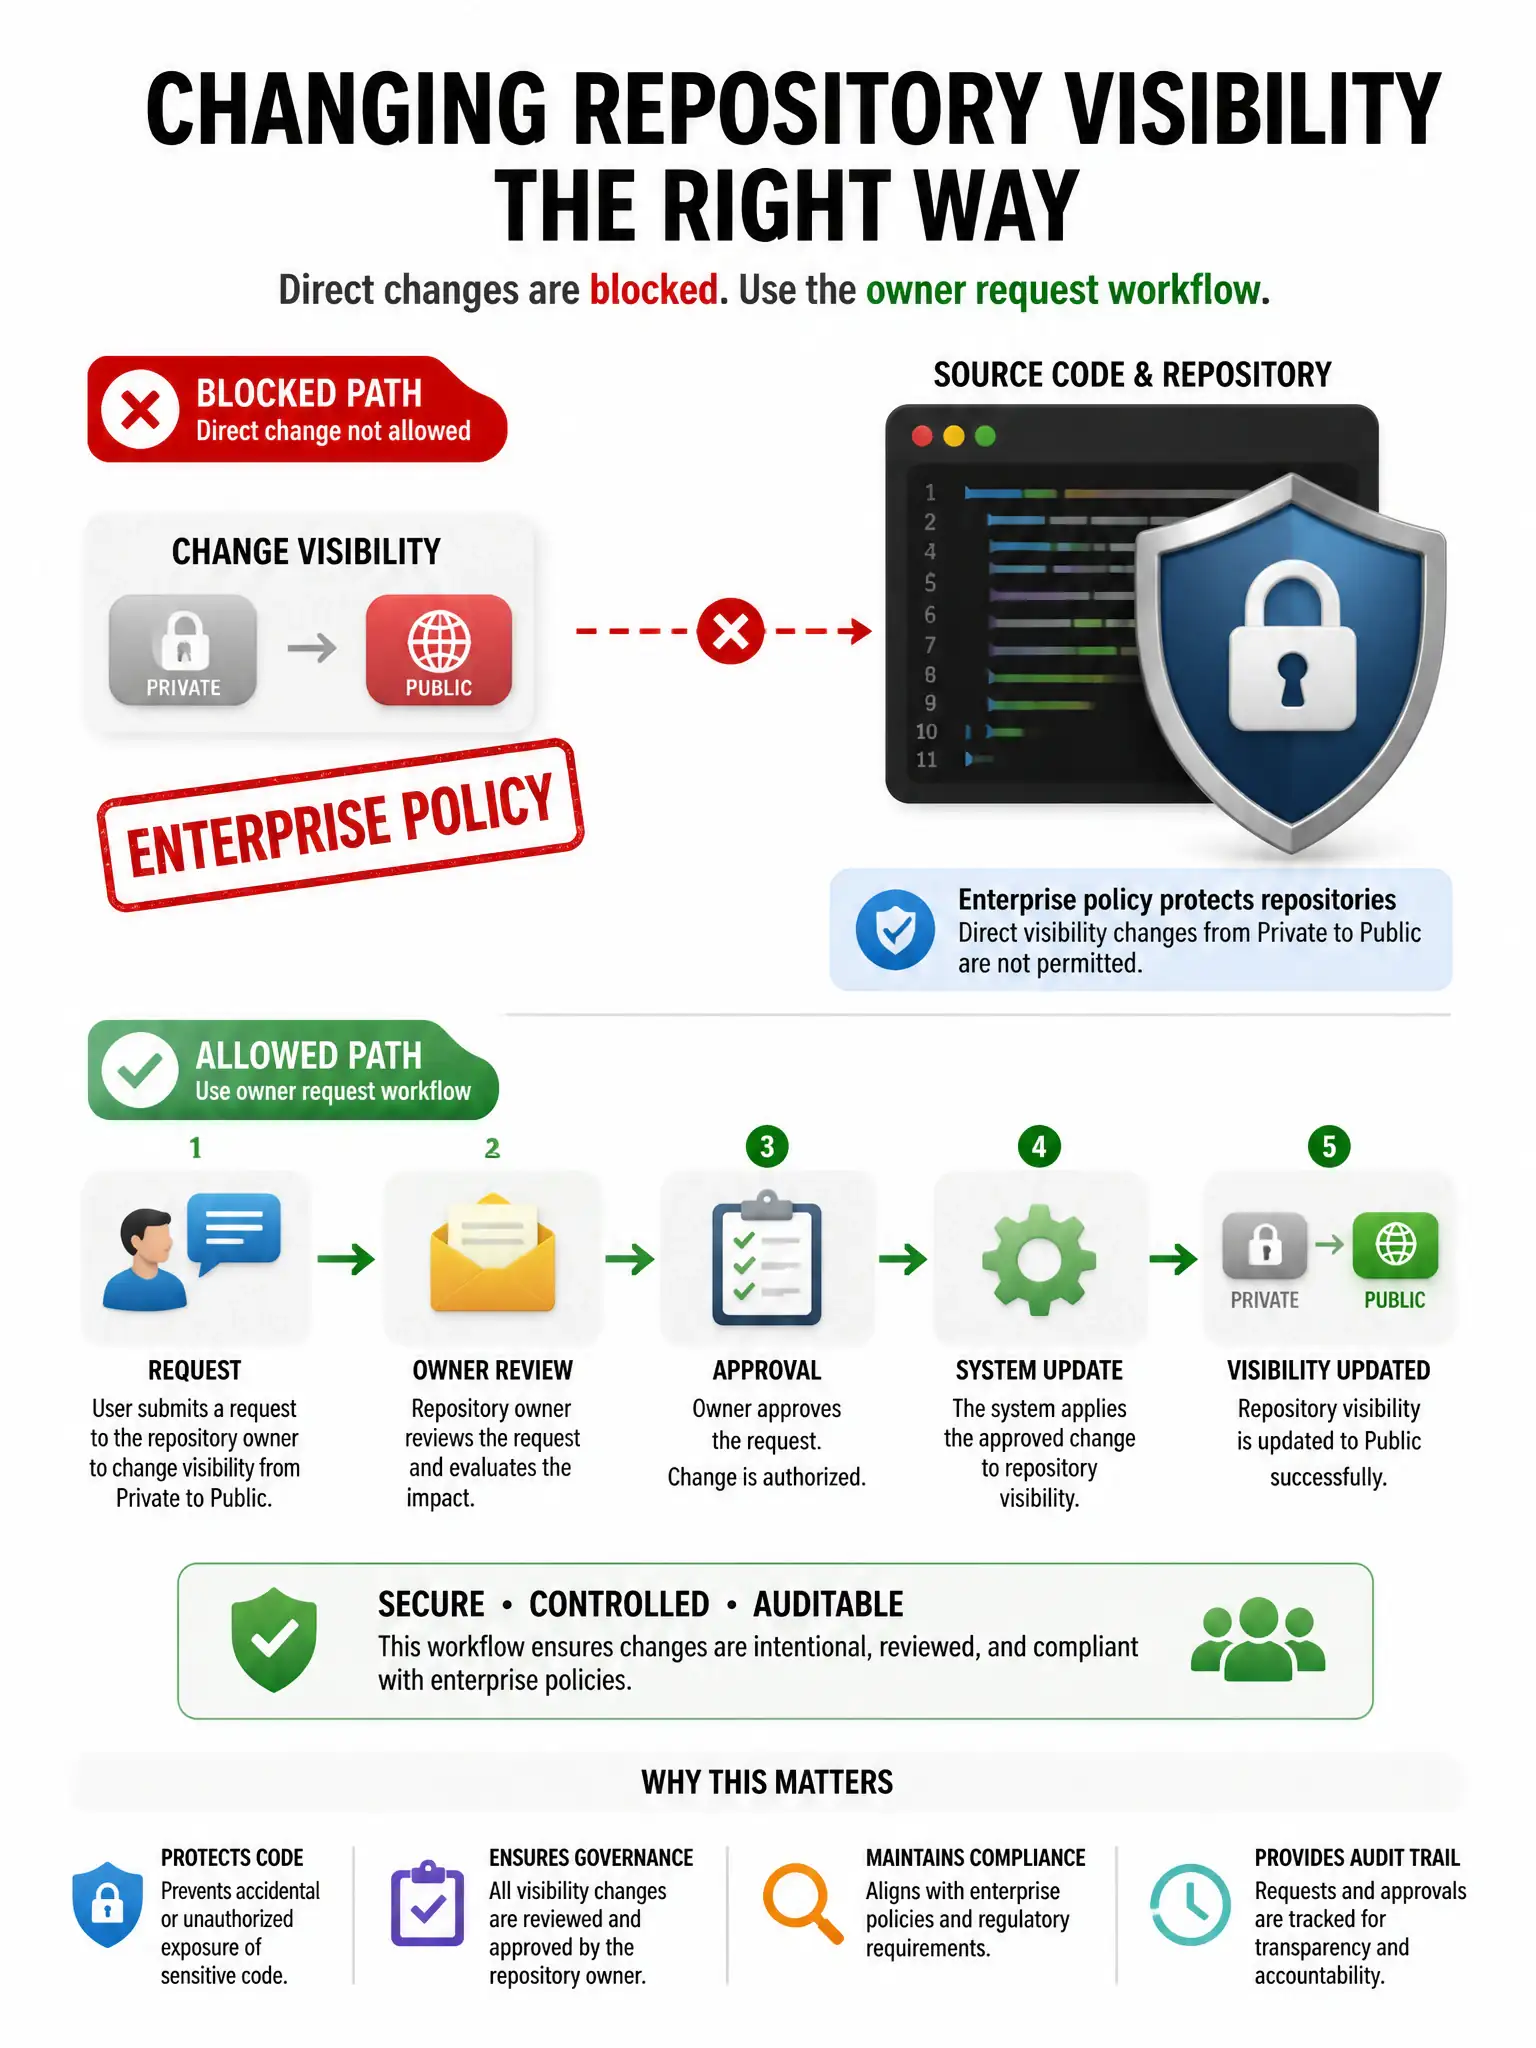
An enterprise policy prevents members from changing repository visibility. What risk does this primarily reduce?
Select an answer to reveal the explanation.
Short Explanation
The classic oops: someone flips a private repo to public and secrets or IP hit the open internet. When you lock visibility changes, you stop that class of accidents. It isn't about SSH cloning or rewriting author fields.
Full Explanation
Restricting repository visibility changes primarily reduces the risk of accidental public exposure of private repositories. Visibility change restrictions keep private/internal code from becoming public without authorized owners, which is a common source of intellectual-property and secret leaks. The inability to clone repositories over SSH is unrelated to visibility policy. Loss of Git commit authorship metadata is unrelated to authorship metadata. Automatic deletion of Actions artifacts every minute is unrelated to Actions artifact retention. Combine with secret scanning, push protection, and external collaborator controls for layered data-leak prevention across the enterprise.