
What is a responsible use of a ruleset bypass list in an organization?
Select an answer to reveal the explanation.
Short Explanation
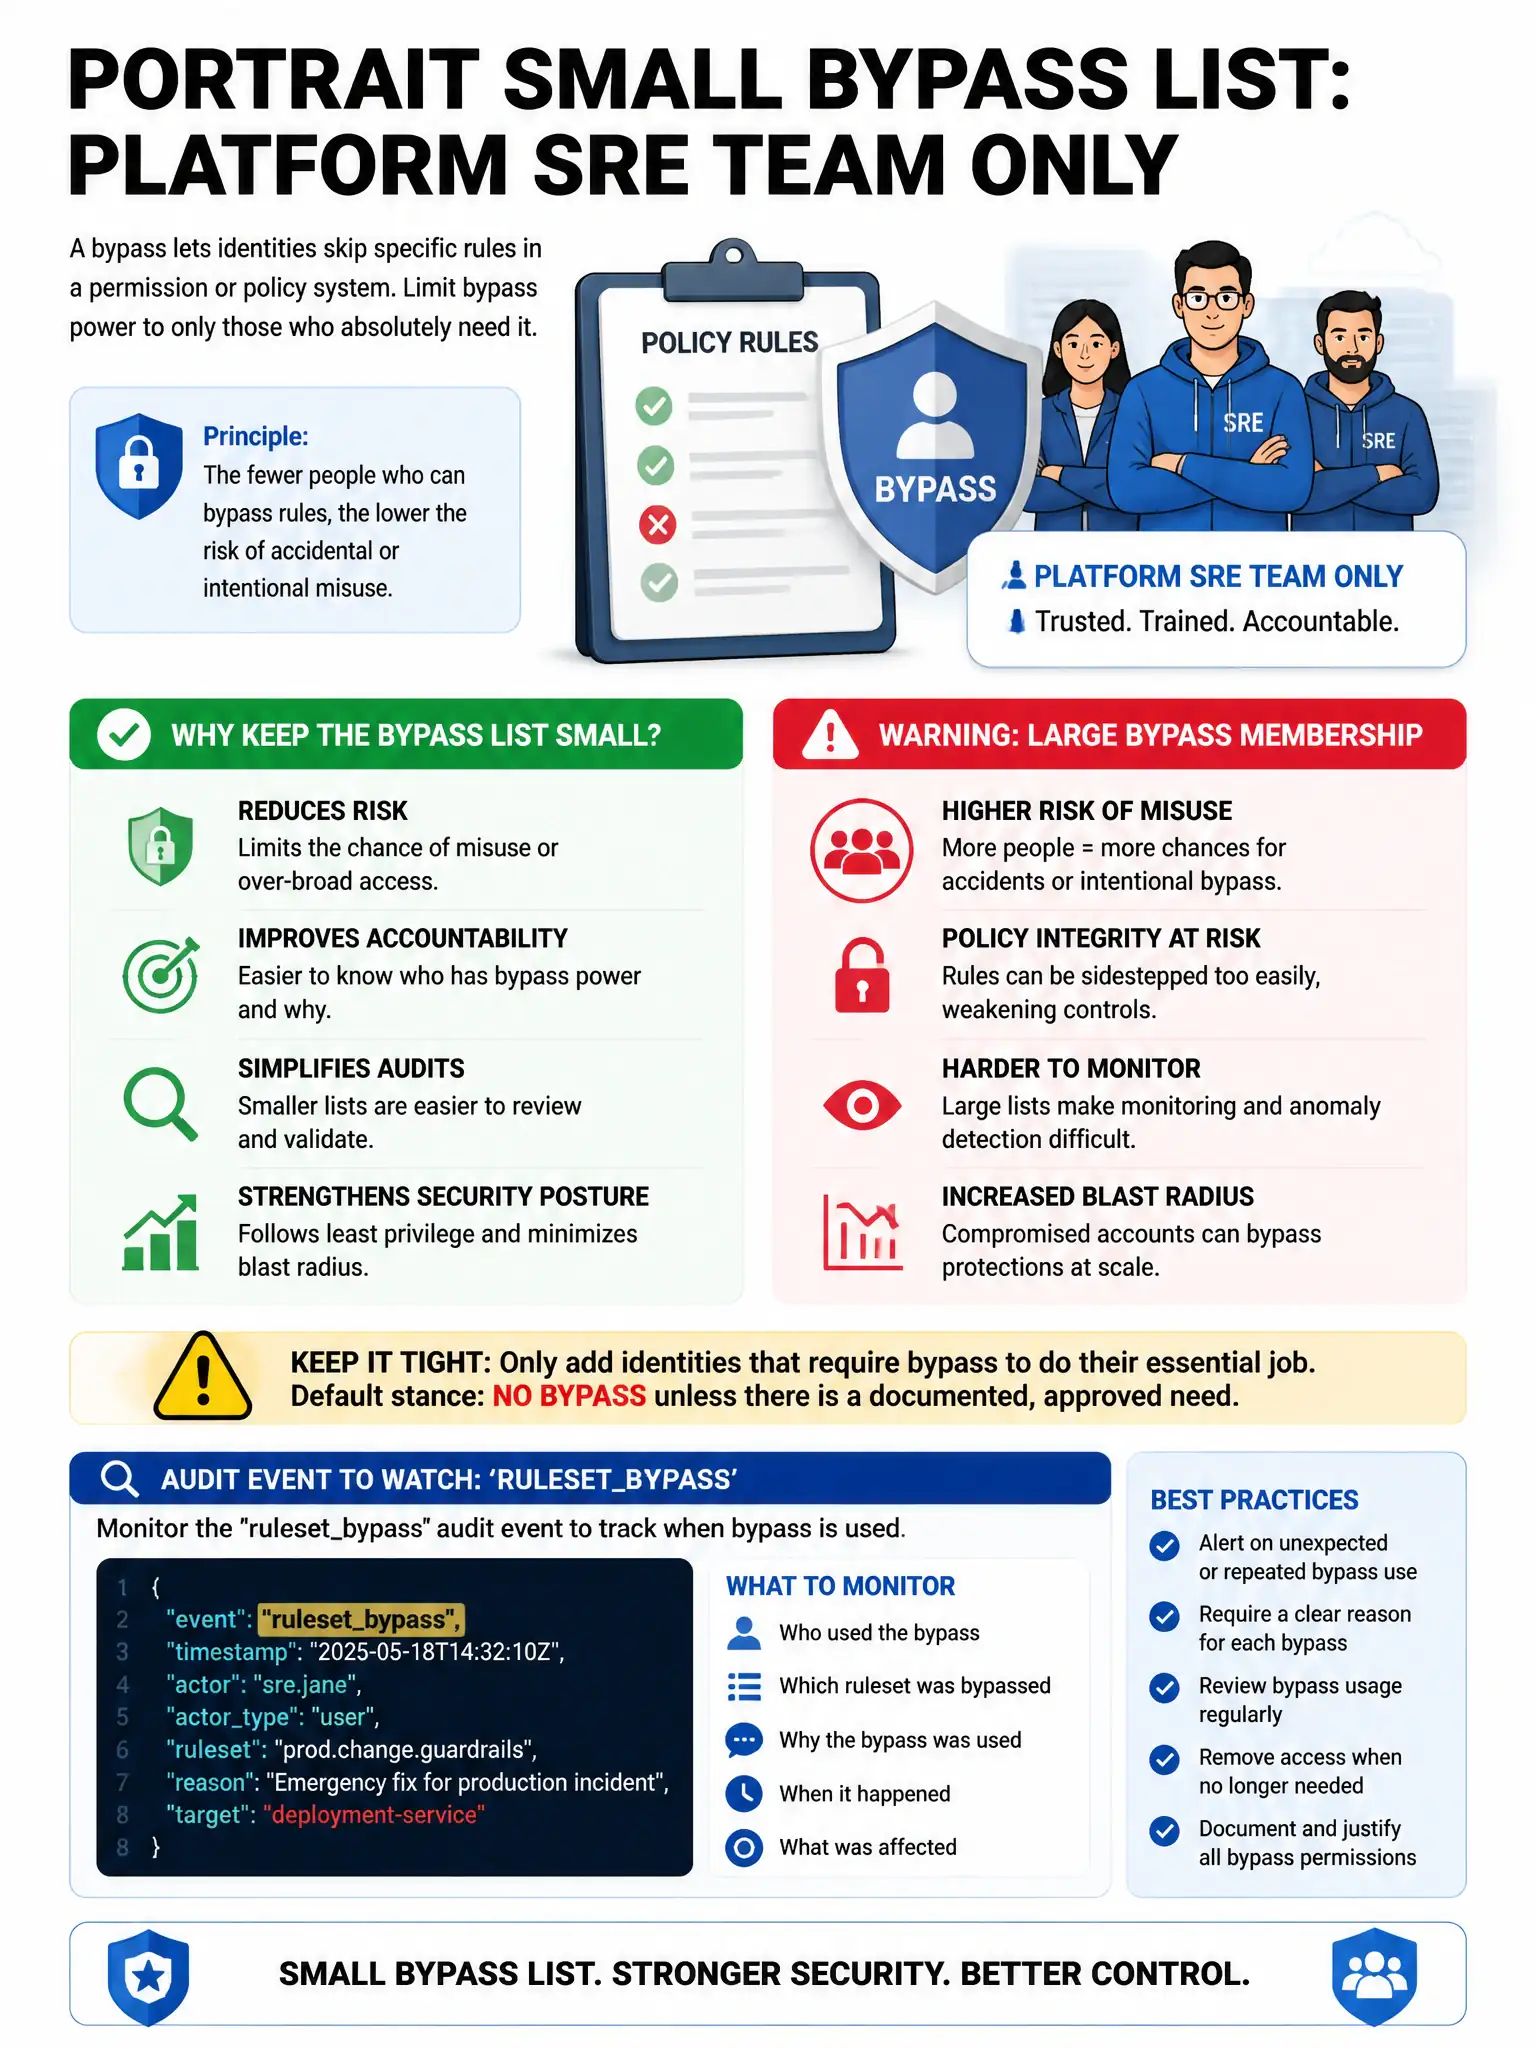
The bypass list is break-glass, not a lounge for ignoring security. Keep it tiny—incident commanders or platform owners—log usage, and review membership quarterly. If half the company is on it, you don’t have a ruleset; you have theater.
Full Explanation
The correct answer is allowing a tightly controlled set of roles or teams to bypass rules during approved emergency procedures. Ruleset bypass actors can merge or push when policy would otherwise block, which is sometimes necessary for production incidents. Granting every outside collaborator permanent silent bypass of all security rules is excessive risk because broad silent bypass defeats the control. Disabling secret scanning for the entire enterprise automatically and publishing private packages to the public registry without review are unrelated misuses of bypass lists. Require dual control where possible, alert on bypass events in audit logs, time-box elevated access, and review membership quarterly so the list does not grow into a permanent exception for half the company.