
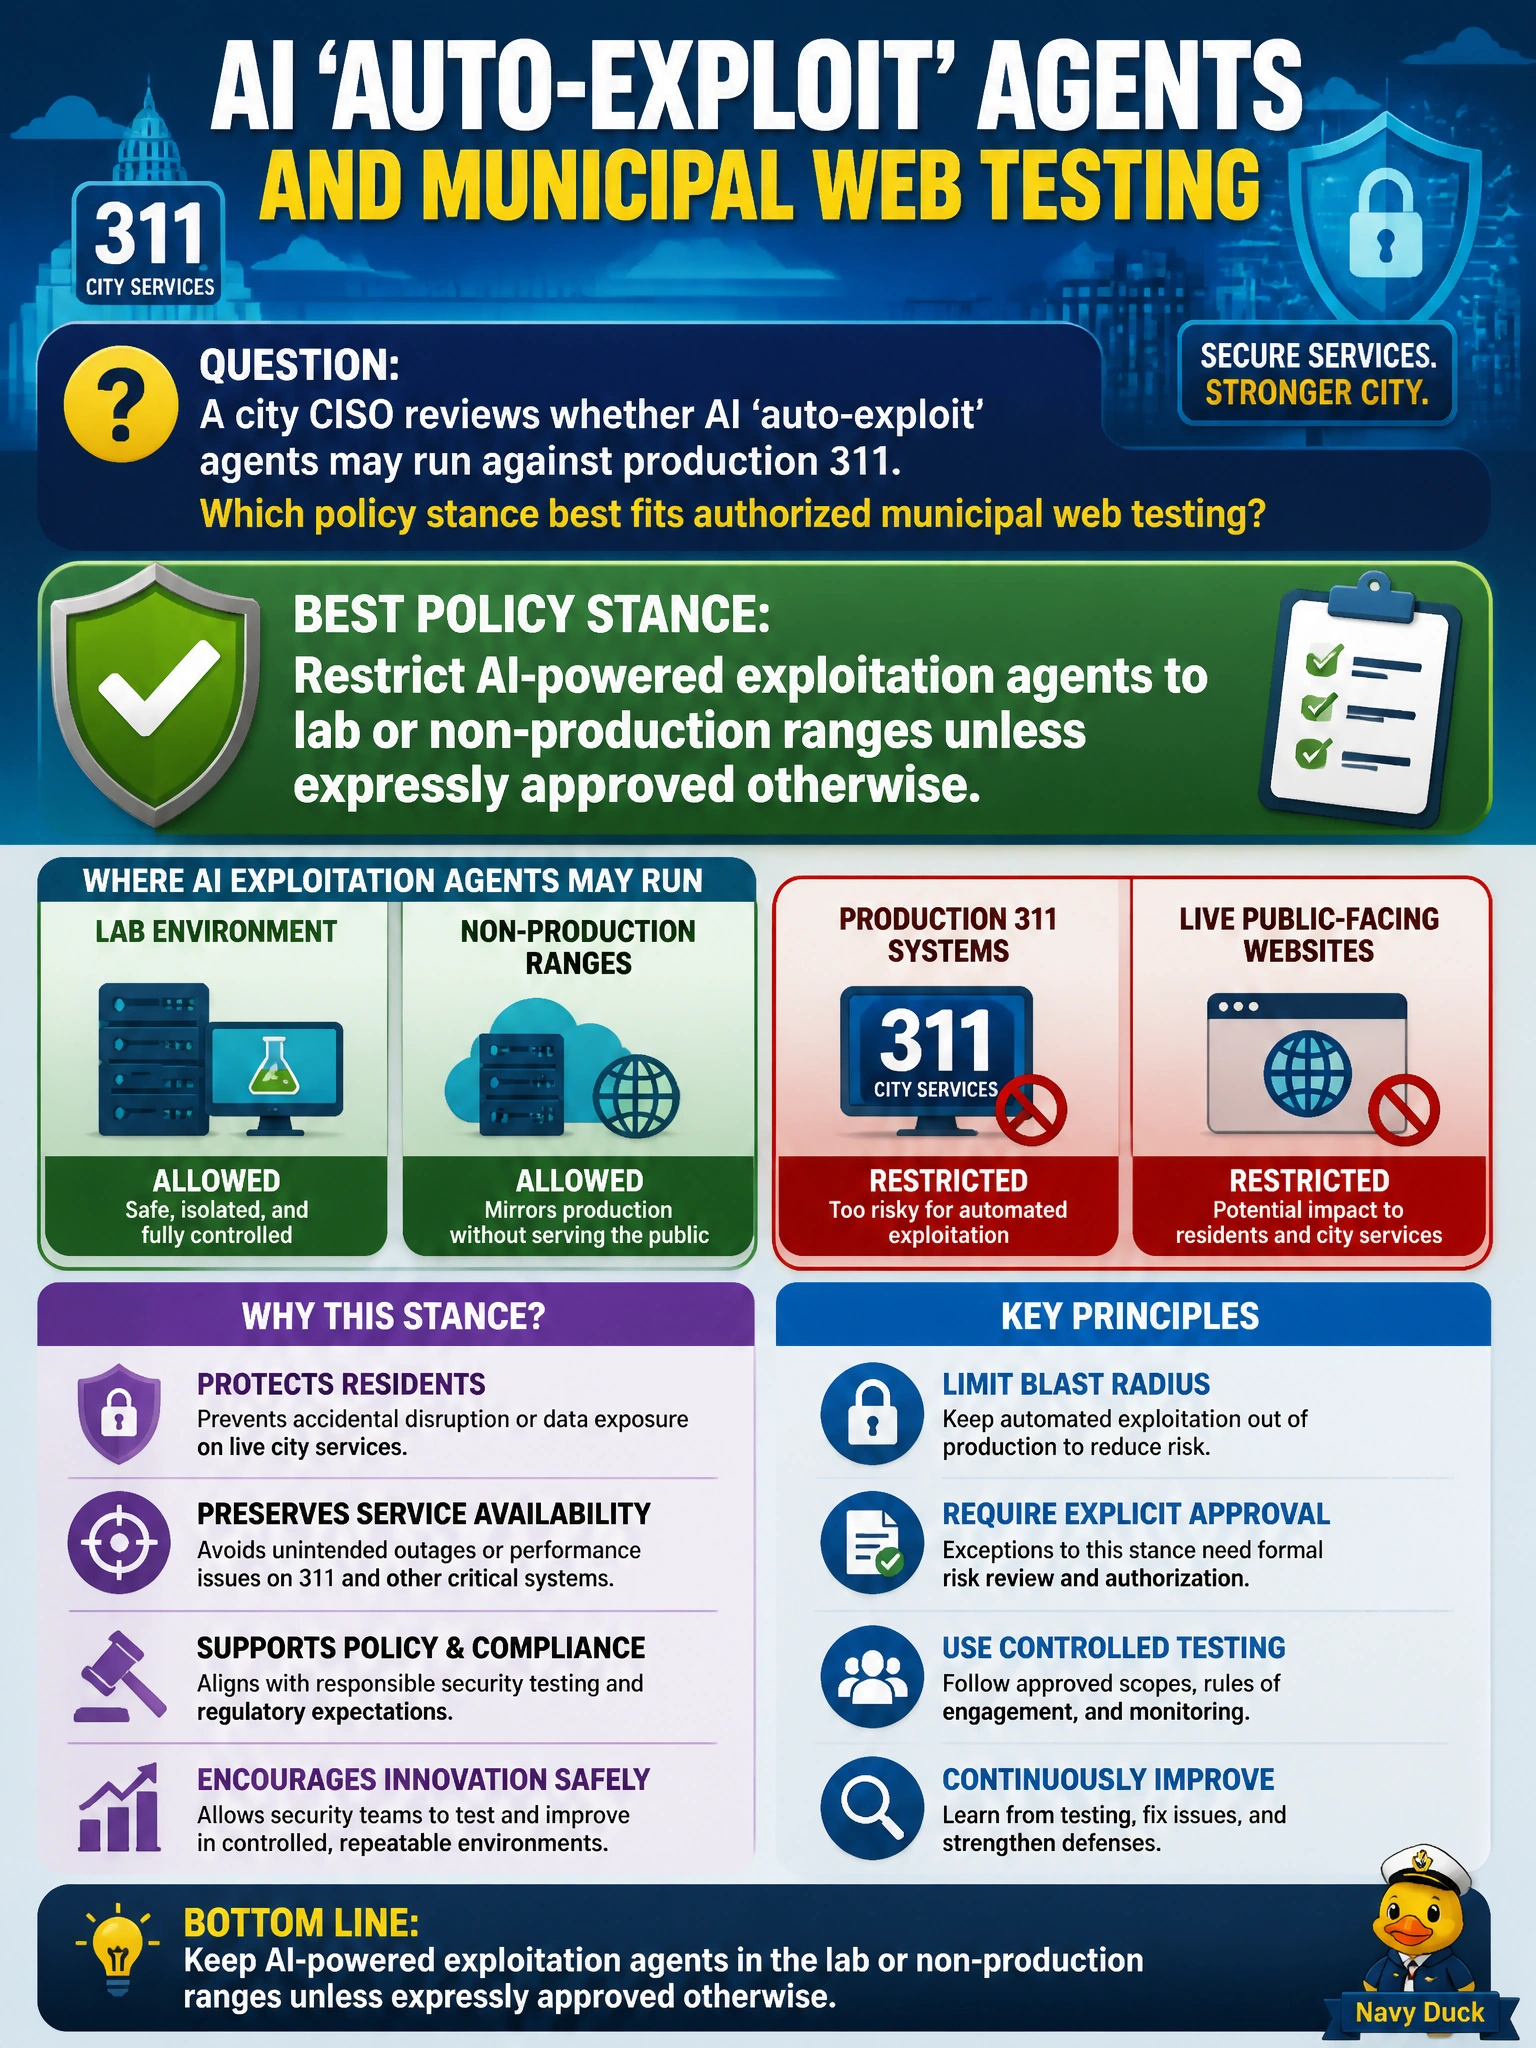
A city CISO reviews whether AI 'auto-exploit' agents may run against production 311. Which policy stance best fits authorized municipal web testing?
Select an answer to reveal the explanation.
Short Explanation
Auto-exploit bots belong in the lab sandbox, not freelancing on live 311 at 2 a.m. High ticket volume is not a permission slip. Keep production behind express approval and change control.
Full Explanation
AI 'auto-exploit' agents amplify speed and blast radius. For authorized municipal web testing of production 311, the sound policy restricts such agents to lab or non-production ranges unless expressly approved otherwise. That stance preserves change control, limits citizen-facing outage risk, and keeps humans accountable for what runs against live city services. Ticket volume pressure is not a substitute for express approval, and 311's public visibility makes uncontrolled exploitation especially costly.
Allowing auto-exploit agents on production whenever ticket volume is high prioritizes backlog optics over safety and can create cascading citizen-service failures. Requiring auto-exploit agents to replace human ROE entirely removes the authorizing framework testers must follow and invites scope creep. Mandating overnight auto-exploit on every public form without change control is an availability and integrity hazard on a citizen service portal.
Exam caveat: production vs lab policy items reward restricting auto-exploit agents to non-production unless expressly approved. Operational check: default auto-exploit to lab/staging ranges, require named approval and change tickets for any production exception, define kill criteria, and monitor for unintended impact if an exception is granted.