
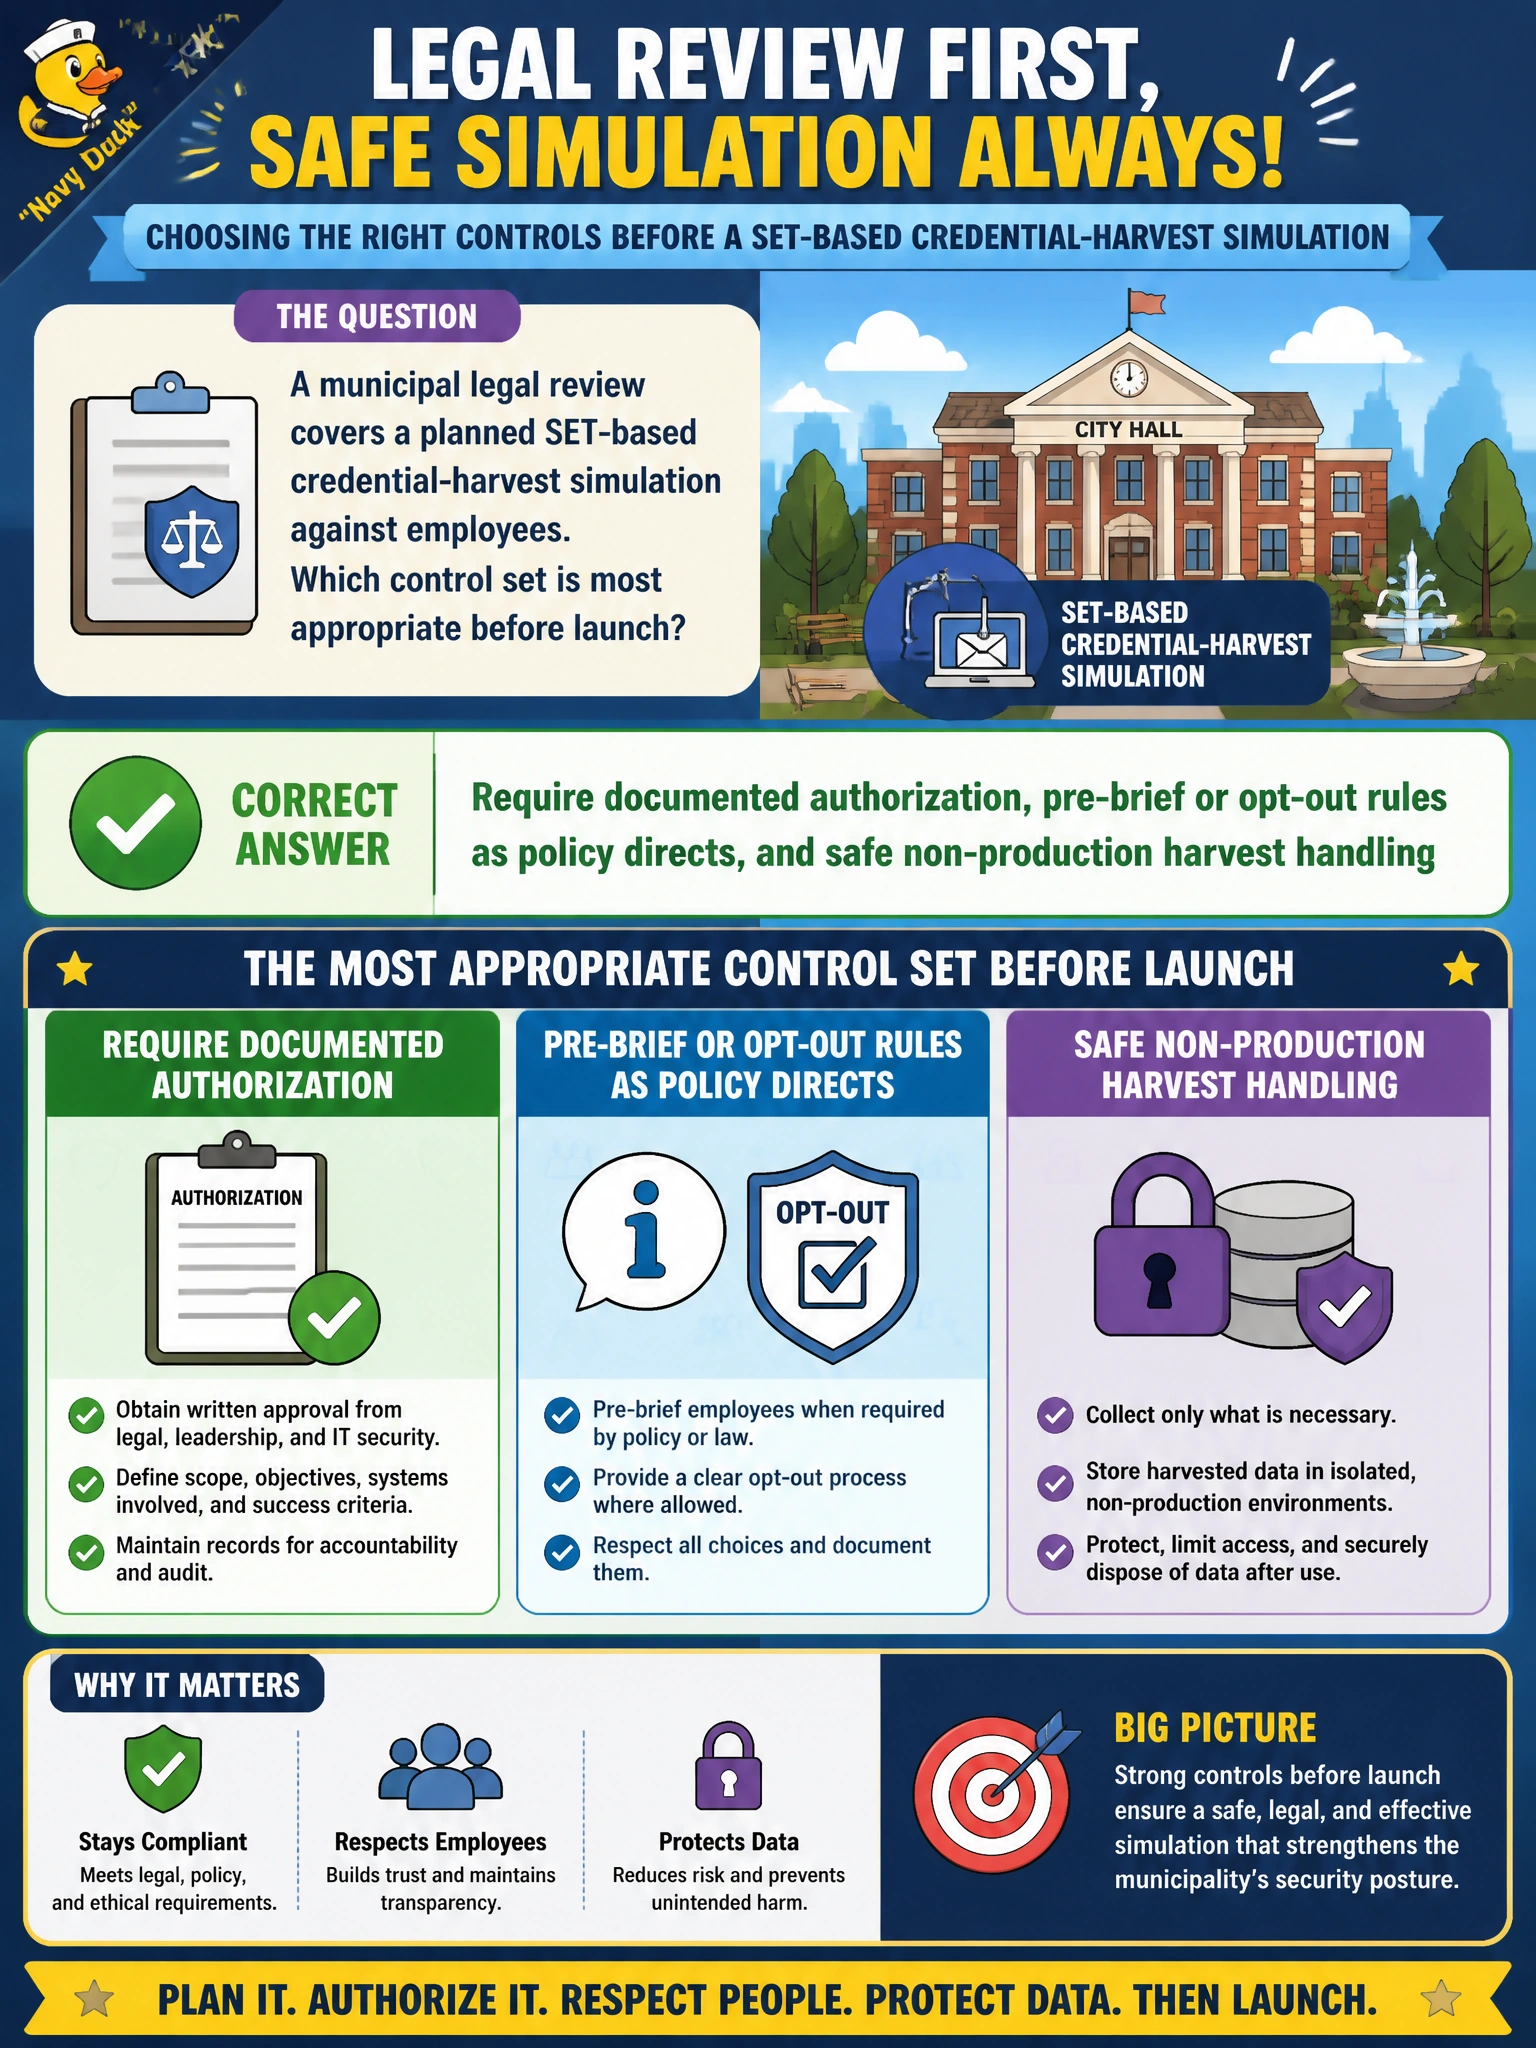
A municipal legal review covers a planned SET-based credential-harvest simulation against employees. Which control set is most appropriate before launch?
Select an answer to reveal the explanation.
Short Explanation
Credential-harvest drills with SET are not a surprise gotcha against live city logins. Get the paper authorization, follow pre-brief or opt-out rules, and keep harvest pages from eating real production passwords. Legal is part of the kit, not an afterthought.
Full Explanation
Before a municipal legal review clears a planned SET-based credential-harvest simulation against employees, the appropriate control set is documented authorization, pre-brief or opt-out rules as policy directs, and safe non-production harvest handling. Credential-harvest modules can closely resemble real attacks; without clear authorization and privacy-safe landing design, the exercise can collect live secrets, panic staff, or collide with production identity systems. Skipping pre-briefing solely so reactions remain completely natural may violate city policy where notice or opt-out is required and can create labor and legal risk disproportionate to training value. Collecting real production passwords on the harvest page to measure true risk severity turns the drill into an actual credential compromise event and expands blast radius if those passwords are reused. Running SET against production identity systems without opt-out because staff signed a handbook stretches handbook language into blanket consent for live identity attacks and is not a substitute for exercise-specific authorization. Exam caveat: GOAA civic SET scenarios test legal and safety gating around credential harvest—not how to maximize password capture. Operational check: obtain written authorization, implement pre-brief/opt-out as policy requires, point harvest pages at safe markers or fake captures, and keep SET off production IdP validation paths.