
An organization wants to implement a vulnerability management program with risk-based prioritization. Beyond the CVSS base score, which additional factor most significantly changes the effective risk of a vulnerability?
Select an answer to reveal the explanation.
Short Explanation
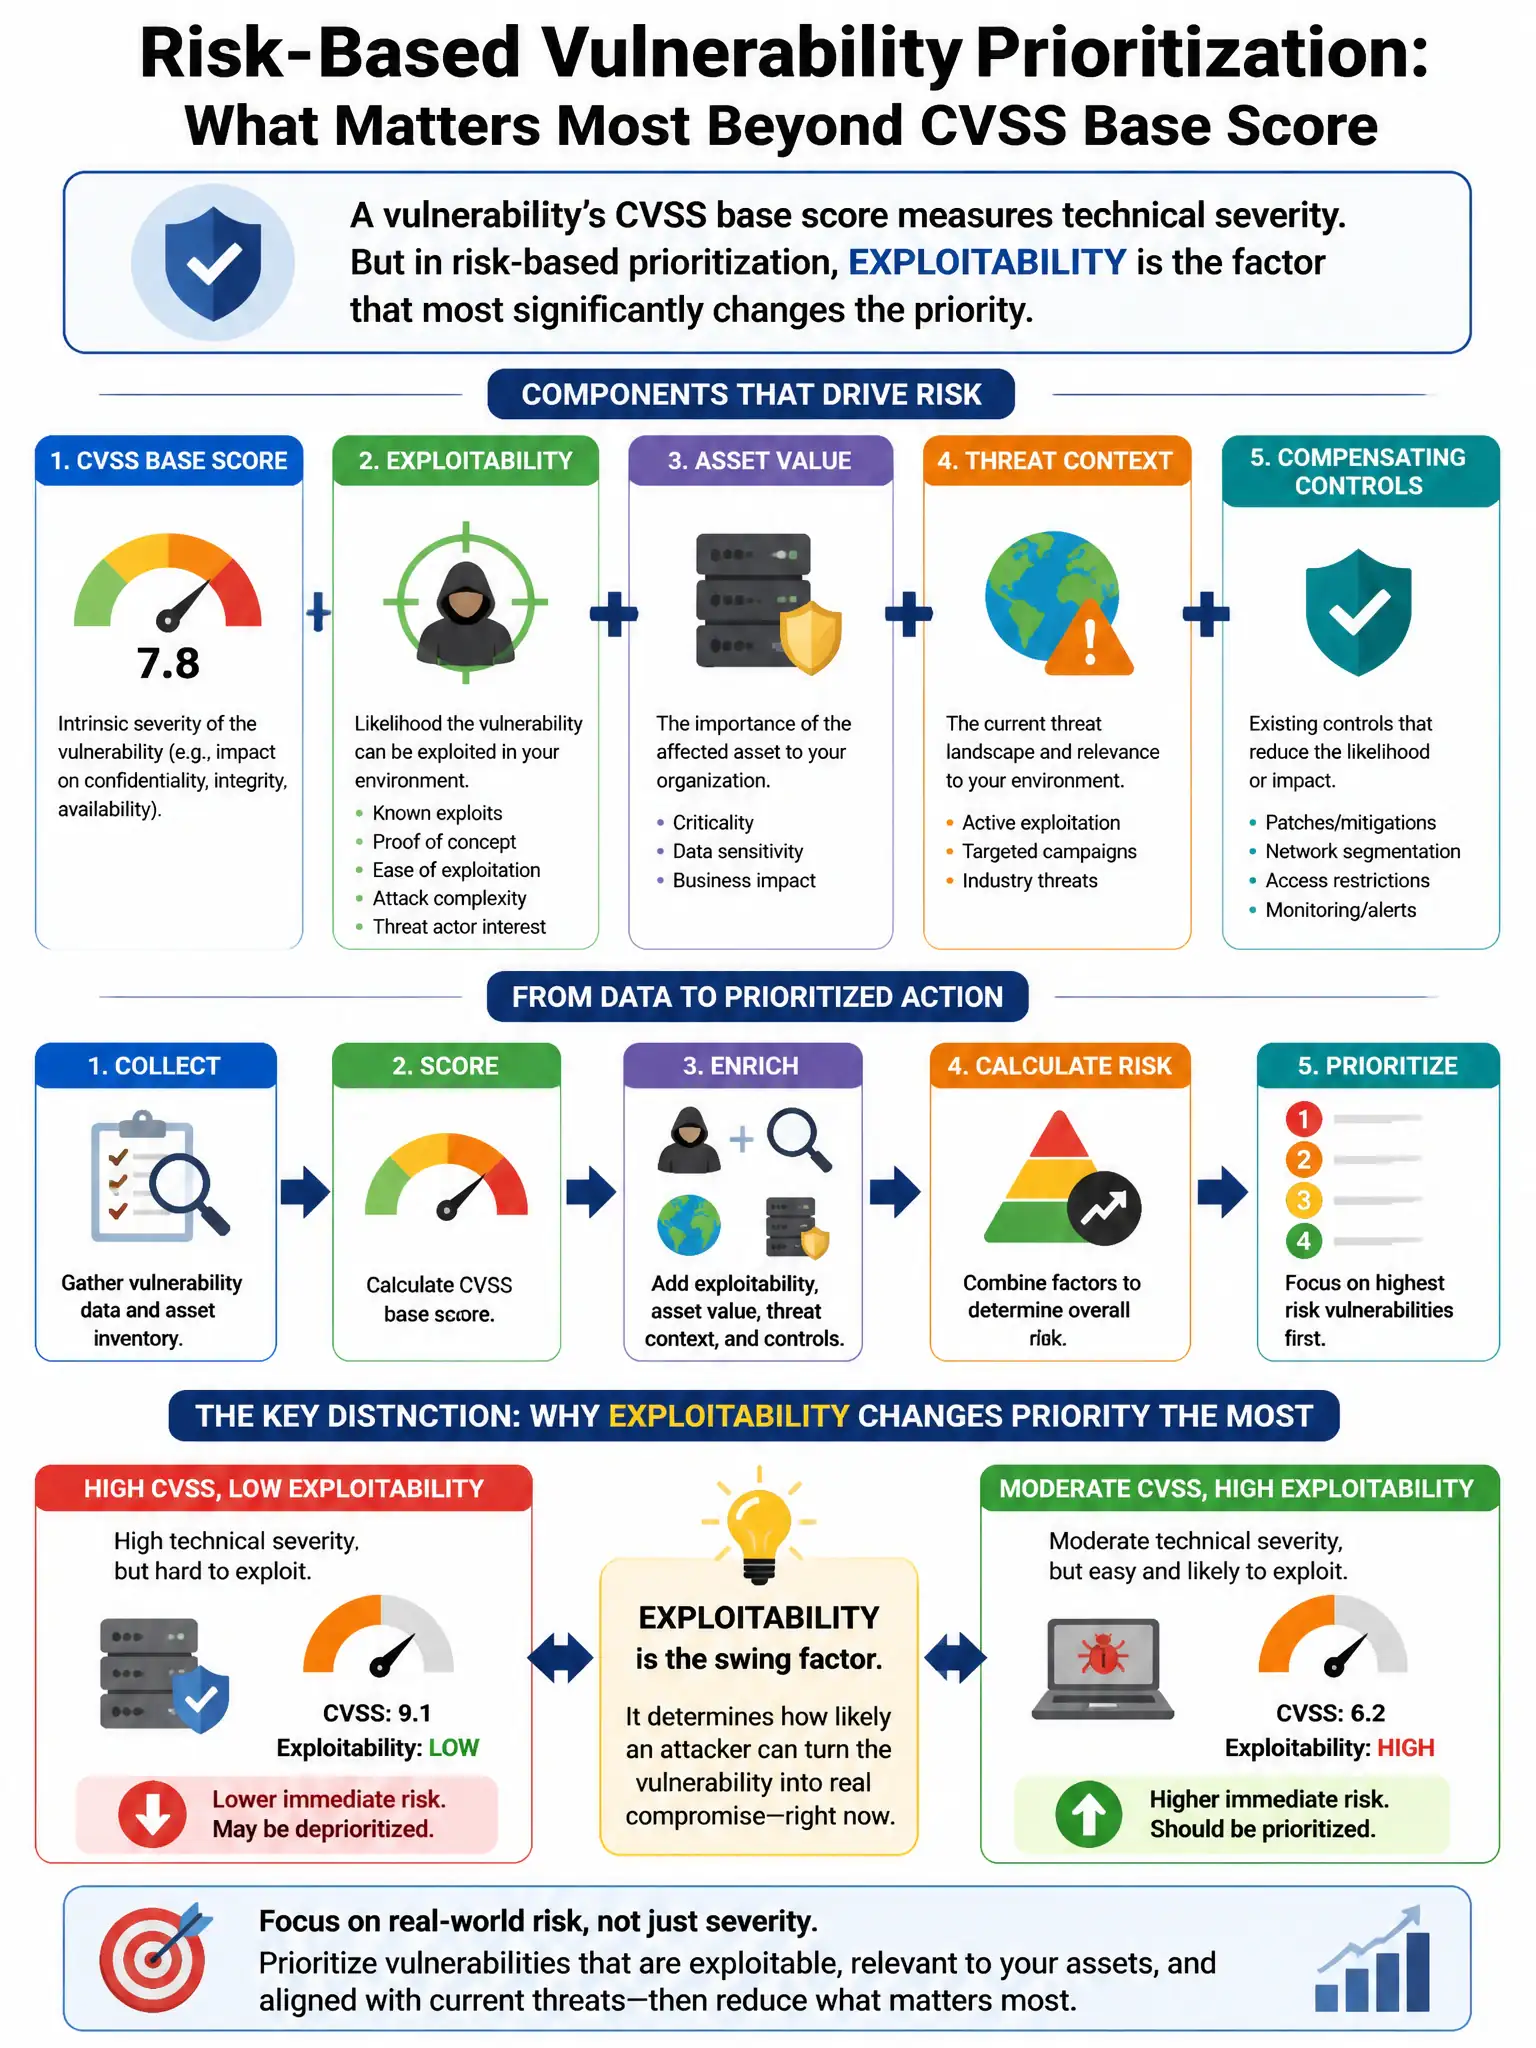
Here's the deal — threat intelligence confirming active exploitation in the wild is the factor that most changes effective risk, because it turns a theoretical vulnerability into an immediate, actionable threat. Code size, advisory tone, and CVE assignment source don't tell you whether attackers are actually using it against organizations like yours.
Full Explanation
The factor that most significantly changes effective risk is threat intelligence confirming active exploitation in the wild, especially when a weaponized exploit is publicly available and being used in attacks targeting similar organizations. This dramatically increases the probability of exploitation, turning a theoretical risk into an active threat; a vulnerability actively exploited by threat actors against the same industry sector is immediately actionable regardless of its CVSS score. The number of lines of code in the vulnerable component is wrong because code complexity affects how difficult the vulnerability is to analyze but does not directly indicate exploitation likelihood. The vendor's communication style in the security advisory is wrong because it has no bearing on the technical risk of the vulnerability. Whether the CVE was assigned by MITRE or a CNA is wrong because it does not affect the technical severity or exploitation likelihood.